
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
219 results
sandbox-runtime preview

sandbox-runtime

GitHubanthropic-experimental/sandbox-runtime

A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.

configuration-auditingcontainer-securitydefensive-tools+4
4.9k
8 days ago
RedELK preview

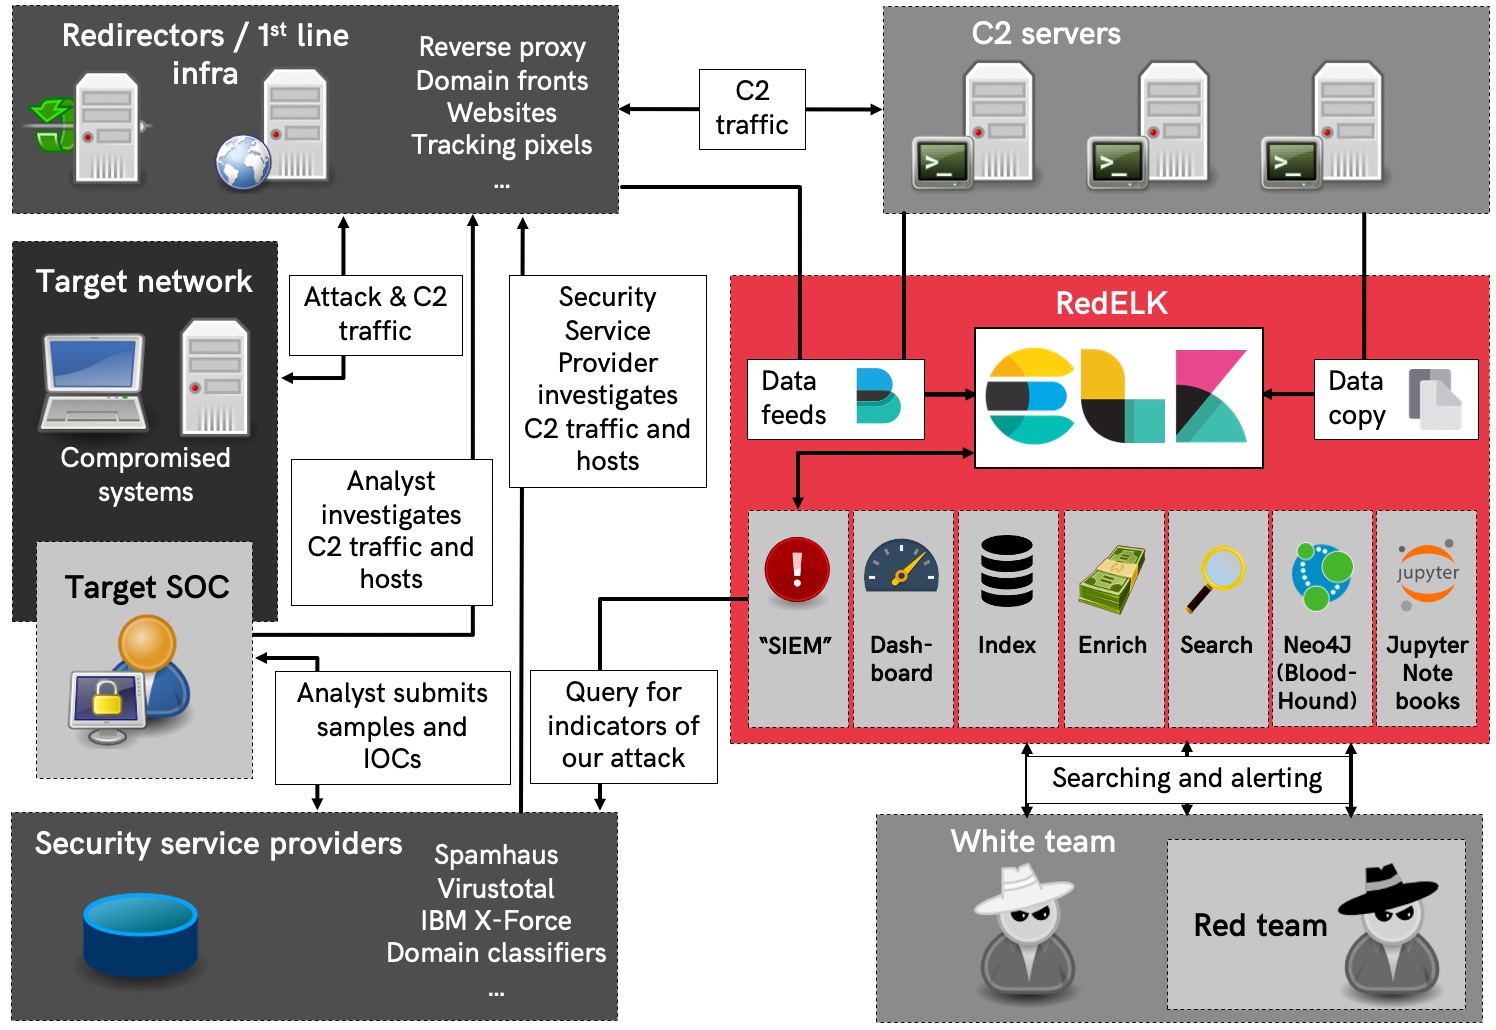
RedELK

GitHuboutflanknl/redelk

Red Team's SIEM - tool for Red Teams used for tracking and alarming about Blue Team activities as well as better usability in long term operations.

defensive-toolsincident-responseinformation-gathering+4
2.7k1 day ago
APT-Hunter preview

APT-Hunter

GitHubahmedkhlief/apt-hunter

APT-Hunter is Threat Hunting tool for windows event logs which made by purple team mindset to provide detect APT movements hidden in the sea of…

forensicsincident-responselog-analysis+1
1.4k1 month ago
avml preview

avml

GitHubmicrosoft/avml

Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…

digital-forensicsforensicsincident-response+1
1.1k11 days ago
Zircolite preview

Zircolite

GitHubwagga40/zircolite

A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs

forensicsincident-responselog-analysis+1
8411 day ago
hawk preview

hawk

GitHubt0pcyber/hawk

Powershell Based tool for gathering information related to O365 intrusions and potential Breaches

cloud-infrastructure-securitycloud-securitydigital-forensics+3
9491 year ago
DumpsterFire preview

DumpsterFire

GitHubtrycatchhcf/dumpsterfire

"Security Incidents In A Box!" A modular, menu-driven, cross-platform tool for building customized, time-delayed, distributed security events.…

defensive-toolseducationincident-response+3
1.0k6 years ago
dfir-orc preview

dfir-orc

GitHubdfir-orc/dfir-orc

Forensics artefact collection tool for systems running Microsoft Windows

defensive-toolsdigital-forensicsforensics+2
4451 month ago
ALFA preview

ALFA

GitHubinvictus-ir/alfa

Automated forensic analysis tool for Google Workspace audit logs. Acquires all log types, maps events to MITRE ATT&CK Cloud Framework, and identifies…

cloud-securitydigital-forensicsforensics+3
1835 days ago
TrueTree preview

TrueTree

GitHubthemittenmac/truetree

A command line tool for pstree-like output on macOS with additional pid capturing capabilities

digital-forensicsforensicsincident-response+1
28513 days ago
dfirtriage preview

dfirtriage

GitHubtravisfoley/dfirtriage

Digital forensic acquisition tool for Windows based incident response.

digital-forensicsforensicsincident-response+1
3482 years ago
ketshash preview

ketshash

GitHubcyberark/ketshash

A little tool for detecting suspicious privileged NTLM connections, in particular Pass-The-Hash attack, based on event viewer logs.

authenticationdefensive-toolsincident-response+3
1691 year ago
Fennec preview

Fennec

GitHubabdulrhmanalfaifi/fennec

Artifact collection tool for *nix systems

digital-forensicsforensicsincident-response+3
2202 years ago
metahub preview

metahub

GitHubgabrielsoltz/metahub

Automated security findings enrichment and impact evaluation tool for AWS. Enriches vulnerability data with resource context, associations, and tags…

cloud-securityconfiguration-auditingincident-response+3
1778 months ago
SharePointDumper preview

SharePointDumper

GitHubzh54321/sharepointdumper

PowerShell SharePoint extraction + auditing tool for red/blue/purple teams. Enumerates all SharePoint sites/drives a user can access via Microsoft…

authenticationcloud-securitydata-exfiltration+7
1679 months ago
vinifera preview

vinifera

GitHubzomato/vinifera

A GitHub recon/monitoring tool for finding internal leaks belonging to your organisation.

incident-responseinformation-gatheringosint+2
942 years ago
ThreatHound preview

ThreatHound

GitHubmazx0p/threathound

Automated threat hunting and incident response tool for Windows Event Logs with Sigma rule integration, real-time detection, and forensic artifact…

digital-forensicsincident-responselog-analysis+1
1602 years ago
detectree preview

detectree

GitHubwithsecurelabs/detectree

Interactive data visualization tool for blue teams to analyze detection data, understand relationships, reduce alert fatigue, and improve incident…

defensive-toolsincident-responselog-analysis+1
1263 years ago
Previous12…13Next