
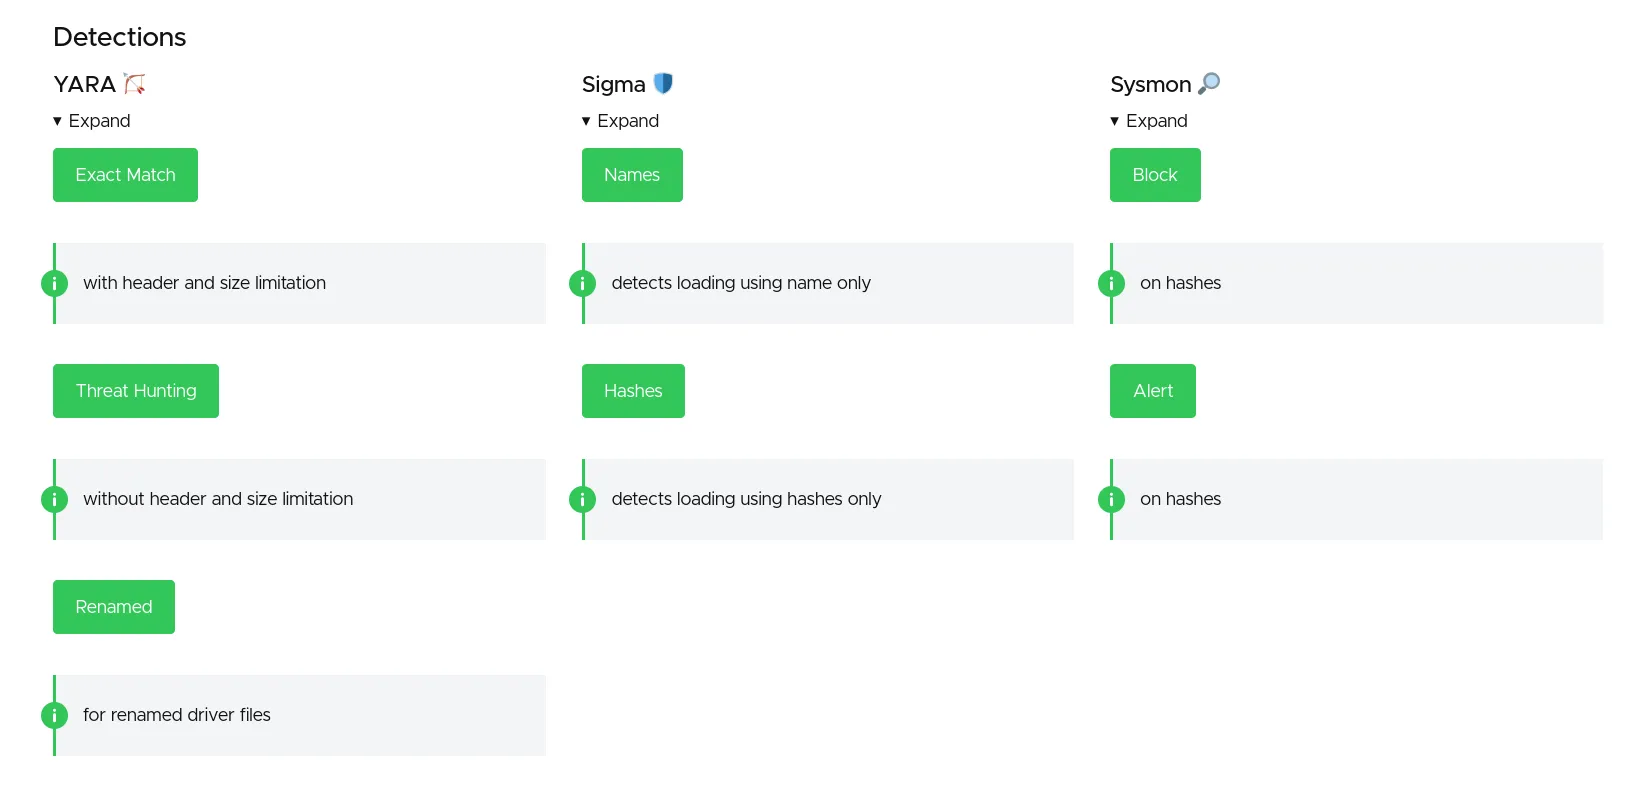
LOLDrivers
 magicsword-io/loldrivers
Curated database of vulnerable and malicious Windows drivers with YARA, Sigma, ClamAV, and Sysmon detection rules for proactive threat hunting and…
curated-resourceseducationforensics+5
1.8k
magicsword-io/loldriversCurated database of vulnerable and malicious Windows drivers with YARA, Sigma, ClamAV, and Sysmon detection rules for proactive threat hunting and…
 otrf/security-datasets
Re-play Security Events
 theflink/hunt-sleeping-beacons
Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
 marcosd4h/memhunter
Live hunting of code injection techniques
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
 the-dfir-report/sigma-rules
Rules generated from our investigations.
 botherder/androidqf
Portable forensic acquisition tool for Android devices that collects relevant data via USB debugging to identify potential spyware or compromise…
 op7ic/blueteam.lab
Blue Team detection lab created with Terraform and Ansible in Azure.
 safelineman/agentic-soc-simulation
AI 驱动的 SOC 仿真平台
 dsnezhkov/racketeer
Agent-based ransomware simulation toolkit for controlled detection testing across Windows endpoints and network assets, with a cross-platform…
 joe-desimone/patriot
In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
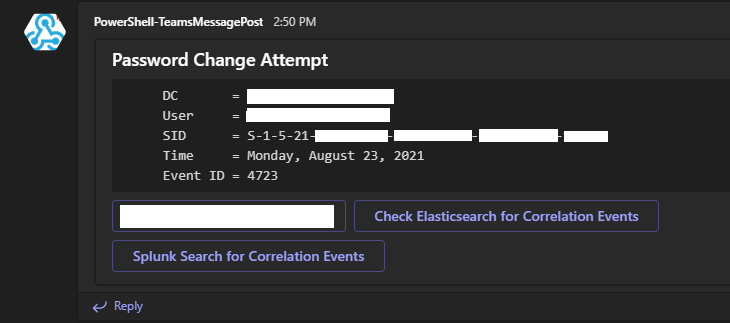 osbornepro/btps-secpack
PowerShell-based security toolkit for small-to-medium enterprises, providing automated alerts, Active Directory hardening, Windows Event Forwarding,…
 malgamy/yara_rules
Curated signature-rule collection for detecting and classifying malicious files via pattern matching, with CLI instructions for scanning files and…
 spoofzu/jvmxray
Externalize Java application access to protected resources as log messages.
 theflink/hunt-weird-imageloads
Small tool to play with IOCs caused by Imageload events
 iomoath/filewatchtower
FWT is a security analysis and file monitoring tool that utilizes Sysmon events.
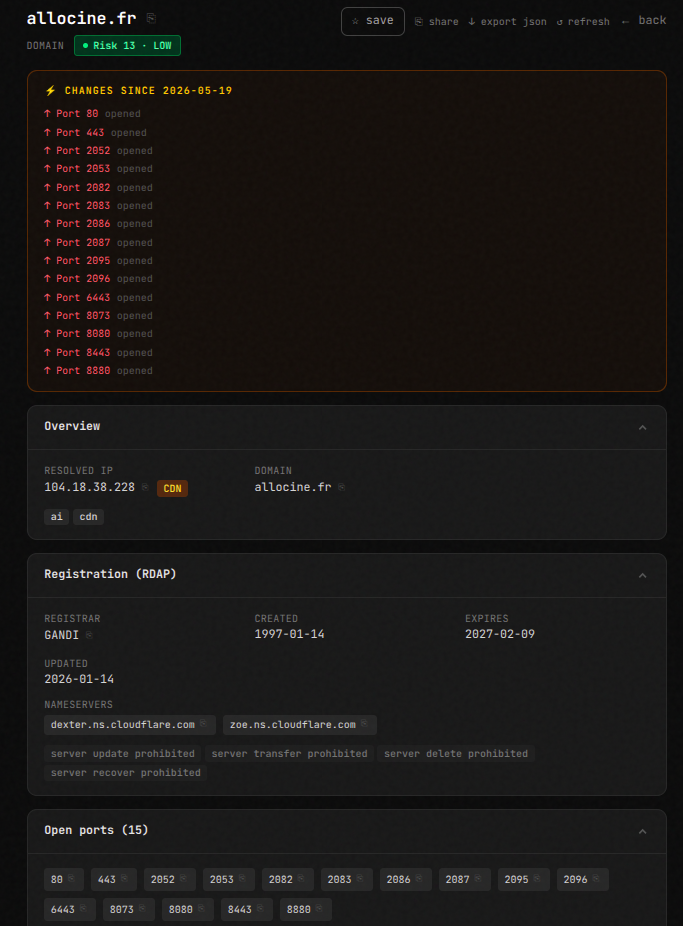 teycir/seekyou
OSINT intelligence on any IP, domain, or ASN
 nccgroup/yaml2yara
Generate bulk YARA rules from YAML input