
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
1322 results
Malcolm preview

Malcolm

GitHubcisagov/malcolm

Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
digital-forensicsdns-analysisforensics+9
2.5k
9h 14m ago
CVE-2025-55182-Researching-process preview

CVE-2025-55182-Researching-process

GitHubtechwithorgito/cve-2025-55182-researching-process

Defensive research repository for CVE-2025-55182 (Pre-Auth RCE in React Server Components/Next.js). Includes technical analysis, detection rules…
curated-resourceseducationexploitation+6
5 months ago
CVE-2025-55182-Researching-process preview

CVE-2025-55182-Researching-process

GitHuborgito1015/cve-2025-55182-researching-process

Defensive research repository for CVE-2025-55182 (Pre-Auth RCE in React Server Components/Next.js). Includes vulnerability analysis, detection rules…
educationexploitationincident-response+6
16 months ago
ThreatHound preview

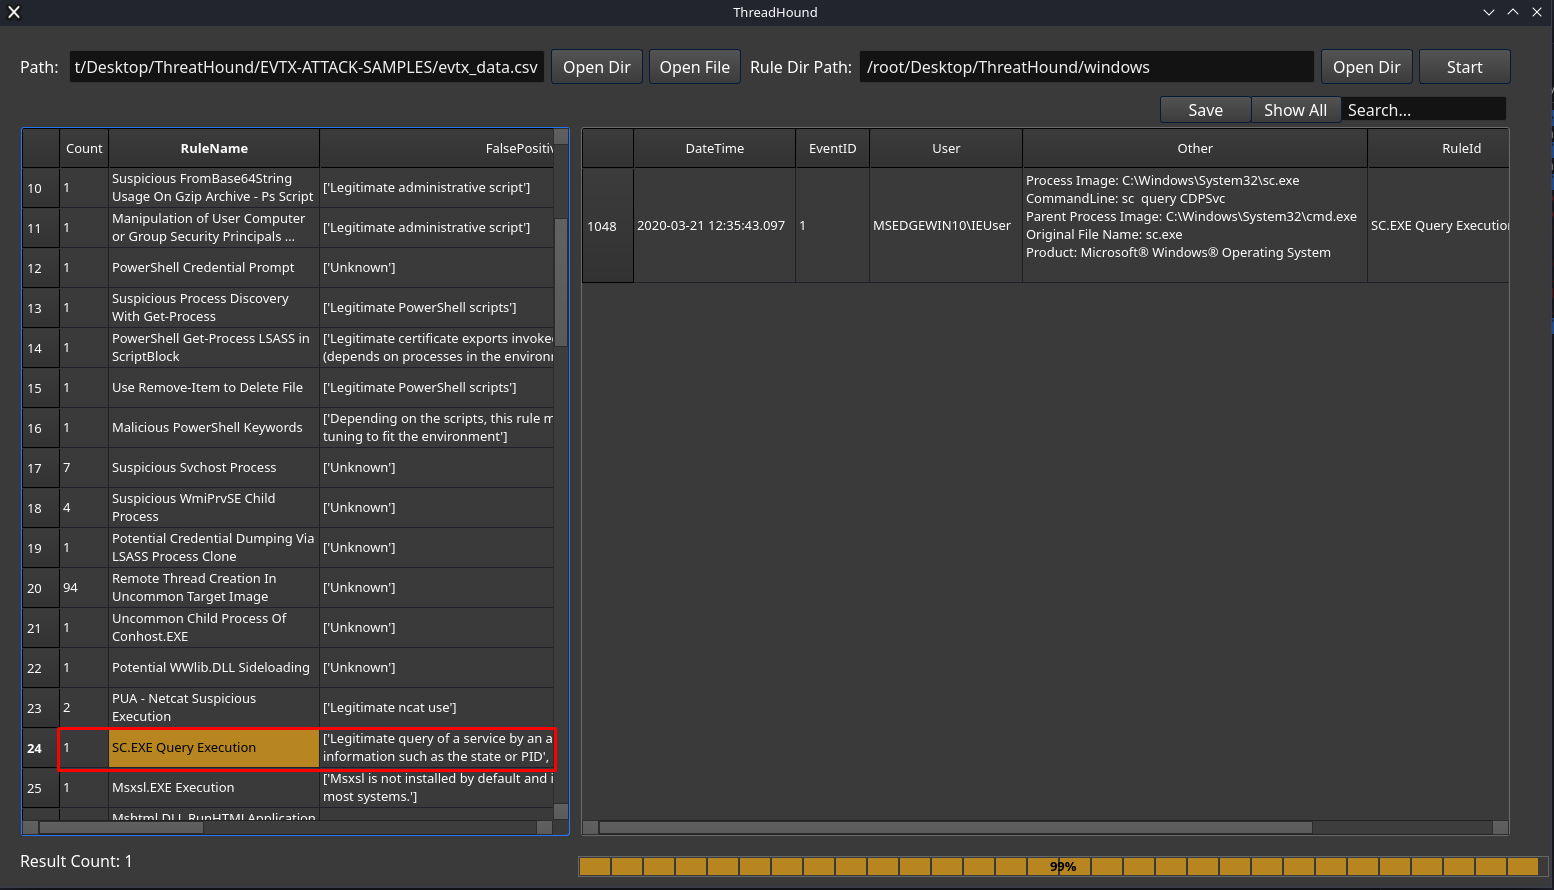
ThreatHound

GitHubmazx0p/threathound

Automated threat hunting and incident response tool for Windows Event Logs with Sigma rule integration, real-time detection, and forensic artifact…

digital-forensicsincident-responselog-analysis+1
1602 years ago
cloud-audit preview

cloud-audit

GitHubal0ne/cloud-audit

Automated cloud security auditing tool that detects AK/SK credential misuse by periodically auditing cloud platform logs using anomaly detection,…
anomaly-detectioncloud-securityincident-response+2
442 years ago
phantom-playbooks preview

phantom-playbooks

GitHubcorelight/phantom-playbooks

Automated security incident response playbooks for Splunk Phantom, integrating Zeek logs, DNS analysis, and VirusTotal threat intelligence to…
defensive-toolsincident-responseintrusion-detection+4
93 years ago
caldera preview

caldera

GitHubapache/caldera

Automated Adversary Emulation Platform

adversarial-attackcommand-and-controlctf+7
7.1k2 months ago
IntelOwl preview

IntelOwl

GitHubintelowlproject/intelowl

Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
curated-resourcesdigital-forensicsdynamic-analysis-sandboxing+14
4.7k2 months ago
Watcher preview

Watcher

GitHubthalesgroup-cert/watcher

AI-powered threat intelligence platform for automated CVE/ransomware monitoring, domain surveillance, data leak detection, and incident response with…

ai-securitydata-exfiltrationdns-subdomain-enumeration+7
1.4k15 days ago
Python-Honeypot preview

Python-Honeypot

GitHubowasp/python-honeypot

OWASP Honeypot, Automated Deception Framework.
api-securitycontainer-securitydefensive-tools+4
4822 years ago
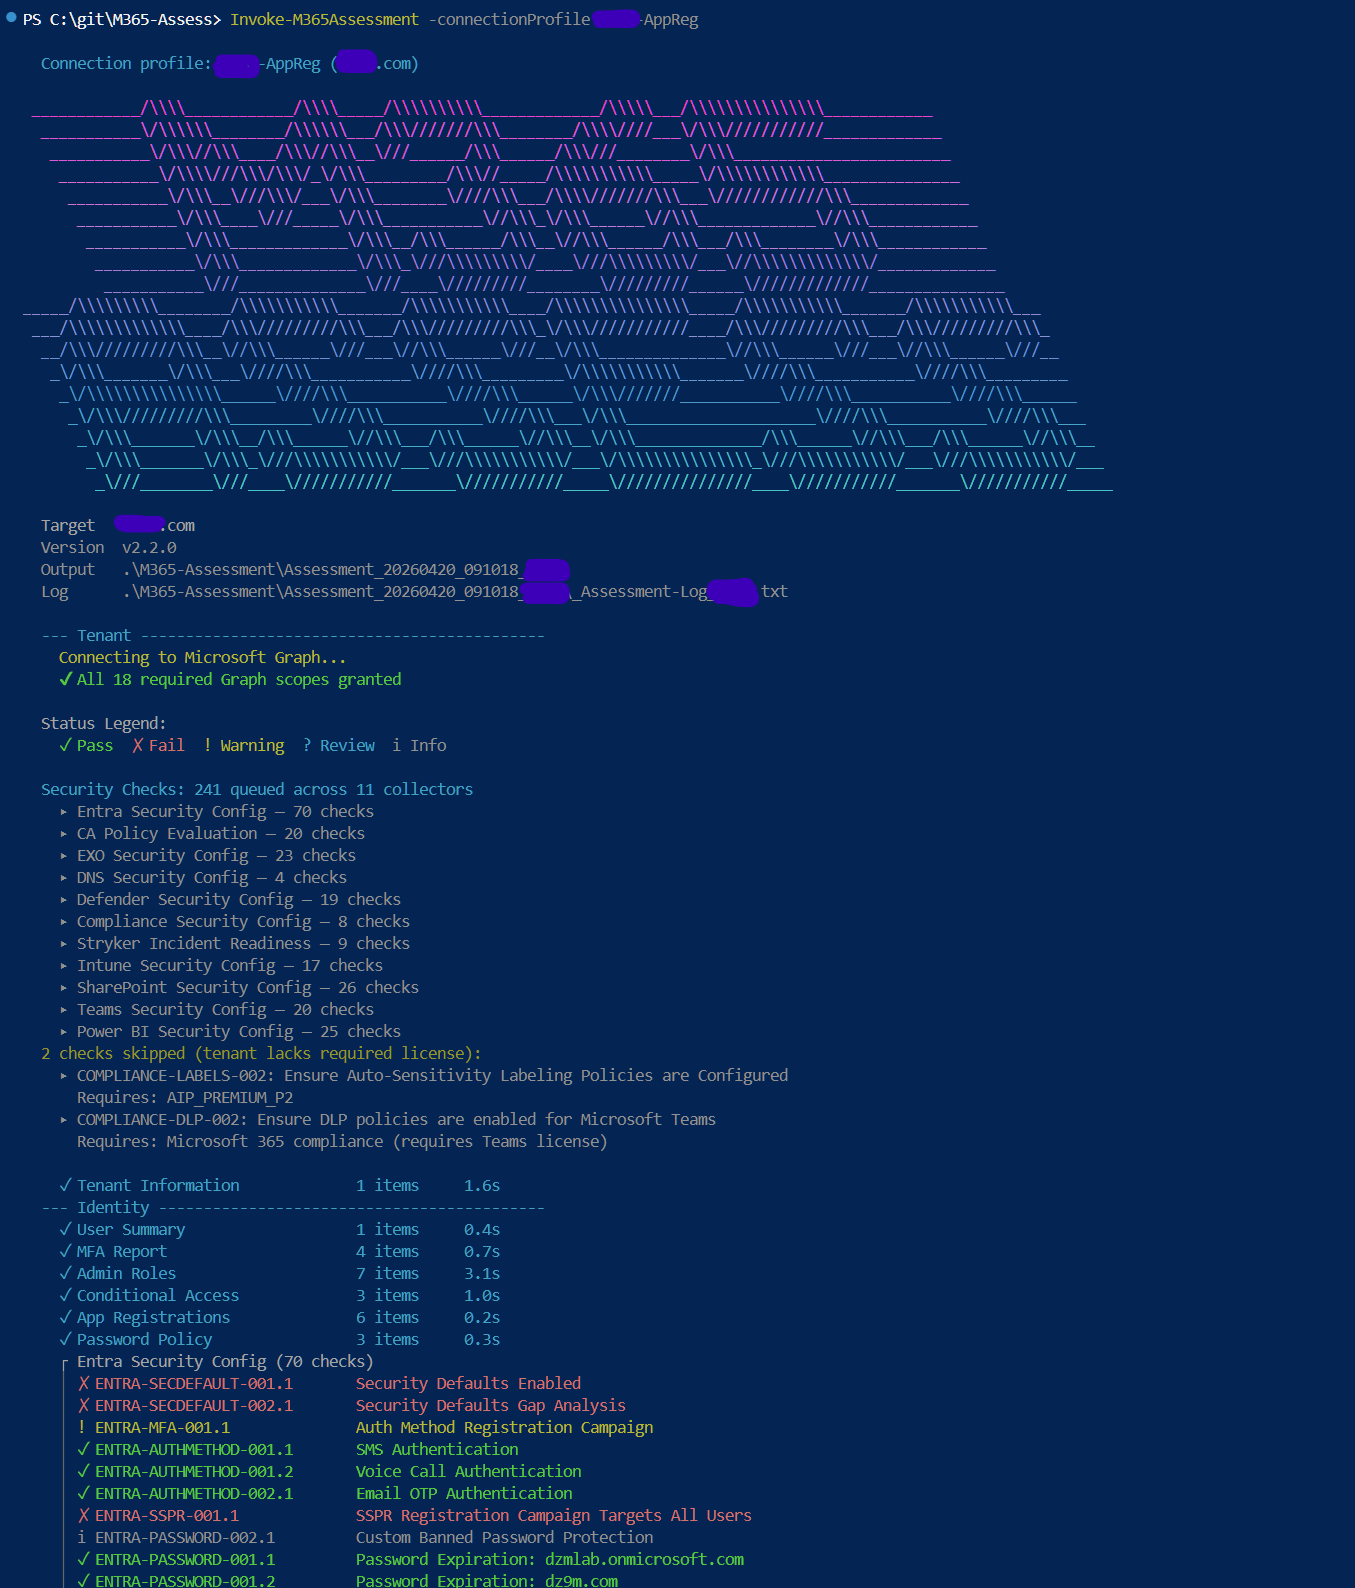
M365-Assess preview

M365-Assess

GitHubgalvnyz/m365-assess

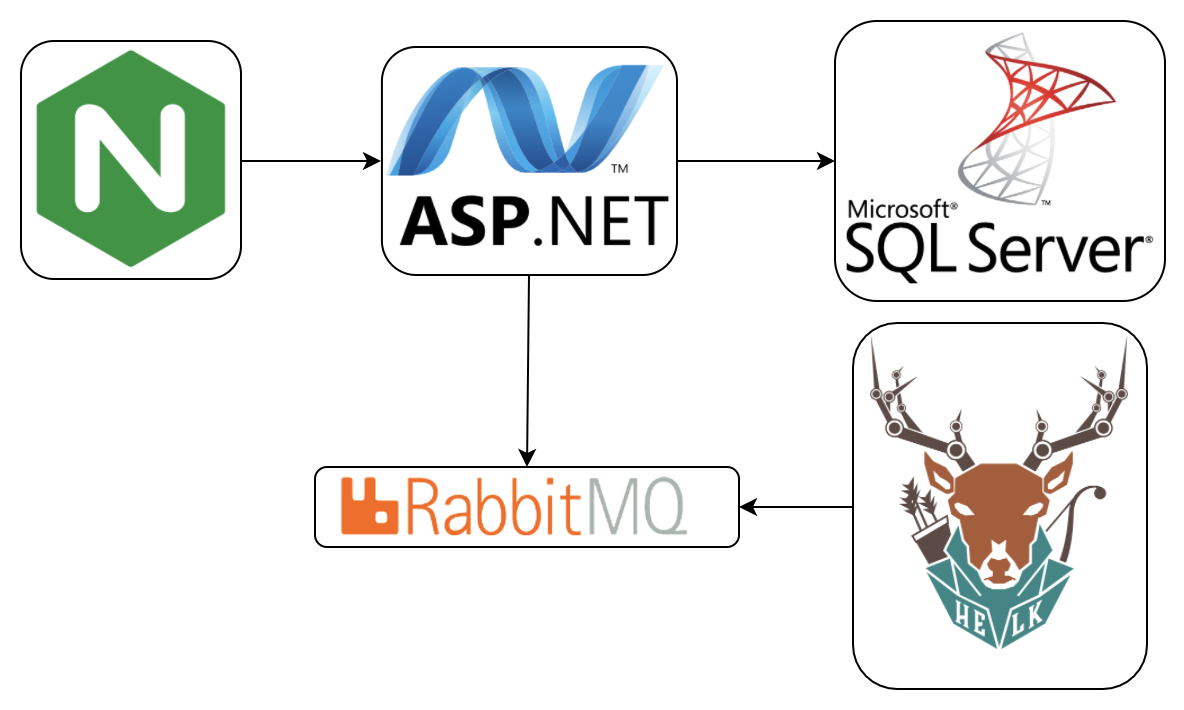
290+ Automated checks across 14 compliance frameworks, interactive HTML report, no data leaves your machine.
cloud-securityconfiguration-auditingdevsecops+4
18913 days ago
ACE preview

ACE

GitHubinvoke-ir/ace

Automated, Collection, and Enrichment Platform

digital-forensicsforensicsincident-response+2
3258 years ago
LinuxCatScale preview

LinuxCatScale

GitHubwithsecurelabs/linuxcatscale

Incident Response collection and processing scripts with automated reporting scripts

digital-forensicsforensicsincident-response+2
3382 years ago
WELA preview

WELA

GitHubyamato-security/wela

Audits Windows event log settings against best-practice guidelines and Sigma-rule detectability, with automated configuration for DFIR readiness.
configuration-auditingdigital-forensicsincident-response+1
1182 days ago
brawl-public-game-001 preview

brawl-public-game-001

GitHubmitre/brawl-public-game-001

Data from a BRAWL Automated Adversary Emulation Exercise
adversarial-attackcloud-securitydigital-forensics+7
2158 years ago
Collect-MemoryDump preview

Collect-MemoryDump

GitHublethal-forensics/collect-memorydump

Automated PowerShell script for forensically sound Windows memory acquisition, including crash/raw dumps, pagefile collection, triage artifacts, and…

digital-forensicsforensicsincident-response+1
2651 year ago
TuxResponse preview

TuxResponse

GitHubla3ar0v/tuxresponse

Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
digital-forensicsdisk-forensicsforensics+5
906 months ago
SyntheticSun preview

SyntheticSun

GitHubjonrau1/syntheticsun

Serverless AWS security automation framework that ingests threat intelligence, applies ML-based anomaly detection (RCF, IP Insights), and enriches…

anomaly-detectioncloud-securityincident-response+3
825 years ago
Previous123…74Next