
n8n-cve-2025-68613-thm
 khin-96/n8n-cve-2025-68613-thm
Educational walkthrough for exploiting CVE-2025-68613, a critical RCE in n8n workflow automation. Covers expression injection, sandbox escape,…
command-and-controleducationexploitation+6
1
khin-96/n8n-cve-2025-68613-thmEducational walkthrough for exploiting CVE-2025-68613, a critical RCE in n8n workflow automation. Covers expression injection, sandbox escape,…
 serpilrivas/log4shell-homework9
Log4Shell (CVE-2021-44228) exploit demo for SEAS 8405. Includes a vulnerable Spring Boot app, fake LDAP server, Docker setup, MITRE mapping, incident…
 airbus-cert/cve-2024-4040
Scanner for CVE-2024-4040
 zerozenxlabs/cve-2025-61882-oracle-ebs
Operational exploit for CVE-2025-61882 in Oracle E-Business Suite, with research artifacts for defensive validation, detection engineering, incident…
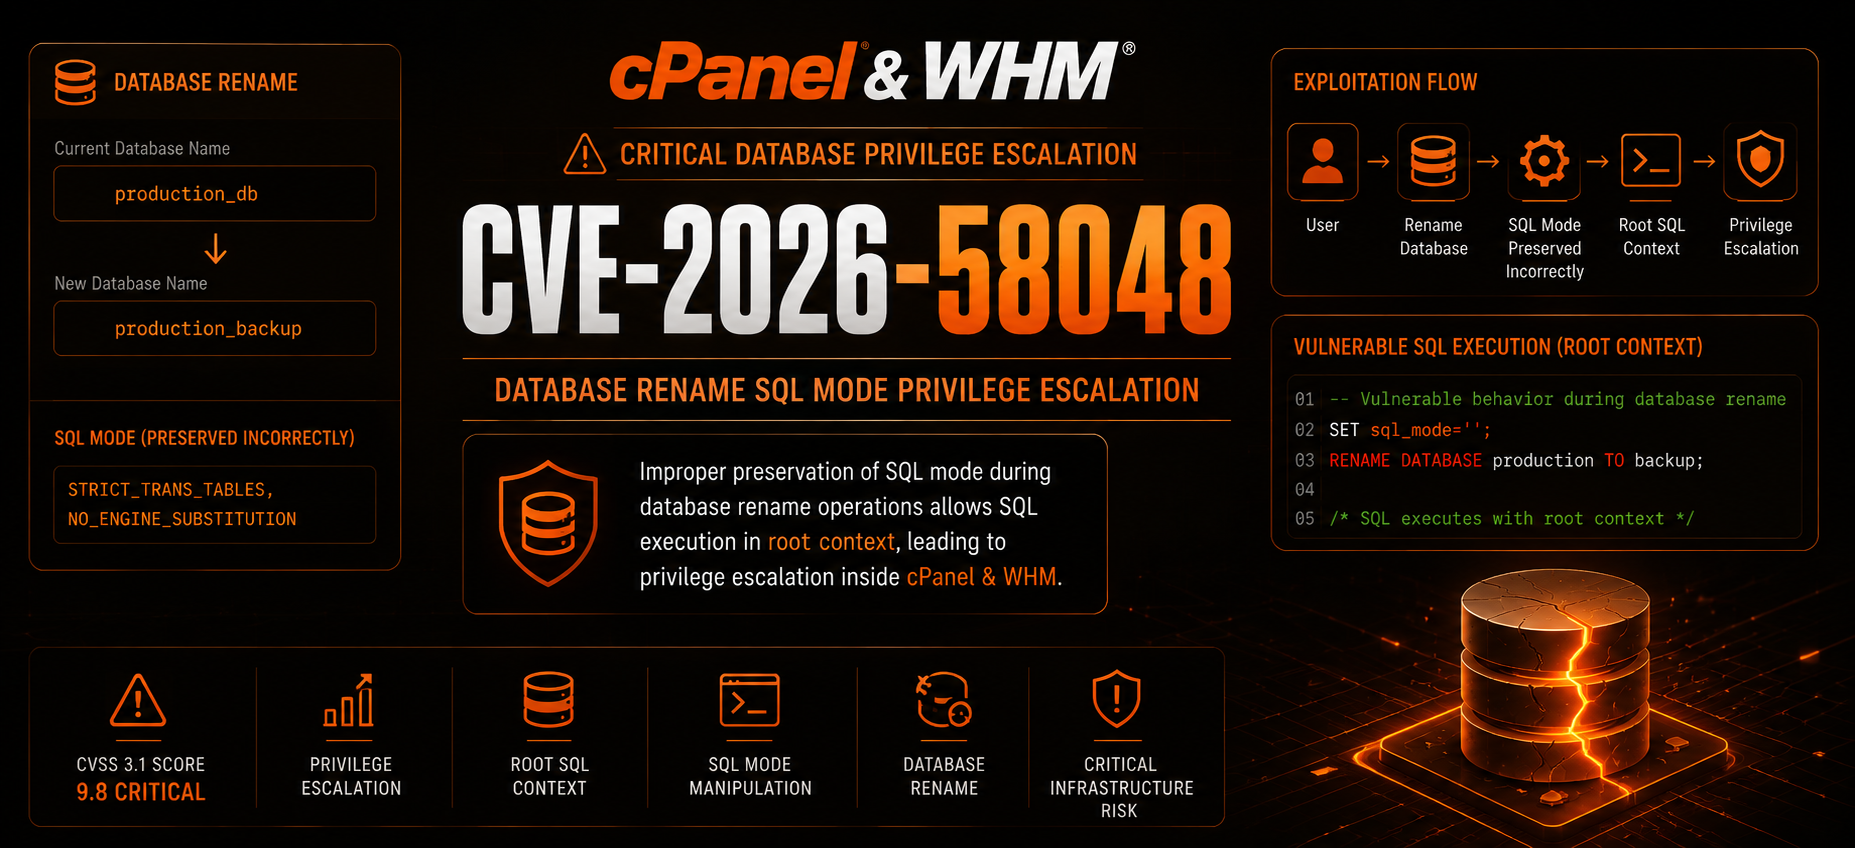 tc4dy/cve-2026-58048-poc-exploit
👾 CVE-2026-58048 – cPanel Root SQL Execution Toolkit (CVSS 9.4) | Full Red/Blue Team Toolkit suite for unpatched cPanel & WHM 11.x. 2 tools: Safe…
 kaleth4/cve-2026-64638
Technical analysis and defensive mitigation for a WordPress Core pre-auth XSS-to-RCE chain, including sanitizer bypass, DOM clobbering, JSONP abuse,…
 jeffreybxu/five-nights-at-follina-s
A Fullstack Academy Cybersecurity project examining the full cycle of the Follina (CVE-2022-30190) vulnerability, from exploit to detection and…
 exptechtw/cve-2025-66478
Real-world attack log analysis of CVE-2025-66478 (Next.js Server Actions RCE) with malware samples, attacker IP tracking, and container security…
 yosasasutsut/blackash-cve-2025-53770
Technical analysis and detection guidance for CVE-2025-53770, a critical unauthenticated RCE vulnerability in Microsoft SharePoint Server exploited…
 michaael01/letsdefend--soc-342-cve-2025-53770-sharepoint-exploit-toolshell
Detailed walkthrough of CVE-2025-53770 (ToolShell) SharePoint zero-day exploitation, including RCE analysis, MachineKey exfiltration, payload…
 masriyan/cve-2026-85097
Detection, verification and incident-response toolkit for CVE-2026-85097: remote Bricksforge assessment, log IOC hunting, filesystem implant audit,…
 mandiant/strace
A DTrace on Windows Reimplementation
 mingshenhk/citrixbleed-2-cve-2025-5777-poc-
详细讲解CitrixBleed 2 — CVE-2025-5777(越界泄漏)PoC 和检测套件
 qingtengyun/cve-2021-44228-qingteng-online-patch
Hot-patch CVE-2021-44228 by exploiting the vulnerability itself.
 adityabhatt3010/cve-2025-53770-sharepoint-zero-day-variant-exploited-for-full-rce
A critical zero-auth RCE vulnerability in SharePoint (CVE-2025-53770), now exploited in the wild, building directly on the spoofing flaw…
 instawp/wp2shell-scan
Detect & clean up wp2shell (CVE-2026-63030) WordPress compromise — bulk-runnable, read-only by default
 si13nttt/cve-2025-32432
Python PoC exploiting CVE-2025-32432, an unauthenticated RCE in Craft CMS via Yii DI gadget injection, with assetId scanning, reverse shell, and…
 0xblackash/cve-2026-48908
CVE-2026-48908