DIAL
 cred-club/dial
Event-driven AWS security misconfiguration detection framework that monitors multiple accounts in real-time, triggering alerts via Lambda for IAM,…
cloud-infrastructure-securitycloud-securitydefensive-tools+2
95
cred-club/dialEvent-driven AWS security misconfiguration detection framework that monitors multiple accounts in real-time, triggering alerts via Lambda for IAM,…
 jonrau1/syntheticsun
Serverless AWS security automation framework that ingests threat intelligence, applies ML-based anomaly detection (RCF, IP Insights), and enriches…
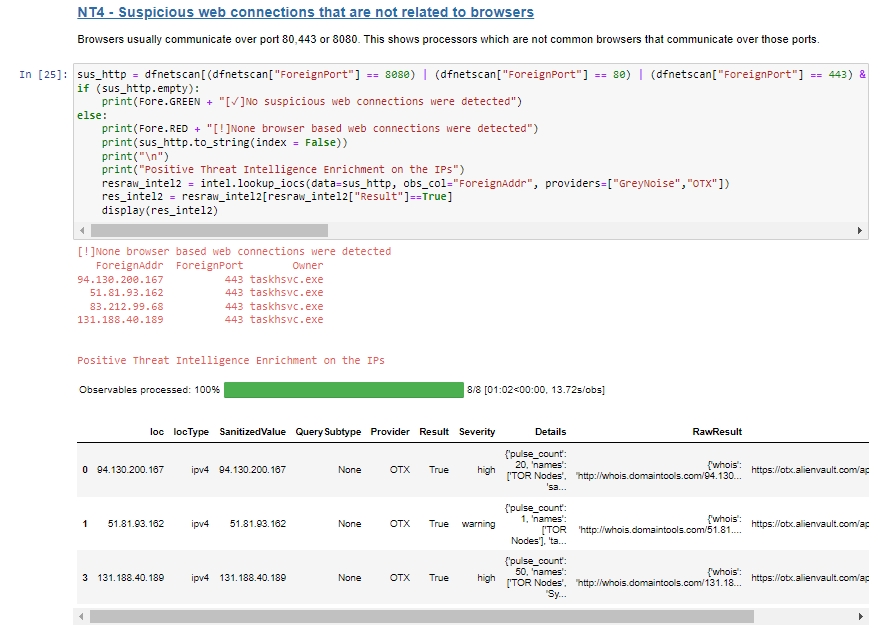 blueteam0ps/memoptix
A Jupyter notebook to assist with the analysis of the output generated from Volatility memory extraction framework.
 adversarial-detection-engineering/adversarial-detection-engineering-framework
A framework and taxonomy for identifying, classifying, and reasoning about detection logic bugs in SIEM, EDR, and XDR rules, with concrete examples…
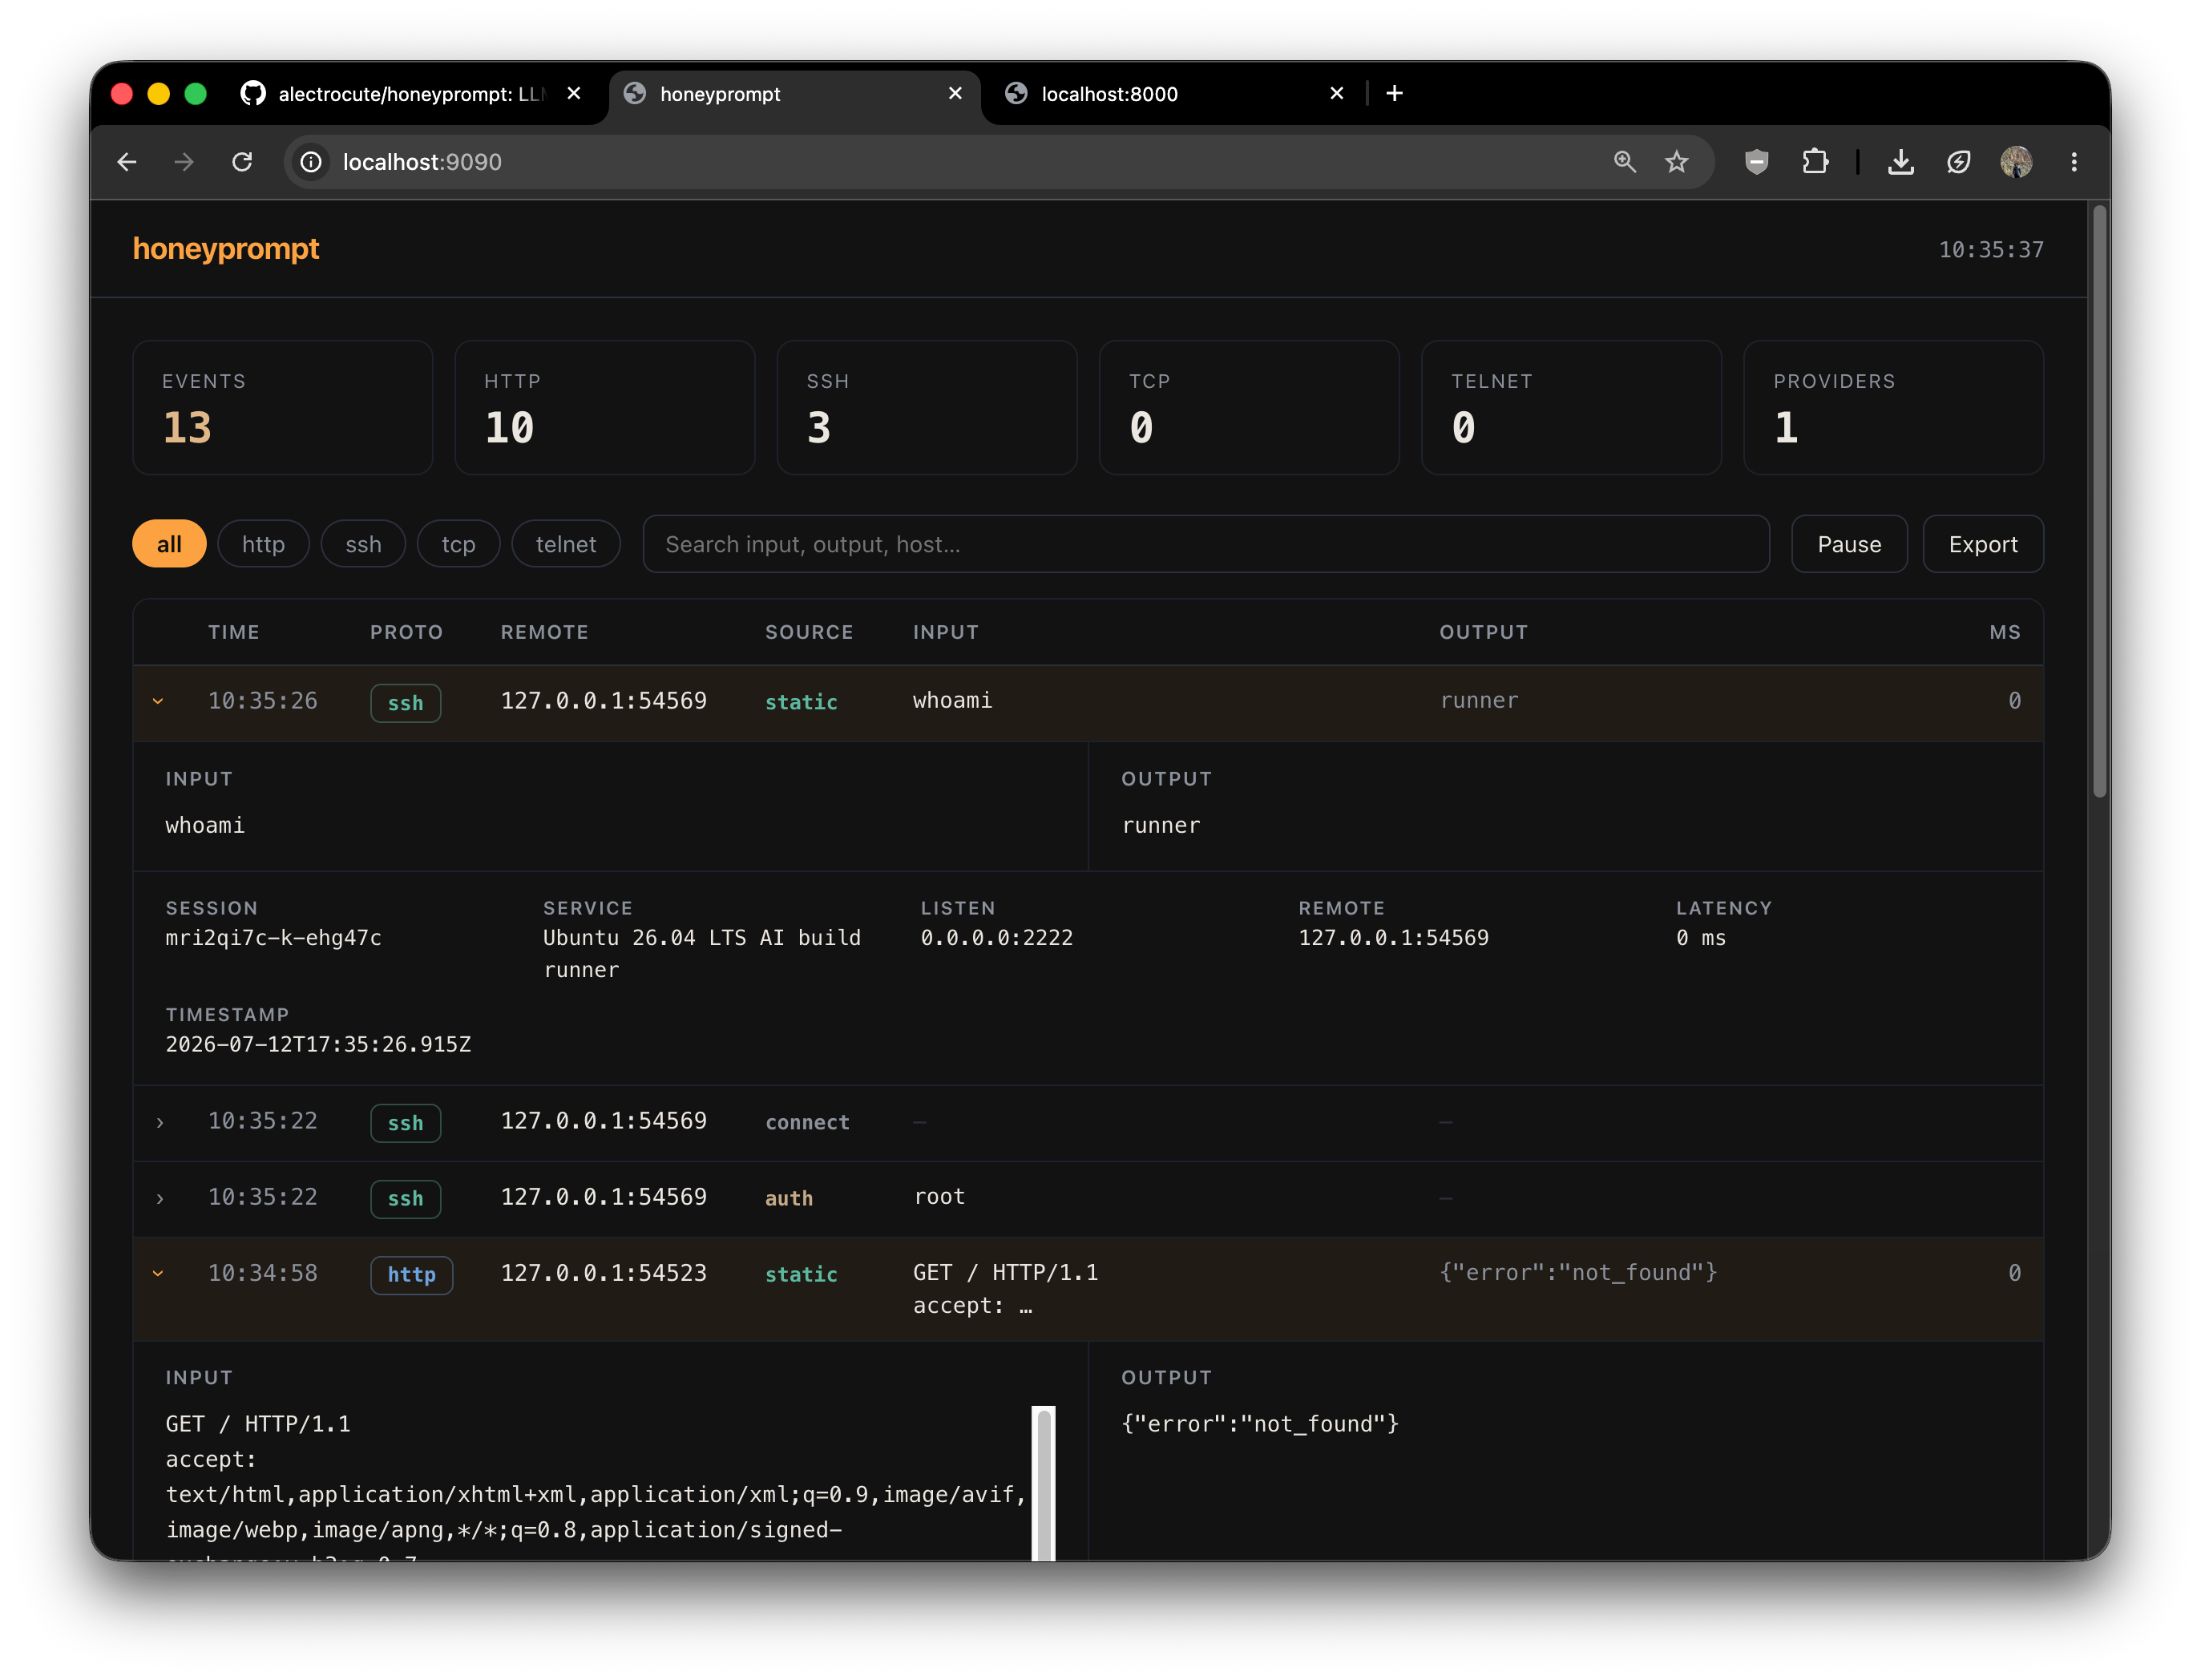 alectrocute/honeyprompt
LLM-first deception framework: "The honeypot that talks back!™"
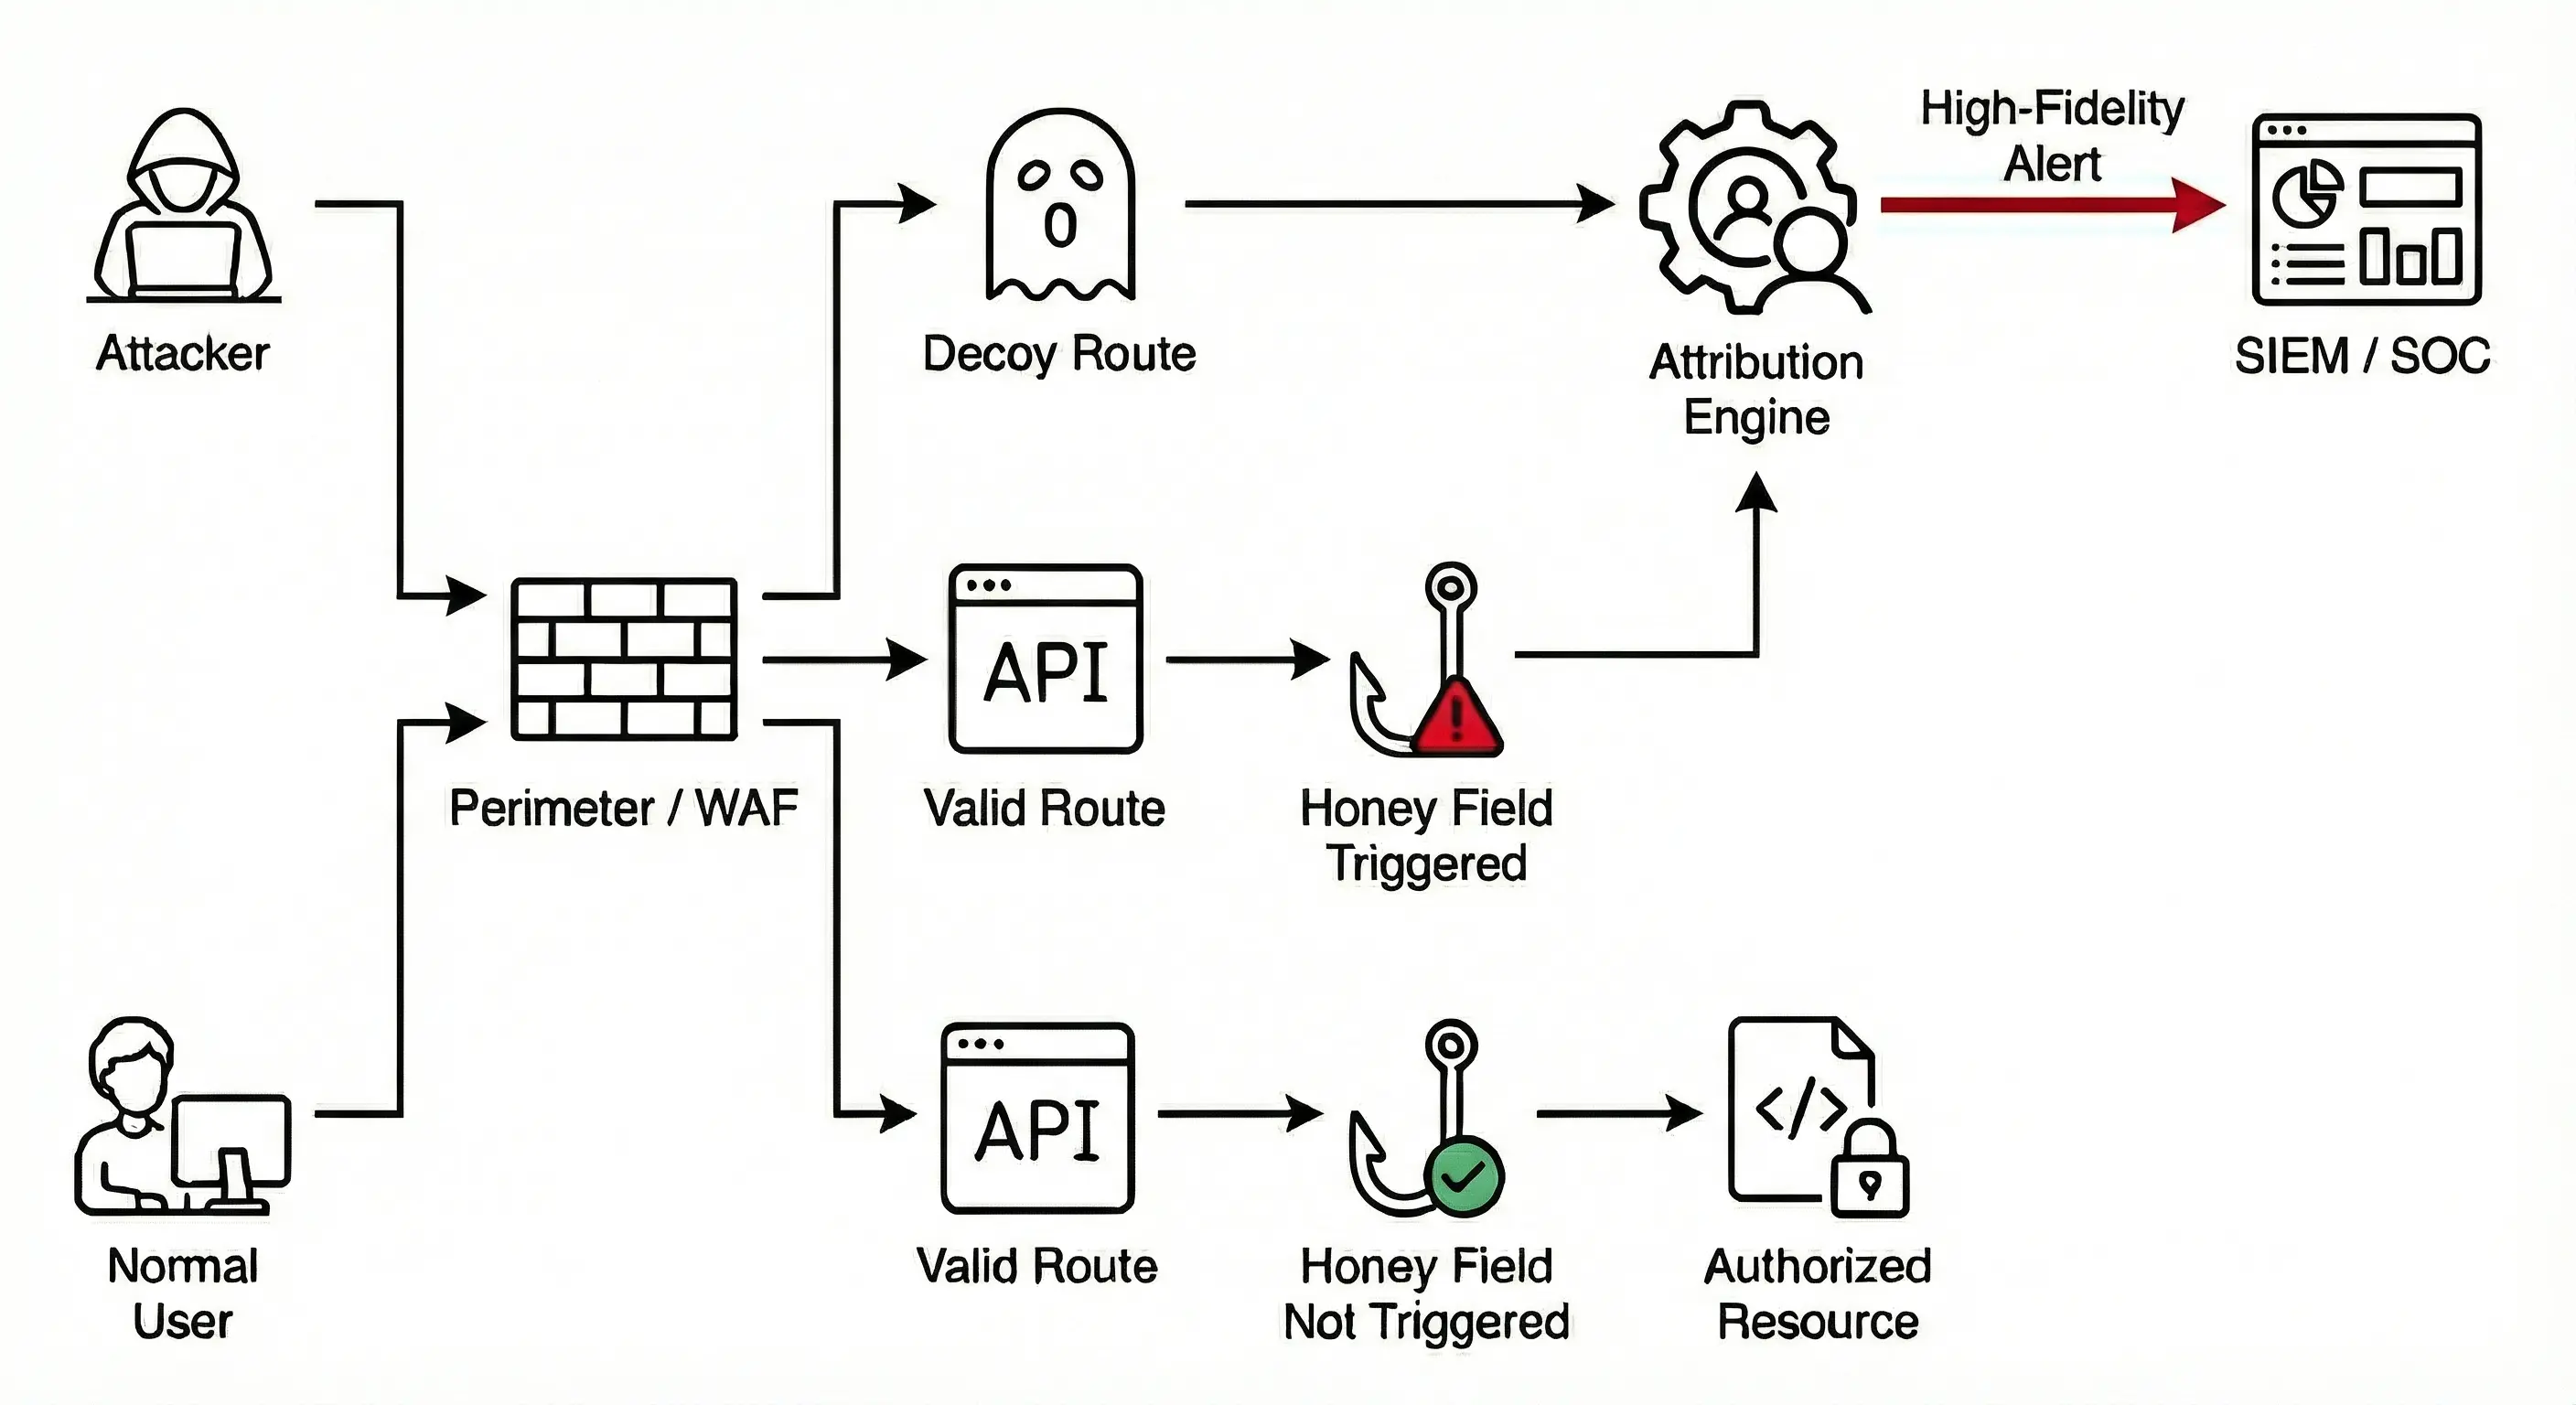 trappsec-dev/trappsec
Open-source framework for embedding realistic decoy routes and honey fields into APIs to detect attackers probing business logic, converting…
 dereeqw/berrysentinel
Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…
 corelight/c2-detection-manjusaka
Detection of Manjusaka C2 framework
 mahdi13830510/cve-2026-31431-mitigation-suite
Kernel-runtime defense framework for AF_ALG vulnerabilities, featuring eBPF socket tracing, Ansible hardening, and a crypto auditor for drift…
 nightfullstar/openclaw-defender
Multi-layer security framework for AI agent ecosystems. Provides pre-installation skill auditing, file integrity monitoring, runtime protection, and…
 theevidencehunter/forensix
Digital Forensics Intelligence Framework
 nerium-security/cve-2025-55182
Host-based detection rules for the RCE vulnerability in the React JavaScript framework.
 daryllundy/cve-2025-32463
Detection framework for CVE-2025-32463 sudo privilege escalation vulnerability. Provides real-time monitoring, forensic analysis, and SIEM…
 volatilityfoundation/volatility
An advanced memory forensics framework