

pipelock
 luckypipewrench/pipelock
Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
ai-securityapi-securitycloud-security+8
912
luckypipewrench/pipelockOpen-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
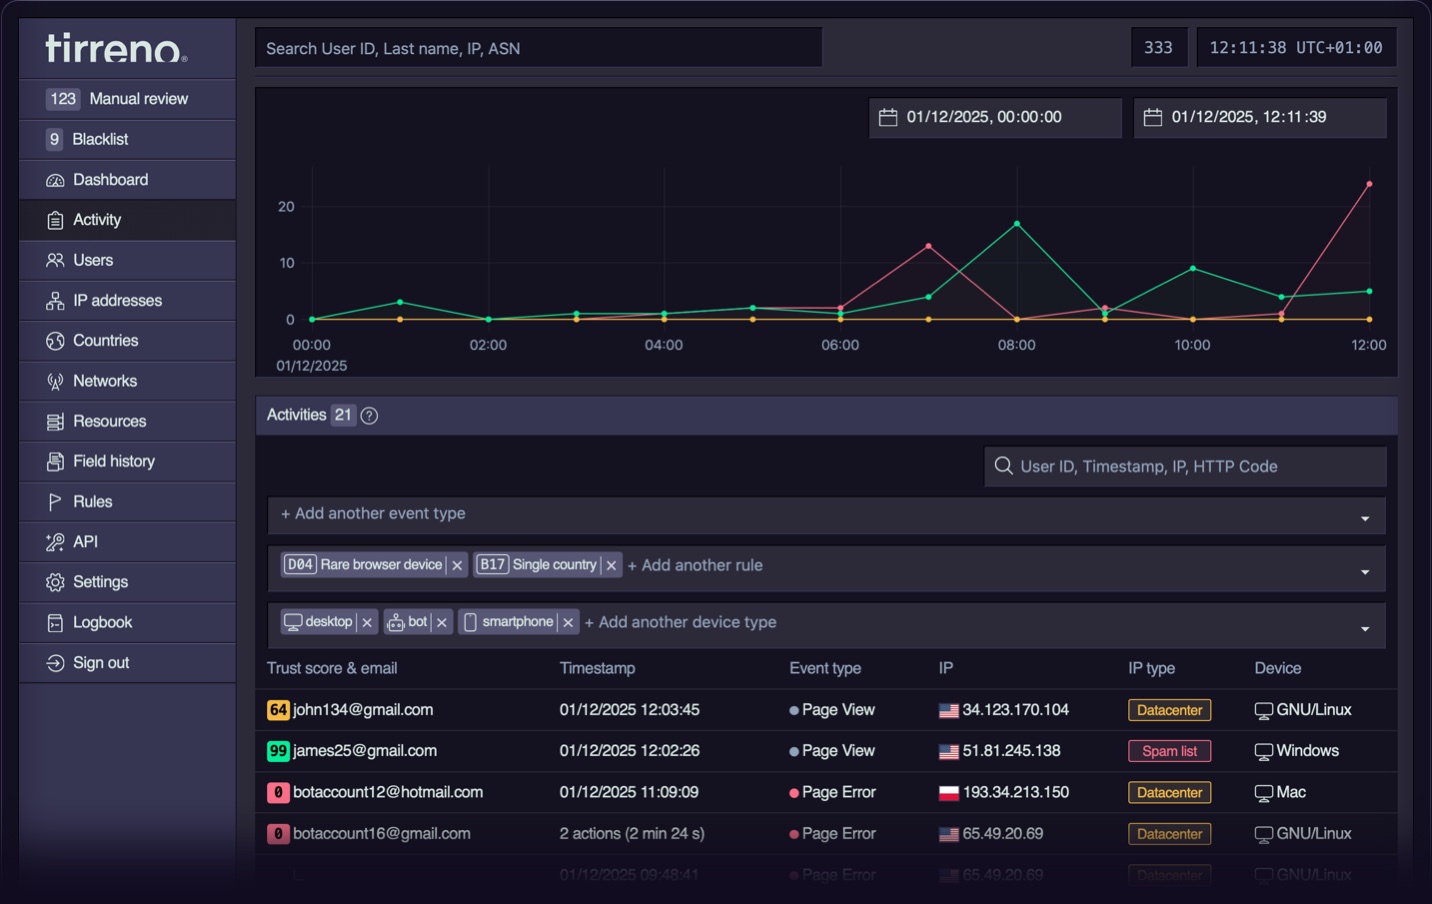 tirrenotechnologies/tirreno
Open-source security framework for real-time event tracking, threat detection, and risk scoring. Monitors user behavior, detects fraud, bot attacks,…
 sjkim1127/reversecore_mcp
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
 beelzebub-labs/beelzebub
A secure low code deception runtime framework, leveraging AI for System Virtualization.
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 jay123anta/laravel-threat-detection
Passive Laravel middleware that detects and logs SQL injection, XSS, RCE, bot scanners, and 175+ attack patterns. Features a built-in dashboard,…
 hashicorp-forge/grove
A Software as a Service (SaaS) log collection framework.
 elastic/agent-skills
Official Elastic Skills
 iocx-dev/iocx
An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…
 tracehound/tracehound
Operational security controls with forensic guarantees

 roxanne_ardary/securekit
Securekit is a protocol-agnostic security kernel that enforces zero-trust, sandboxed execution for AI tool use. It sits between any LLM or agent…
 skelersecurity/wordpress-skelersecurity-core-security-cve-2026-63030
Temporary WordPress plugin requiring authentication for the Core REST Batch API endpoint to mitigate the wp2shell vulnerability chain…
 roxanne_ardary/securecivic
SecureCivic is a citizen-built, open source identity verification platform designed for SSA adoption. It replaces private data brokers with a secure,…
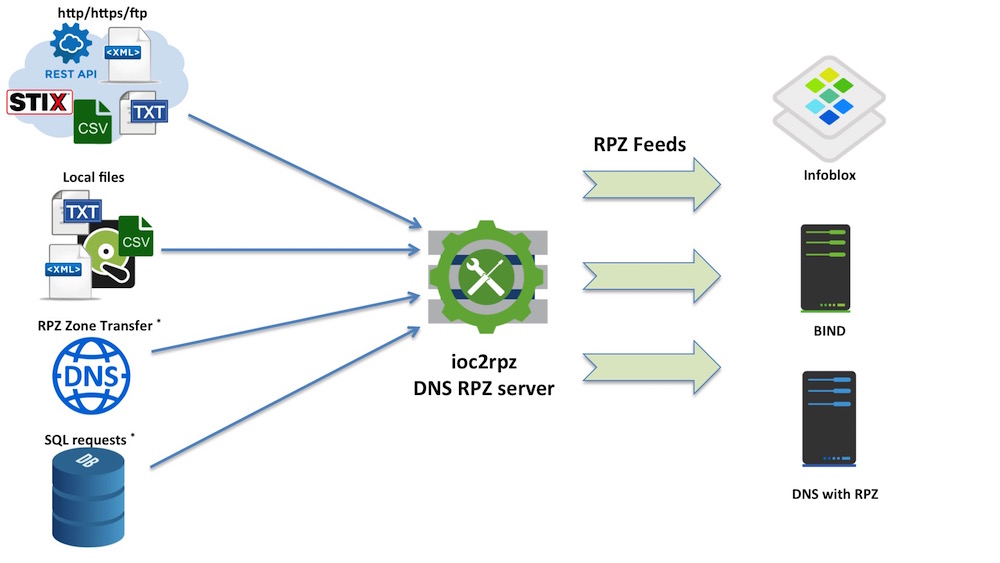 homas/ioc2rpz
ioc2rpz is a place where threat intelligence meets DNS.
 mukul975/cve-mcp-server
Production-grade MCP server giving Claude 27 security intelligence tools across 21 APIs — CVE lookup, EPSS scoring, CISA KEV, MITRE ATT&CK, Shodan,…
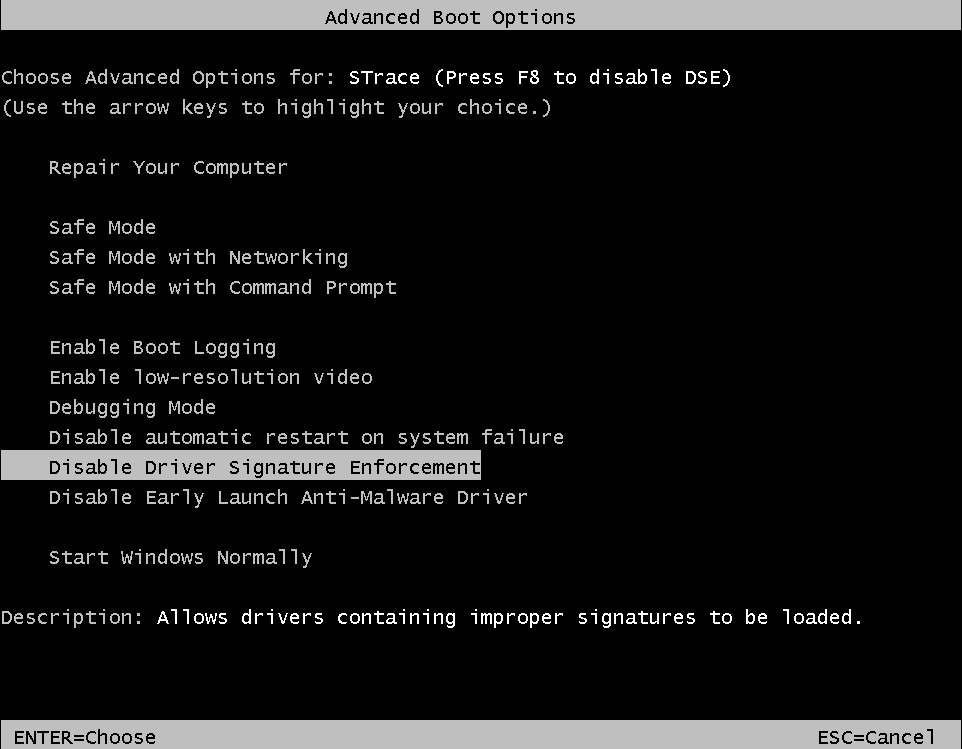 mandiant/strace
A DTrace on Windows Reimplementation
 quantumworld-dpdns-io/cve-2026-42945
Full CVE-2026-42945 research repository with heap buffer overflow analysis, RCE exploit (heap spray + Feng Shui), detection scripts, and patching…
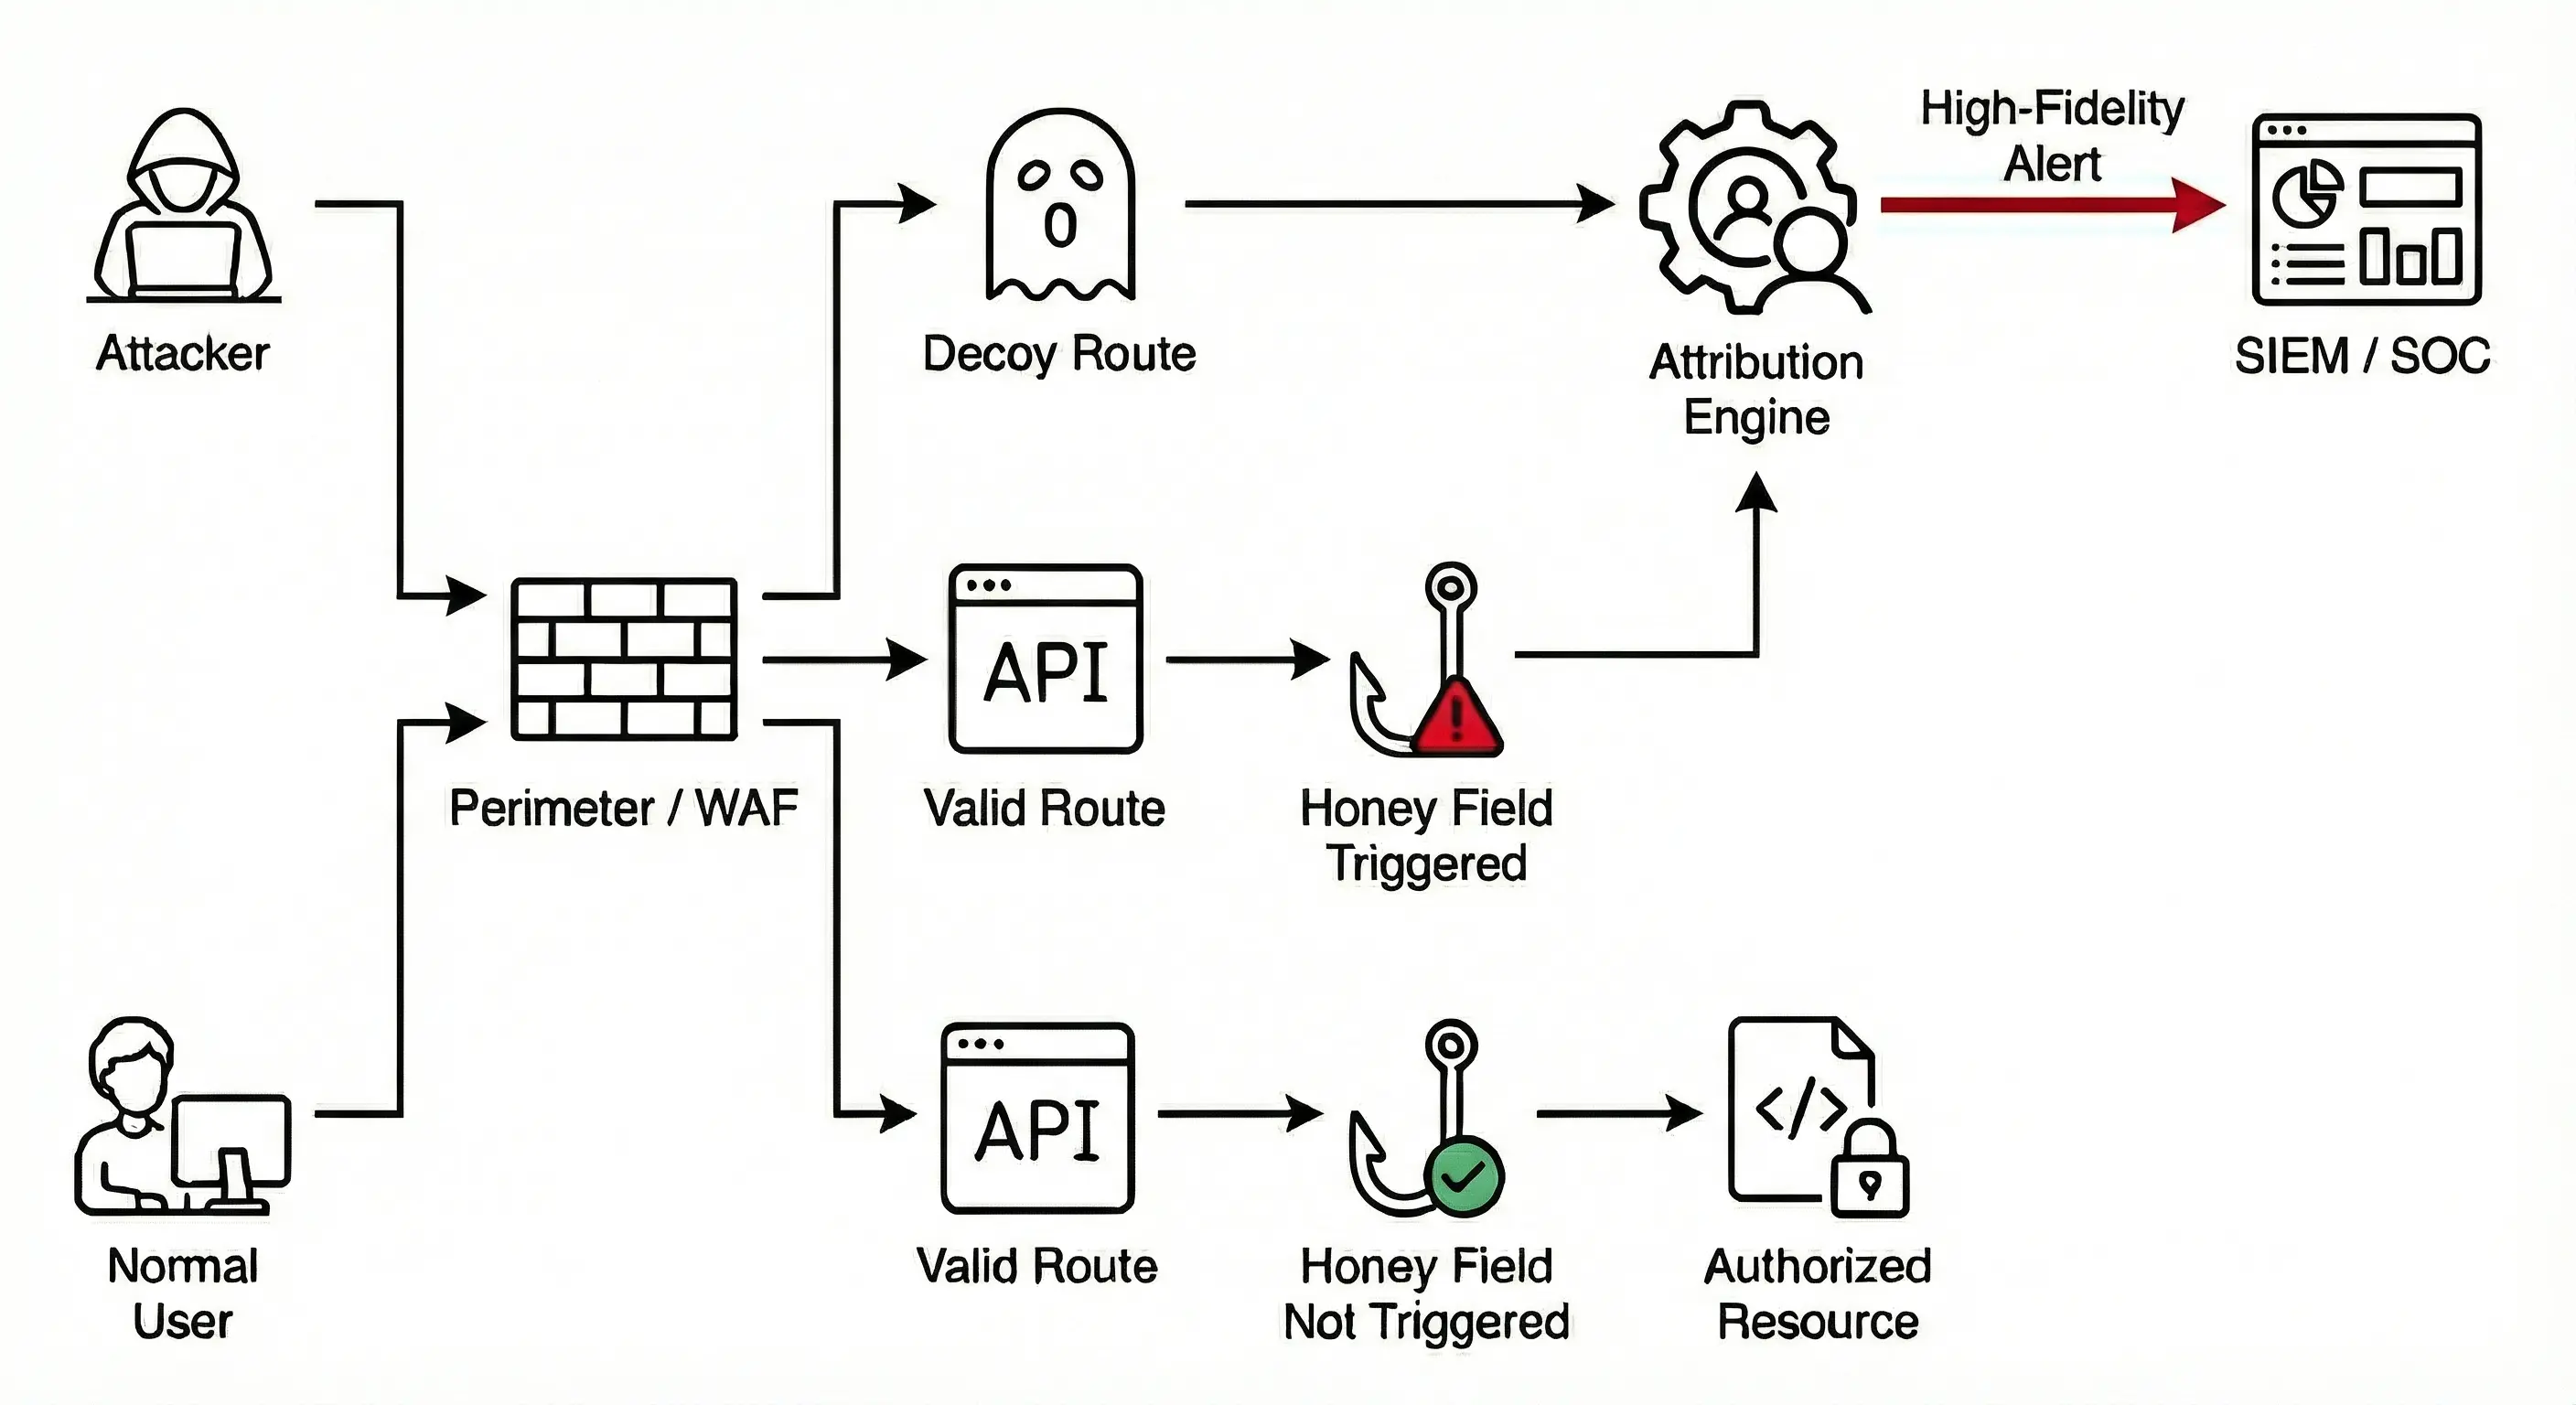 trappsec-dev/trappsec
Open-source framework for embedding realistic decoy routes and honey fields into APIs to detect attackers probing business logic, converting…