
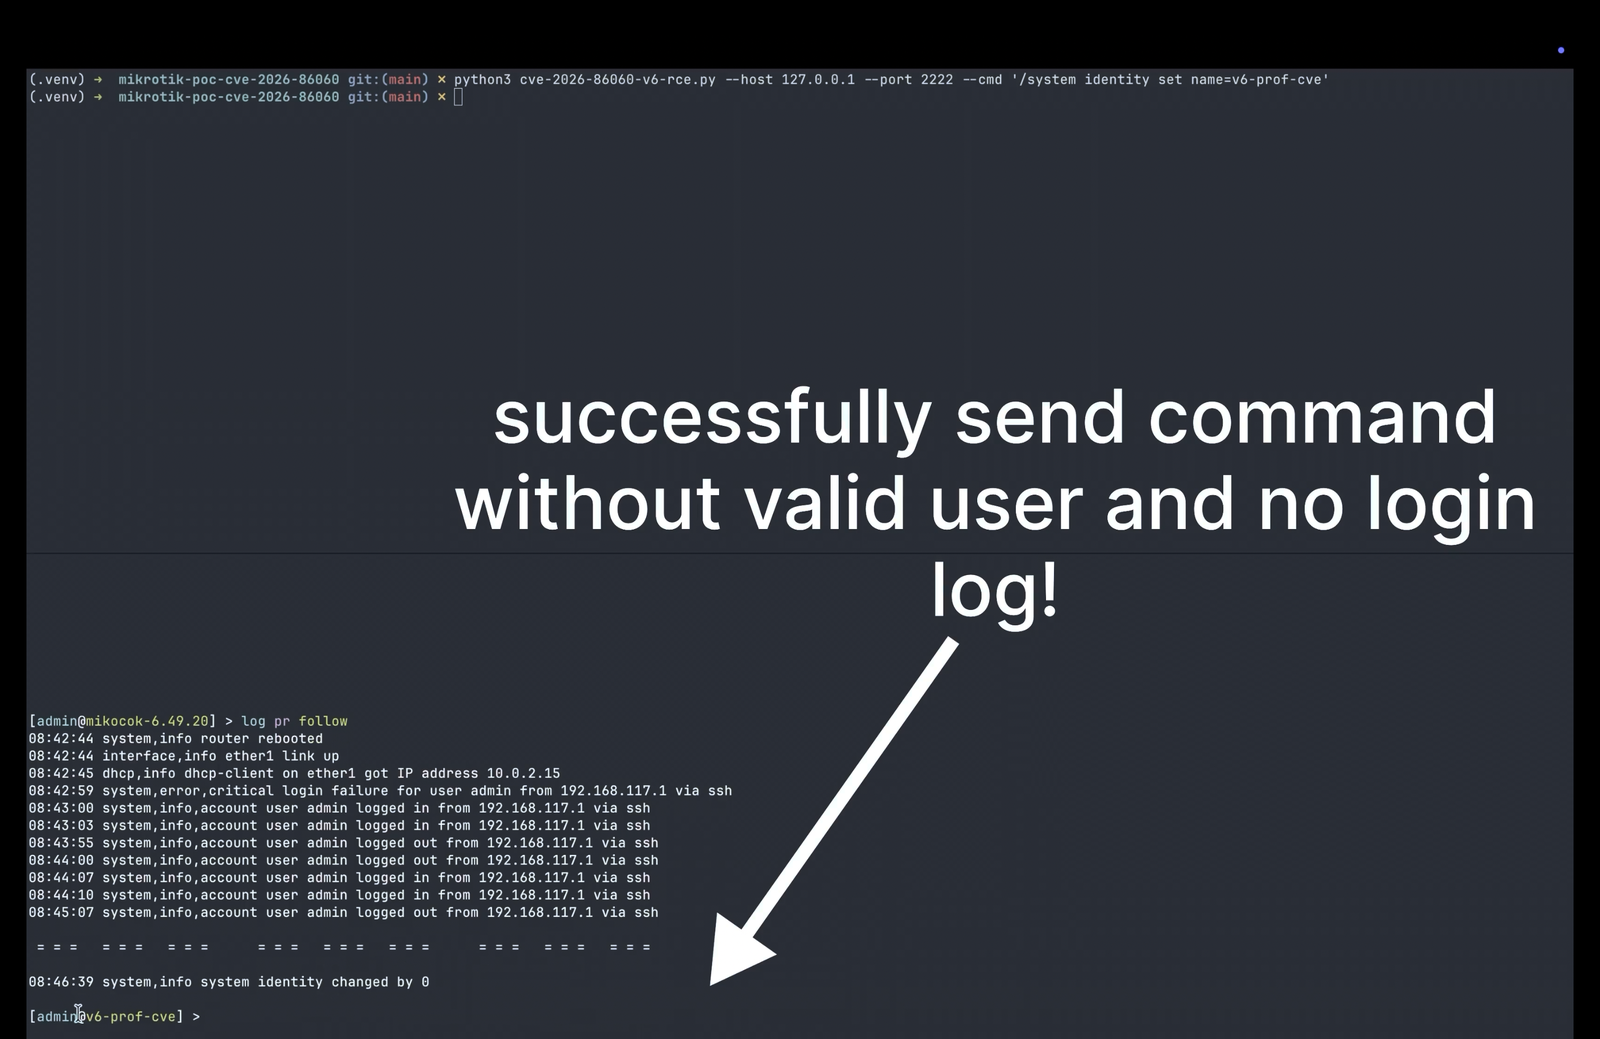
cve-2026-86060
 bahirul/cve-2026-86060
Advisory for CVE-2026-86060, a critical pre-auth privilege escalation in MikroTik RouterOS SSH, with impact analysis, detection guidance, and…
defensive-toolsembedded-systems-securityexploitation+4
bahirul/cve-2026-86060Advisory for CVE-2026-86060, a critical pre-auth privilege escalation in MikroTik RouterOS SSH, with impact analysis, detection guidance, and…
 badrrx/wifi-spiderweb
An active cyber defense & honeypot system for OpenWrt routers running from a USB drive.
 joaoreis13/flight-risk
Security toolkit for CVE-2025-55182 (React2Shell) — scan, detect, correlate, and test React Server Components RCE vulnerability
 logesh-git001/cve-2025-55182
"One crafted HTTP request can compromise your entire server." — React Security Team, Dec 2025
 rewantchaudhari/nextjs-rce-incident-response
Real-world incident response for CVE-2025-55182 (React2Shell) — script injection, server remediation, and post-incident report
 adityabhatt3010/react2shell-cve-2025-55182-the-deserialization-bug-that-broke-the-web
React2Shell, CVE-2025-55182, RCE Vulnerability: A critical breakdown of the unsafe deserialization flaw in React Server Components that enables…
 moisestapia/http-react2shell
Detection of the React Server Actions Exploit vector – CVE-2025-55182 / CVE-2025-66478
 rocklambros/react2shell_hunter
AWS Organization-wide detection toolkit for CVE-2025-55182 & CVE-2025-66478 (React Server Components / Next.js RCE vulnerabilities)
 ngvcanh/cve-2025-55182-attack-analysis
Real-world attack analysis of CVE-2025-55182 (React2Shell) - React Server Components RCE vulnerability
 keysau/get-log4j-windows.ps1
Identifying all log4j components across all windows servers, entire domain, can be multi domain. CVE-2021-44228
 authomize/log4j-log4shell-affected
Lists of affected components and affected apps/vendors by CVE-2021-44228 (aka Log4shell or Log4j RCE). This list is meant as a resource for security…