

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
30 results
mvt preview

mvt

GitHubmvt-project/mvt

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
android-securitydigital-forensicsdisk-forensics+7
14.4k
1 day ago
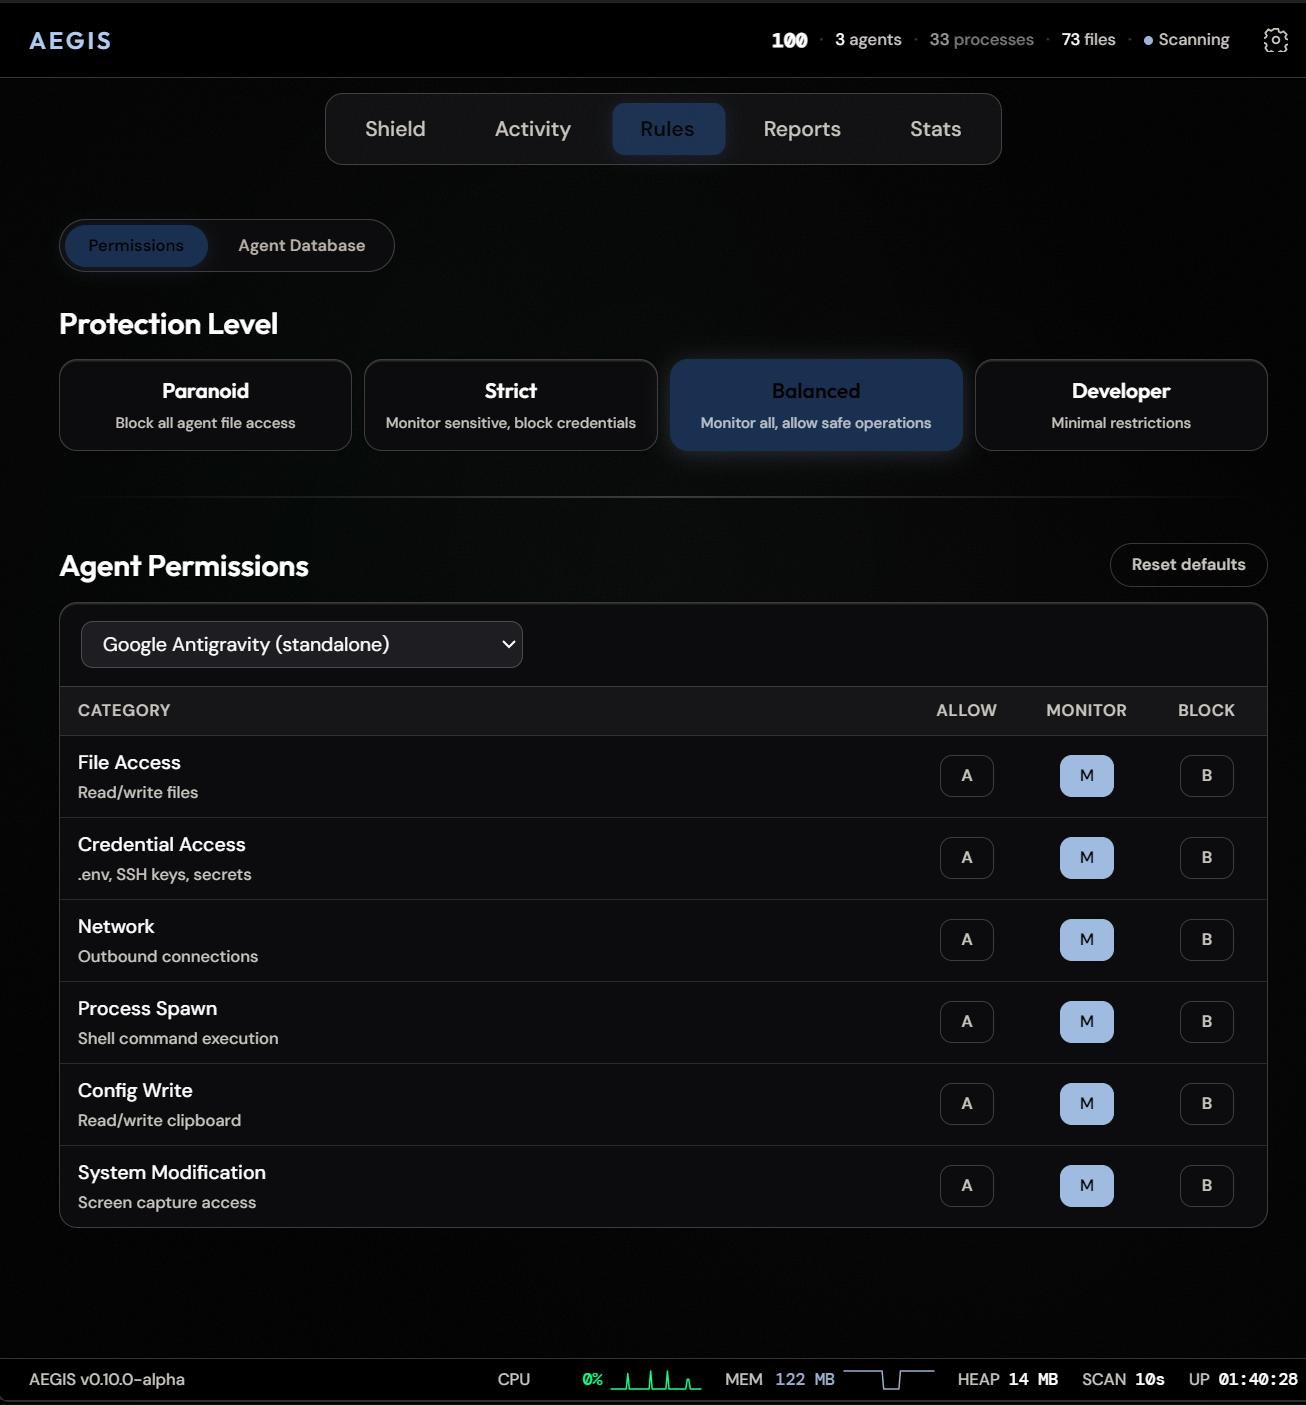
Aegis preview

Aegis

GitHubantropos17/aegis

Desktop monitoring and local security reviews for AI agents, with opt-in policy-controlled execution and MCP action tools. Windows primary;…

ai-securityanomaly-detectiondefensive-tools+4
1522 days ago
sandbox-runtime preview

sandbox-runtime

GitHubanthropic-experimental/sandbox-runtime

A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
configuration-auditingcontainer-securitydefensive-tools+4
5.3k2 days ago
regipy preview

regipy

GitHubmkorman90/regipy

Regipy is an os independent python library for parsing offline registry hives
digital-forensicsforensicsincident-response+1
27710 days ago
CVE-2026-73570 preview

CVE-2026-73570

GitHubhainhc/cve-2026-73570

Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…
email-securityexploitationincident-response+3
14 days ago
Linux-Kodachi preview

Linux-Kodachi

GitHubwmal/linux-kodachi

Hardened Debian-based privacy OS with pre-integrated anonymity stack (Tor, VPN, DNSCrypt), anti-forensic tooling, SOC security center, and standalone…
cryptographydigital-forensicseducation+9
49915 days ago
androidqf preview

androidqf

GitHubmvt-project/androidqf

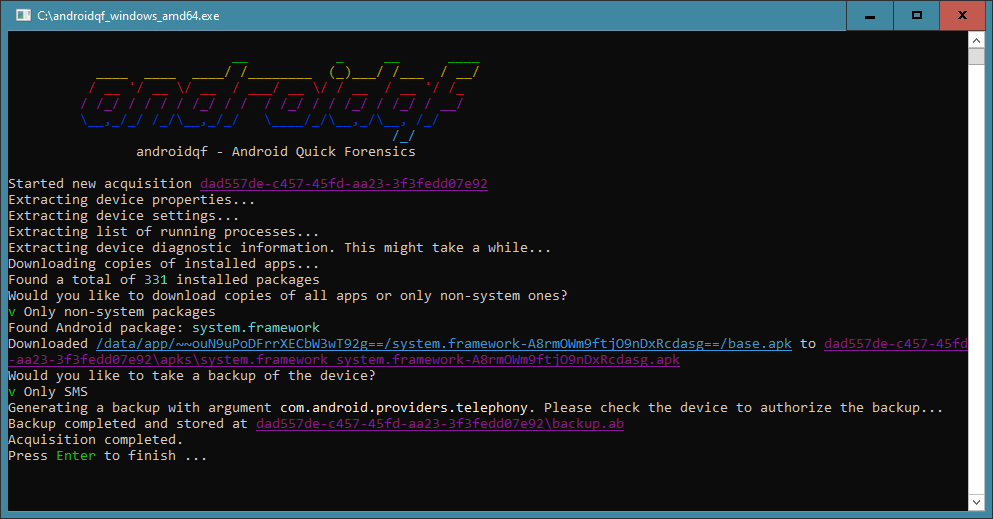
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
android-securitydata-recoverydigital-forensics+4
29822 days ago
Credential-Hunting preview

Credential-Hunting

GitHubnecr00/credential-hunting

CredsHunter - Credential Hunting scripts for Windows and Linux OS

forensicsincident-responseinformation-gathering+7
1831 month ago
OneAlert preview

OneAlert

GitHubmangod12/onealert

AI-powered SOC for OT/ICS networks — 6 autonomous agents, MITRE ATT&CK mapping, Suricata/Zeek ingestion, human-in-the-loop response, 330+ tests.…

ai-securityincident-responsenetwork-security+1
341 month ago
CVE-2026-25089 preview

CVE-2026-25089

GitHub0xblackash/cve-2026-25089

CVE-2026-25089

command-and-controleducationexploitation+3
33 months ago
Android-rce-analizi preview

Android-rce-analizi

GitHubbfurkanyildiz/android-rce-analizi

Android CVE-2024-0044, 43093, 23706 zafiyet analizi ve PoC lab ortamı
android-securityctfdevsecops+8
23 months ago
cve-checker-2026 preview

cve-checker-2026

GitHubsebinxavi/cve-checker-2026

Multi-OS vulnerability checker for CVE-2026-31431 (Linux kernel) and CVE-2026-41940 (cPanel)
configuration-auditingforensicsincident-response+3
14 months ago
PAN-OS-CVE-2024-3400-Command-Injection-Investigation preview

PAN-OS-CVE-2024-3400-Command-Injection-Investigation

GitHubzedocun/pan-os-cve-2024-3400-command-injection-investigation

Investigation of a PAN-OS CVE-2024-3400 command injection attempt, analyzing payload delivery, internal processing, and execution validation based on…
digital-forensicsincident-responselog-analysis+3
15 months ago
CVE-2025-48593 preview

CVE-2025-48593

GitHublogesh-git001/cve-2025-48593

"A single malicious packet can own your device." — Android Security Team, Nov 2025
android-securitybluetooth-securityeducation+7
75 months ago
fsmon preview

fsmon

GitHubnowsecure/fsmon

Filesystem monitor tool for Linux/Android iOS/macOS

android-securitydigital-forensicsdynamic-analysis-sandboxing+5
1.0k5 months ago
Judge-Jury-and-Executable preview

Judge-Jury-and-Executable

GitHubadamwhitehat/judge-jury-and-executable

A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
database-securitydigital-forensicsdisk-forensics+8
855 months ago
azure-vulnerability-remediation-project preview

azure-vulnerability-remediation-project

GitHubdawnsmithcyber/azure-vulnerability-remediation-project

End-to-end vulnerability management lifecycle on Azure Windows Server 2025. Features OS patching and network-level compensating controls (NSG) to…
cloud-infrastructure-securitycloud-securityconfiguration-auditing+6
15 months ago
autotimeliner preview

autotimeliner

GitHubandreafortuna/autotimeliner

Automagically extract forensic timeline from volatile memory dump

digital-forensicsforensicsincident-response+1
1336 months ago
Previous12Next