
cowrie
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/
defensive-toolsincident-responseinformation-gathering+3
cowrie/cowrieCowrie SSH/Telnet Honeypot https://docs.cowrie.org/
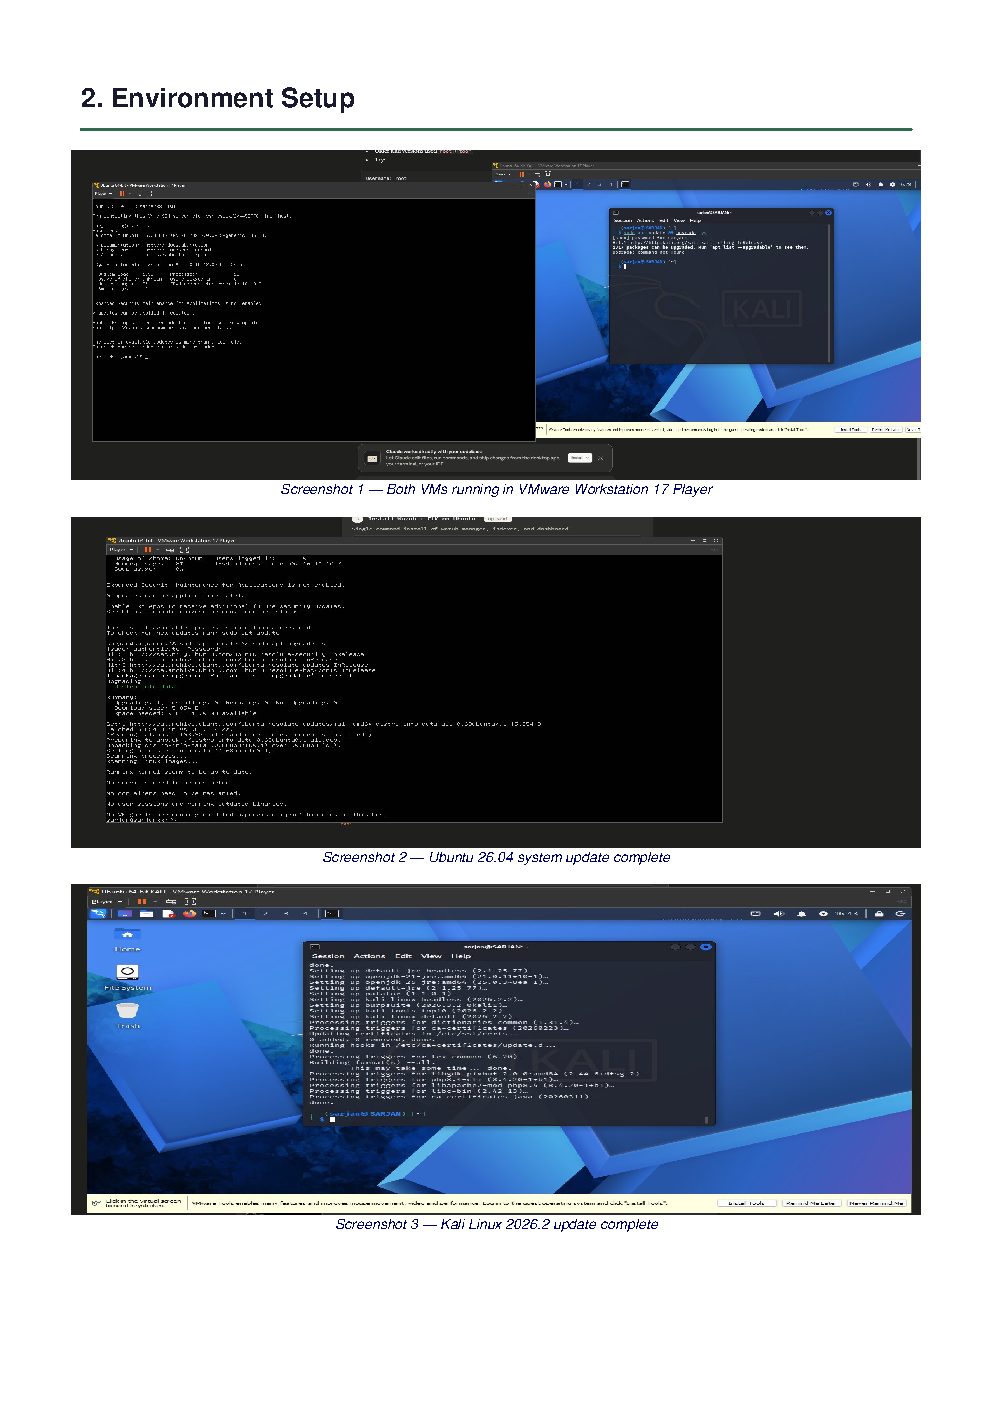 sarjanpatel22/siem-threat-detection-lab
Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…

 password123456/malwarescanner
Hash-based malware scanner for incident response. Scans files recursively using known malware hashes, supports multithreading, extension filtering,…
 castro-ian/cve-2024-4573-mitigation-script
Detects NTLM authentication status by checking LmCompatibilityLevel registry value to assess exposure to CVE-2024-43451 and mitigate credential relay…
 iomoath/filewatchtower
FWT is a security analysis and file monitoring tool that utilizes Sysmon events.
 dave_m/clamtk
An easy to use, light-weight, on-demand virus scanner for Linux systems. For additional help, see the <a…
 ohmyadd/wetland
A high interaction SSH honeypot
 immersive-labs-sec/bruteratel-detectiontools
A collection of Tools and Rules for decoding Brute Ratel C4 badgers
 occamsec/log4j-checker
Bash and PowerShell scripts to scan a local filesystem for Log4j .jar files which could be vulnerable to CVE-2021-44228 aka Log4Shell.
 g0tmi1k/kippo-g0tmi1k
Medium-interaction SSH honeypot that logs brute force attacks and full attacker shell interactions, with customization options to reduce…