

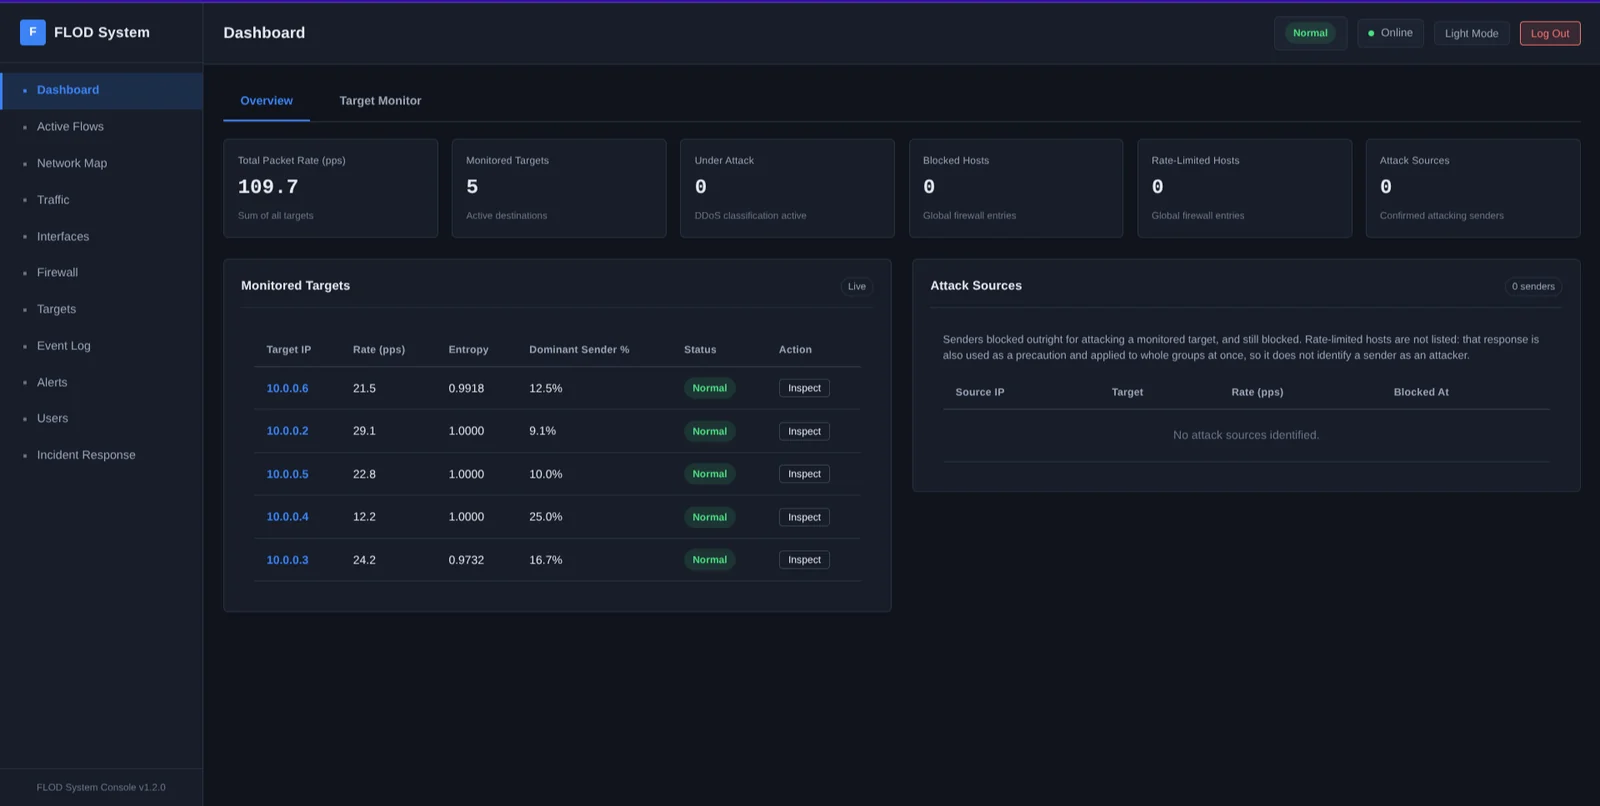
 devinblack001/ddos-reduction-system
Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…
 a2awais/threat-hunting
Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…
 zhoucc-cpu/cve-2023-23397-detection-lab
Detection and mitigation research lab for CVE-2023-23397 using network and endpoint security telemetry.
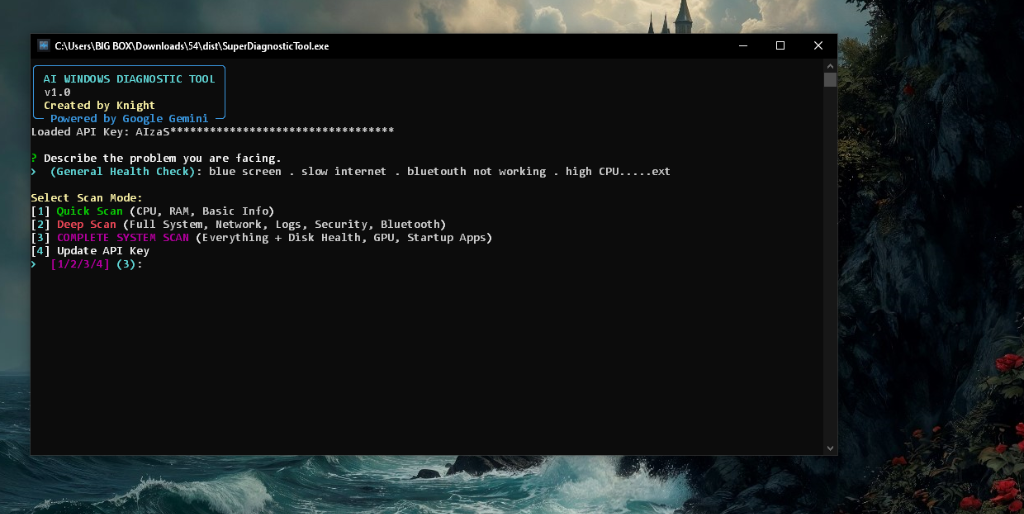 guettaf-hossam/superdiagnostictool
AI-powered Windows diagnostic & auto-repair tool using Google Gemini. Detect crashes, optimize performance, scan for malware, and generate PowerShell…
 withsecureopensource/chainsaw
Rapidly Search and Hunt through Windows Forensic Artefacts
 alloysecuregroup/phantomfs
Windows honeypot using ProjFS to project decoy files that trigger Event Log and desktop alerts when accessed, with SMB remote session logging for…
 aman-sharma-dev/netsentryx
An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
 joertx07/printnightmare-detection-lab
Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…
 0x0allenace/windows-malware-behavioral-analysis
Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…
 jpcertcc/logontracer
Investigate malicious Windows logon by visualizing and analyzing Windows event log
 zavikhttak/follina-msdt-threat-investigation
🔵 Threat analysis writeup for Follina (CVE-2022-30190) — Microsoft MSDT RCE zero-day exploited in the wild. Covers static analysis, VirusTotal,…
 0xsp-srd/aether
Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
 bedrock-safeguard/gentlemen-decryptor
First-ever decryptor for The Gentlemen ransomware — recovers encryption keys from process memory dumps using X25519 ephemeral key extraction. 35/35…
 navya240/intel471-threat-hunting-cve-2023-46604
My first hands-on Intel 471 threat hunting workshop experience investigating CVE-2023-46604 using Elastic SIEM, vulnerability intelligence, and…
 rohitmalik7/cve-2024-38063-detection-mitigation-system
End-to-end cybersecurity project demonstrating detection and mitigation of CVE-2024-38063 using IDS, host-based monitoring, and virtual lab attack…
 ichhyak22/eternalblue-exploit-demonstration-ms17-010
Cybersecurity lab demonstrating exploitation of CVE-2017-0144 (EternalBlue) using Metasploit against a vulnerable Windows 7 VM, achieving…
 v3ng4mxv1p3r/mobile-drop-device-soc-detection
End-to-end simulation of detecting a root-less Android Drop Device (Casper) using Wazuh SIEM to capture Layer 7 attacks like Shellshock…