
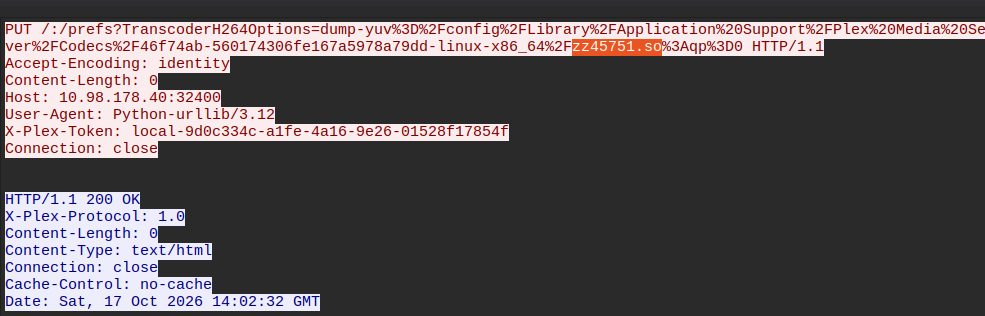
plex2shell_pcap
 boredhackerblog/plex2shell_pcap
Packet capture artifacts of plex2shell exploitation against Plex, including lab and in-the-wild traffic, for building and validating detection…
exploitationincident-responsenetwork-forensics+3
1
boredhackerblog/plex2shell_pcapPacket capture artifacts of plex2shell exploitation against Plex, including lab and in-the-wild traffic, for building and validating detection…
 mceeomoba/apex-kev-change-desk
Offline CISA KEV snapshot comparison for field-level change review. Free prototype, not a security assessment. AI-assisted development.
 techupdate24/fortimail-zero-day-cve-2026-104286
A complete guide and workflow for integrating Agile sprints with DevOps CI/CD pipelines.
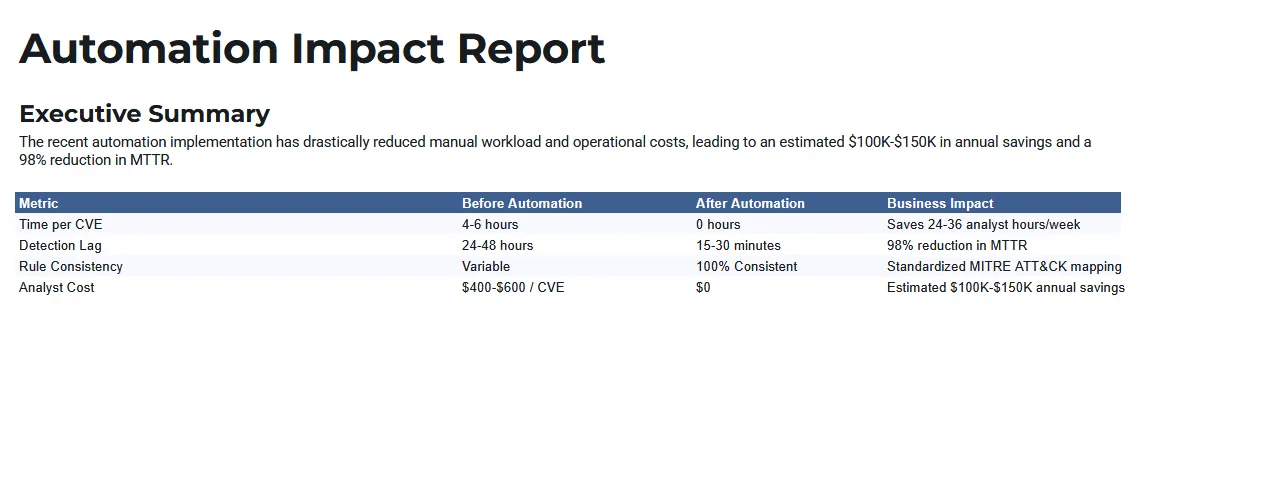 manishrawat21/cisa-kev-threat-intel-orchestrator
Zero-touch pipeline that turns newly weaponized CVEs from the CISA Known Exploited Vulnerabilities (KEV) catalog into production-ready Sigma…
 jwa7470/cve-2026-20131-post-incident-written-report
Post-incident report on CVE-2026-20131 (CVSS 10.0), a Cisco FMC insecure deserialization vulnerability exploited by Interlock ransomware. Details…
 gduma-phdata/patch-cve-2026-31337
Patch: RCE via authentication bypass (Ivanti Connect Secure)
 gopasteverything/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
 zavikhttak/follina-msdt-threat-investigation
🔵 Threat analysis writeup for Follina (CVE-2022-30190) — Microsoft MSDT RCE zero-day exploited in the wild. Covers static analysis, VirusTotal,…
 eyesecurity/wp2shell-compromise-scanner-plugin
Read-only WordPress plugin that scans for artifacts of the wp2shell exploit chain (CVE-2026-63030 / CVE-2026-60137)
 mrrawbit/sonicwall-sma1000-zero-day-ioc-check
Unofficial Bash IoC checker for SonicWall SMA1000 appliances affected by actively exploited CVE-2026-15409 and CVE-2026-15410.
 probablysecure/triage-cve-2021-44228-log4shell-log4j-
Goal is to triage well known attack and learn how security teams quickly respond.
 probablysecure/triage-cve-2017-0144
Goal is to triage well known attacks and learn how security teams quickly respond.
 sentinel-aidefense/cve-2026-21509
CVE-2026-21509 Research writeup
 mahfuzreham/cpanel-cve-2026-41940
cPanel CVE-2026-41940 nuclear.x86 Security Audit & Cleanup Script
 criann/check-cve-2026-23111
Script to check if system are vulnable to cve-2026-23111
 justjeff211/conti-ransomware-writeup
Conducted a full SOC investigation into a Conti ransomware compromise of an Exchange server using Splunk 8.2.2. Analysed 28,145 events across Windows…
 mrk336/inside-cve-2026-20805-how-a-windows-dwm-flaw-exposed-sensitive-data
CVE‑2026‑20805: A Windows Desktop Window Manager flaw causing local information disclosure. Requires low privileges, no user interaction. Rated CVSS…
 mrk336/kernel-chaos-weaponizing-cve-2025-62215-for-system-privilege-escalation
Hands‑on analysis of CVE‑2025‑62215, a Windows Kernel race condition exploited in the wild. Demonstrates privilege escalation to SYSTEM, detection…