
ti-a-ti-cveexploitchecker
 shadowguardai/ti-a-ti-cveexploitchecker
Determines if public exploits are available for a given CVE. Uses APIs like exploit-db or NVD to ide
incident-responseinformation-gatheringioc-management+5
shadowguardai/ti-a-ti-cveexploitcheckerDetermines if public exploits are available for a given CVE. Uses APIs like exploit-db or NVD to ide
 phpatch/weblogchecker
Free access-log compromise analyzer: webshell interactions, exploitation patterns and brute-force bursts in your Apache/nginx logs - severity,…
 drb-ra/c2intelfeeds
Automatically generated C2 threat intelligence feeds of IPs, domains, URL paths, and implant configuration metadata, derived from internet scanning…
 dshield-isc/dshield
Installs and configures a DShield honeypot sensor on Raspberry Pi or Ubuntu, running Cowrie SSH and HTTP honeypots and forwarding firewall logs to…
 0xajstrike/opcuatrap
High-interaction OPC UA honeypot for ICS/SCADA — multi-profile (oil & gas, water, power grid), live process simulation, per-session threat scoring,…
 0x4d31/honeypot-data
Public honeypot datasets and observation reports with HTTP/TLS fingerprint data (JA3/JA4), pseudonymized source IPs, and exploitation attempt…
 jaksi/sshesame
An easy to set up and use SSH honeypot, a fake SSH server that lets anyone in and logs their activity
 fazmin/cve-intel
Local security intelligence for CVE triage - 40 data sources and 41 tools, risk scores and an MCP server for AI agents, all in native Rust. Private…
 opencti-platform/connectors
Collection of OpenCTI connectors that ingest and synchronize threat intelligence, IOCs, and CTI data from external sources like MISP and MITRE ATT&CK…
 watchtowrlabs/citrix-netscaler-cve-2026-88771-iocs
Indicators of Compromise and hunting guidance for CVE-2026-88771, an unauthenticated command injection in Citrix NetScaler ADC and Gateway, covering…
 confused-binary/waf-fu
Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
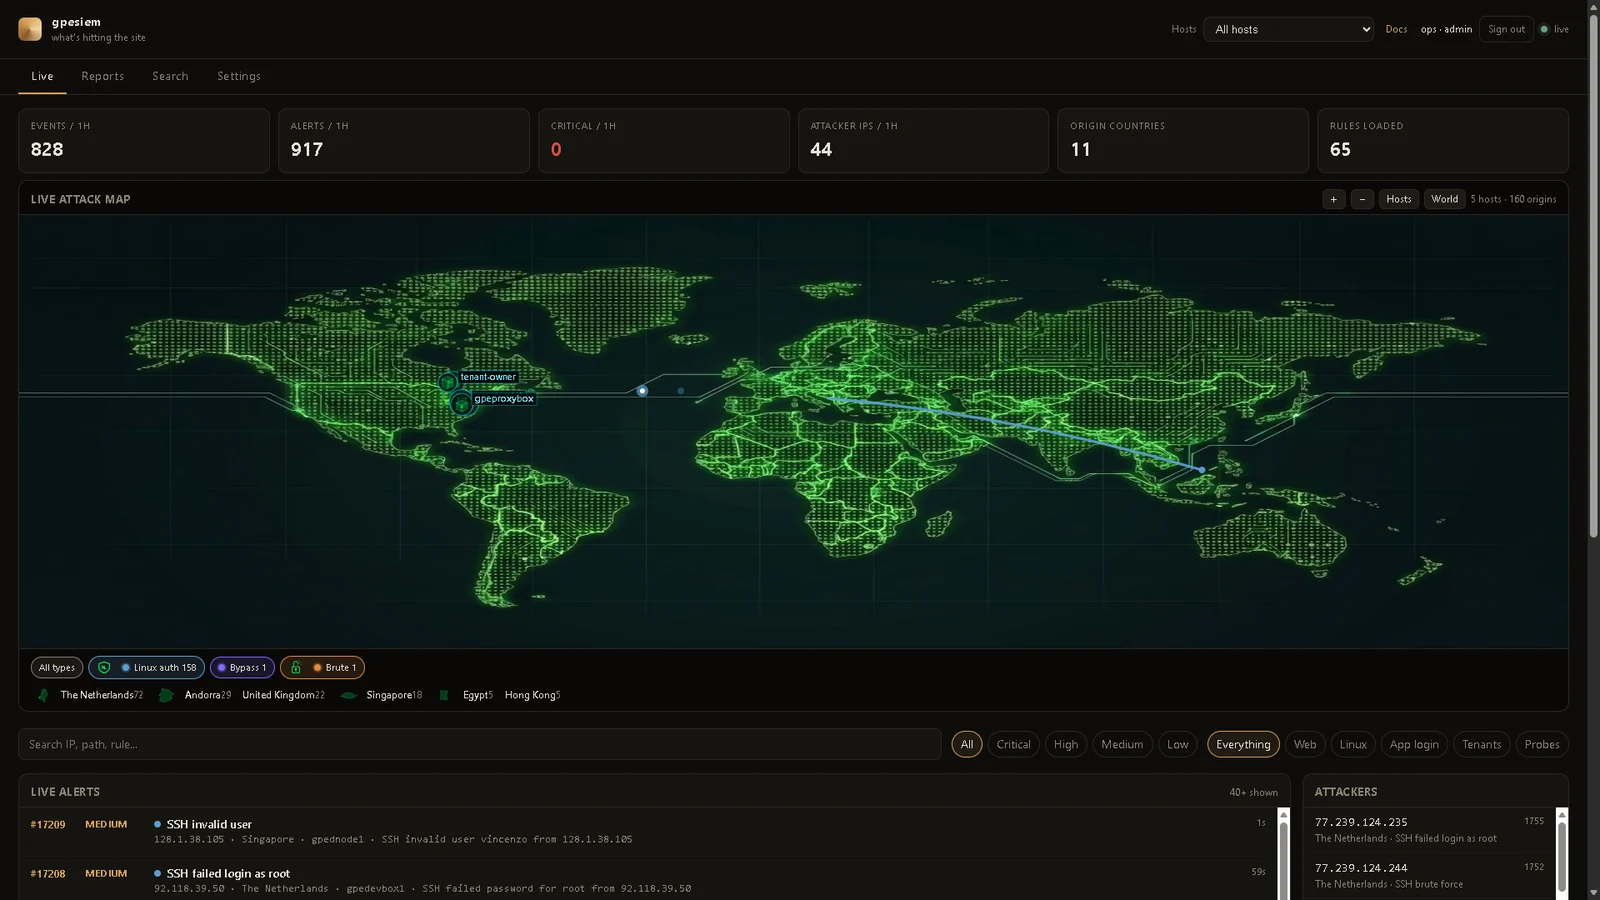 gopasteverything/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
 niffyhunt/wraithwall-toolkit
Deception-engineering tools pulled from a production platform that takes live attacker traffic, supply-chain canary tokens, honeypot logs → MITRE…
 wadesweaponshed/cve-2026-93616_checks
Shell and SmartDashboard scripts that check Check Point management servers for indicators of compromise tied to CVE-2026-93616, including rogue…
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 duggytuxy/data-shield_ipv4_blocklist
Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
 jithinkrishnanrs/gitlab-cve-2026-85706-ioc
CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…