
hotcell
 msuiche/hotcell
Runtime exploit monitor for Apple document/image pipelines (iOS/macOS) — EXPMON concept: Frida agent + behavioral rules. First target: the…
binary-analysisdefensive-toolsdynamic-analysis-sandboxing+7
10
msuiche/hotcellRuntime exploit monitor for Apple document/image pipelines (iOS/macOS) — EXPMON concept: Frida agent + behavioral rules. First target: the…
 alvaroguzmancode/cve-2026-99999
Spanish guide and Bash script to check whether a Linux host is exposed to CVE-2026-99999 (PwnEscape) VM-to-host kernel escape, with patch…
 zombiepm/cve-2026-98432-mitigation
Interim nftables mitigation for CVE-2026-98432, automatic rollback and Russian administrator guide. Not a kernel patch.
 xxhjkl/cve-2026-98432-check
Read-only Linux kernel checker for CVE-2026-98432 that detects vulnerable or unpatched kernels, flags reboot-required states, and offers optional…
 igreklg/cve-2026-98432-mitigation
Audits Debian/Ubuntu kernels for CVE-2026-98432 and applies persistent nftables and sysctl mitigations, then guides kernel upgrade and rollback.
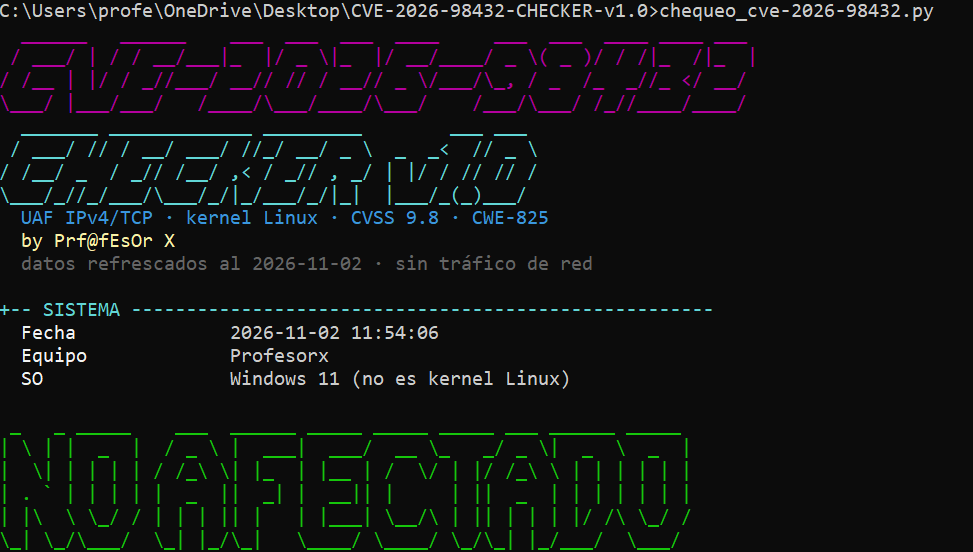 pr0fes0r-x/cve-2026-98432-checker-v-1.0-
El script hace una revisión de tu Linux frente a esa vulnerabilidad, sin tocar nada por defecto: osea mira tu kernel — lee tu versión real de Linux…
 mchorfa/csumguard
Restricted eBPF TC ingress guard, CO-RE detector, verified loader, and C11 VMM launch supervisor for CVE-2026-99999
 kingahmadr/cve-2026-99999-kernel-check
Checks Linux KVM hosts for CVE-2026-99999 kernel exposure, identifies fixed kernel targets, and scans many hosts over SSH with JSON/CSV reports.
 quaerendir/cve-2026-99999-audit
Read-only Bash audit script that triages CVE-2026-99999 (PwnEscape) Linux kernel IPv4 checksum OOB write, checking patch status, module reachability,…
 sqzer-x/cve-2026-99999-scanner
Checks whether a Linux system is affected by CVE-2026-99999 (PwnEscape) and prints or applies the distribution-specific kernel fix
 mc493/kshield
Emergency Zero-Downtime Linux Kernel Defense & Attack-Surface Disarmer. Active hotpatching for CVE-2026-98432 (MPTCP RCE), CVE-2024-1086,…
 quaerendir/cve-2026-98432-audit
Read-only bash audit script that triages CVE-2026-98432, a Linux kernel IPv4 TCP use-after-free, by checking kernel changelogs, distro fix matrices,…
 typhoon1217/cve-2026-98432-mitigation
Temporary mitigation for CVE-2026-98432 (Linux IPv4 TCP ireq_opt use-after-free): drop IPv4 TCP with IP options, disable MPTCP. Tested scripts +…
 axisops/cve-2026-98432
Ansible role and Python script that detect Linux kernel exposure to CVE-2026-98432 and apply an nftables rule dropping inbound IPv4 SYNs carrying IP…
 maxigentr/netviser-linux-security-auditor
Read-only, agentless Linux kernel security configuration auditor (local & SSH). Initial focus: TCP migration / MPTCP checks for CVE-2026-98432.
 mahdi-salmanzade/cve-2026-98432
Guide and read-only check script for CVE-2026-98432, a Linux IPv4 TCP use-after-free: detect kernel patch status, apply an iptables stopgap, and…
 fbuff-tools/cve-2026-98432-checker
Check a Linux server for CVE-2026-98432 (IPv4 TCP use-after-free, CVSS 9.8): root cause explained, read-only check script and mitigations.
 scriptzteam/paranoid-cve-2026-98432
Drop incoming IPv4 TCP packets whose IP header contains options.