
ADRecon
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
defensive-toolsdigital-forensicsincident-response+6
981
adrecon/adreconPowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
 withsecurelabs/esfang
ESF modular ingestion tool for development and research.
 jacobideji/aiiroverlay
AI IR Overlay™ — practical incident response framework for AI agents in production. Built on NIST SP 800-61 r3, mapped to NIST AI RMF, NIST CSF 2.0,…
 mahdi13830510/cve-2026-31431-mitigation-suite
Kernel-runtime defense framework for AF_ALG vulnerabilities, featuring eBPF socket tracing, Ansible hardening, and a crypto auditor for drift…
 kacos2000/evtx_log_browser
Evtx Log (xml) Browser
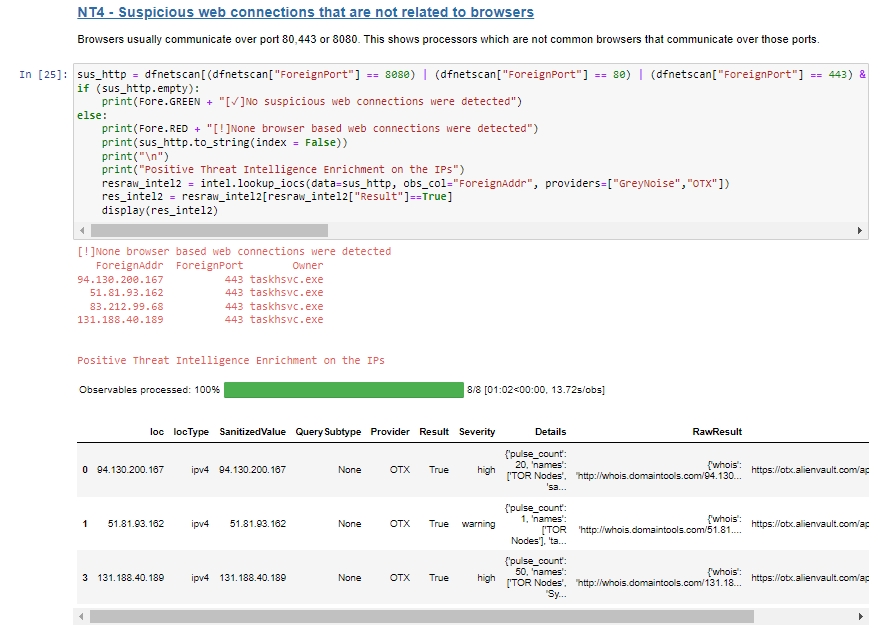 blueteam0ps/memoptix
A Jupyter notebook to assist with the analysis of the output generated from Volatility memory extraction framework.
 facebookincubator/ttpforge
The TTPForge is a Cybersecurity Framework for developing, automating, and executing attacker Tactics, Techniques, and Procedures (TTPs).
 theevidencehunter/forensix
Digital Forensics Intelligence Framework
 corelight/c2-detection-manjusaka
Detection of Manjusaka C2 framework
 owasp/python-honeypot
OWASP Honeypot, Automated Deception Framework.
 nerium-security/cve-2025-55182
Host-based detection rules for the RCE vulnerability in the React JavaScript framework.
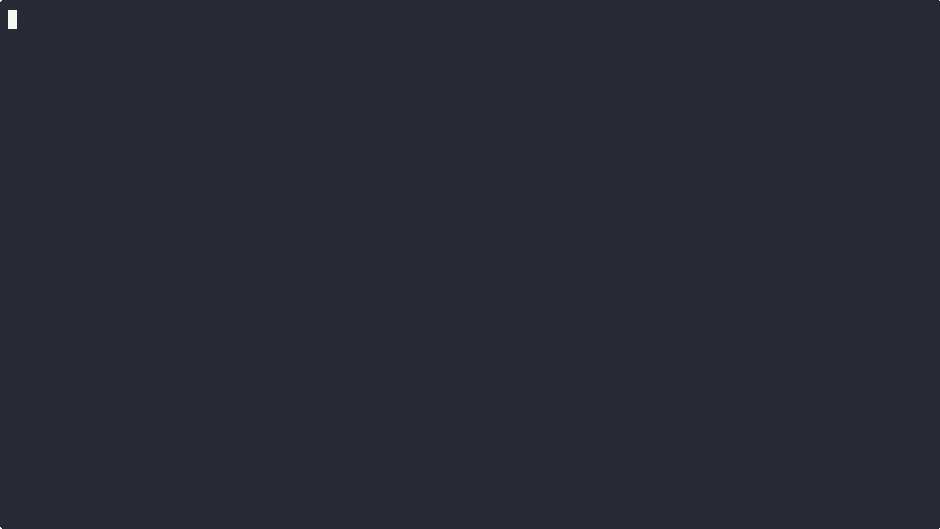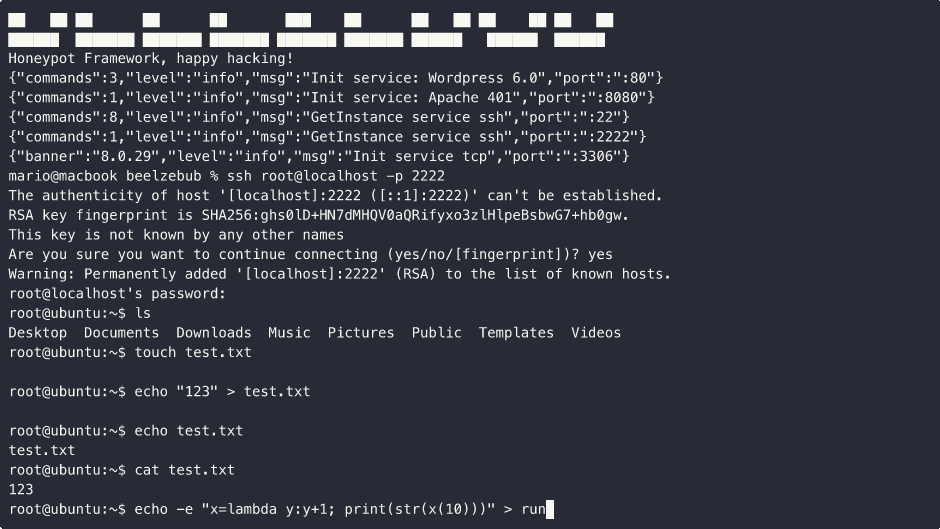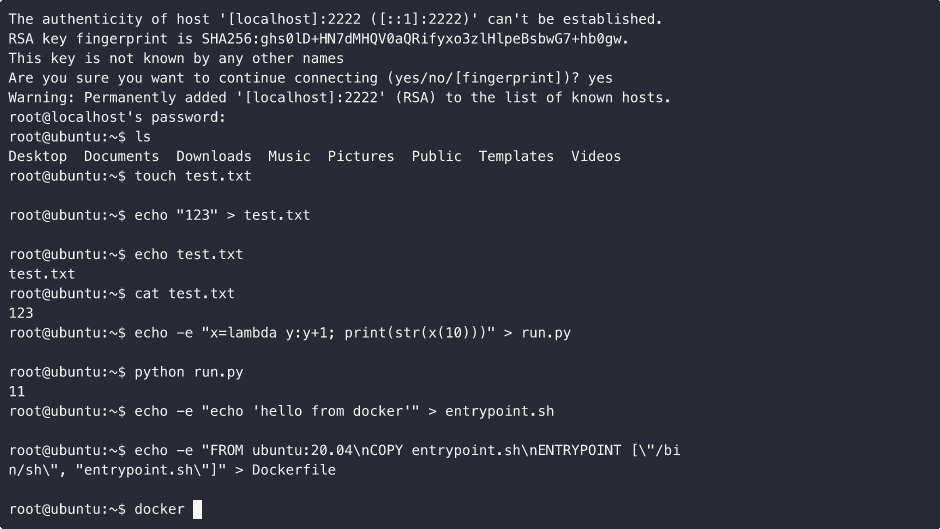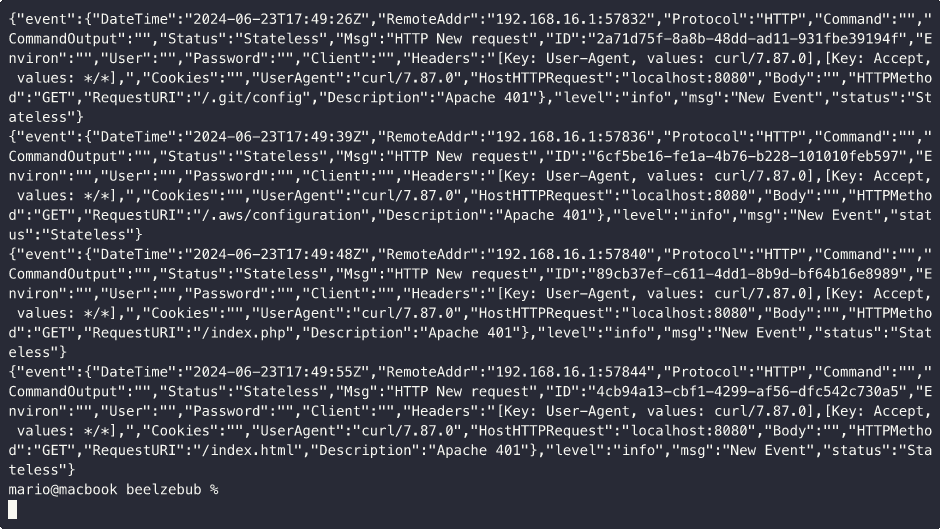 beelzebub-labs/beelzebub
A secure low code deception runtime framework, leveraging AI for System Virtualization.
 daryllundy/cve-2025-32463
Detection framework for CVE-2025-32463 sudo privilege escalation vulnerability. Provides real-time monitoring, forensic analysis, and SIEM…
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…
 nebulock-inc/agentic-threat-hunting-framework
ATHF is a framework for agentic threat hunting - building systems that can remember, learn, and act with increasing autonomy.
 nightfullstar/openclaw-defender
Multi-layer security framework for AI agent ecosystems. Provides pre-installation skill auditing, file integrity monitoring, runtime protection, and…
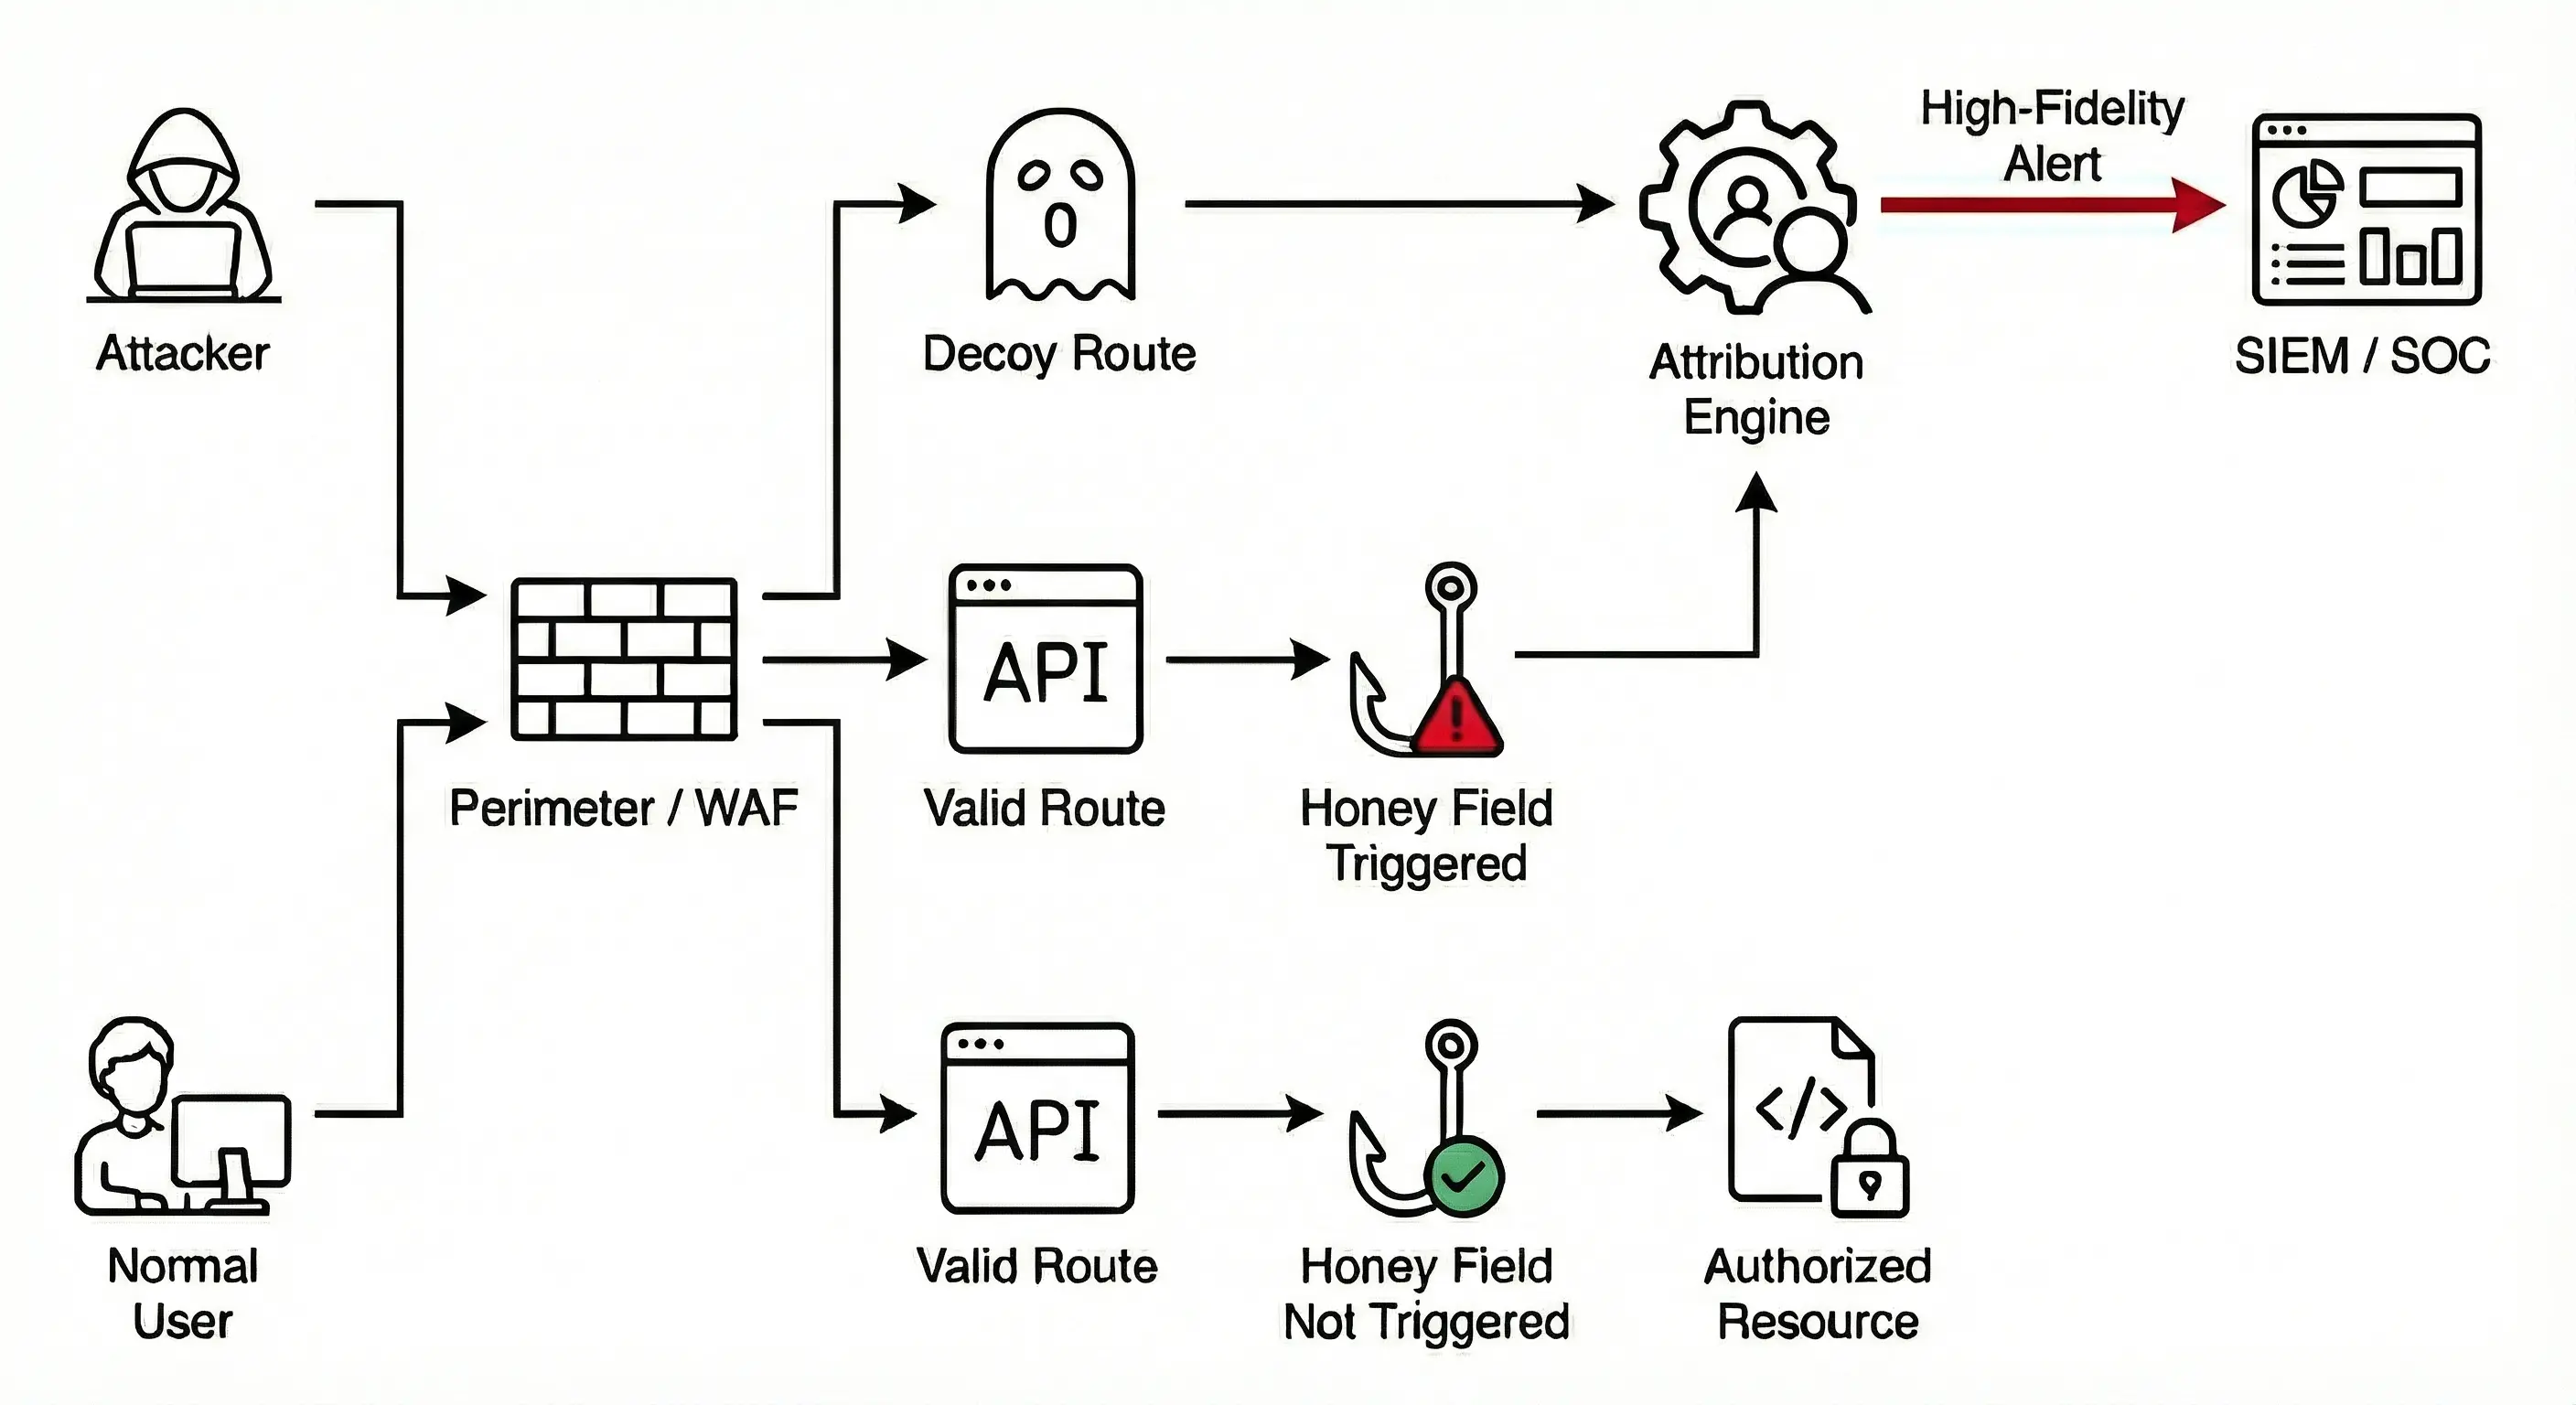 trappsec-dev/trappsec
Open-source framework for embedding realistic decoy routes and honey fields into APIs to detect attackers probing business logic, converting…