FLAIR
 withsecurelabs/flair
Lightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…
digital-forensicsforensicsincident-response+2
16
withsecurelabs/flairLightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…
 randomaccess3/awesome-bec
Repository of attack and defensive information for Business Email Compromise investigations
 rtfmkiesel/loldrivers-client
Scan your Windows computer for known vulnerable or malicious drivers.
 jonny-jhnson/ldapmon
Proof-of-concept telemetry collector for Windows LDAP client activity via ETW, logging structured events to Event Viewer with a Sentinel parser for…
 pduggusa/redis-cve-2026-23479-check
Safe read-only version checker + Sigma rule for Redis CVE-2026-23479 (authenticated use-after-free → RCE). Find exposed instances, patch…
 sentinel-aidefense/cve-2025-33073
CVE-2025-33073 Research writeup
 chef-cft/inspec_cve_2019_15224
Example InSpec profile to detect presence of a malicious rest-client gem (CVE-2019-15224)
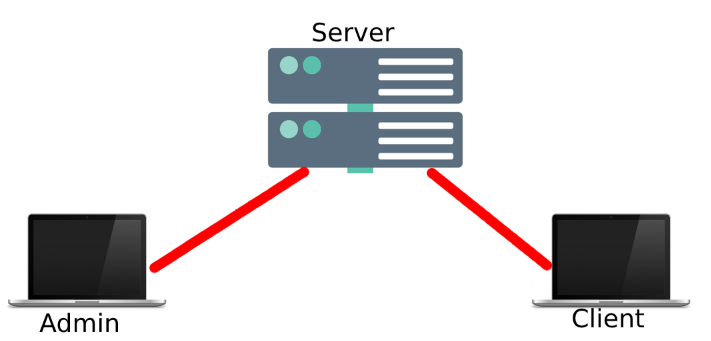 letsdefendio/simple-live-data-collection
Client-server tool for live data collection during incident response. Admin sends requests to clients to gather system information for forensic…
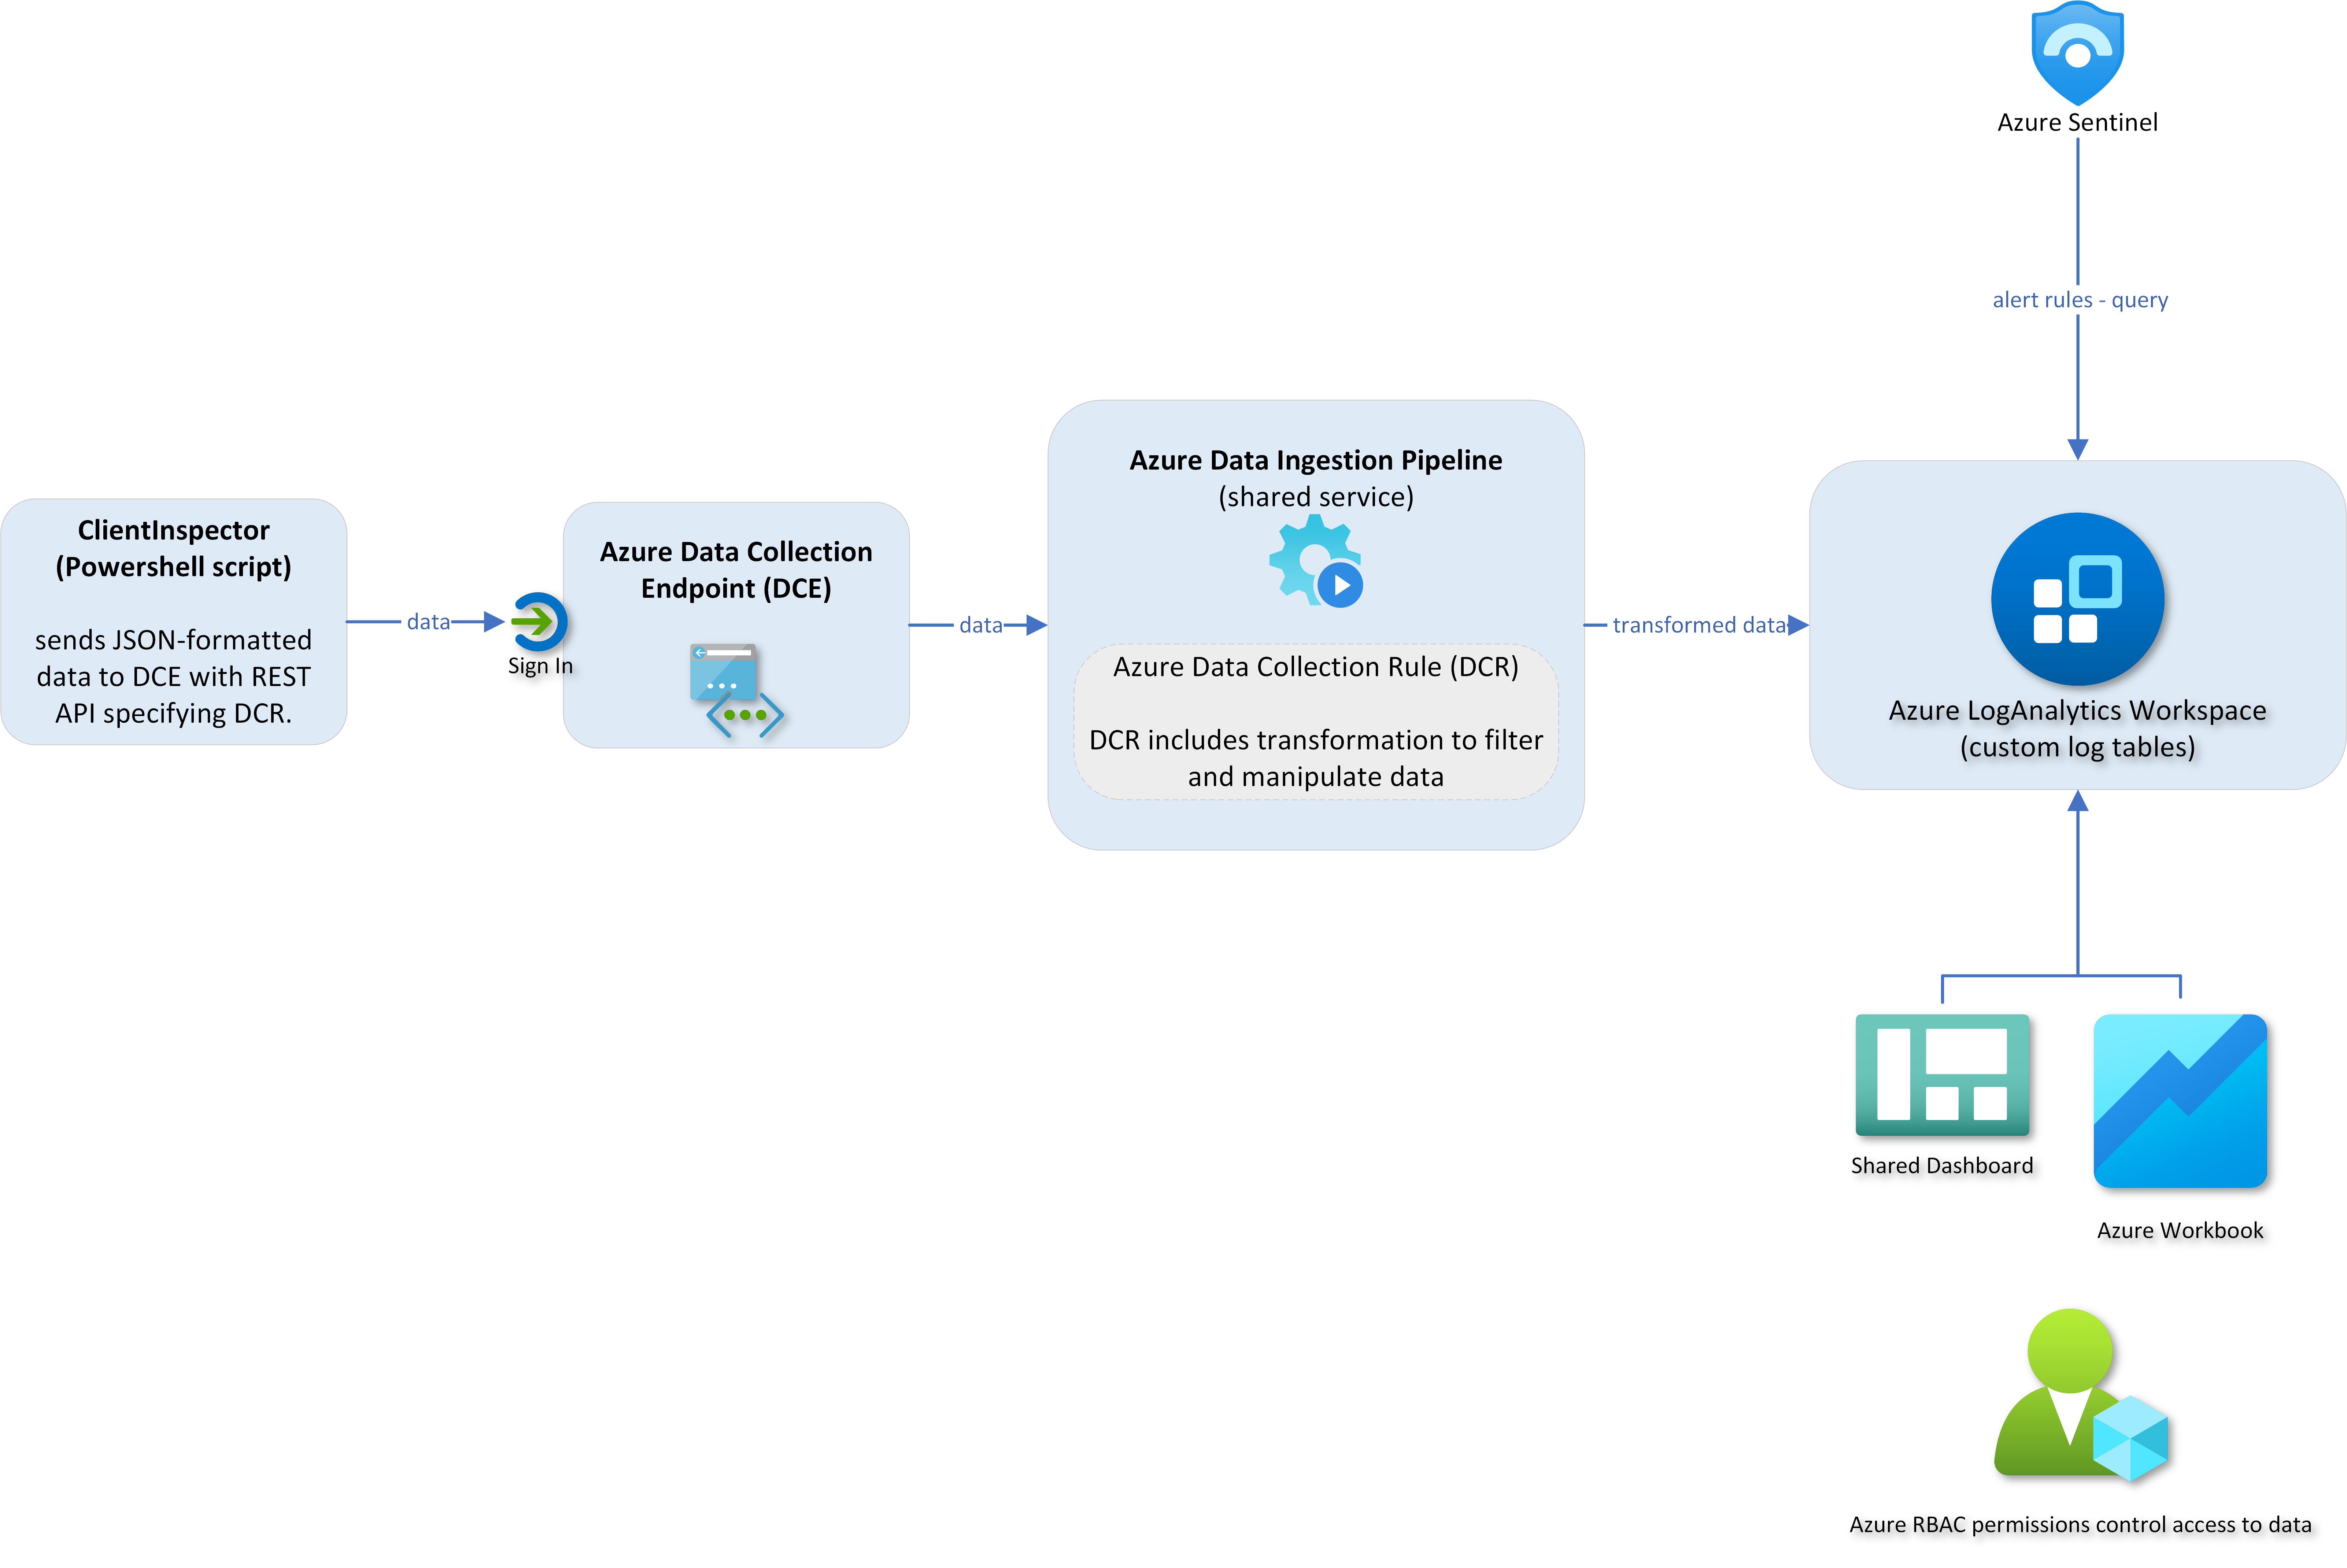 knudsenmorten/clientinspectorv2
Azure-based client inventory and drift detection tool that collects Windows configuration data (antivirus, patching, Bitlocker) into LogAnalytics for…