
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
84 results
cowrie preview

cowrie

GitHubcowrie/cowrie

Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/

defensive-toolsincident-responseinformation-gathering+3
6.6k15h 51m ago
ThreatLens preview

ThreatLens

GitHubabdaullahag/threatlens

Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…

defensive-toolsincident-responseinformation-gathering+7
261 day ago
GPEWebDefender preview

GPEWebDefender

GitHubgopasteverything/gpewebdefender

Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.

defensive-toolsincident-responseinformation-gathering+8
52 months ago
ThreatIntel-Aggregator preview

ThreatIntel-Aggregator

GitHubethan-andrews/threatintel-aggregator

Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…

ai-securitydefensive-toolsincident-response+7
601 month ago
connectors preview

connectors

GitHubopencti-platform/connectors

Collection of OpenCTI connectors that ingest and synchronize threat intelligence, IOCs, and CTI data from external sources like MISP and MITRE ATT&CK…

defensive-toolsincident-responseinformation-gathering+5
59118h 52m ago
C2IntelFeeds preview

C2IntelFeeds

GitHubdrb-ra/c2intelfeeds

Automatically generated C2 threat intelligence feeds of IPs, domains, URL paths, and implant configuration metadata, derived from internet scanning…

command-and-controldefensive-toolsincident-response+6
7463 days ago
passivedns preview

passivedns

GitHubgamelinux/passivedns

A network sniffer that logs all DNS server replies for use in a passive DNS setup

dns-analysisforensicsincident-response+3
1.7k12 days ago
cve-intel preview

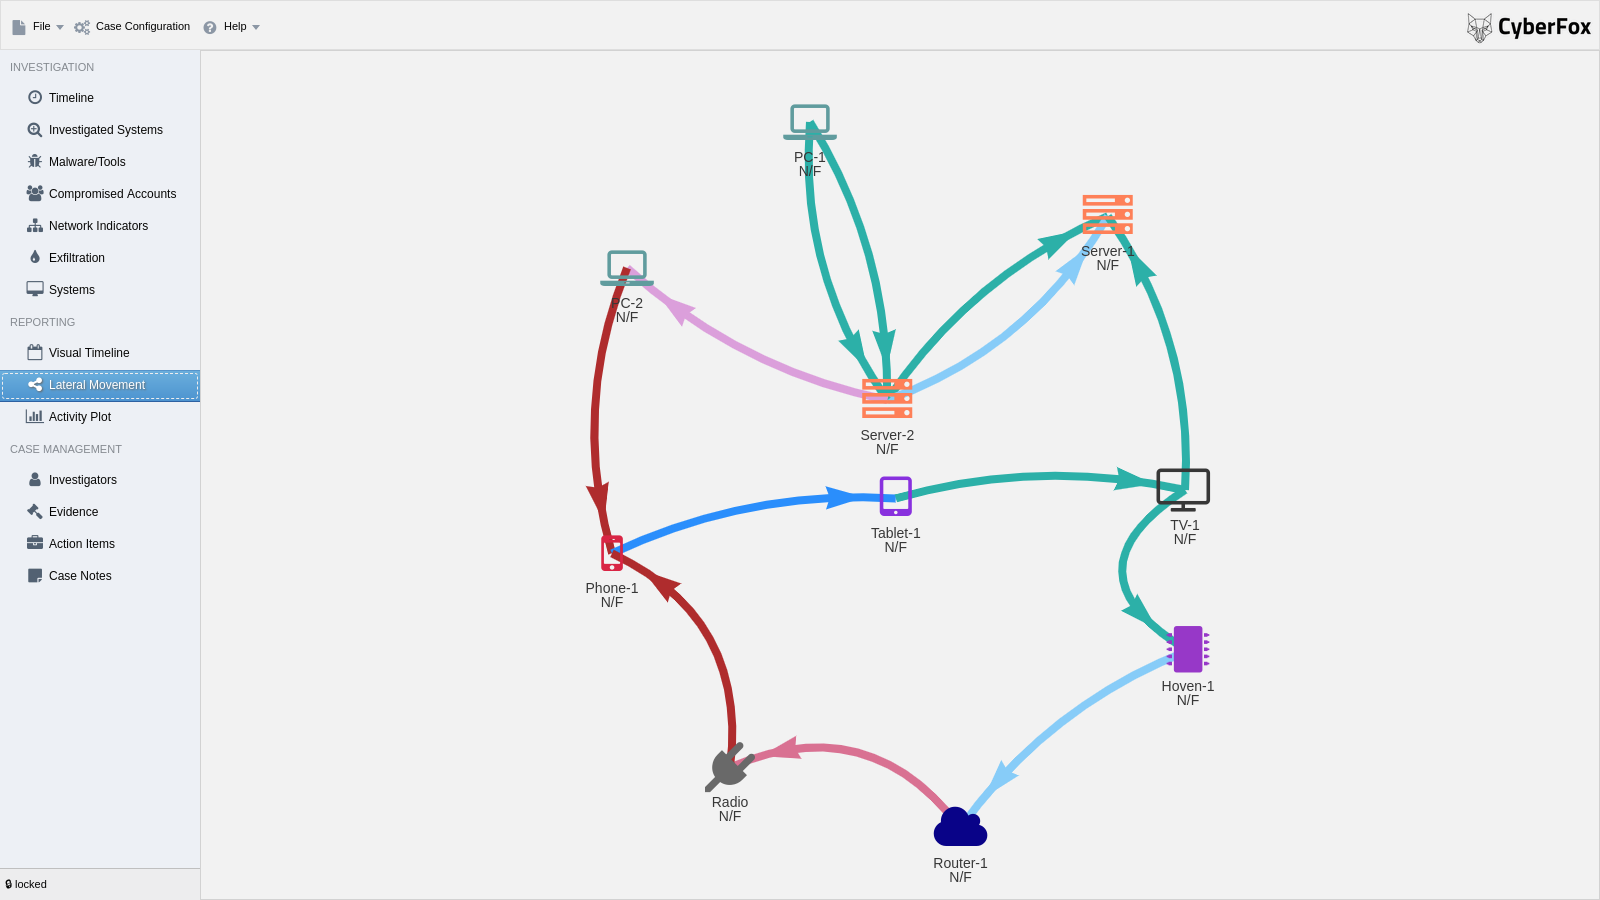
cve-intel

GitHubfazmin/cve-intel

Local security intelligence for CVE triage - 40 data sources and 41 tools, risk scores and an MCP server for AI agents, all in native Rust. Private…
ai-securitydevsecopsincident-response+8
1182 days ago
wraithwall-toolkit preview

wraithwall-toolkit

GitHubniffyhunt/wraithwall-toolkit

Deception-engineering tools pulled from a production platform that takes live attacker traffic, supply-chain canary tokens, honeypot logs → MITRE…
cryptographydefensive-toolsincident-response+4
22 days ago
Aurora-Incident-Response preview

Aurora-Incident-Response

GitHubcyb3rfox/aurora-incident-response

Incident Response Documentation made easy. Developed by Incident Responders for Incident Responders

digital-forensicsforensicsincident-response+3
1.1k4 years ago
Data-Shield_IPv4_Blocklist preview

Data-Shield_IPv4_Blocklist

GitHubduggytuxy/data-shield_ipv4_blocklist

Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…

defensive-toolsincident-responseinformation-gathering+5
62338 minutes ago
ADRecon preview

ADRecon

GitHubadrecon/adrecon

PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
defensive-toolsdigital-forensicsincident-response+6
9892 years ago
MacOSThreatTrack preview

MacOSThreatTrack

GitHubab2pentest/macosthreattrack

Bash tool used for proactive detection of malicious activity on macOS systems.
digital-forensicsincident-responseinformation-gathering+1
401 year ago
SOC-Multitool preview

SOC-Multitool

GitHubzdhenard42/soc-multitool

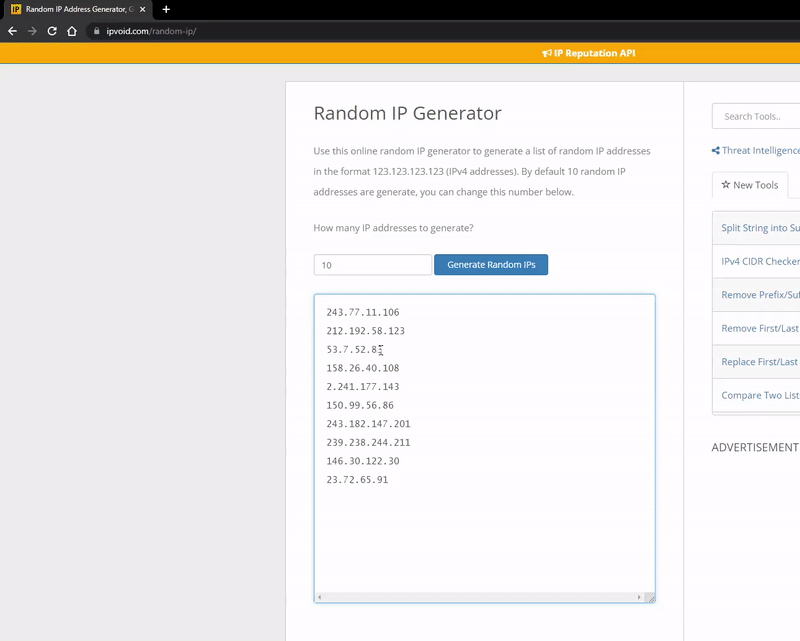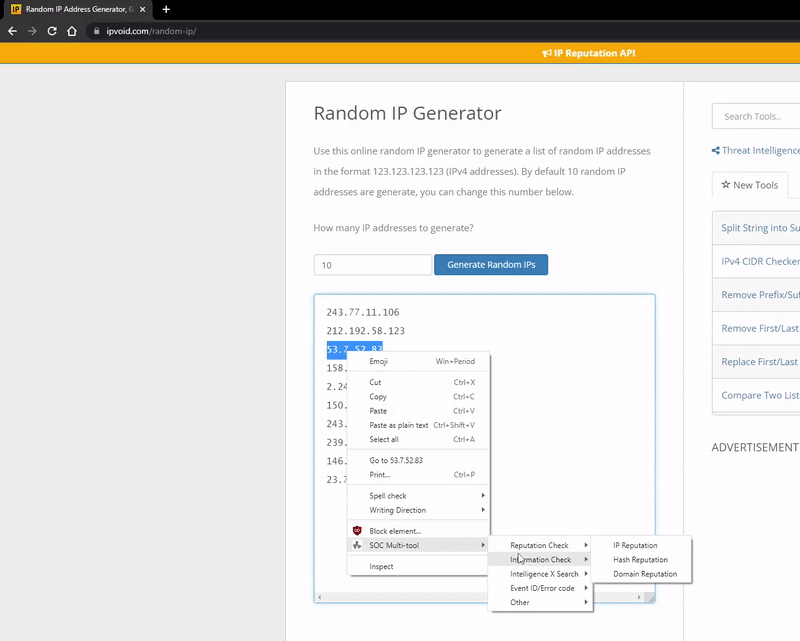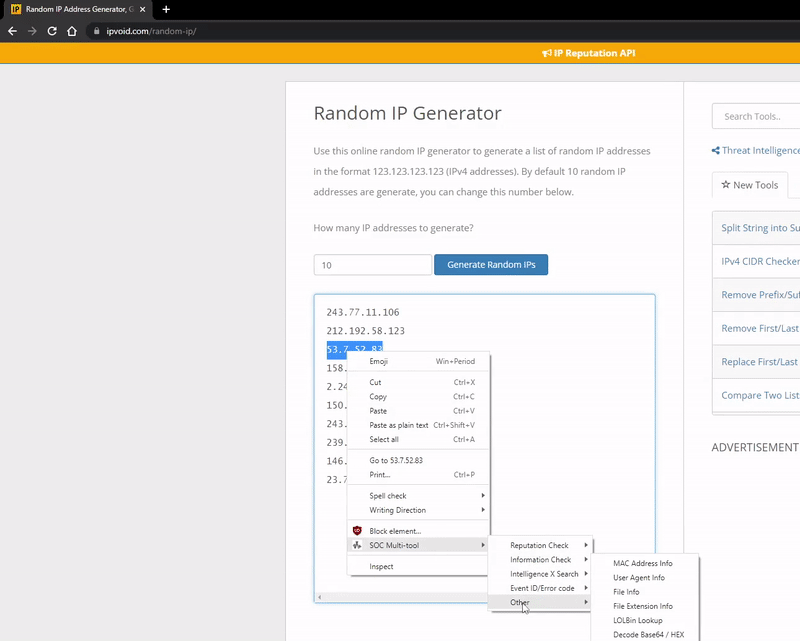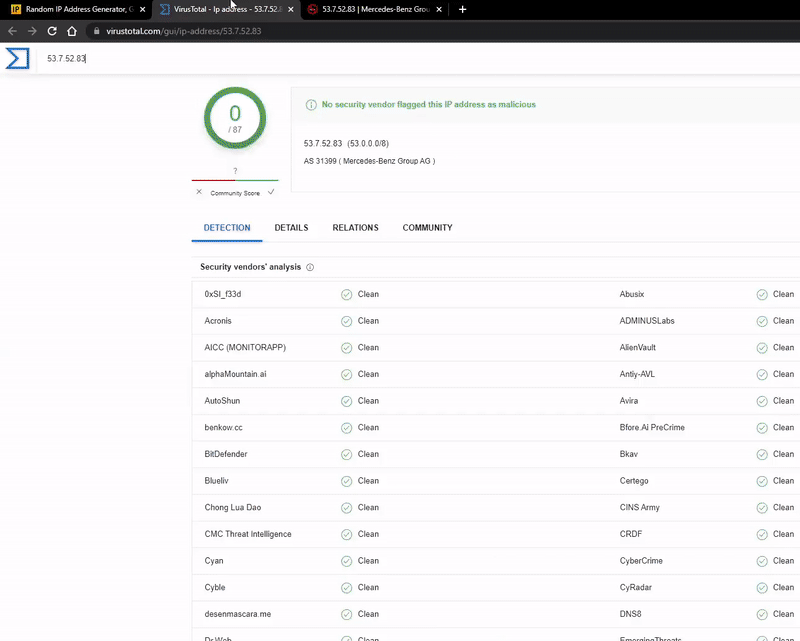
A powerful and user-friendly browser extension that streamlines investigations for security professionals.
incident-responseinformation-gatheringosint+1
4221 year ago
SessionView preview

SessionView

GitHublsecqt/sessionview

A portable C# utility for enumerating local and remote windows sessions

digital-forensicsforensicsincident-response+3
5610 months ago
gitlab-cve-2026-85706-ioc preview

gitlab-cve-2026-85706-ioc

GitHubjithinkrishnanrs/gitlab-cve-2026-85706-ioc

CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…
defensive-toolsincident-responseinformation-gathering+8
21 month ago
thrunt-god preview

thrunt-god

GitHubbackbay-labs/thrunt-god

Threat hunting command system for agentic IDEs

incident-responseinformation-gatheringintrusion-detection+5
413 months ago
dshield preview

dshield

GitHubdshield-isc/dshield

Installs and configures a DShield honeypot sensor on Raspberry Pi or Ubuntu, running Cowrie SSH and HTTP honeypots and forwarding firewall logs to…

defensive-toolsincident-responseinformation-gathering+5
53625 days ago
Previous12345Next