
cve-2026-27483-lab
 nabhan-mohy/cve-2026-27483-lab
A containerized enterprise-style lab for researching and defending against CVE-2026-27483.
educationexploitationincident-response+5
1
nabhan-mohy/cve-2026-27483-labA containerized enterprise-style lab for researching and defending against CVE-2026-27483.
 ethan-andrews/exploitarium-detections
KQL detection rules for Microsoft Sentinel and Defender XDR covering the bikini/exploitarium anonymous disclosure — a personal research archive of…
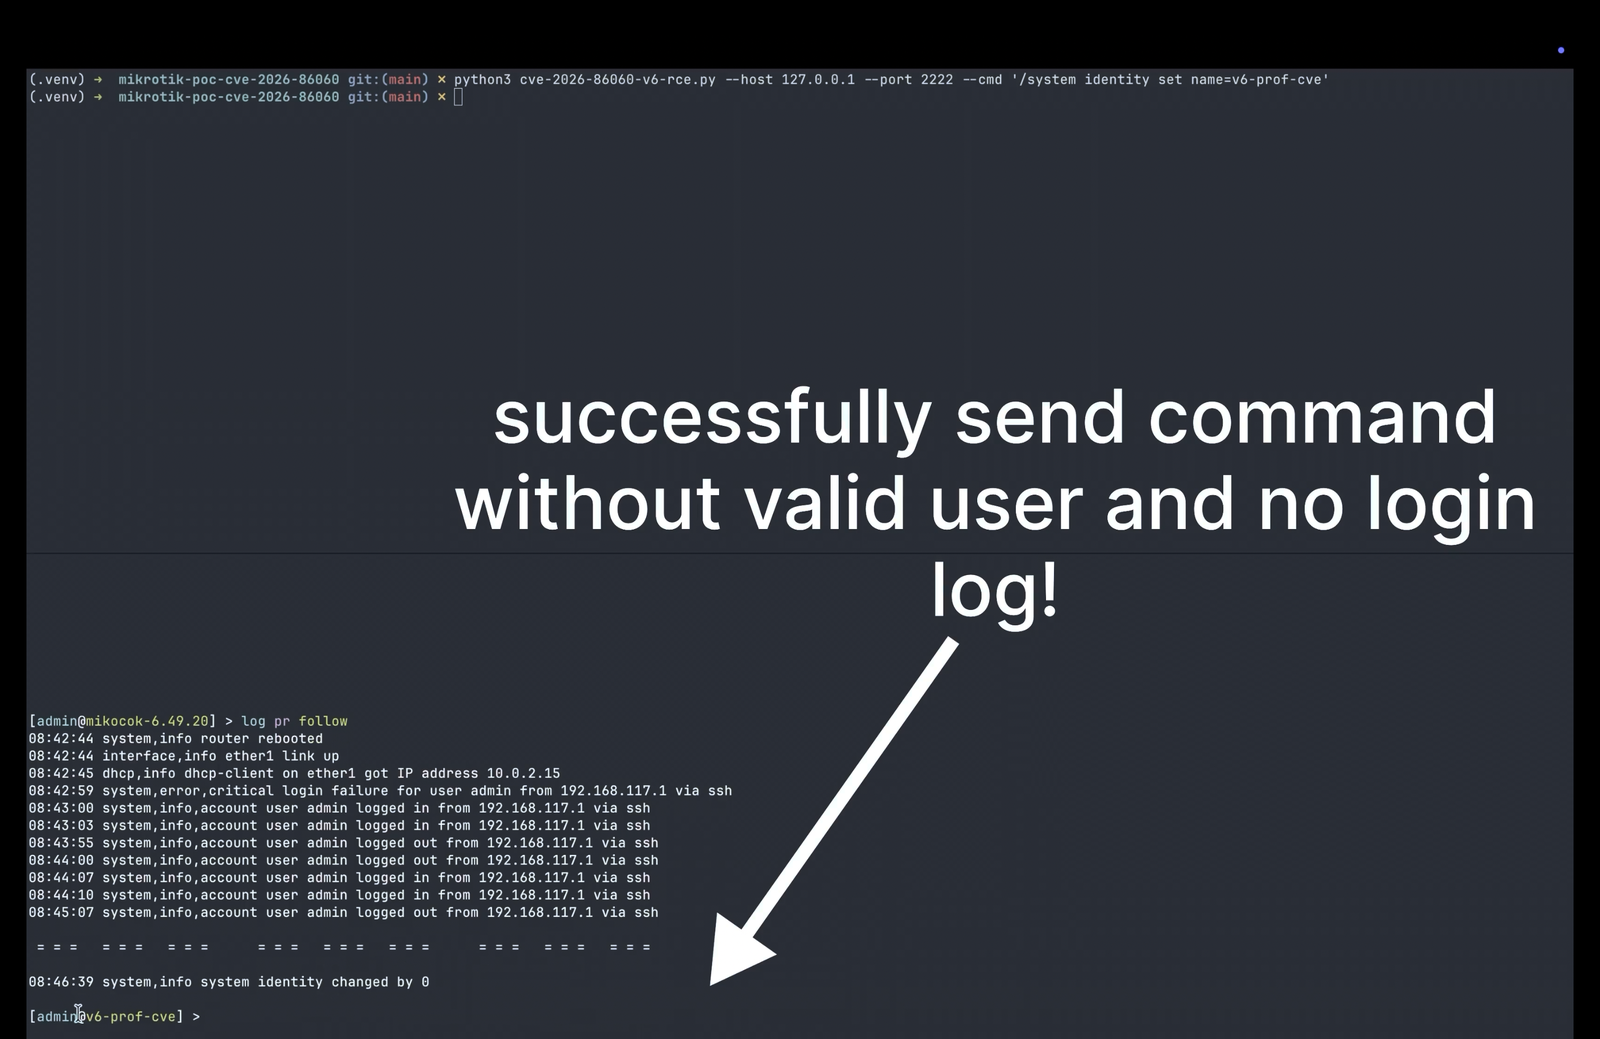 bahirul/cve-2026-86060
Advisory for CVE-2026-86060, a critical pre-auth privilege escalation in MikroTik RouterOS SSH, with impact analysis, detection guidance, and…
 jithinkrishnanrs/stylesmuggler-ioc-toolkit
StyleSmuggler (CVE-2026-75650) IOC toolkit for Magento Open Source and Adobe Commerce. Detect compromised stores, Rust implants, PHP web shells,…
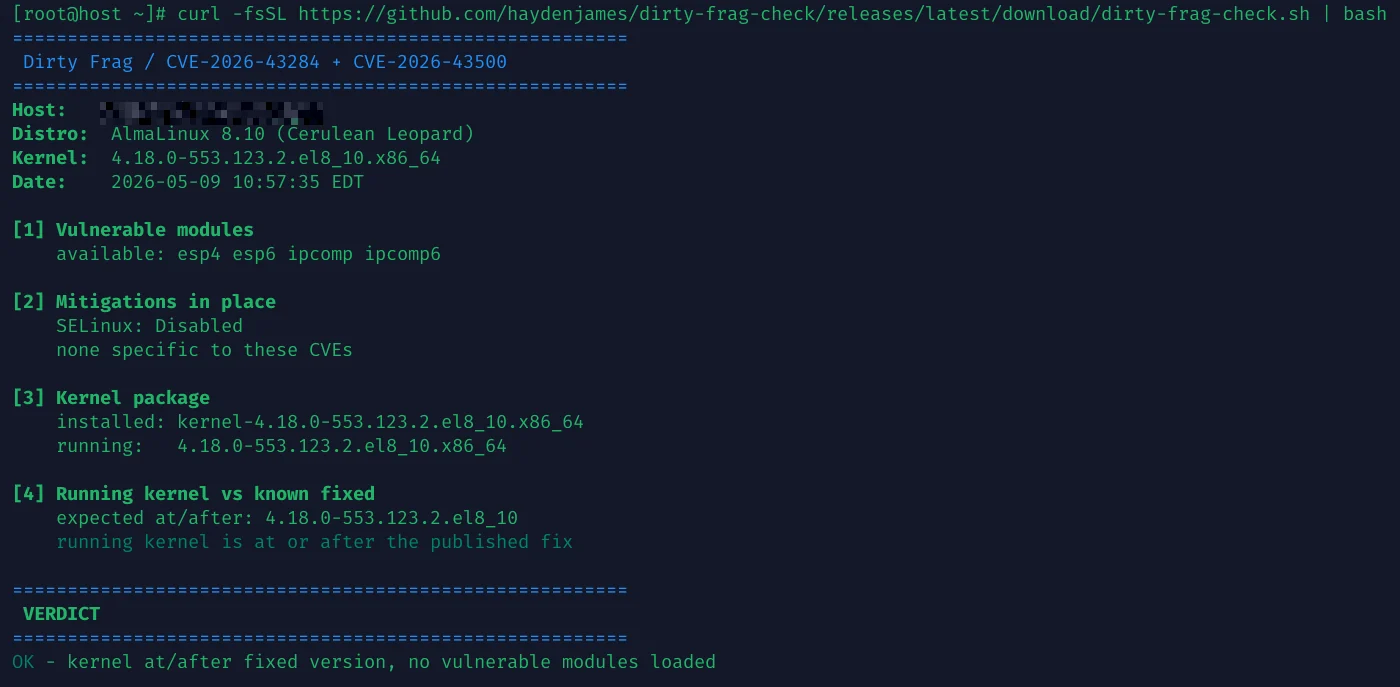 haydenjames/dirty-frag-check
Read-only checker for CVE-2026-43284 / CVE-2026-43500 (Dirty Frag) Linux kernel local-root vulns
 underh0st/cpanel-audit-remediation-tool
Audit and incident response tool for CVE-2026-41940 vulnerability
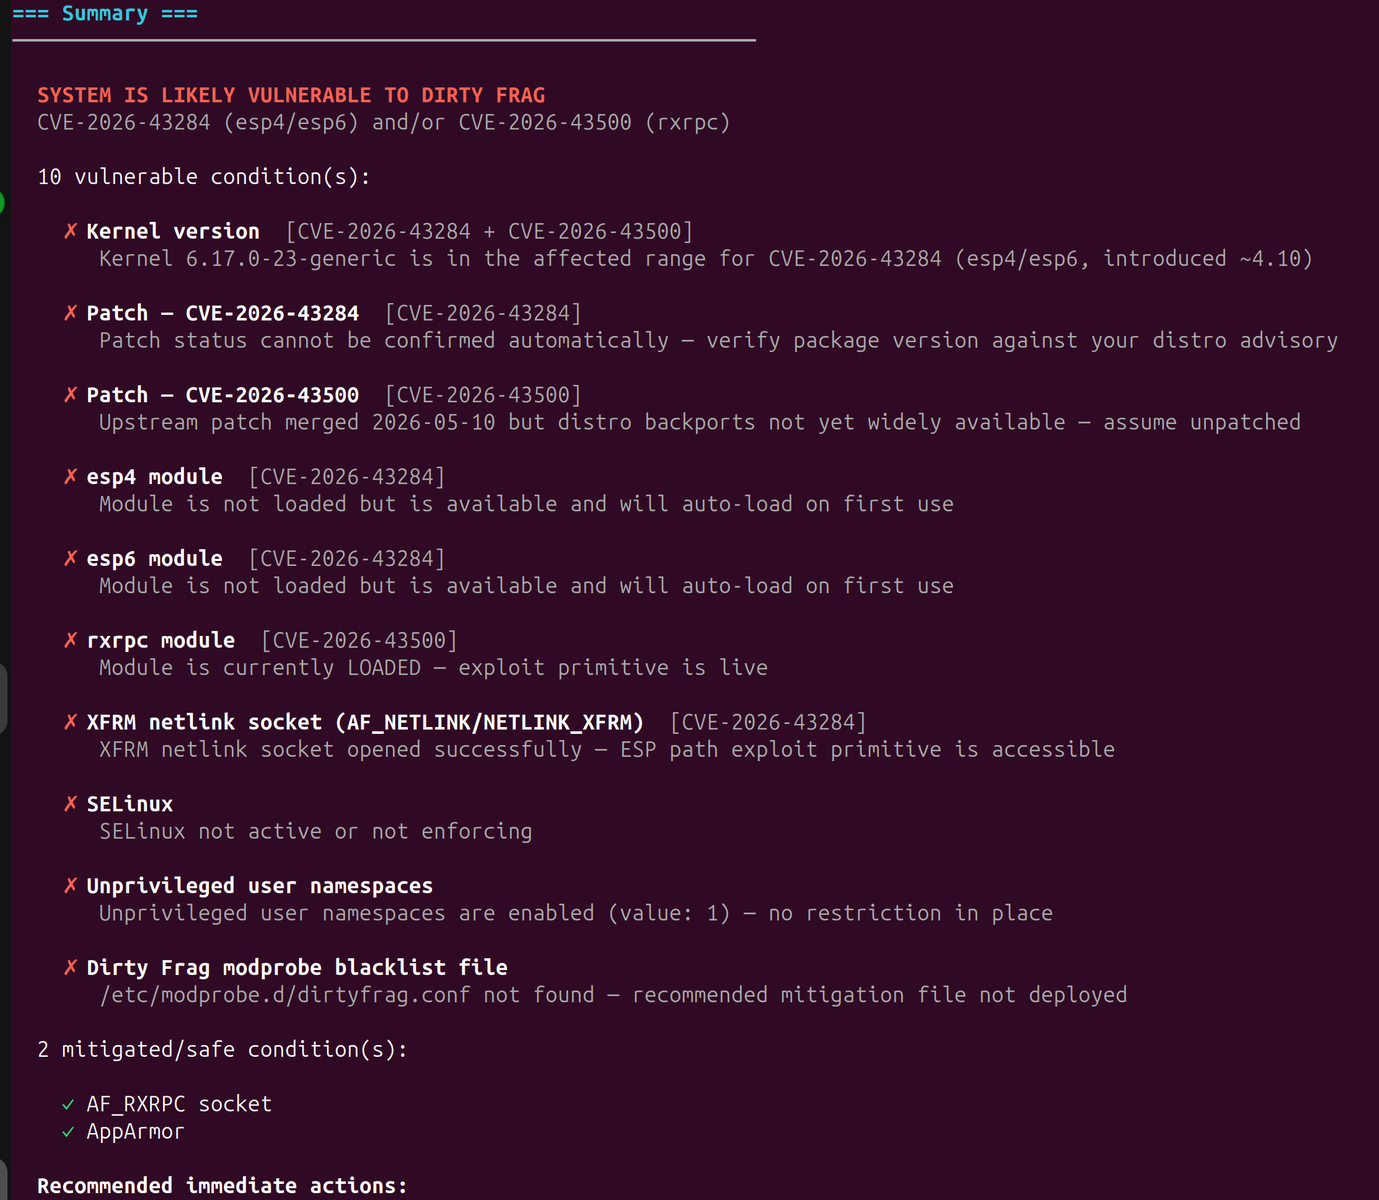 liamromanis101/dirtyfrag-detector
CVE-2026-43284/CVE-2026-43500 'DirtyFrag' Benign patch & mitigation detection script
 hainhc/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…
 boliu83/cve-2026-31431-algif-aead-remediator
Kubernetes DaemonSet to detect and remediate CVE-2026-31431 (GHSA-2274-3hgr-wxv6) — algif_aead LPE via modprobe blacklist
 chpratik/cve-2026-50522
Deserialization of untrusted data in Microsoft Office SharePoint allows an unauthorized attacker to execute code over a network.
 disqualifier/psa-2026-00043-recovery
Recovery notes for proxmox advisory ID: PSA-2026-00043-1 (CVE-2023-54391)
 0xblackash/cve-2026-72898
CVE-2026-72898
 habibkaratas/sorry-ransomware-analysis
Sorry ransomware (.sorry) IOCs, YARA rules and forensic analysis - CVE-2026-41940 cPanel campaign
 sec17br/cve-2026-31431-copy-fail
Bash script to assess Linux host exposure to CVE-2026-31431, check kernel module status, apply mitigation by blocking algif_aead, and update kernel…
 jwa7470/cve-2026-20131-post-incident-written-report
Post-incident report on CVE-2026-20131 (CVSS 10.0), a Cisco FMC insecure deserialization vulnerability exploited by Interlock ransomware. Details…
 cyberdudebivash/cyberdudebivash-cisco-asyncos-cve-2025-20393-scanner
This tool helps identify exposure to CVE-2025-20393 by checking for open TCP/6025 ports, responsive Spam Quarantine interfaces, and known…
 techupdate24/fortimail-zero-day-cve-2026-104286
A complete guide and workflow for integrating Agile sprints with DevOps CI/CD pipelines.
 kaleth4/cve-2026-64638
Technical analysis and defensive mitigation for a WordPress Core pre-auth XSS-to-RCE chain, including sanitizer bypass, DOM clobbering, JSONP abuse,…