
CVE-2025-31702
 itres-labs/cve-2025-31702
Repository with tools, exploits, and material associated with the analysis and discovery process of CVE-2025-31702 and other related security issues.
digital-forensicsexploitationincident-response+3
11
itres-labs/cve-2025-31702Repository with tools, exploits, and material associated with the analysis and discovery process of CVE-2025-31702 and other related security issues.
 logesh-git001/cve-2025-48593
"A single malicious packet can own your device." — Android Security Team, Nov 2025
 abc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
 cyberdudebivash/cyberdudebivash-cisco-asyncos-cve-2025-20393-scanner
This tool helps identify exposure to CVE-2025-20393 by checking for open TCP/6025 ports, responsive Spam Quarantine interfaces, and known…
 adityabhatt3010/cve-2025-8088-winrar-zero-day-path-traversal
An engaging walkthrough on uncovering, patching, and securing the WinRAR CVE-2025-8088 with a hands-on hacker’s twist.
 mrk336/cluster-chaos-exploiting-cve-2025-59359-for-kubernetes-takeover
A hands-on forensic walkthrough of CVE-2025-59359, a critical OS command injection flaw in Chaos-Mesh. Learn how attackers hijack Kubernetes clusters…
 aliksir/nextjs-security-scanner
Bash script to detect CVE-2025-55182 (React2Shell) and credential exposure in Next.js projects. Zero dependencies.
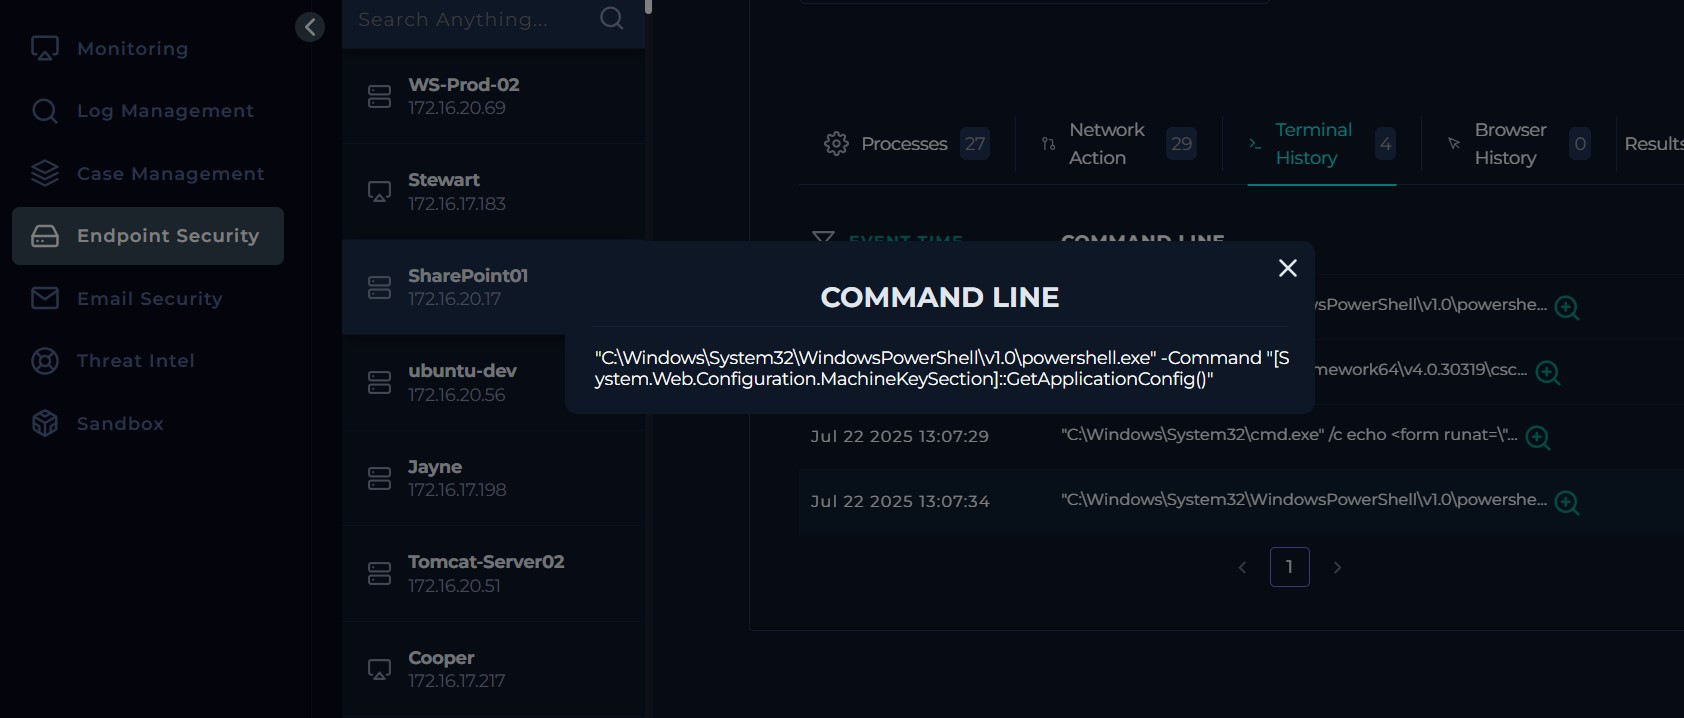 victormbogu1/letsdefend-soc342-cve-2025-53770-sharepoint-toolshell-auth-bypass-andrce-eventid-320
Step-by-step walkthrough of a LetsDefend SOC342 lab analyzing CVE-2025-53770 SharePoint ToolShell auth bypass and RCE, including attack chain,…
 faysalferdous/cve-2025-68645-exploiting-zimbra-webmail-lfi-vulnerability
Defender-focused reference pack for CVE-2025-68645 Zimbra LFI, including Sigma/Splunk detection rules, WAF mitigation snippets, IOC patterns, and…
 cyprianatsyor/toolshell-cve-2025-53770-sharepoint-exploit-lab-letsdefend
Step-by-step walkthrough of exploiting CVE-2025-53770 (ToolShell) in a LetsDefend lab, covering RCE, web shell deployment, and incident response…
 renat0z3r0/notepadpp-supply-chain-iocs
IoCs and detection rules for the Notepad++ supply chain attack (CVE-2025-15556) — Lotus Blossom APT, June–December 2025. Includes Falcon LogScale…
 adityabhatt3010/cve-2025-61882-oracle-e-business-suite-pre-auth-rce-exploit
A critical pre-authentication Remote Code Execution (RCE) flaw in Oracle E-Business Suite (versions 12.2.3 - 12.2.14) allows attackers to gain full…
 onapsis/onapsis_cve-2025-31324_scanner_tools
Python-based scanner for CVE-2025-31324 that identifies vulnerable SAP NetWeaver Visual Composer instances and detects indicators of compromise from…
 mrk336/from-foothold-to-domain-admin-weaponizing-cve-2025-54918-in-real-world-devops
Simulated exploitation and mitigation of CVE-2025-54918 (Windows NTLM flaw). Includes detection scripts, Ansible patching, and CI/CD hardening.…
 logesh-git001/cve-2025-55182
"One crafted HTTP request can compromise your entire server." — React Security Team, Dec 2025
 khin-96/n8n-cve-2025-68613-thm
Educational walkthrough for exploiting CVE-2025-68613, a critical RCE in n8n workflow automation. Covers expression injection, sandbox escape,…
 zenzue/cve-2025-50154
PowerShell toolkit to audit, harden, and hunt for insecure NTLM/SMB usage, addressing CVE-2025-50154 credential leak risks with event log analysis…
 ilhamrzr/rar-anomaly-inspector
Defensive PowerShell tool for static inspection of RAR archives and detection of CVE-2025-8088 path traversal anomalies.