
camjacking
 cappricio-securities/camjacking
CamJacking is a tool designed for use in human penetration testing tool. It is intended to simulate potential security threats by testing the…
educationimpersonation-toolsinformation-gathering+5
71
cappricio-securities/camjackingCamJacking is a tool designed for use in human penetration testing tool. It is intended to simulate potential security threats by testing the…
 dtrecherel/dnsspoof
A DNS spoofer tool written in Python3.
 alperenugurlu/nac_bypass_agent
This function combines all the above functions and takes necessary information from the user to change the IP and MAC address, start the responder…
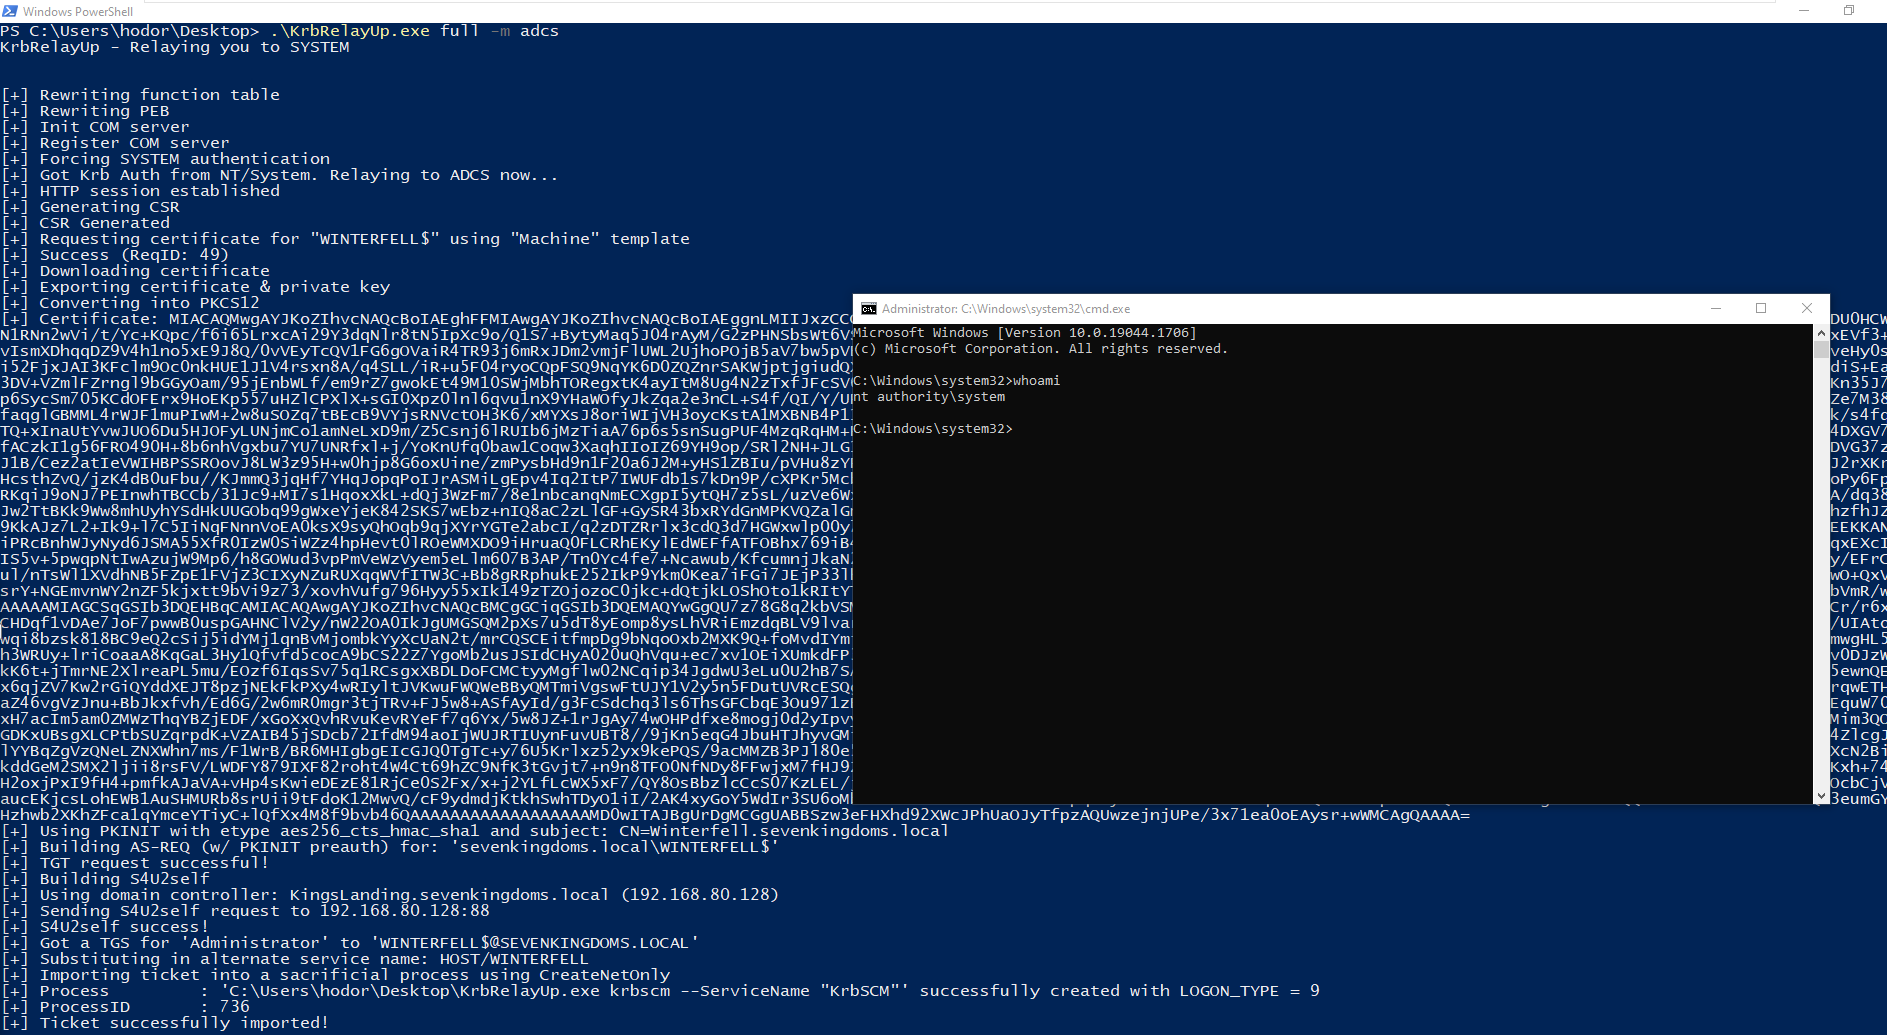 dec0ne/krbrelayup
KrbRelayUp - a universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings).
 byt3bl33d3r/spamchannel
Spoof emails from any of the +2 Million domains using MailChannels (DEFCON 31 Talk)
 quentinhardy/pytmipe
Python library and client for token manipulations and impersonations for privilege escalation on Windows
 kgretzky/evilginx2
Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…
 synacktiv/nord-stream
Nord Stream is a tool that allows you to extract secrets stored inside CI/CD environments by deploying malicious pipelines. It currently supports…
 nccgroup/whowasi
Impersonate Logged In Accounts & Execute Commands
 sanupl/cve-2021-46067
CVE-2021-46067 - In Vehicle Service Management System 1.0 an attacker can steal the cookies leading to Full Account Takeover.
 bishopfox/ca-clone
Scripts to clone CA certificates for use in HTTPS client attacks.
 millad7/sogo_web_mail-vulnerability-cve-2025-50340
Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail Allows a user to send emails on behalf of another user.
 priyankvadaliya/hack-captive-portal
This script helps to pass through the captive portals in public Wi-Fi networks. It hijacks IP and MAC from somebody who is already connected and…
 nccgroup/droppedconnection
Emulates a Cisco ASA Anyconnect VPN service for credential harvesting and VBS payload delivery in red team phishing operations.
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 leftp/backupcreds
A C# implementation of dumping credentials from Windows Credential Manager
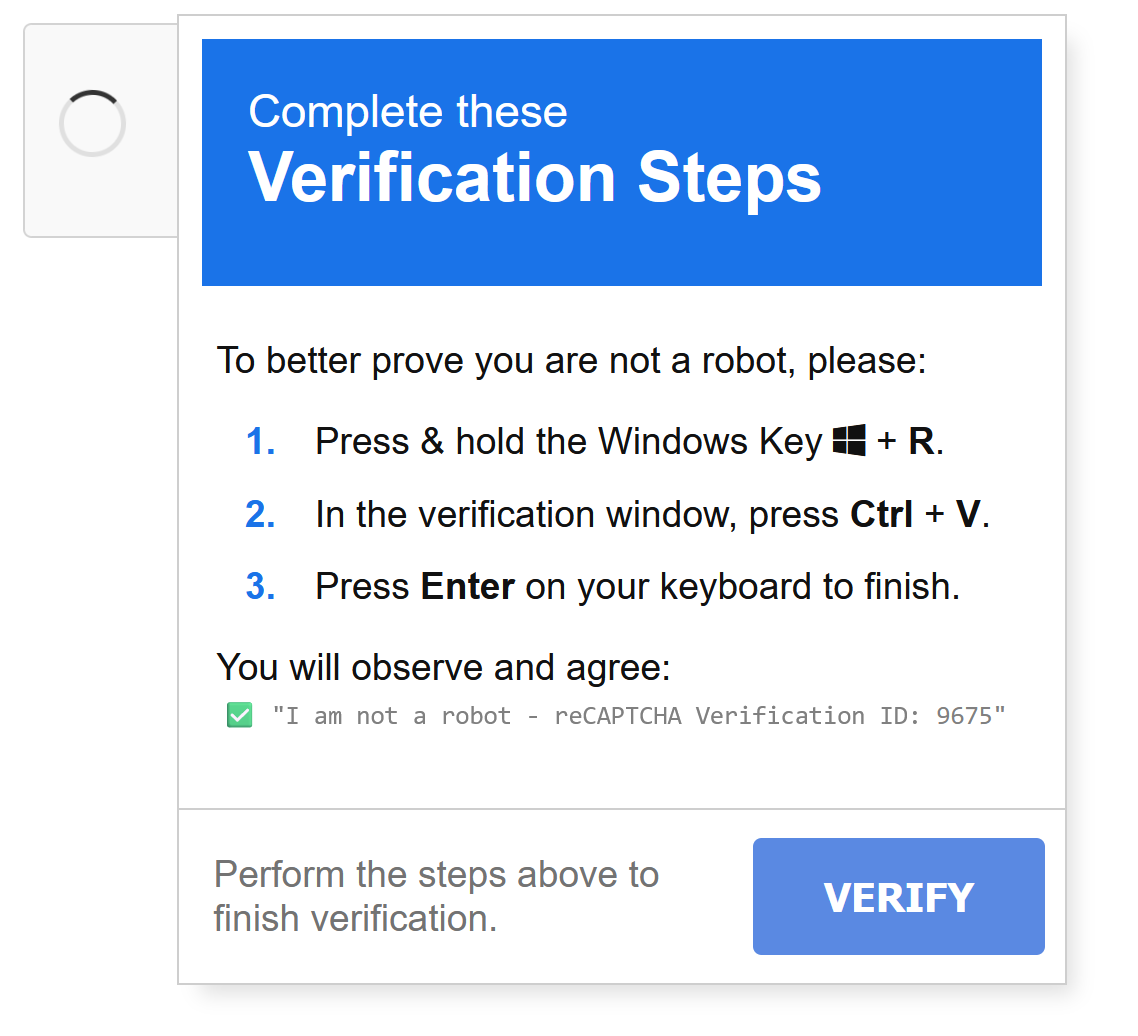 johnhammond/recaptcha-phish
Phishing with a fake reCAPTCHA
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…