
Deep-Live-Cam
 hacksider/deep-live-cam
real time face swap and one-click video deepfake with only a single image
ai-securityimpersonation-toolsosint-social-engineering+2
96.7k
hacksider/deep-live-camreal time face swap and one-click video deepfake with only a single image
 ytkoka/impersonate-proxy
A local MITM proxy that lets you control TLS fingerprints (JA3/JA4), HTTP/2 fingerprints, HTTP header order, and User-Agent — all from a single YAML…
 0x4meliorate/mimic
Frameless Browser‑in‑the‑Browser (BitB) - No iframes, no frame‑busting issues. A single‑script Shadow DOM / MutationObserver library for realistic…
 drk1wi/modlishka
Modlishka. Reverse Proxy.
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…
 kgretzky/evilginx2
Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…
 synacktiv/prox-ez
HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…
 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
 crimsonforge-io/king-phisher
Simulate realistic phishing campaigns with credential harvesting, email tracking, and landing page cloning for security awareness training and…
 mzhmo/powershellkerberos
Some scripts to abuse kerberos using Powershell
 jienweng/yappy
AI-powered LinkedIn engagement assistant
 cappricio-securities/socialengineering
SEt framework
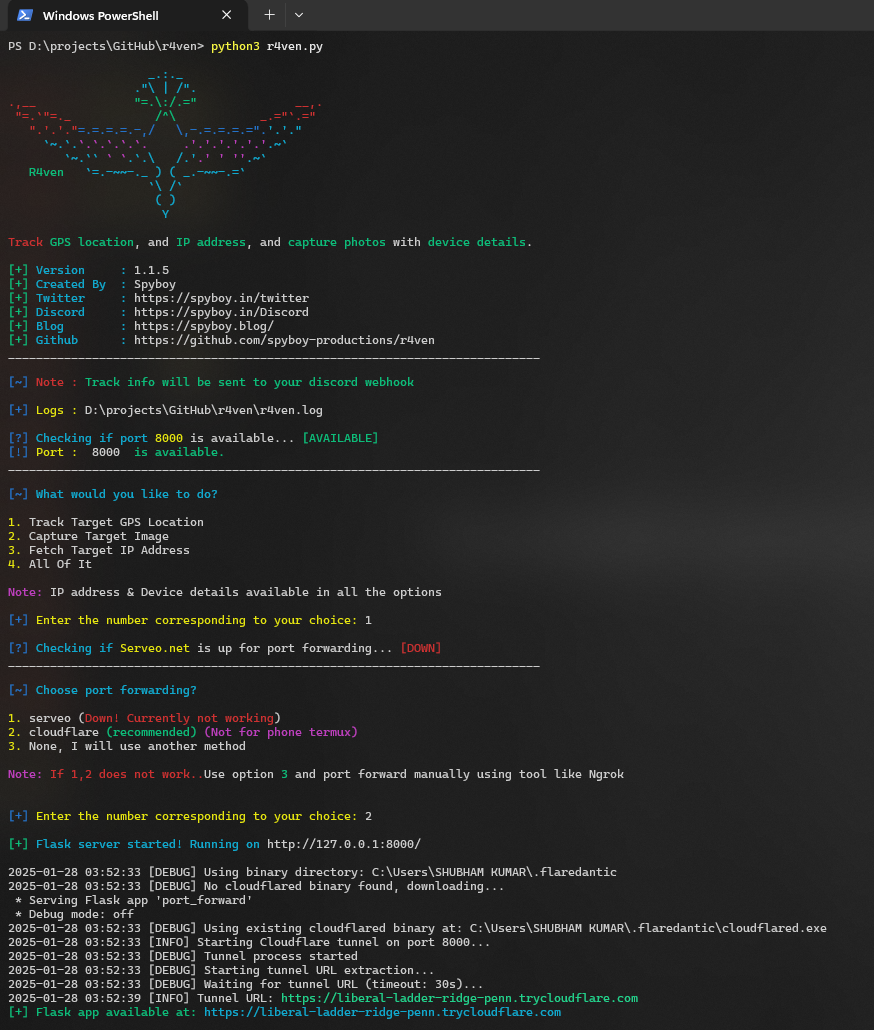 spyboy-productions/r4ven
Track the GPS location of the user's smartphone or PC and capture a picture of the target, along with IP and device information.
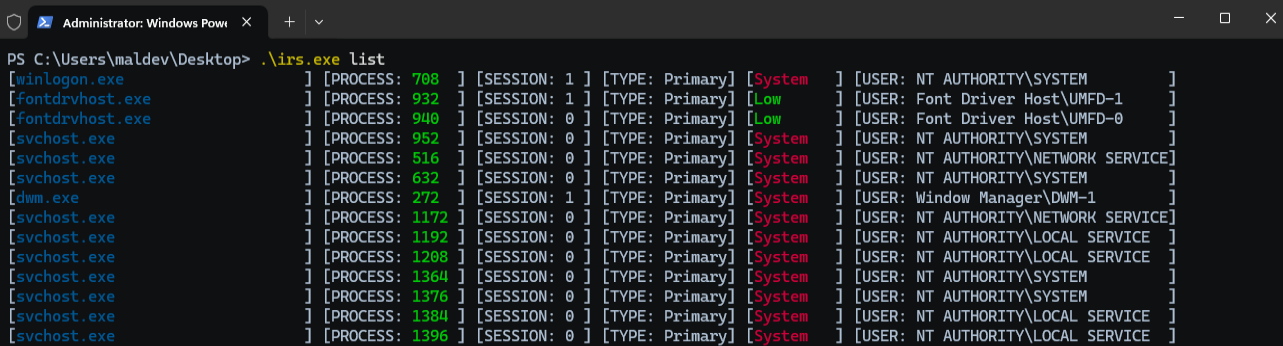 zblurx/impersonate-rs
Rusty Impersonate
 millad7/sogo_web_mail-vulnerability-cve-2025-50340
Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail Allows a user to send emails on behalf of another user.
 rasta-mouse/spawnwith
Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…
 muraenateam/muraena
Automates phishing and post-phishing activities with an almost-transparent reverse proxy that dynamically mirrors target web apps and interacts with…
 rweijnen/createdump
Leverage WindowsApp createdump tool to obtain an lsass dump