
Christmas
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
adversarial-attackids-ips-evasionpayload-development+3
257
maldev-academy/christmasPoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 nuclearphoenixx/fake-sandbox
👁🗨 This script will simulate fake processes of analysis sandbox/VM software that some malware will try to avoid.
 3xpl01tc0d3r/processinjection
This program is designed to demonstrate various process injection techniques
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 reveng007/darkwidow
Indirect Dynamic Syscall, SSN + Syscall address sorting via Modified TartarusGate approach + Remote Process Injection via APC Early Bird + Spawns a…
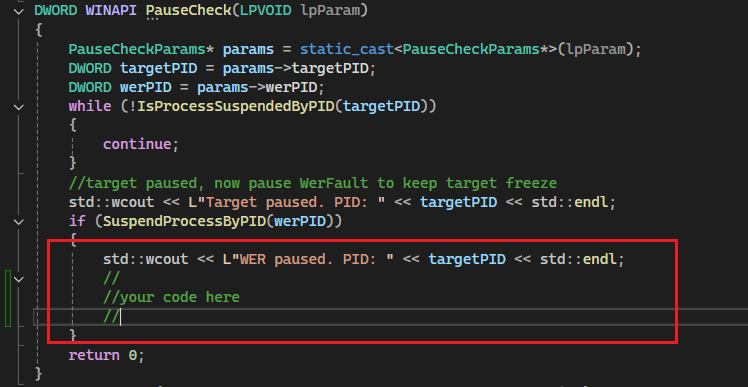 twosevenonet/edr-freeze
EDR-Freeze is a tool that puts a process of EDR, AntiMalware into a coma state.
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 s12cybersecurity/windefenderkiller
Windows Defender Killer | Registry-Based Disablement + BYOVD Process Termination (C++)
 malwaretech/edr-preloader
An EDR bypass that prevents EDRs from hooking or loading DLLs into our process by hijacking the AppVerifier layer
 flangvik/amsi.fail
C# Azure Function with an HTTP trigger that generates obfuscated PowerShell snippets that break or disable AMSI for the current process.
 pushpenderindia/crypter
Python-based crypter that encrypts source code with AES-256 and Base64, evades VM detection via registry, process, and MAC checks, and executes…
 twosevenonet/injectsetconsole
Proof of Concept for Process Code Injection Without Using WriteProcessMemory
 solomonsklash/sleepycrypt
A shellcode function to encrypt a running process image when sleeping.
 rsmudge/unhook-bof
Remove API hooks from a Beacon process.
 loosehose/silentbutdeadly
SilentButDeadly is a network communication blocker specifically designed to neutralize EDR/AV software by preventing their cloud connectivity using…
 saadahla/ntdlll-unhooking-collection
different ntdll unhooking techniques : unhooking ntdll from disk, from KnownDlls, from suspended process, from remote server (fileless)
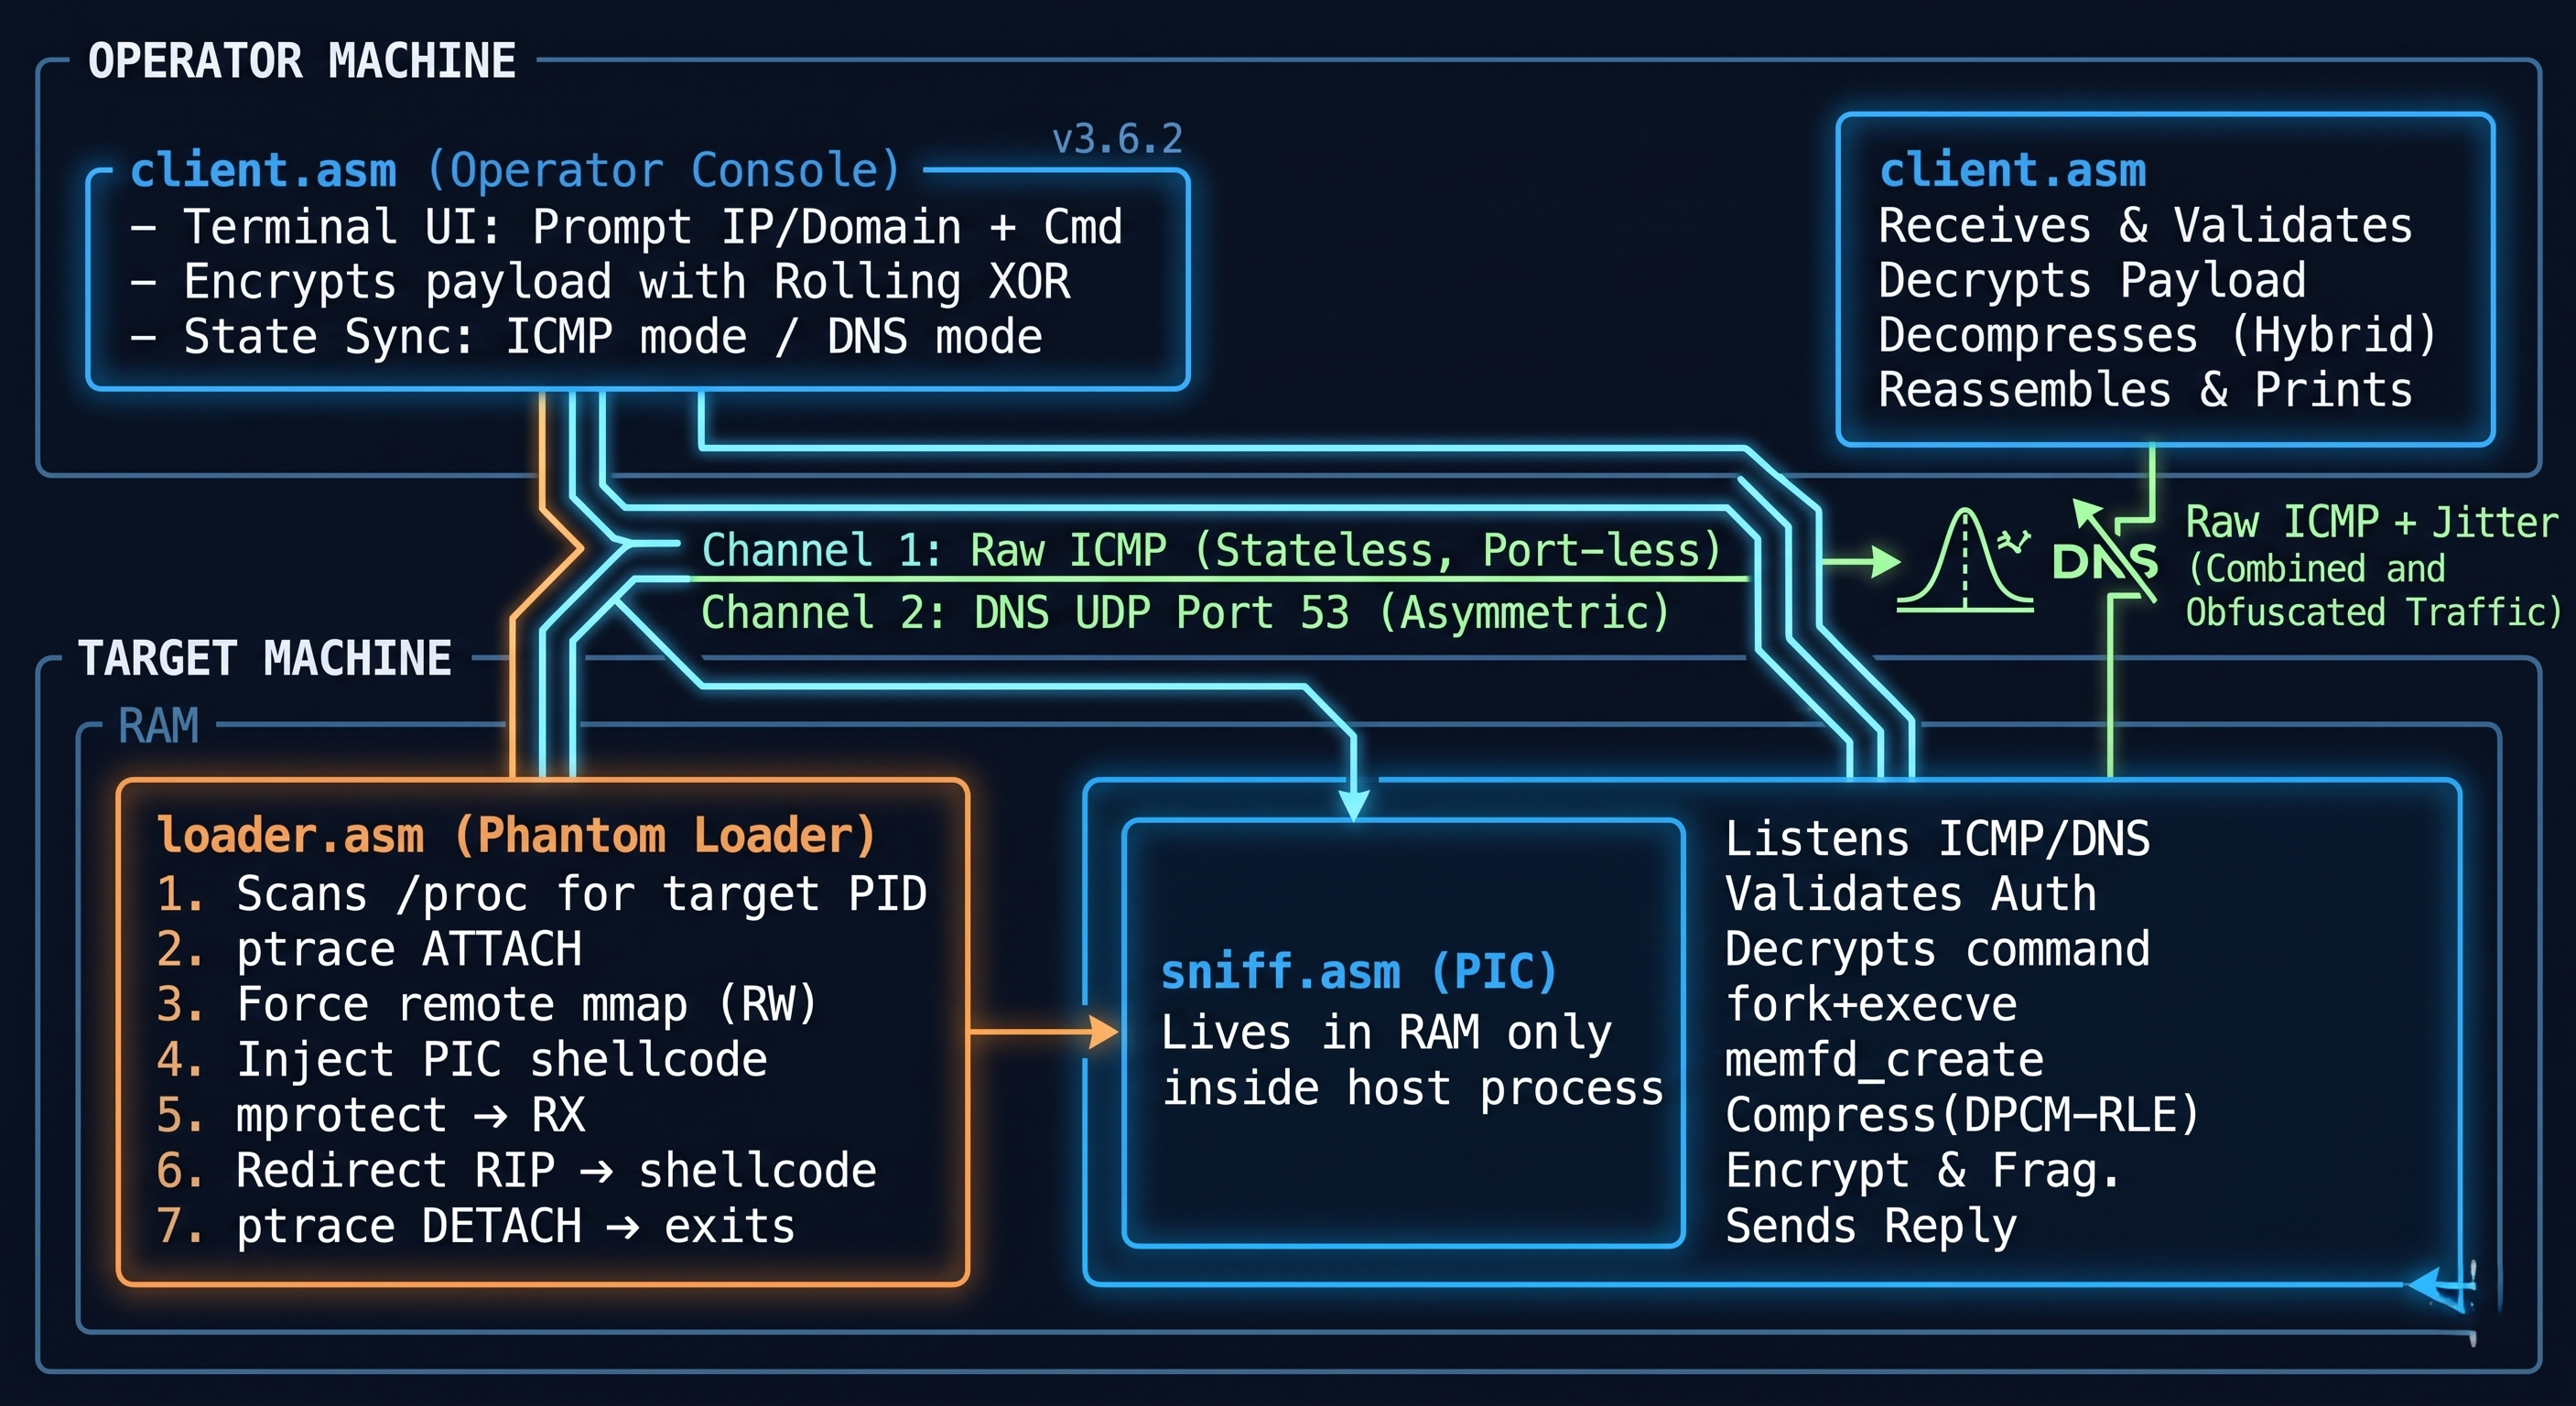 jm00nj/icmp-ghost-a-fileless-x64-assembly-c2-agent
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…