

Windows-SignedBinary
 mr-un1k0d3r/windows-signedbinary
Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
adversarial-attackbinary-analysishash-analysis+4
mr-un1k0d3r/windows-signedbinaryMutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
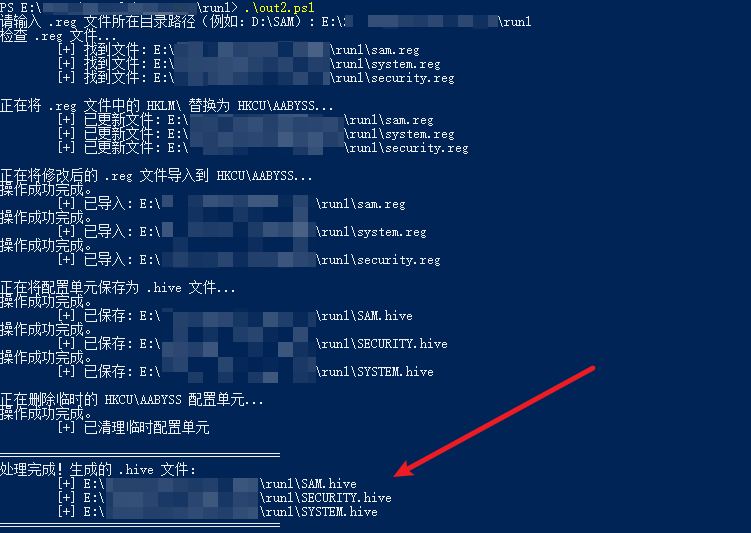 aabysszg/hashdump-bypassedr
Windows绕过EDR实现DumpHash
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 jpillora/chisel
Fast TCP/UDP tunnel over HTTP with SSH encryption, supporting reverse port forwarding, SOCKS5 proxy, and client authentication for secure network…
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 crowdsecurity/crowdsec
Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…
 yarrick/iodine
Tunnel IPv4 data through DNS servers to bypass firewall restrictions and provide covert network access for penetration testing.
 ultrafunkamsterdam/nodriver
Successor of Undetected-Chromedriver. Providing a blazing fast framework for web automation, webscraping, bots and any other creative ideas which are…
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
 iagox86/dnscat2
Encrypted command-and-control tunnel over DNS protocol. Creates stealthy C&C channels for penetration testing, with file transfer, shell access, and…
 phra/pezor
Pack shellcode and PE executables into evasive payloads with anti-debug, unhooking, syscall, and memory fluctuation techniques for red-team…
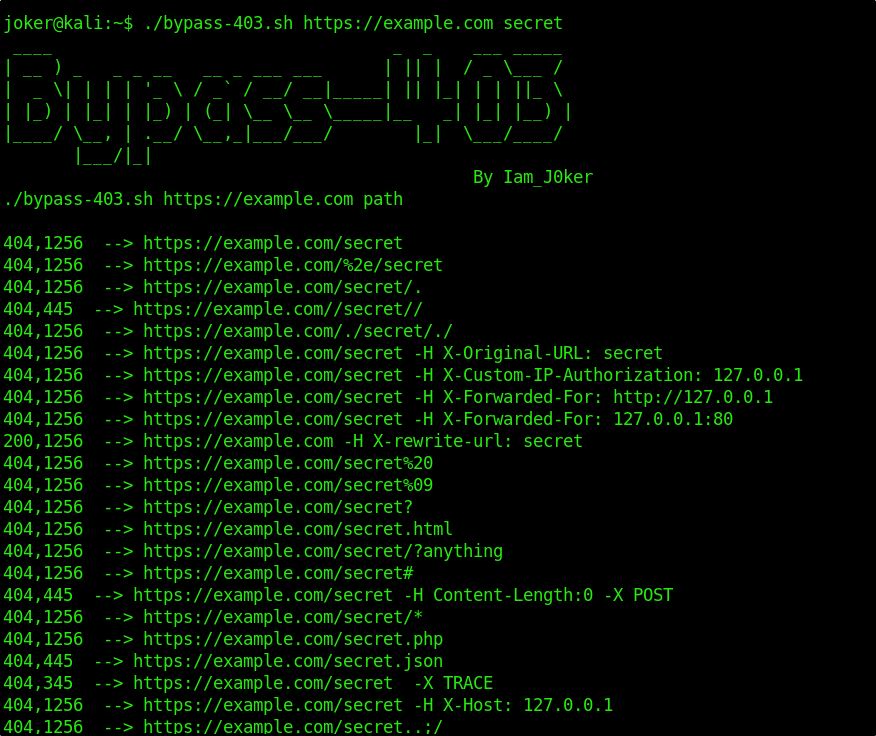 iamj0ker/bypass-403
A simple script just made for self use for bypassing 403
 egebalci/sgn
Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…