Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
37 results
EAC-Kernel-Packet-Fucker preview

EAC-Kernel-Packet-Fucker

GitHubgmh5225/eac-kernel-packet-fucker

Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…

anti-botbinary-analysisencryption-decryption-tools+6
17
4 years ago
shouganaiyo-loader preview

shouganaiyo-loader

GitHubnccgroup/shouganaiyo-loader

shouganaiyo-loader is a cross-platform Frida-based Node.js command-line tool that forces Java processes to load a Java/JVMTI agent regardless of…

exploitationids-ips-evasionpenetration-testing+2
394 years ago
NullSection preview

NullSection

GitHubmatheuzsecurity/nullsection

ELF anti-reversing tool that overwrites section headers with nullbytes to prevent static analysis by disassemblers and debuggers, rendering functions…

anti-botbinary-analysiseducation+2
673 years ago
HyperDeceit preview

HyperDeceit

GitHubxyrem/hyperdeceit

HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…

adversarial-attackbinary-analysisids-ips-evasion+3
3833 years ago
CallObfuscator preview

CallObfuscator

GitHubd35ha/callobfuscator

Obfuscate specific windows apis with different apis

binary-analysisdefensive-toolsdynamic-analysis-sandboxing+4
1.0k5 years ago
EDRs preview

EDRs

GitHubmr-un1k0d3r/edrs

Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.

binary-analysiscurated-resourcesids-ips-evasion+3
2.2k6 months ago
SafeLine preview

SafeLine

GitHubchaitin/safeline

Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…

anti-botapi-securityapi-security-testing+8
22.7k17 days ago
hades preview

hades

GitHubf1zm0/hades

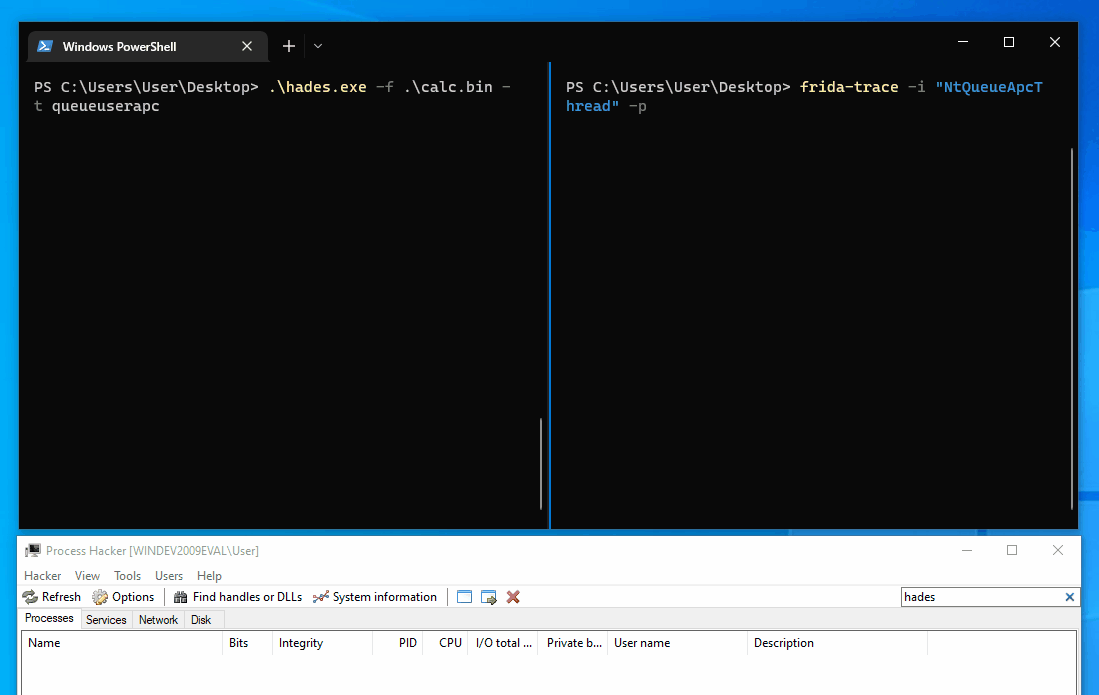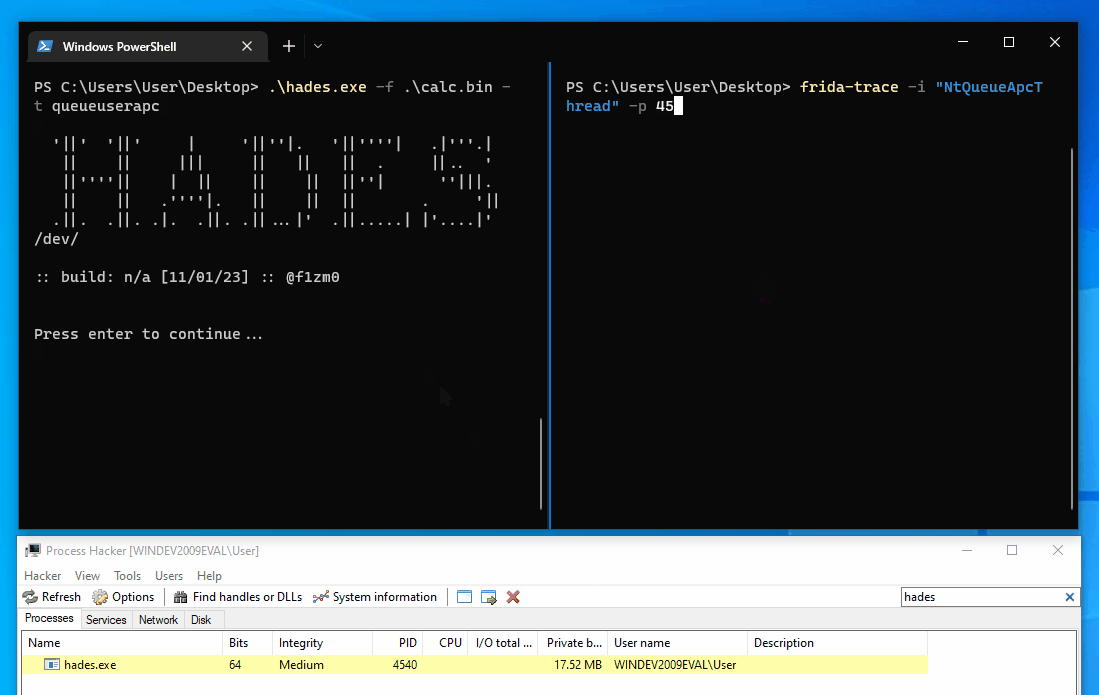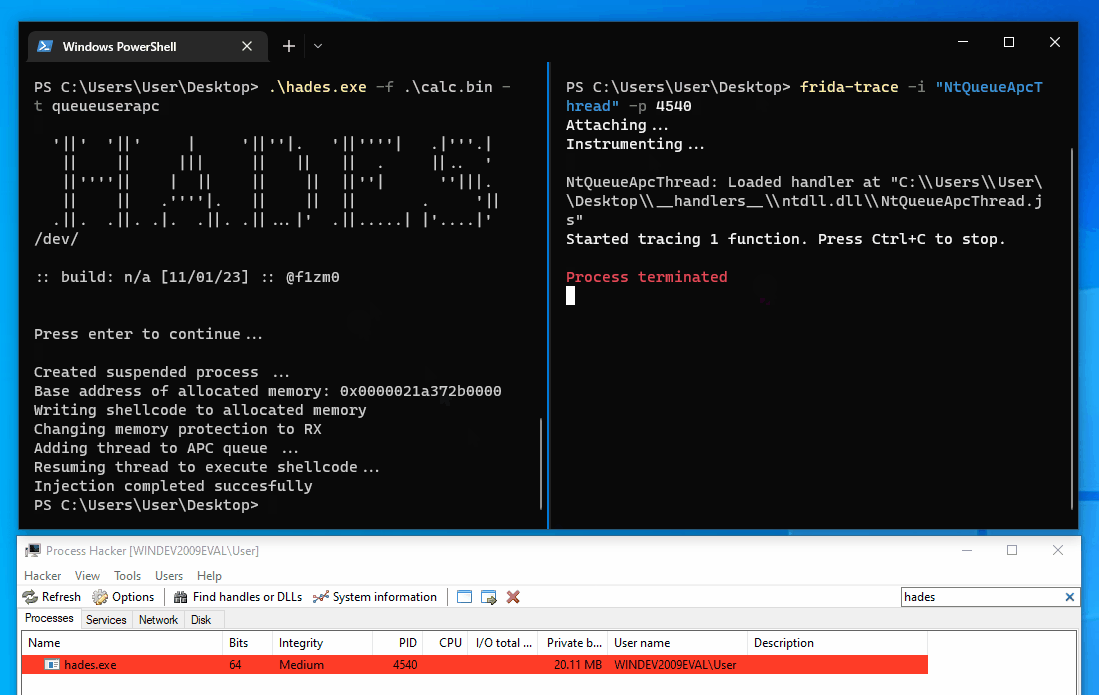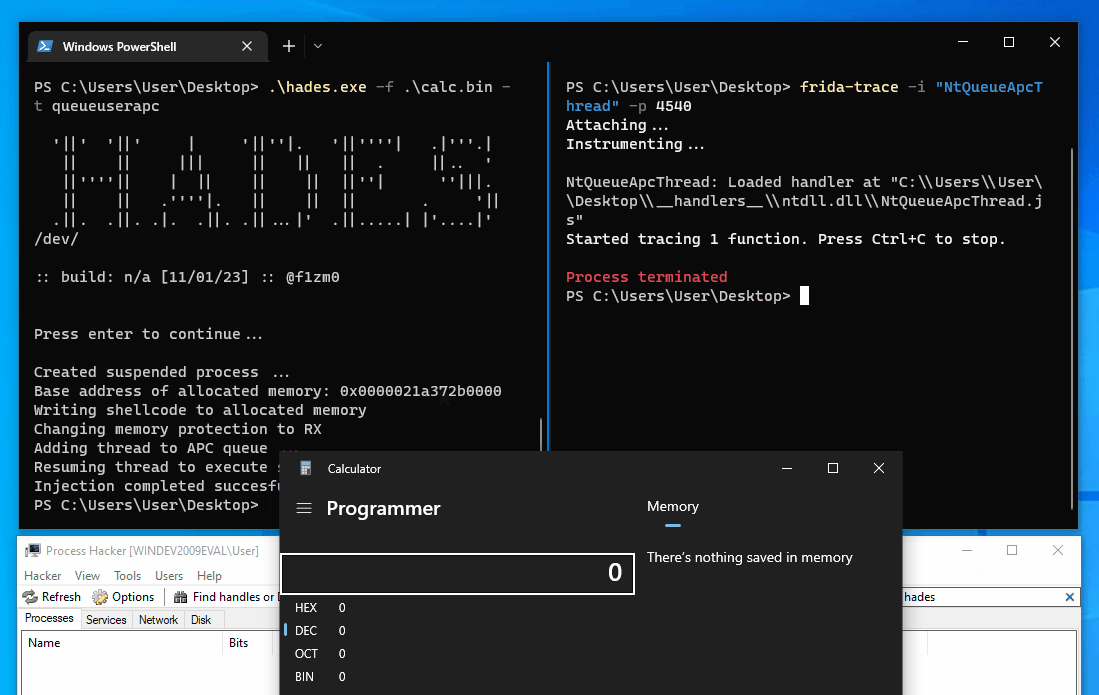
Go shellcode loader that combines multiple evasion techniques

ids-ips-evasionshellcodeshellcode-generation
3923 years ago
AMSI-patches-learned-till-now preview

AMSI-patches-learned-till-now

GitHubreveng007/amsi-patches-learned-till-now

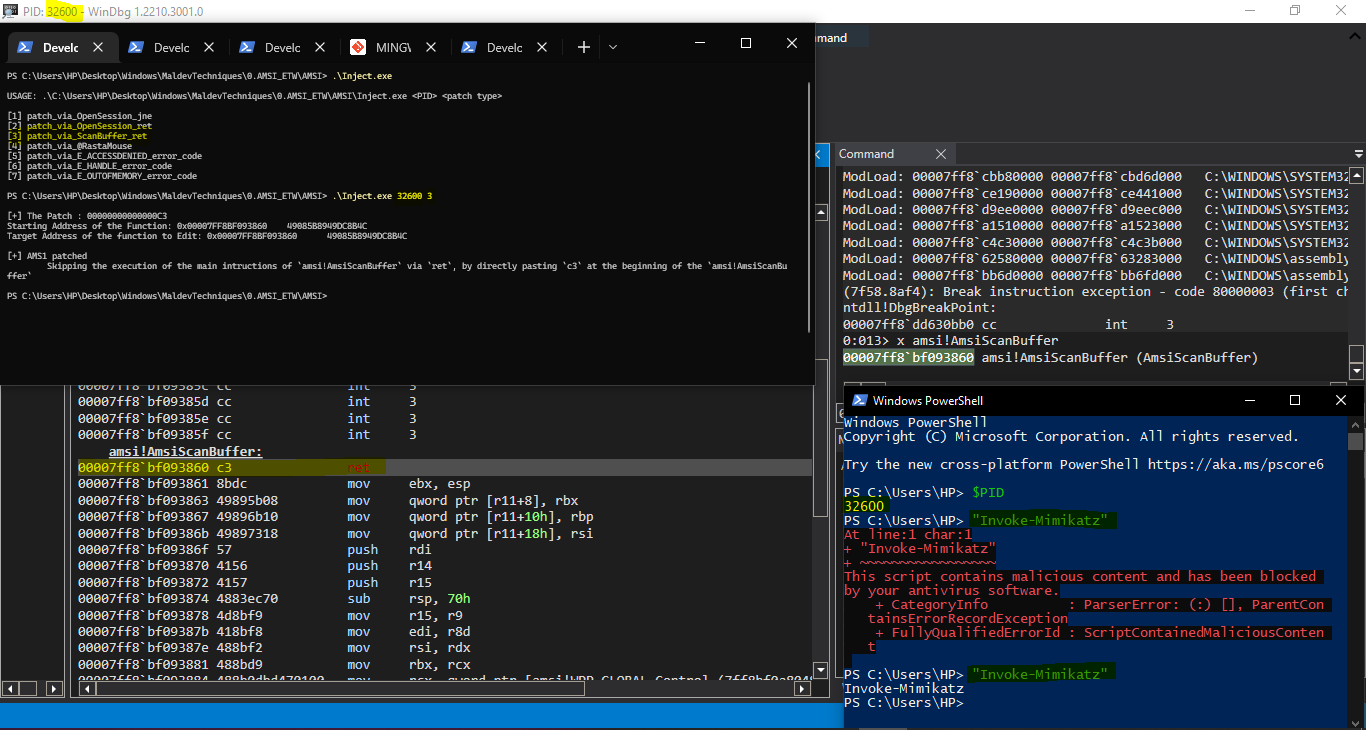
I have documented all of the AMSI patches that I learned till now

curated-resourceseducationids-ips-evasion+3
7211 months ago
Nodejs-Tracer preview

Nodejs-Tracer

GitHubcheckpointsw/nodejs-tracer

Runtime tracer for Node.js malware analysis that hooks core modules, logs calls, spoofs anti-analysis checks, and captures file writes and HTTP…

anti-botdynamic-analysis-sandboxingids-ips-evasion+3
819 months ago
RedWarden preview
Archived

RedWarden

GitHubmgeeky/redwarden

Cobalt Strike C2 Reverse proxy that fends off Blue Teams, AVs, EDRs, scanners through packet inspection and malleable profile correlation

command-and-controlexploit-frameworksids-ips-evasion+8
9934 years ago
OffensiveRust preview

OffensiveRust

GitHubtrickster0/offensiverust

Rust Weaponization for Red Team Engagements.

binary-exploitationcommand-and-controleducation+9
3.0k3 years ago
FUD-UUID-Shellcode preview

FUD-UUID-Shellcode

GitHubbl4ckm1rror/fud-uuid-shellcode

C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…

binary-exploitationdefensive-toolsexploitation+6
3343 years ago
AtomicSyscall preview

AtomicSyscall

GitHubdaem0nc0re/atomicsyscall

Tools and PoCs for Windows syscall investigation.

adversarial-attackbinary-analysiseducation+3
36410 months ago
Windows-SignedBinary preview

Windows-SignedBinary

GitHubmr-un1k0d3r/windows-signedbinary

Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…

adversarial-attackbinary-analysishash-analysis+4
2617 years ago
ROPInjector preview

ROPInjector

GitHubgpoulios/ropinjector

Patching ROP-encoded shellcodes into PEs

binary-analysisbinary-exploitationexploitation+7
1868 years ago
peCloakCapstone preview

peCloakCapstone

GitHubv-p-b/pecloakcapstone

Platform independent peCloak fork based on Capstone

binary-analysisids-ips-evasionmalware-analysis+2
10911 years ago
360WFP_Exploit preview

360WFP_Exploit

GitHubkyxiaxiang/360wfp_exploit

BYOVD: Use 360 ​​WFP driver to block EDR/XDR network connection.

binary-analysisexploitationids-ips-evasion+6
1318 months ago
Previous123Next