

 knqyf263/cve-2021-40346
CVE-2021-40346 PoC (HAProxy HTTP Smuggling)
 ttpreport/siphondns
Covert data exfiltration via DNS
 magisterquis/lutlol
Living Under the Land on Linux ~ Bsides Belfast/Vienna 2025
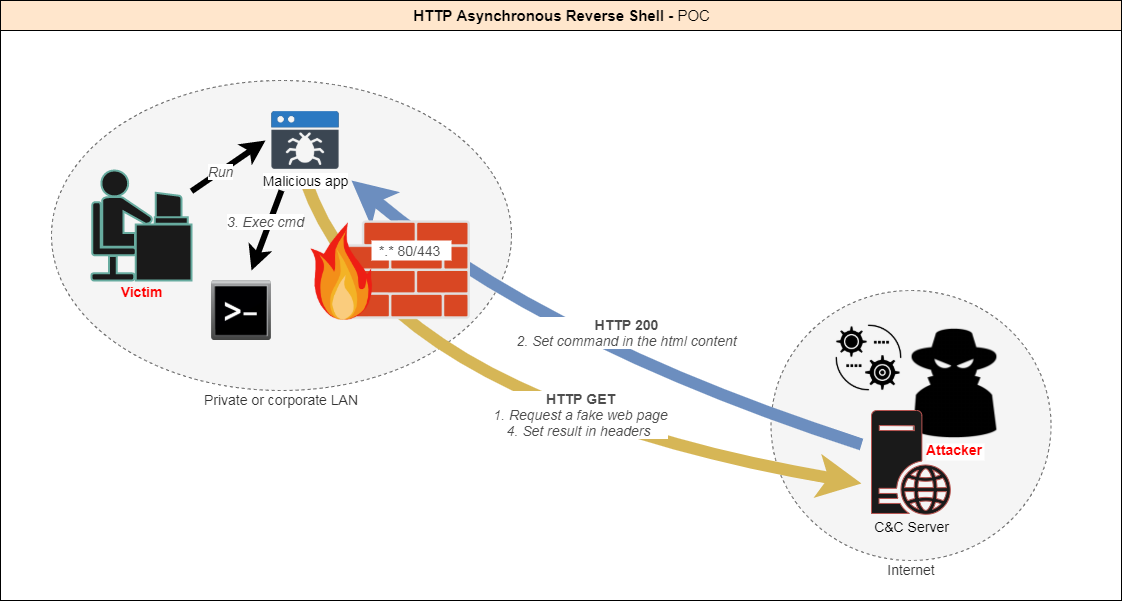 onsec-fr/http-asynchronous-reverse-shell
[POC] Asynchronous reverse shell using the HTTP protocol.

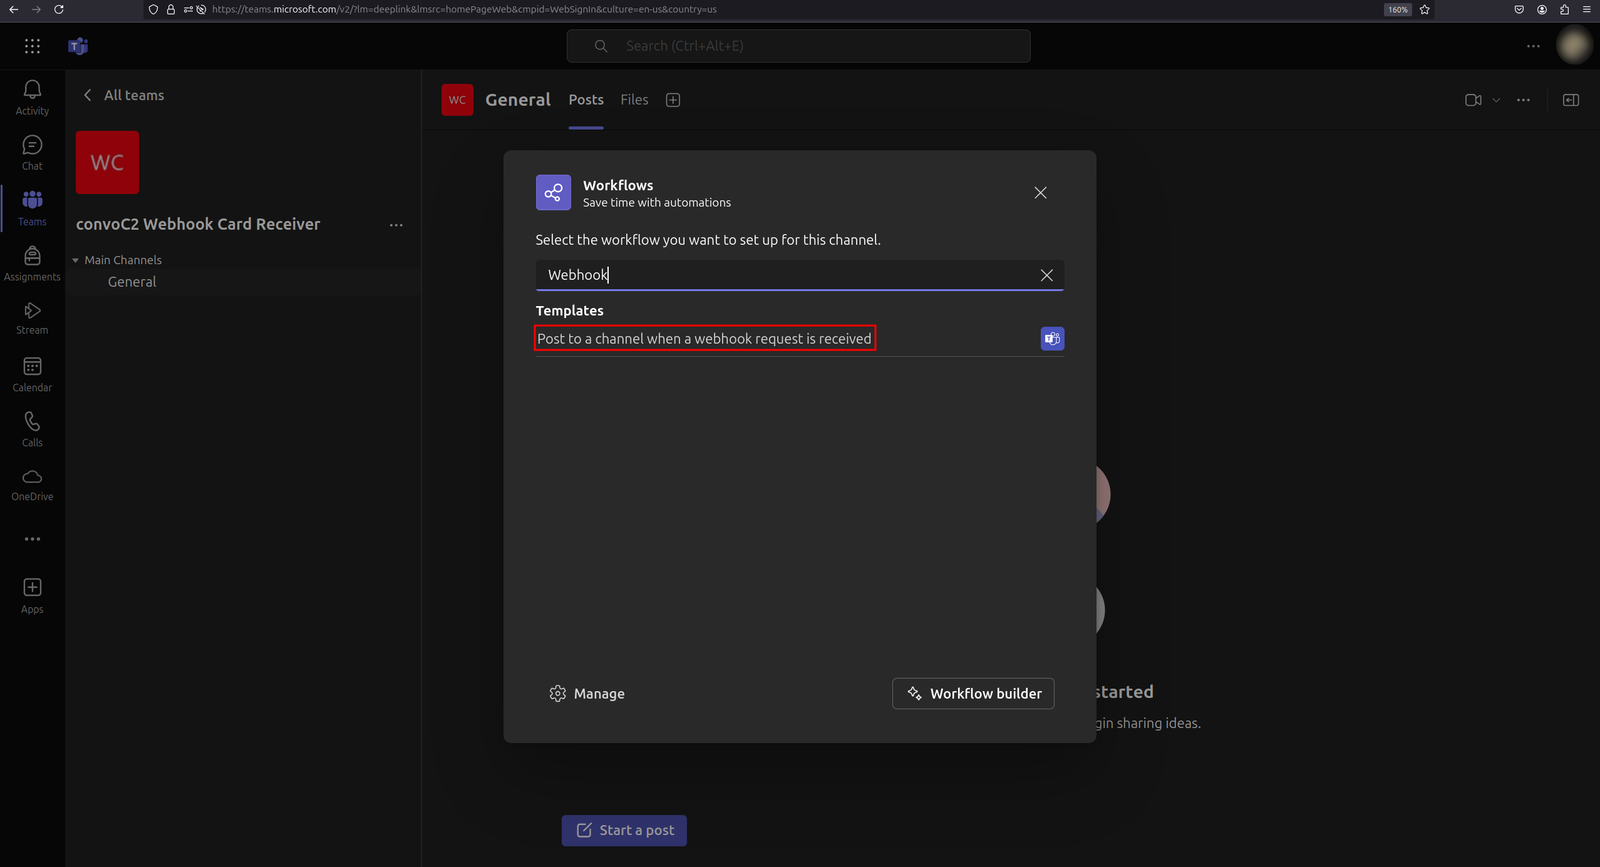 cxnturi0n/convoc2
C2 infrastructure over Microsoft Teams.
 matheuzsecurity/ringreaper
Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
 zerodaylab/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
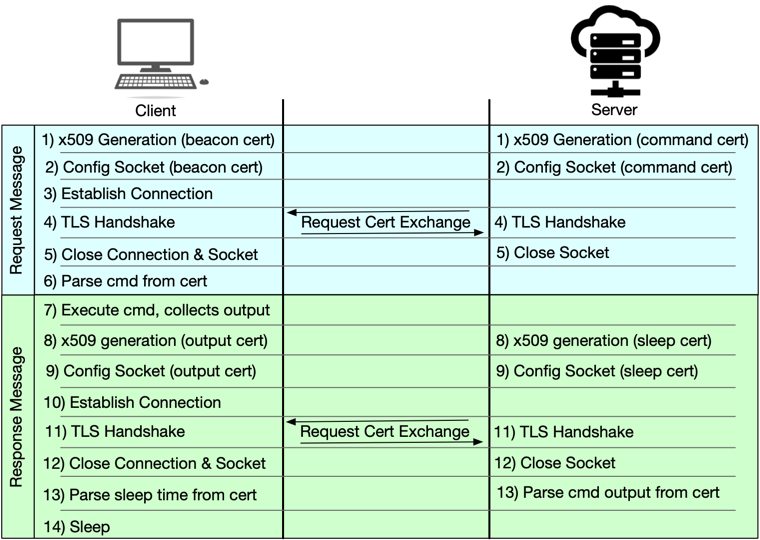 jconwell/secret_handshake
A prototype malware C2 channel using x509 certificates over mTLS
 krixx1337/burner-net
Zero-trust anti-forensic HTTP client. Wipes secrets. Severs traces. CPR in a Stealth Tank. 👻
 abraxas/veneficus
Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.
 masterking32/masterhttprelayvpn
Domain-fronted HTTP/SOCKS5 proxy tunneling traffic through Google Apps Script with MITM TLS interception, HTTP/1-2 multiplexing, and DPI evasion.
 matro7sh/bypassav
This map lists the essential techniques to bypass anti-virus and EDR
 blacksnufkin/byovd
BYOVD research use cases featuring vulnerable driver discovery and reverse engineering methodology. (CVE-2025-52915, CVE-2025-1055, CVE-2026-3609,…
 bc-security/beginners-guide-to-obfuscation
Hands-on red-team obfuscation workshop teaching AMSI bypass, ETW evasion, and payload obfuscation with PowerShell, Visual Basic, and C# to evade…
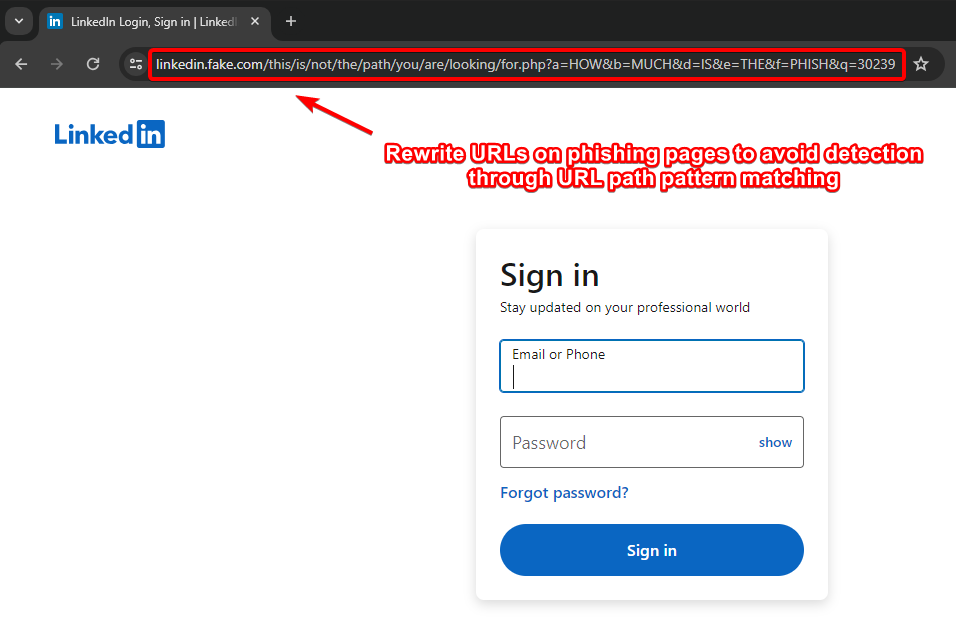 an0nud4y/evilginx-phishing-infra-setup
Evilginx Phishing Infrastructure Setup Guide - Securing Evilginx and Gophish Infrastructure, Removing IOCs, Phishing TTPs