

 mr-un1k0d3r/edrs
Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
 idov31/mrkaplan
PowerShell tool for red teamers that clears execution evidence by stopping event logging, removing file and registry artifacts, and saving timestamps…
 saadahla/anti-sandbox
C++ tool for detecting AnyRun sandbox environments, enabling malware to evade dynamic analysis and automated sandboxing systems.
 gryfman/dlpwn
Red Team tool for covert file exfiltration via Bluetooth audio transmission, encoding binary data into FLAC signals to bypass EDR, XDR, and DLP…
 m00nrise/processhider
Post-exploitation tool for hiding processes from monitoring applications
 shredzwho/ig-detective
OSINT tool researched and designed to hunt down IG handles
 robomotic/invoke-antivm
powershell tool for VM evasion
 mhdgning131/teletunnel
Bypassing EDR's with stealthy c++ telegram Bot and Telegram itself as C2 interface !
 gmh5225/f31
Tool for hiding Kali Linux on the network
 daem0nc0re/atomicsyscall
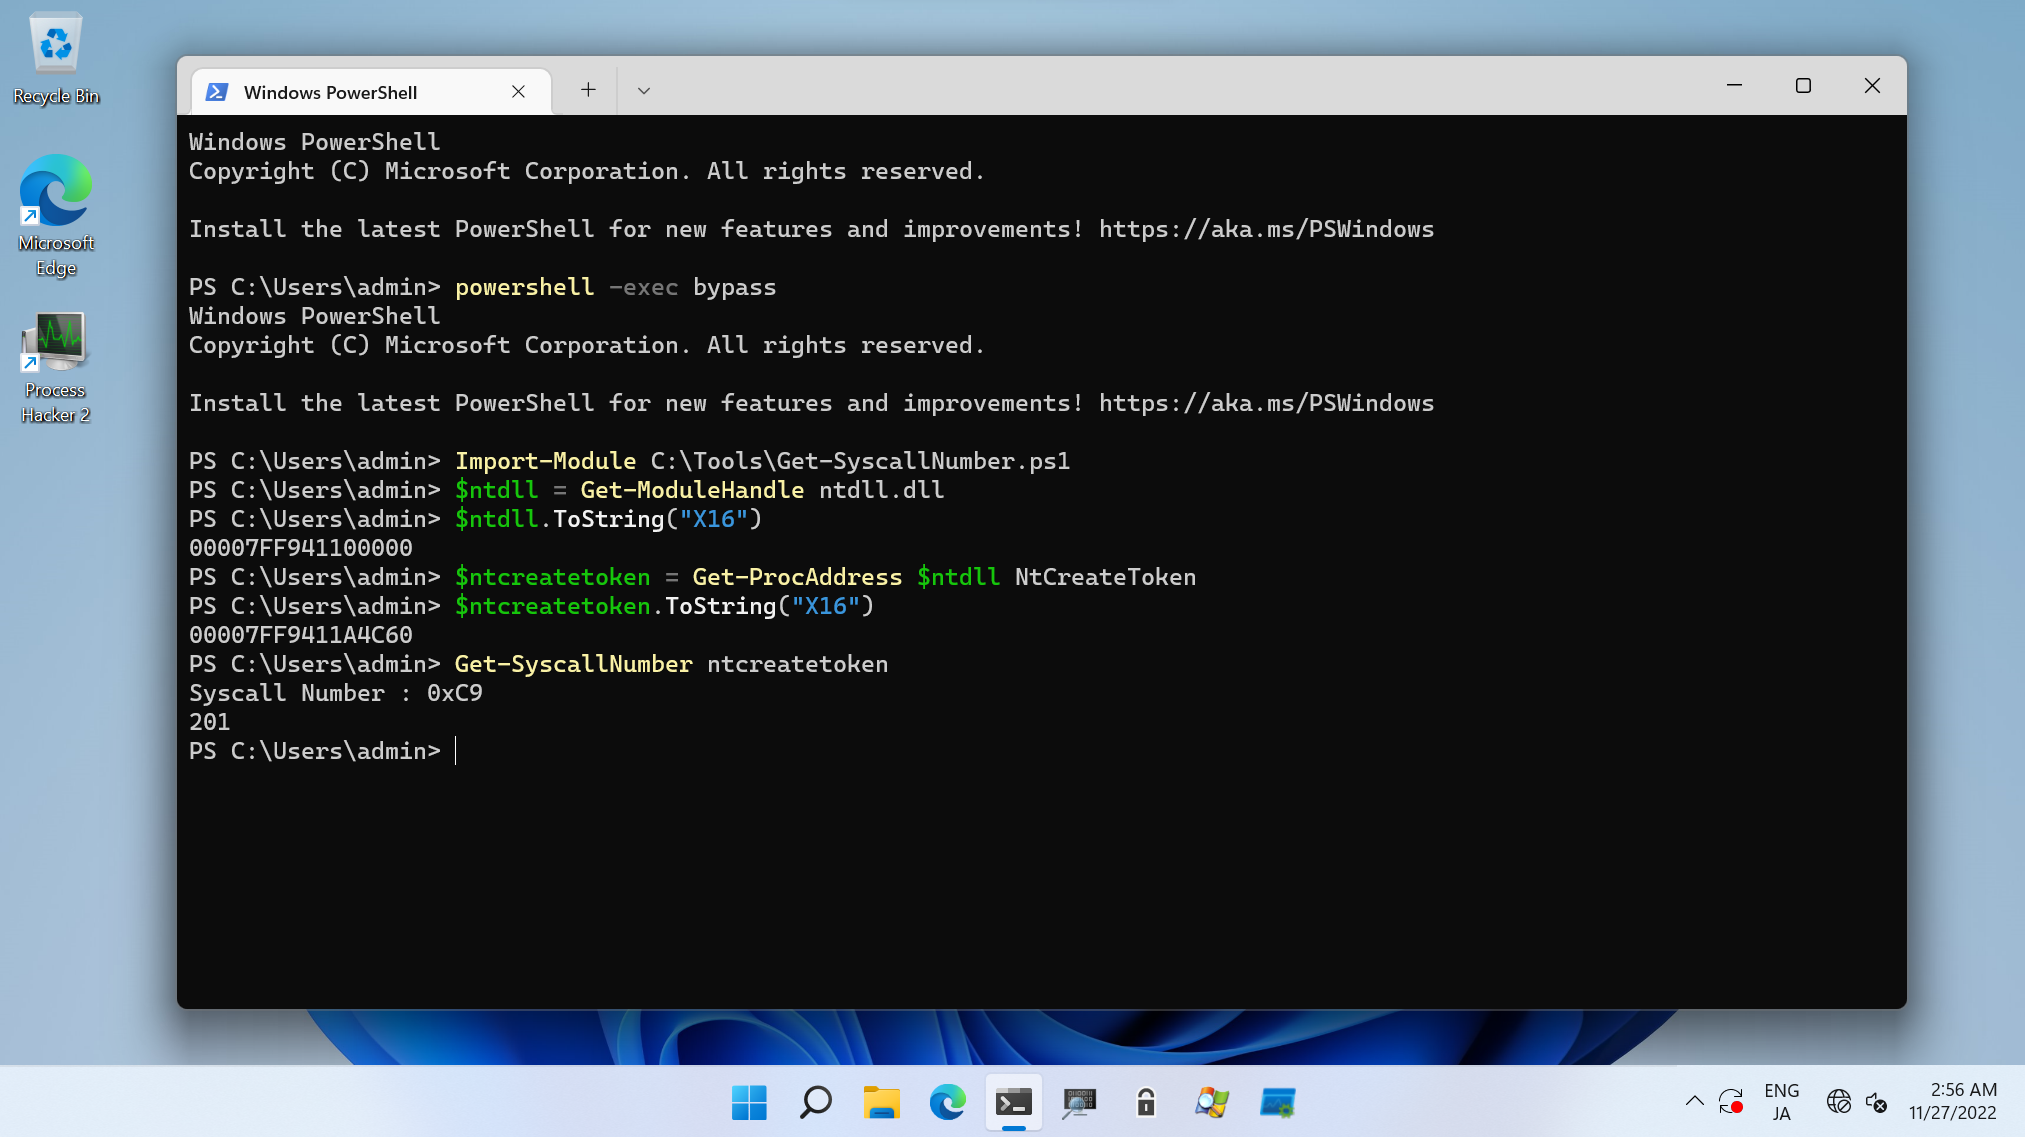
Tools and PoCs for Windows syscall investigation.
 netero1010/schedulerunner
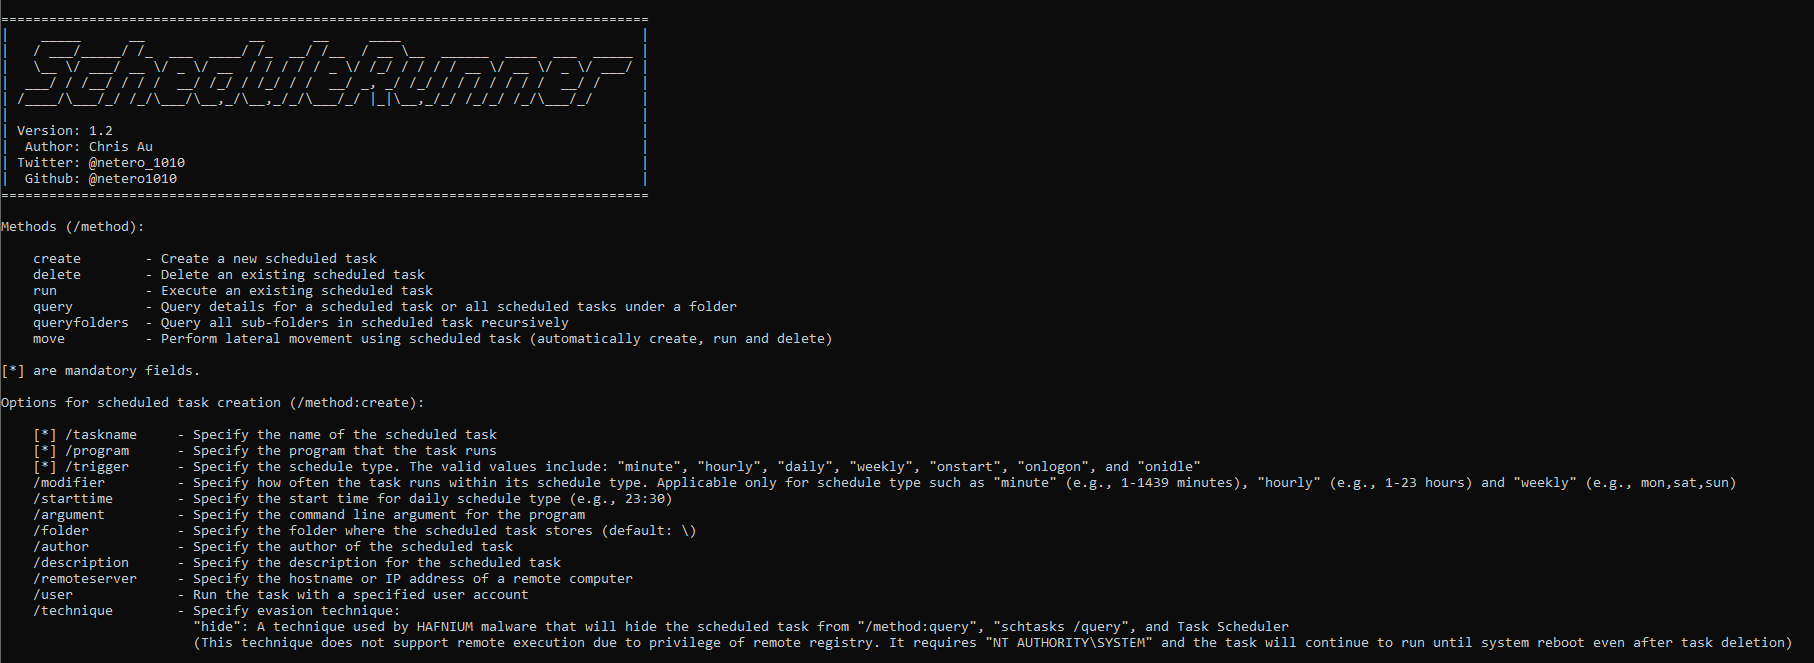
A C# tool with more flexibility to customize scheduled task for both persistence and lateral movement in red team operation
 optiv/freeze
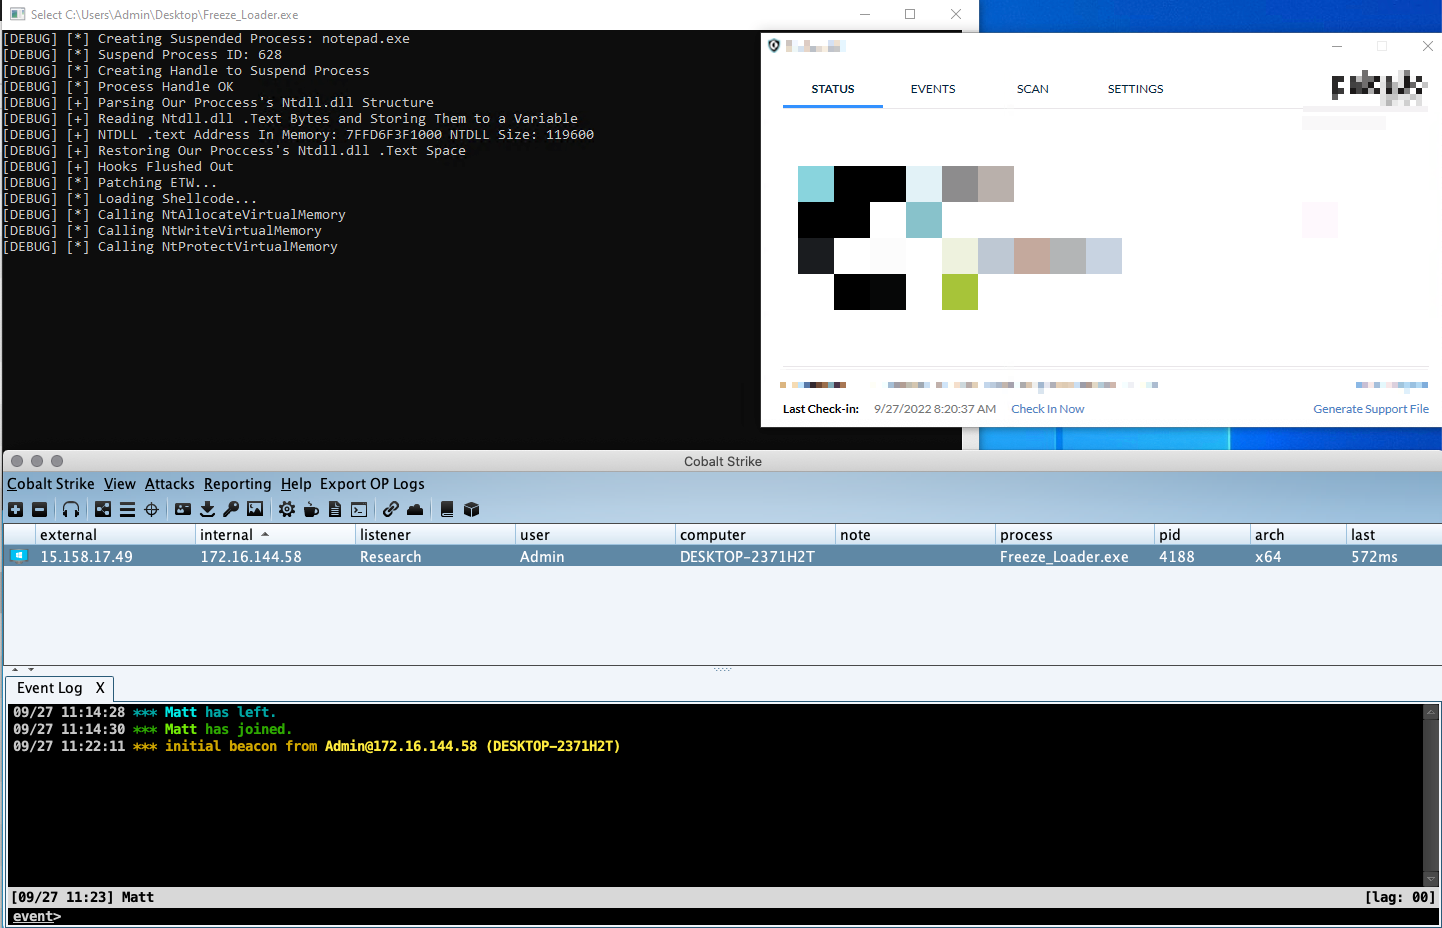
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 sn1r/forbidden-buster
A tool designed to automate various techniques in order to bypass HTTP 401 and 403 response codes and gain access to unauthorized areas in the…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
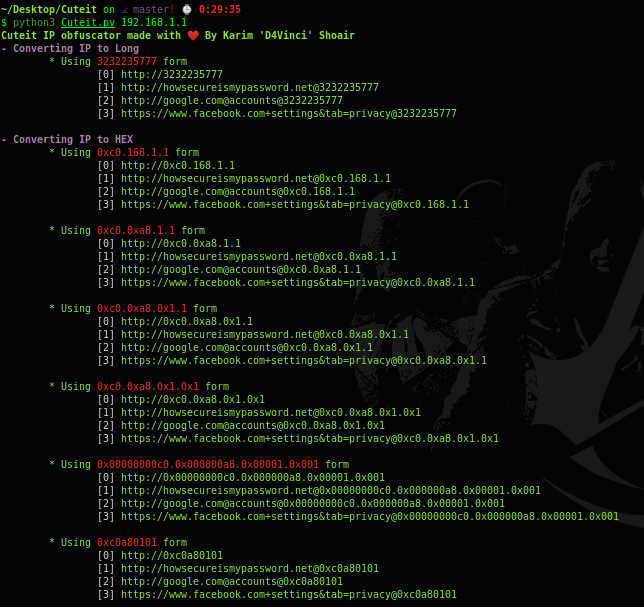 d4vinci/cuteit
IP obfuscator made to make a malicious ip a bit cuter