

MalDev
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
anti-boteducationencryption-decryption-tools+9
captmag/maldevCreation of multiple Malware tools consisting of evasion, enumeration and exploitation
 drk1wi/portspoof
Emulates open ports and service signatures across all 65535 TCP ports to slow reconnaissance, confuse scanners, and waste attacker resources with…
 cenobyte-vincit/memdumper
Abuses macOS debugger entitlements and DYLD_INSERT_LIBRARIES to dump or search a running process's memory while shifting EDR attribution to a signed…
 shredzwho/ig-detective
OSINT tool researched and designed to hunt down IG handles
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 garagehq/nightcrawler
Local AI powered red teamer on a phone
 luemmelsec/pentest-tools-collection
Curated collection of offensive security tools and commands for Active Directory attacks, C2, privilege escalation, obfuscation, and web pentesting.
 ge0rg3/requests-ip-rotator
A Python library to utilize AWS API Gateway's large IP pool as a proxy to generate pseudo-infinite IPs for web scraping and brute forcing.
 orevic21/wazuh-home-soc
Wazuh + Suricata SOC lab detecting real exploits (CVE-2011-2523) and brute-force attacks, with custom detection rules for gaps in default IDS…
 devploit/nomore403
🚫 Advanced tool for security researchers to bypass 403/40X restrictions through smart techniques and adaptive request manipulation. Fast. Precise.…
 lsecqt/portforwarder
TCP Port Forwarding Utility on C
 sentinelxofficial/cve-2025-55182
Pre-authentication RCE exploit for CVE-2025-55182 (React2Shell) targeting React Server Components. Features scanning, OAST verification, WAF bypass,…
 87achrafg-stack/cve-2026-48907
Exploits CVE-2025-9209 in WordPress by querying /wp-json/wp/v2/users, harvesting user keys, tokens, and cookies, bypassing Defender/Imunify360, and…
 kouf320/docker-lab-cve-2017-5638-cve-2021-41773
Docker-based multi-stage attack emulation lab demonstrating CVE-2017-5638 and CVE-2021-41773 exploitation, lateral movement, and Suricata IDS…
 depthsecurity/relayking-depth
Dominate the domain. Relay to royalty.
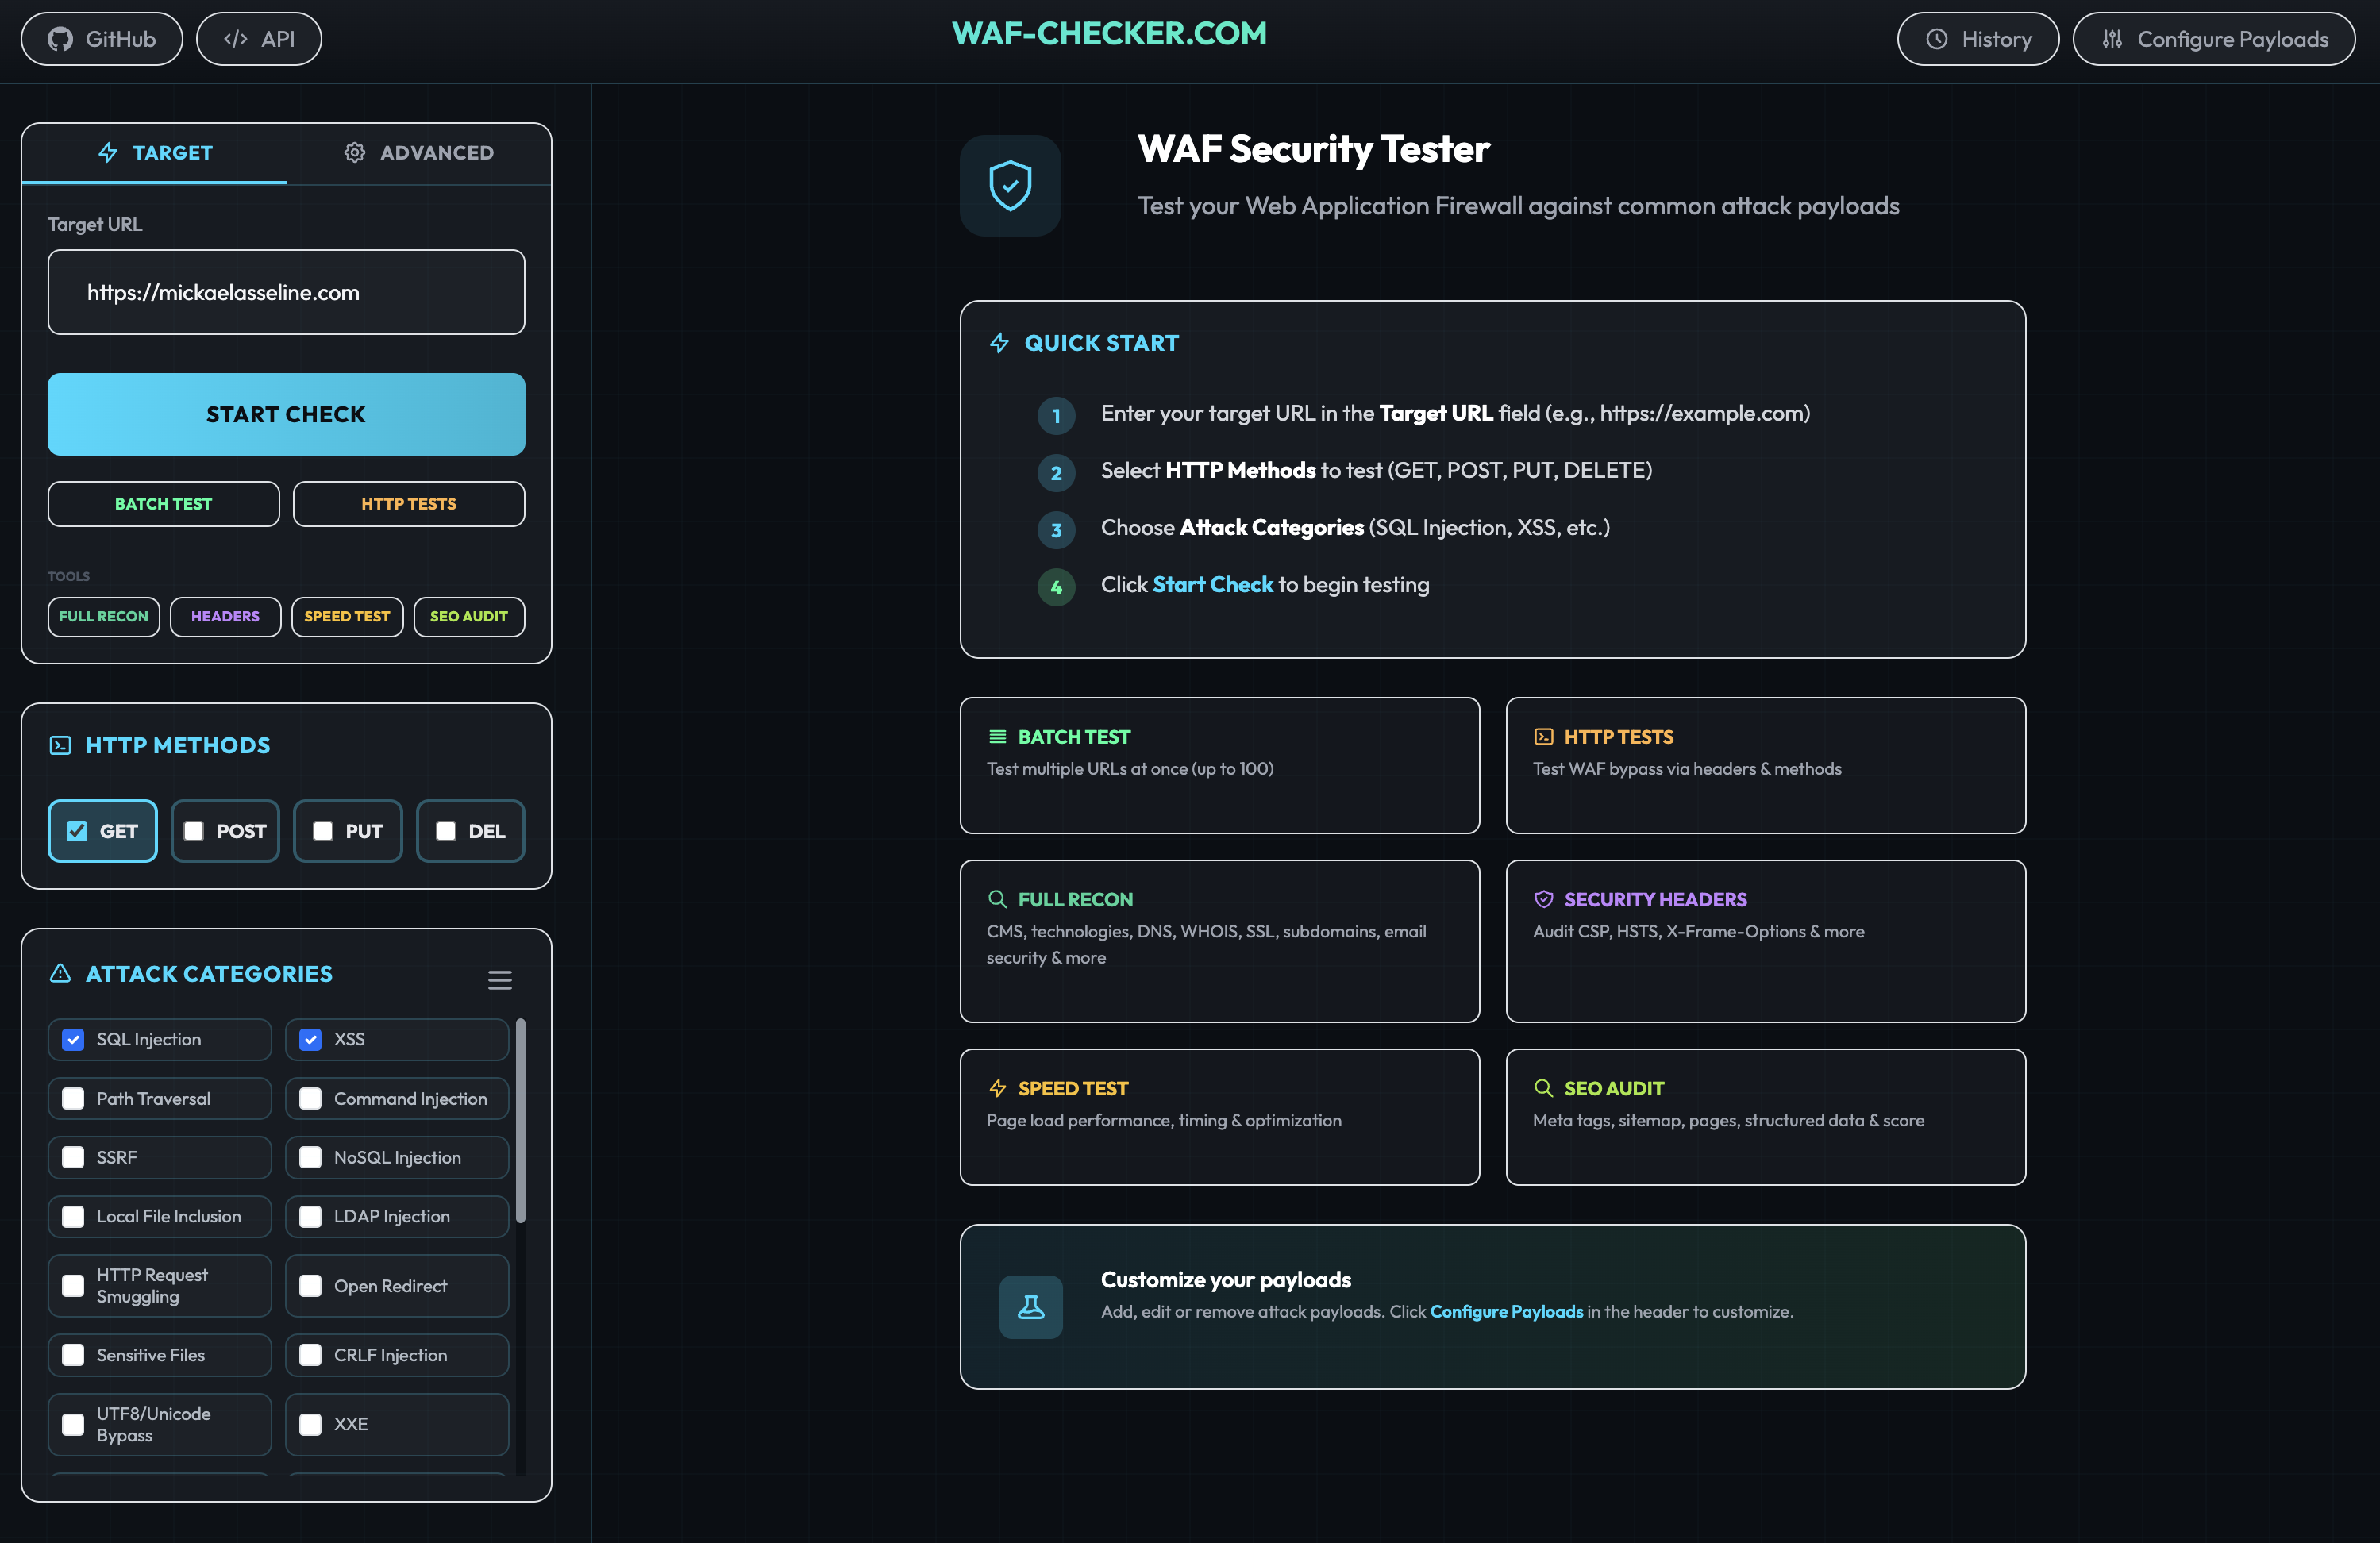 papamica/waf-checker
Tests your WAF with +160 payloads
 calebmadrigal/trackerjacker
Like nmap for mapping wifi networks you're not connected to, plus device tracking