Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
11 results
CrushFTP-AS2-Bypass-Research-CVE-2025-54309 preview

CrushFTP-AS2-Bypass-Research-CVE-2025-54309

GitHubsmileyface101/crushftp-as2-bypass-research-cve-2025-54309

Research on CrushFTP AS2 authentication bypass allowing unauthenticated admin access. Includes PoC scripts, detection rules, and technical analysis…

authenticationdefensive-toolseducation+6
7 days ago
CVE-2026-26718 preview

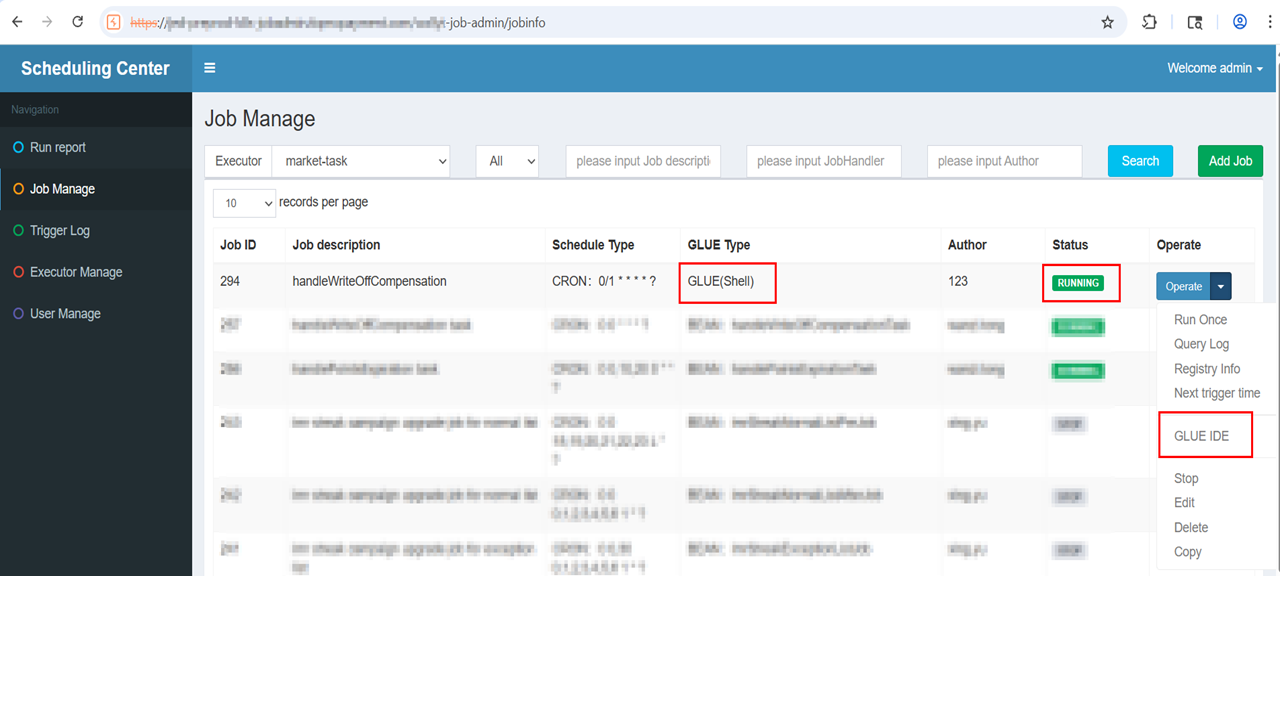
CVE-2026-26718

GitHubibrahim-sartawi/cve-2026-26718

A Cross-Site Request Forgery (CSRF) vulnerability exists in the xxl-job-admin web application that allows an attacker to perform unauthorized…

exploitationids-ips-evasionpenetration-testing+3
13 months ago
CVE-2022-30190-Follina-Lab preview

CVE-2022-30190-Follina-Lab

GitHubu1tr0nex/cve-2022-30190-follina-lab

Full exploit chain lab and Suricata IDS detection for CVE-2022-30190 (Follina) - MSDT RCE

command-and-controleducationexploitation+7
5 months ago
CTT-Serverless-RCE-v1.0---Convergent-Time-Theory-Enhanced-MCP-Exploit preview

CTT-Serverless-RCE-v1.0---Convergent-Time-Theory-Enhanced-MCP-Exploit

GitHubsimoesctt/ctt-serverless-rce-v1.0---convergent-time-theory-enhanced-mcp-exploit

Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…

ai-securitycloud-securitycommand-and-control+8
9 months ago
CVE-2025-29927 preview

CVE-2025-29927

GitHubzs1n/cve-2025-29927

PoC | NextJS Middleware 15.2.2 - Authorization Bypass

authentication-authorizationexploitationids-ips-evasion+3
1 year ago
CVE-2025-53770 preview

CVE-2025-53770

GitHubexfil0/cve-2025-53770

A sophisticated, wizard-driven Python exploit tool targeting CVE-2025-53770, a critical (CVSS 9.8) unauthenticated remote code execution (RCE)…

command-and-controlexploitationids-ips-evasion+7
51 year ago
CVE-2025-41646---Critical-Authentication-Bypass- preview

CVE-2025-41646---Critical-Authentication-Bypass-

GitHubgreenforcenetworks/cve-2025-41646---critical-authentication-bypass-

CVE-2025-41646 - Critical Authentication bypass

authentication-authorizationexploitationids-ips-evasion+5
11 year ago
Typecho-Multiple-Vulnerabilities preview

Typecho-Multiple-Vulnerabilities

GitHubcyberaz0r/typecho-multiple-vulnerabilities

Exploits for Typecho CVE-2024-35538, CVE-2024-35539 and CVE-2024-35540

exploitationids-ips-evasionpenetration-testing+3
12 years ago
cve-2022-27438 preview

cve-2022-27438

GitHubgar-re/cve-2022-27438

Proof-of-concept exploit for CVE-2022-27438, demonstrating remote code execution via spoofed update server in Advanced Installer 19.3. Includes DNS…

dns-analysisexploitationids-ips-evasion+3
3 years ago
irule-cve-2022-22965 preview

irule-cve-2022-22965

GitHubirgoncalves/irule-cve-2022-22965

F5 BIG-IP iRule providing mitigation against CVE-2022-22965 (Spring4Shell) remote code execution vulnerability in Java Spring Framework. Tested on…

exploitationids-ips-evasionmisconfiguration+3
24 years ago
CVE-2020-1938 preview

CVE-2020-1938

GitHubstreghstreek/cve-2020-1938

Detection rules for CVE-2020-1938 (Ghostcat) vulnerability in Apache Tomcat AJP connector, with Suricata and Bro signatures for network-based…

exploitationids-ips-evasionintrusion-detection+2
15 years ago