
evillimiter
 davidsonrafaelk/evillimiter
Tool that monitors, analyzes and limits the bandwidth of devices on the local network without administrative access
ids-ips-evasioninformation-gatheringnetwork-mapping+4
9
davidsonrafaelk/evillimiterTool that monitors, analyzes and limits the bandwidth of devices on the local network without administrative access
 codewhitesec/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
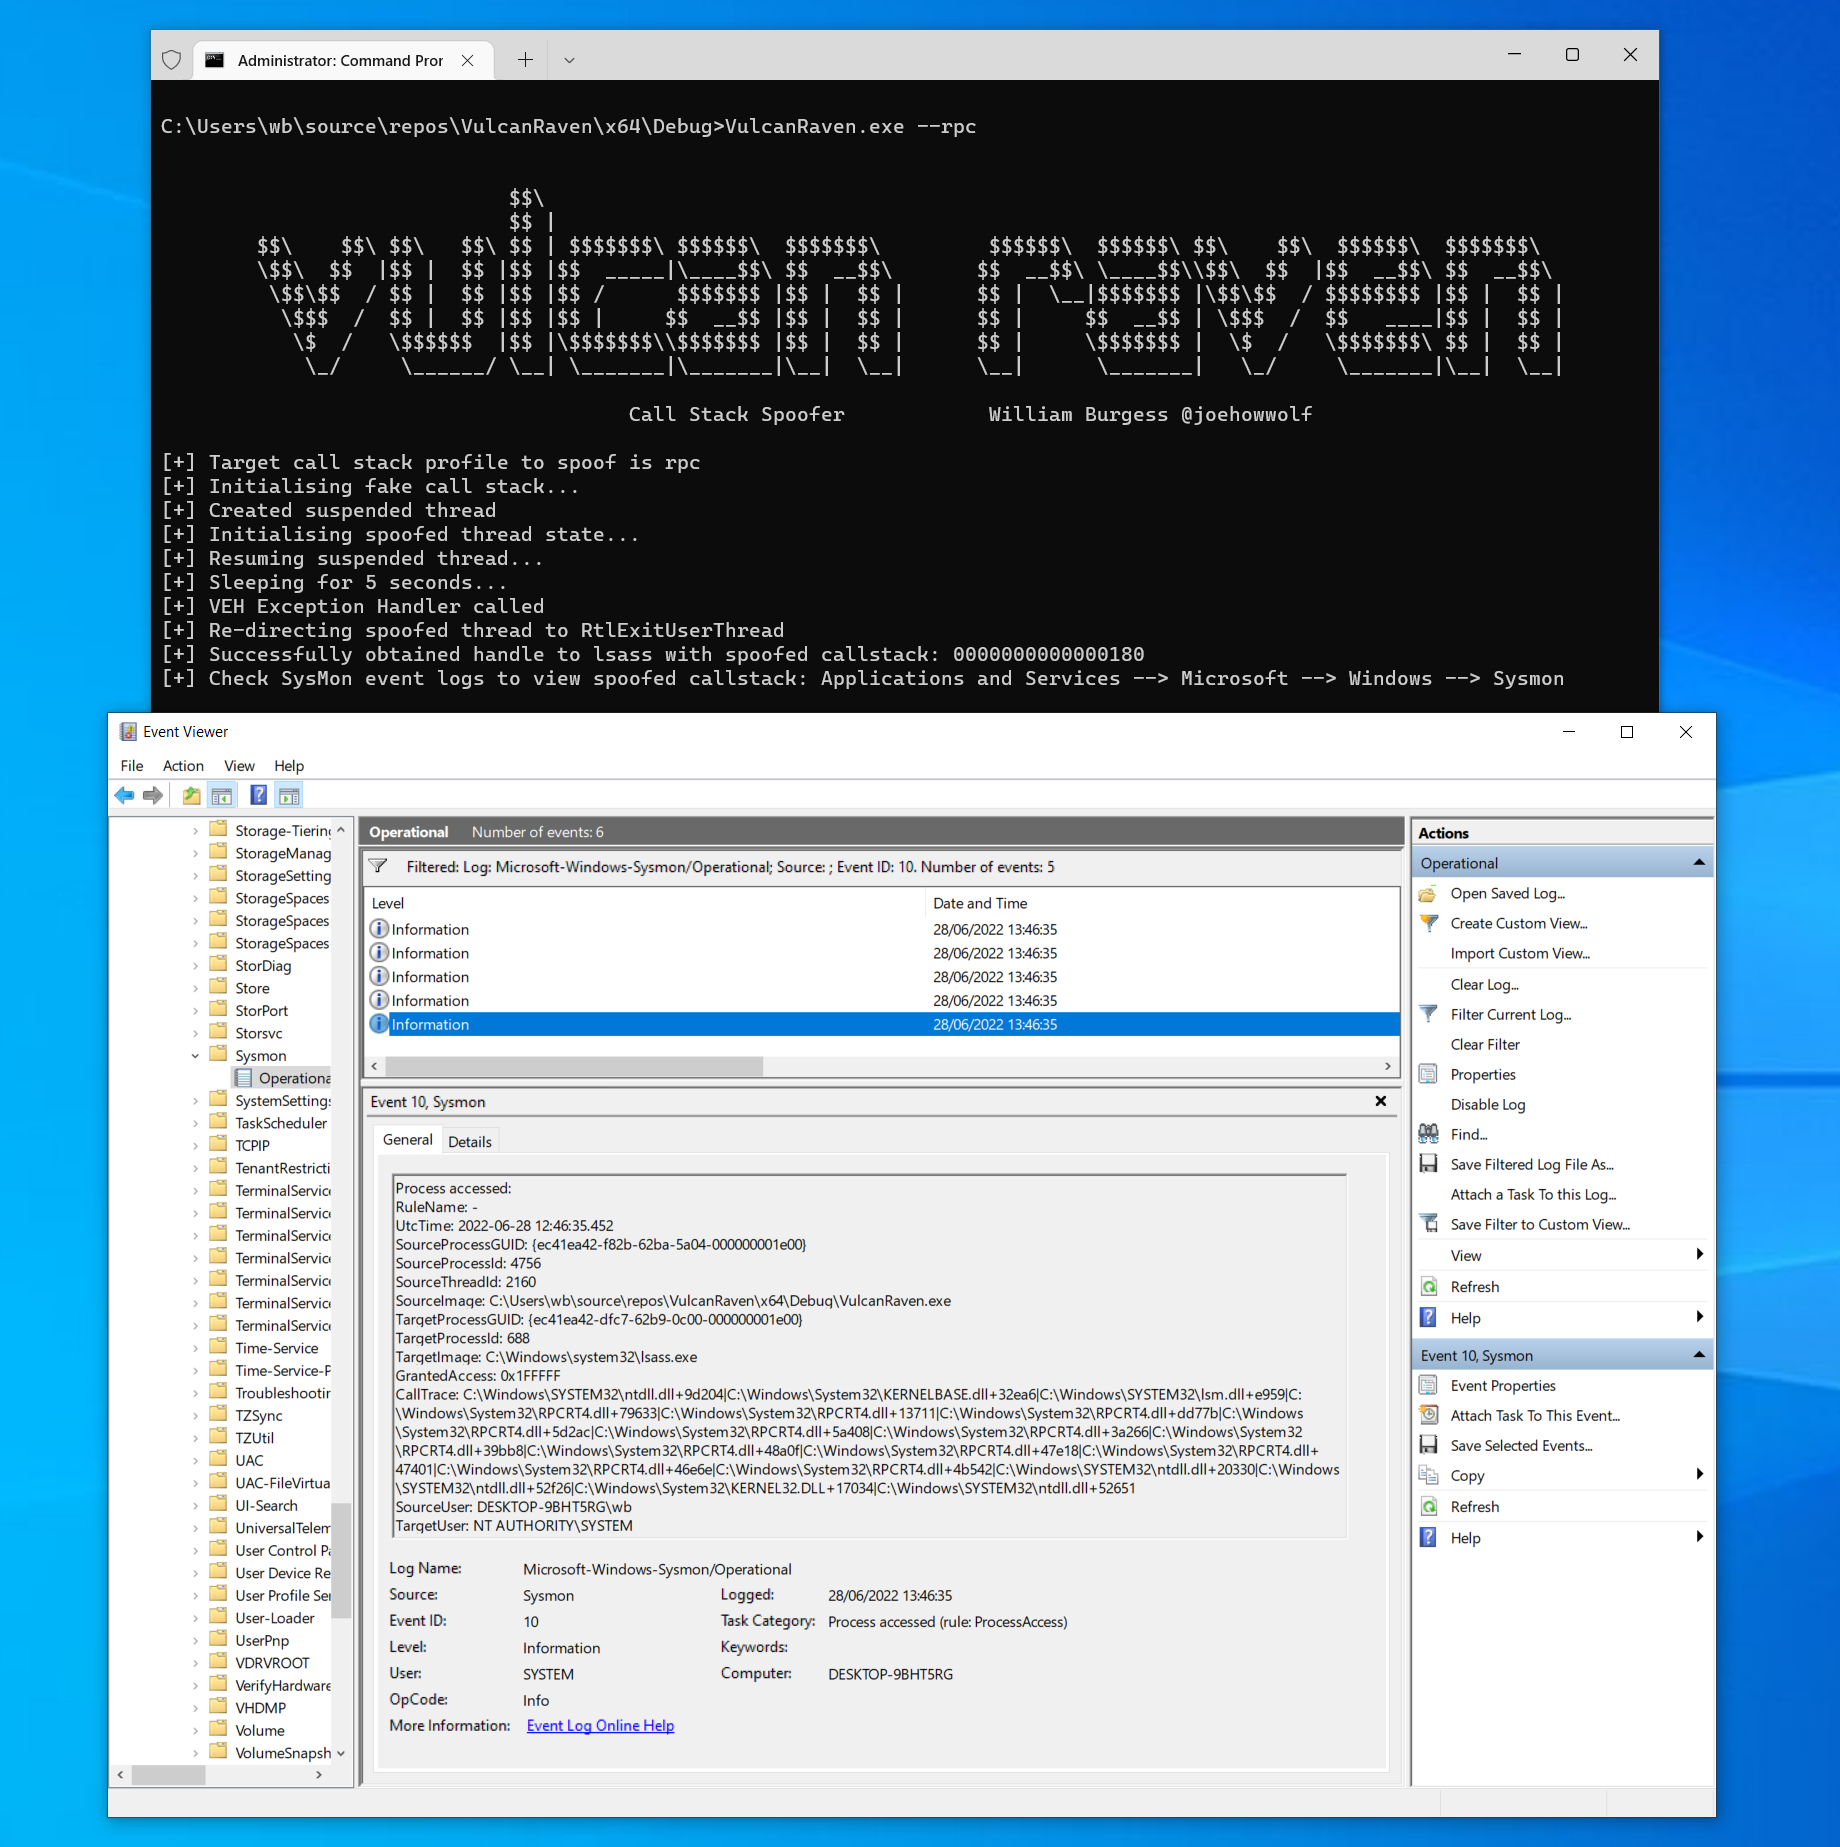 withsecurelabs/callstackspoofer
A PoC implementation for spoofing arbitrary call stacks when making sys calls (e.g. grabbing a handle via NtOpenProcess)
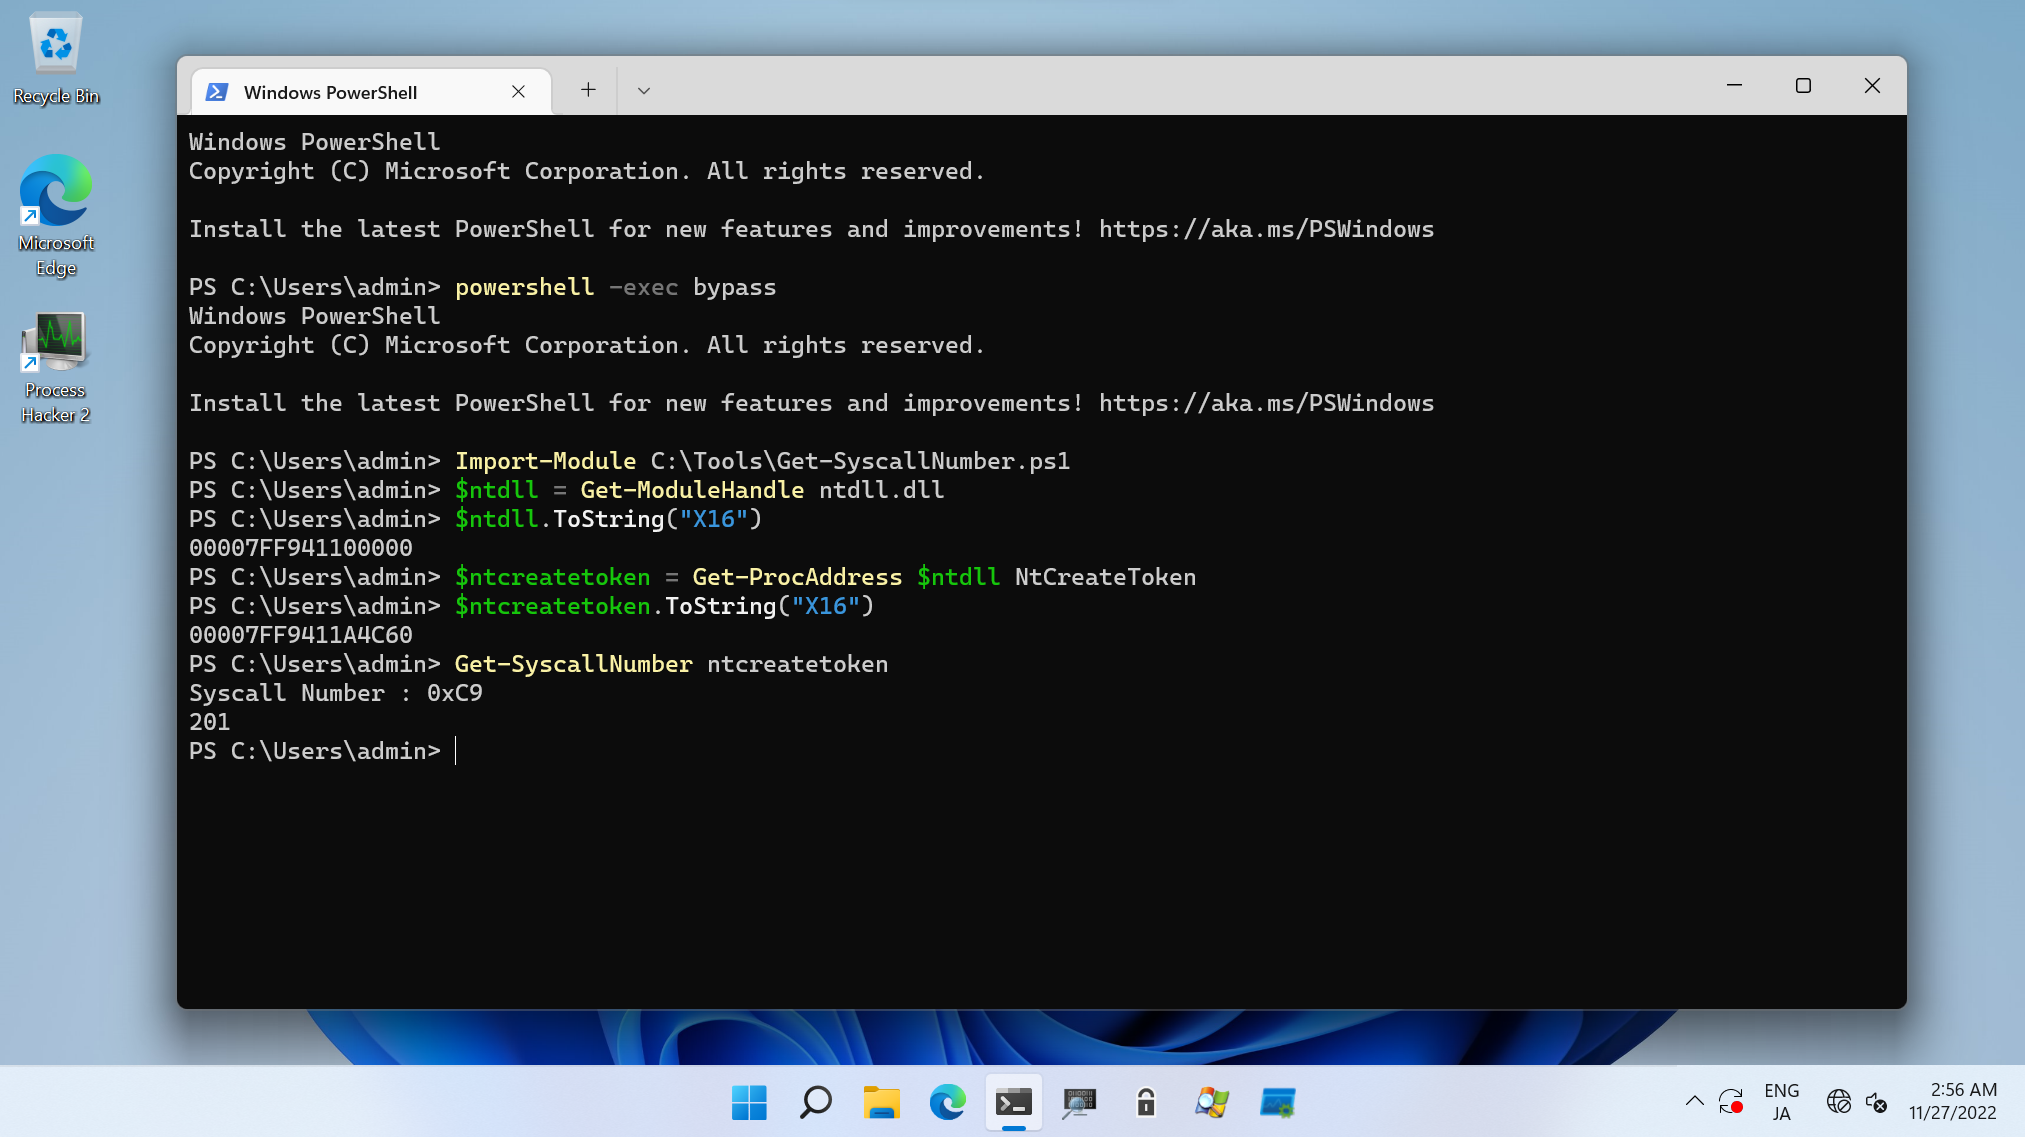 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
 rad9800/wtsrm2
Header-only C++17 library for evasive Windows development: compile-time API hashing, DLL unhooking, hardware breakpoint clearing, VEH removal, and…
 ps1337/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
 pard0p/callstackspoofingpoc
C++ self-Injecting dropper based on various EDR evasion techniques.
 rasta-mouse/cswhispers
Source generator to add D/Invoke and indirect syscall methods to a C# project.
 bc-security/ironsharppack
IronSharpPack is a repo of popular C# projects that have been embedded into IronPython scripts that execute an AMSI bypass and then reflective load…
 opnsense/core
OPNsense GUI, API and systems backend
 toperaproject/topera
IPv6 analysis tool: the other side
 rofl0r/proxychains-ng
proxychains ng (new generation) - a preloader which hooks calls to sockets in dynamically linked programs and redirects it through one or more…
 threatexpress/cs2modrewrite
Convert Cobalt Strike profiles to modrewrite scripts
 xkiian/awswaf
AWS WAF Solver, full reverse implemented in 100% Python & Golang.
 umidguluzada/cyberdefense-lab
A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.