
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
97 results
convoC2 preview

convoC2

GitHubcxnturi0n/convoc2

C2 infrastructure over Microsoft Teams.

command-and-controldata-exfiltrationids-ips-evasion+6
7591 year ago
no-access-protection-x86 preview

no-access-protection-x86

GitHubgmh5225/no-access-protection-x86

It encrypts the text section and set the protection to NO_ACCESS.
anti-botbinary-analysisdefensive-tools+4
13 years ago
glimmer preview

glimmer

GitHublinnemanlabs/glimmer

Adversary emulation and C2 framework for security research
command-and-controlcryptographydata-exfiltration+8
65 months ago
veneficus preview

veneficus

GitHubabraxas/veneficus

Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.

command-and-controldata-exfiltrationids-ips-evasion+8
211h 35m ago
iodine preview

iodine

GitHubyarrick/iodine

Tunnel IPv4 data through DNS servers to bypass firewall restrictions and provide covert network access for penetration testing.
command-and-controldata-exfiltrationids-ips-evasion+4
8.0k1 day ago
bedaisy-bypass preview

bedaisy-bypass

GitHubgmh5225/bedaisy-bypass

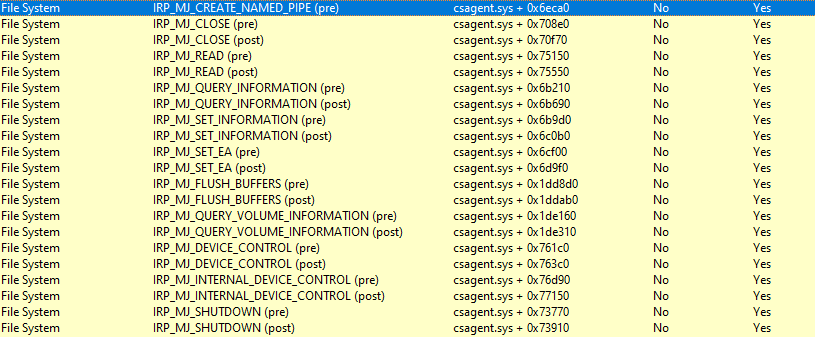
Kernel-mode hook that intercepts, decrypts, and nullifies BEDaisy-to-service report traffic to suppress anti-cheat detection on UEFI and non-UEFI…
adversarial-attackids-ips-evasionred-teaming
53 years ago
Dumpy preview

Dumpy

GitHubkudaes/dumpy

Reuse open handles to dynamically dump LSASS.
data-exfiltrationexploitationids-ips-evasion+3
2462 years ago
EDRs preview

EDRs

GitHubmr-un1k0d3r/edrs

Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.

binary-analysiscurated-resourcesids-ips-evasion+3
2.2k6 months ago
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
5.3k1 month ago
RunAsWinTcb preview

RunAsWinTcb

GitHubtastypepperoni/runaswintcb

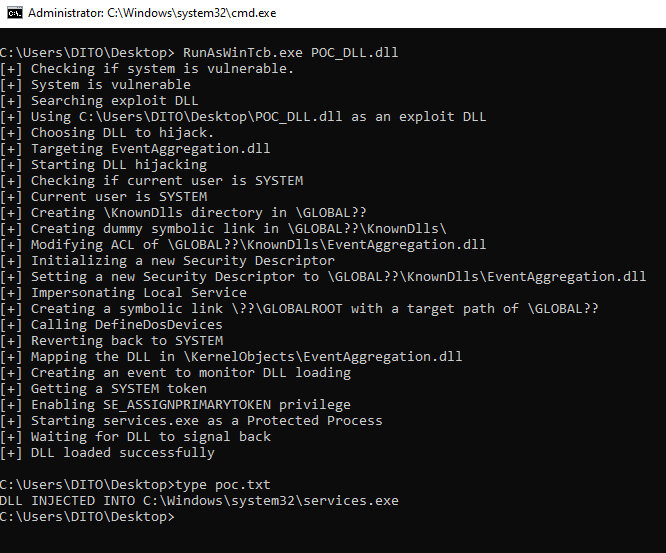
Proof-of-concept C exploit that runs a DLL with WinTcb-Light protection from userland, demonstrating a Windows privilege-escalation primitive and…
exploitationids-ips-evasionpost-exploitation+2
1384 years ago
Burp2Malleable preview

Burp2Malleable

GitHubcodextf2/burp2malleable

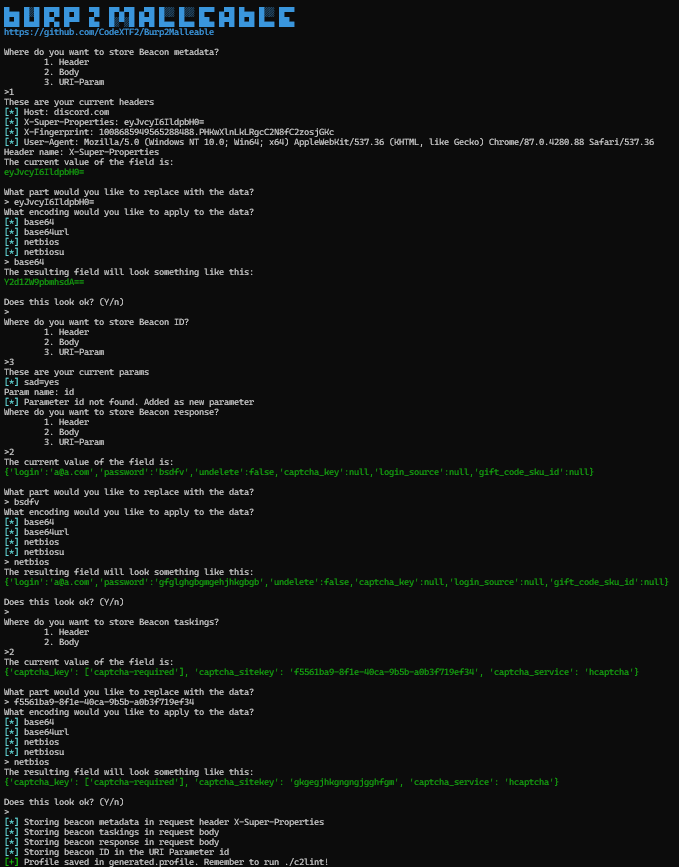
Quick python utility I wrote to turn HTTP requests from burp suite into Cobalt Strike Malleable C2 profiles
command-and-controlids-ips-evasionpayload-development+2
4173 years ago
CallMeWin32kDriver preview

CallMeWin32kDriver

GitHubgmh5225/callmewin32kdriver

Load your driver like win32k.sys
adversarial-attackids-ips-evasionpost-exploitation+1
2574 years ago
PowerSploit preview

PowerSploit

GitHubzerodaylab/powersploit

PowerSploit - A PowerShell Post-Exploitation Framework
command-and-controldata-exfiltrationexploit-frameworks+7
2424 years ago
Cronos preview

Cronos

GitHubidov31/cronos

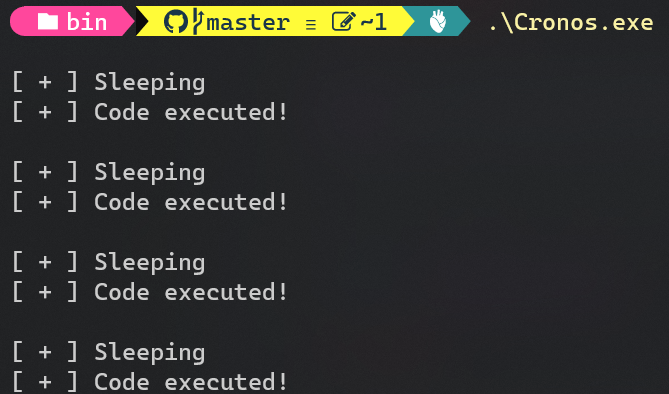
PoC for a sleep obfuscation technique leveraging waitable timers to evade memory scanners.
cryptographyids-ips-evasionpayload-development+2
6303 years ago
AtomicSyscall preview

AtomicSyscall

GitHubdaem0nc0re/atomicsyscall

Tools and PoCs for Windows syscall investigation.
adversarial-attackbinary-analysiseducation+3
36411 months ago
secret_handshake preview

secret_handshake

GitHubjconwell/secret_handshake

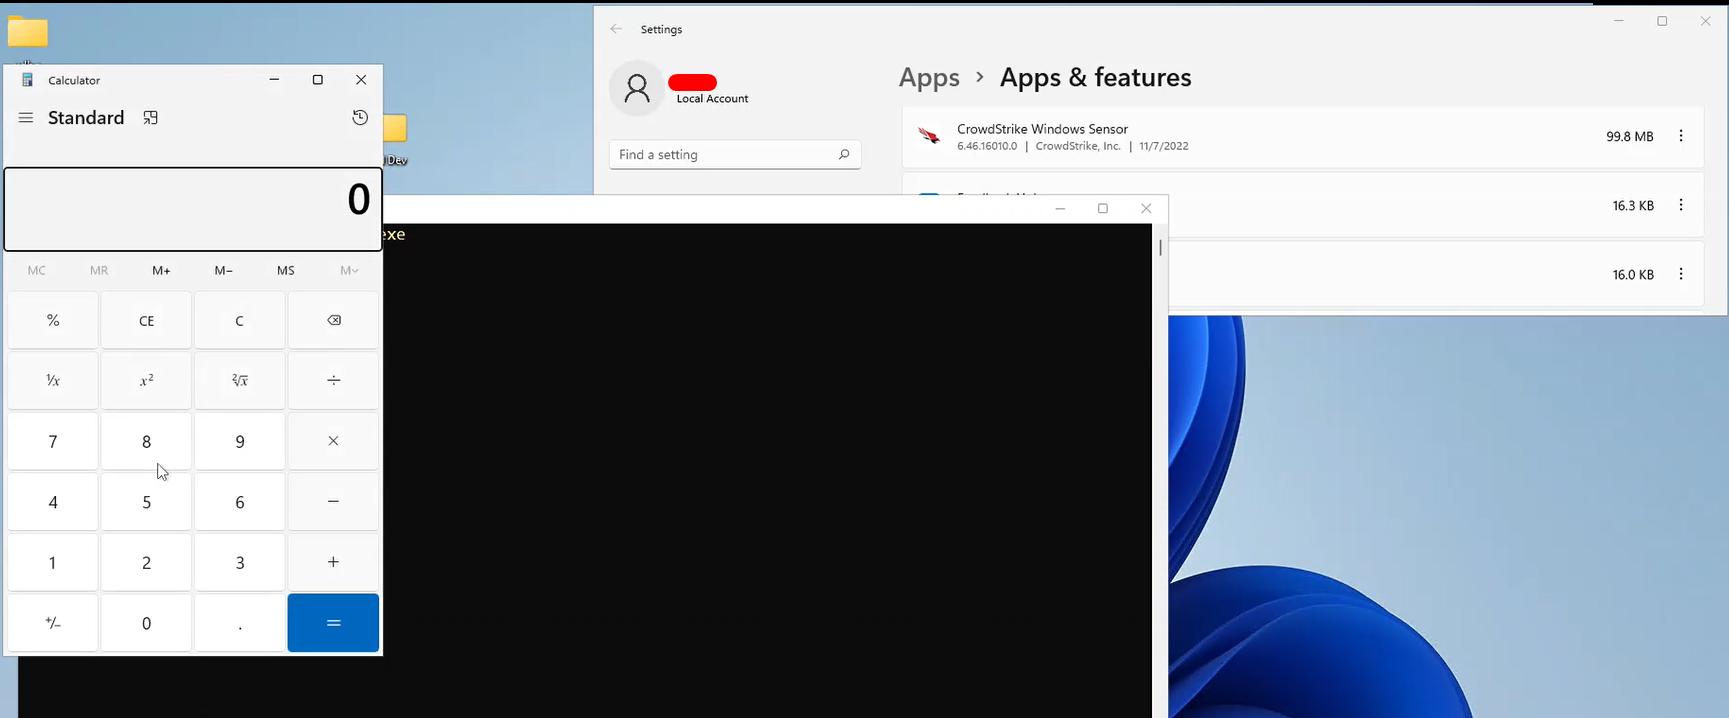
A prototype malware C2 channel using x509 certificates over mTLS
command-and-controldata-exfiltrationids-ips-evasion+1
1532 years ago
D1rkLdr preview

D1rkLdr

GitHubsaadahla/d1rkldr

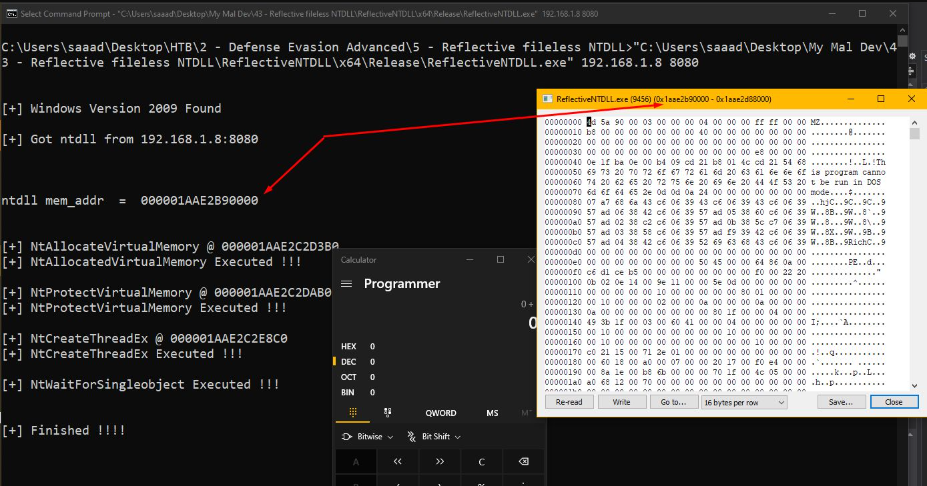
Shellcode Loader with Indirect Dynamic syscall Implementation , shellcode in MAC format, API resolving from PEB, Syscall calll and syscall…
ids-ips-evasionpayload-developmentred-teaming+1
3223 years ago
NTDLLReflection preview

NTDLLReflection

GitHubsaadahla/ntdllreflection

Bypass Userland EDR hooks by Loading Reflective Ntdll in memory from a remote server based on Windows ReleaseID to avoid opening a handle to ntdll ,…

adversarial-attackids-ips-evasionpost-exploitation+1
3063 years ago
Previous123456Next