
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
18 results
TamperingSyscalls preview

TamperingSyscalls

GitHubrad9800/tamperingsyscalls

C++ library that retrieves and spoofs Windows syscall arguments using hardware breakpoints and exception handlers to subvert EDR telemetry.
ids-ips-evasionpayload-developmentpost-exploitation+1
507
4 years ago
Venom preview

Venom

GitHubidov31/venom

Venom is a library that meant to perform evasive communication using stolen browser socket
command-and-controlids-ips-evasionred-teaming+1
3953 years ago
Kernel_VADInjector preview

Kernel_VADInjector

GitHublleon1435/kernel_vadinjector

Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver

adversarial-attackids-ips-evasionpayload-development+3
542 years ago
process-enumeration-stealth preview

process-enumeration-stealth

GitHublloydlabs/process-enumeration-stealth

Stealth Windows process enumeration PoC that lists PIDs using NTFS via NtQueryInformationFile, bypassing standard monitoring APIs and enabling EDR…
ids-ips-evasioninformation-gatheringpost-exploitation+2
842 years ago
Bypass_AV preview

Bypass_AV

GitHubhkl1x/bypass_av

Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…

ids-ips-evasionpayload-developmentpayload-generation+2
10811 months ago
AV-EDR-Lab-Environment-Setup preview

AV-EDR-Lab-Environment-Setup

GitHuban0nud4y/av-edr-lab-environment-setup

AV/EDR Lab environment setup references to help in Malware development

curated-resourcesdefensive-toolseducation+6
4711 year ago
IIS-Backdoor preview

IIS-Backdoor

GitHubnu11secur1ty/iis-backdoor

Stealthy IIS backdoor using hidden ISAPI filter for persistent remote access, data exfiltration, and on-the-fly exploit injection via custom HTTP…

command-and-controlexploitationids-ips-evasion+4
346 years ago
GhostDriver preview

GhostDriver

GitHubblacksnufkin/ghostdriver

yet another AV killer tool using BYOVD
defensive-toolsexploitationids-ips-evasion+4
3142 years ago
CVE-2020-1472-ZeroLogon-Demo-Detection-Mitigation preview

CVE-2020-1472-ZeroLogon-Demo-Detection-Mitigation

GitHubtdevworks/cve-2020-1472-zerologon-demo-detection-mitigation

Educational demo of CVE-2020-1472 (ZeroLogon) detection using Windows Event Logs and Suricata IDS, plus mitigation via Windows Updates. Includes…
educationids-ips-evasionintrusion-detection+3
1 year ago
SilentButDeadly preview

SilentButDeadly

GitHubloosehose/silentbutdeadly

SilentButDeadly is a network communication blocker specifically designed to neutralize EDR/AV software by preventing their cloud connectivity using…
command-and-controldefensive-toolsexploitation+7
45310 months ago
thirdeye preview

thirdeye

GitHublofcz/thirdeye

The Third Eye 👁⃤

anti-botdefensive-toolsids-ips-evasion+2
442 months ago
AntiVE-BehaviorWatch preview

AntiVE-BehaviorWatch

GitHubnirvanaon/antive-behaviorwatch

Embedded GRU neural network for real-time human behavior verification via mouse movement analysis, detecting automated analysis systems, sandboxes,…
anti-botdynamic-analysis-sandboxingids-ips-evasion+3
402 months ago
udp2raw preview

udp2raw

GitHubwangyu-/udp2raw

A Tunnel which Turns UDP Traffic into Encrypted UDP/FakeTCP/ICMP Traffic by using Raw Socket,helps you Bypass UDP FireWalls(or Unstable UDP…
encryption-decryption-toolsids-ips-evasionnetwork-security
8.6k11 months ago
FUD-UUID-Shellcode preview

FUD-UUID-Shellcode

GitHubbl4ckm1rror/fud-uuid-shellcode

C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…
binary-exploitationdefensive-toolsexploitation+6
3343 years ago
Killer preview

Killer

GitHub0xhossam/killer

Killer is a super simple tool designed to bypass AV/EDR security tools using various evasive techniques and used by Patchwork group.
anti-boteducationexploitation+4
8462 years ago
AzureC2Relay preview

AzureC2Relay

GitHubflangvik/azurec2relay

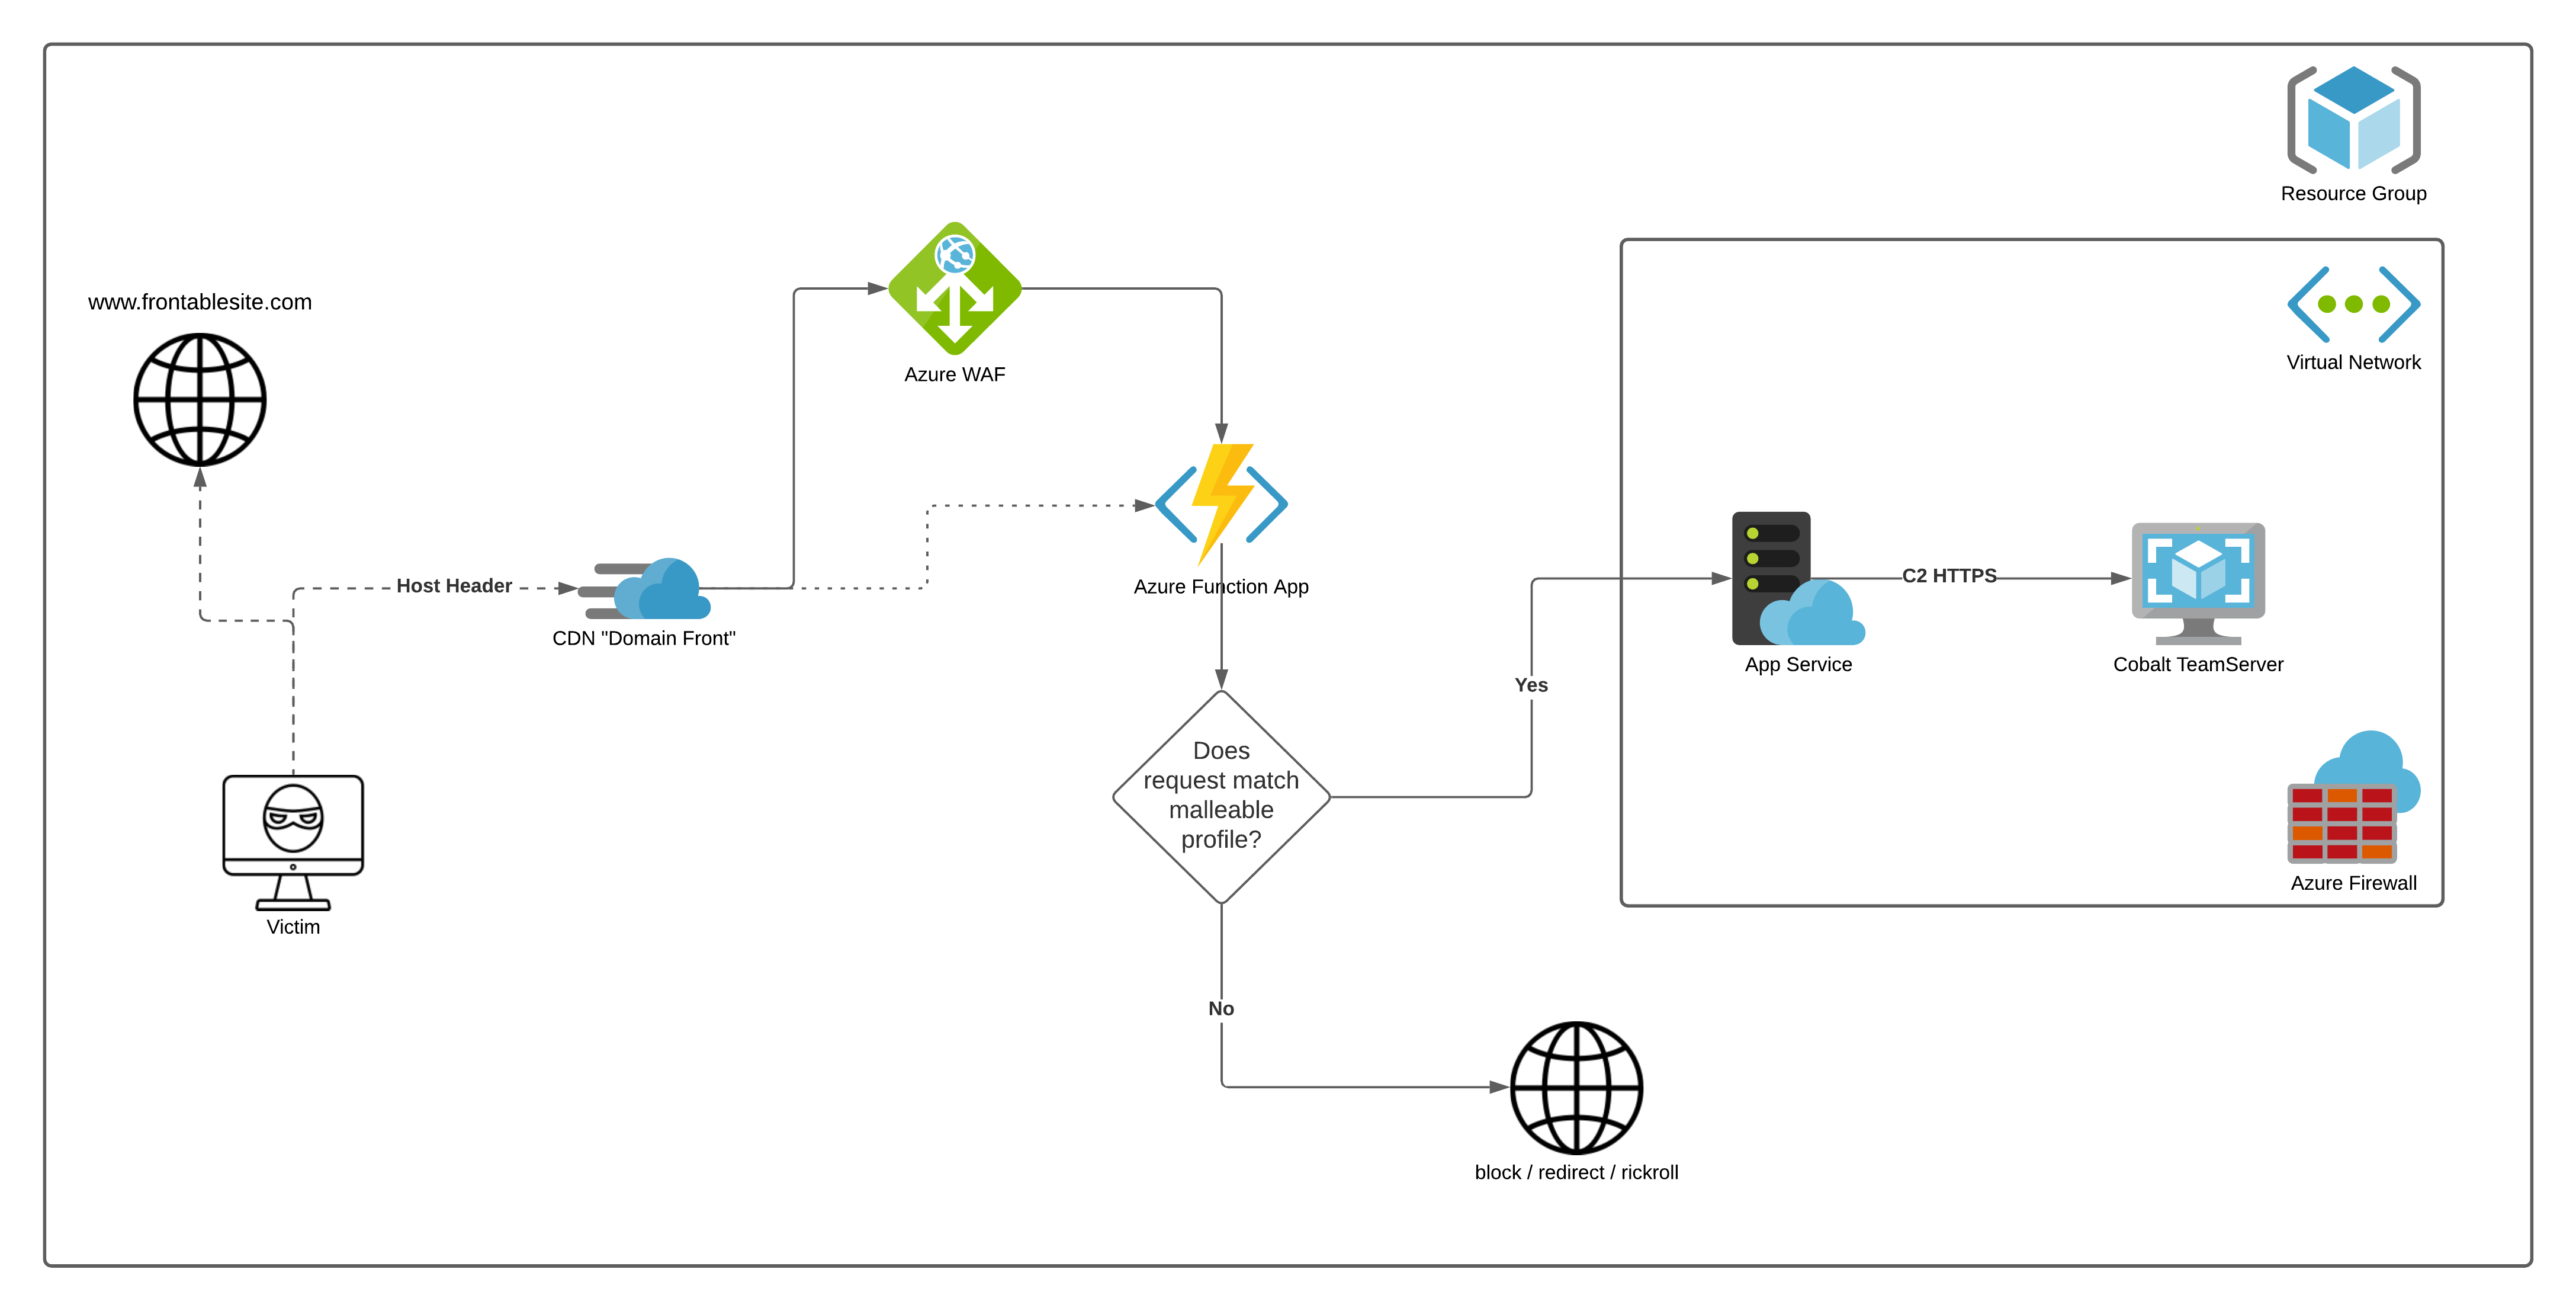
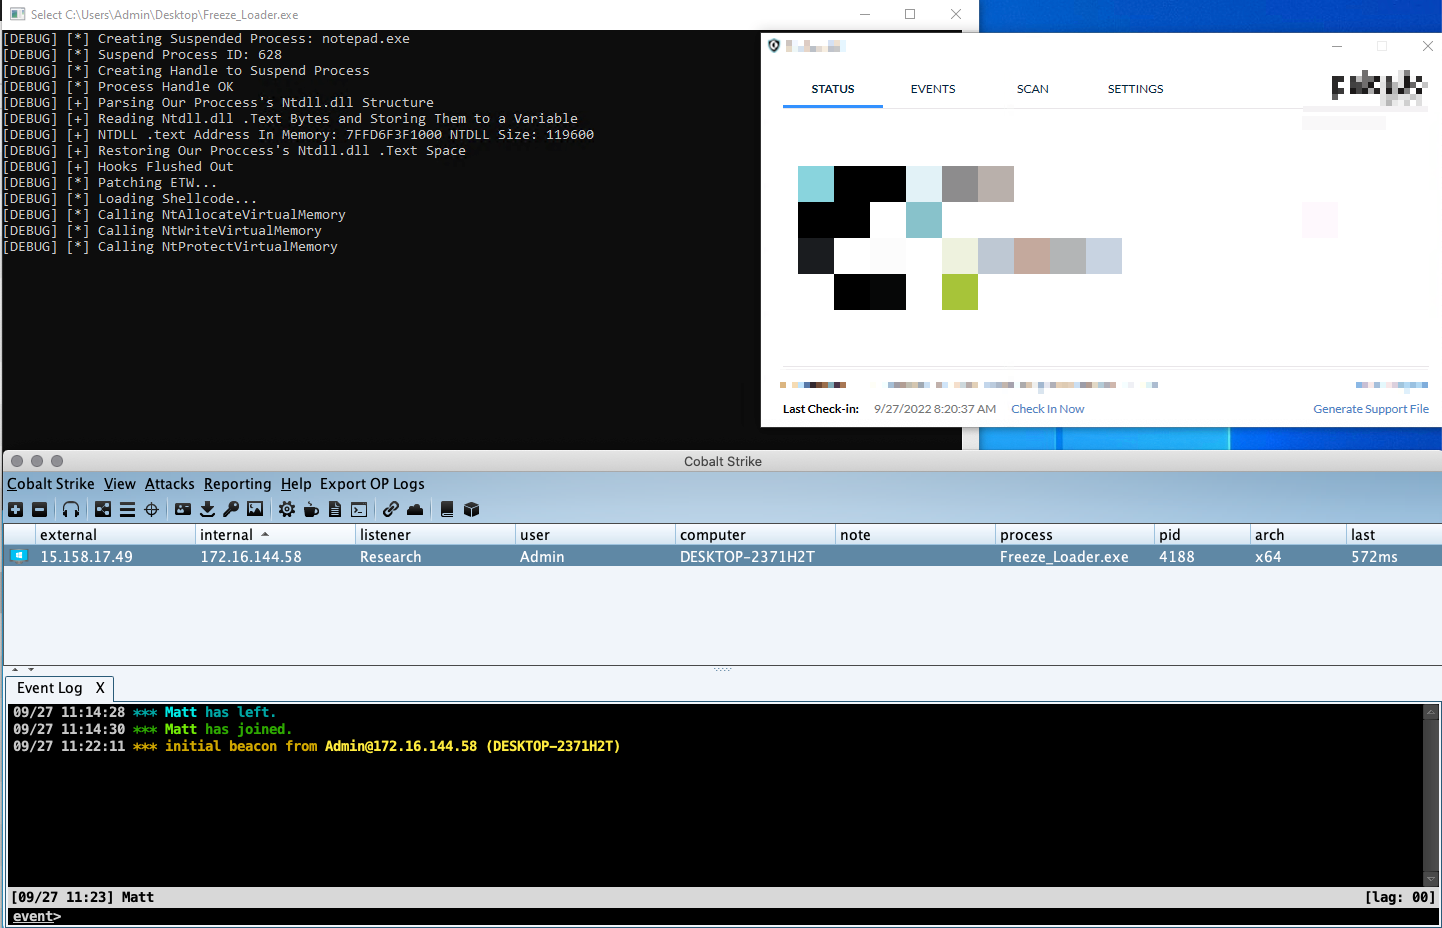
Azure Function that validates and relays Cobalt Strike beacon traffic using malleable C2 profiles, redirecting invalid requests to a decoy site and…
cloud-securitycommand-and-controlids-ips-evasion+2
2335 years ago
Freeze preview
Archived

Freeze

GitHuboptiv/freeze

Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
exploit-frameworksids-ips-evasionpayload-development+8
1.5k3 years ago
MeterPwrShell preview
Archived

MeterPwrShell

GitHubgetrektboy724/meterpwrshell

Automated Tool That Generates The Perfect Meterpreter Powershell Payload

command-and-controlexploit-frameworksids-ips-evasion+7
2275 years ago