
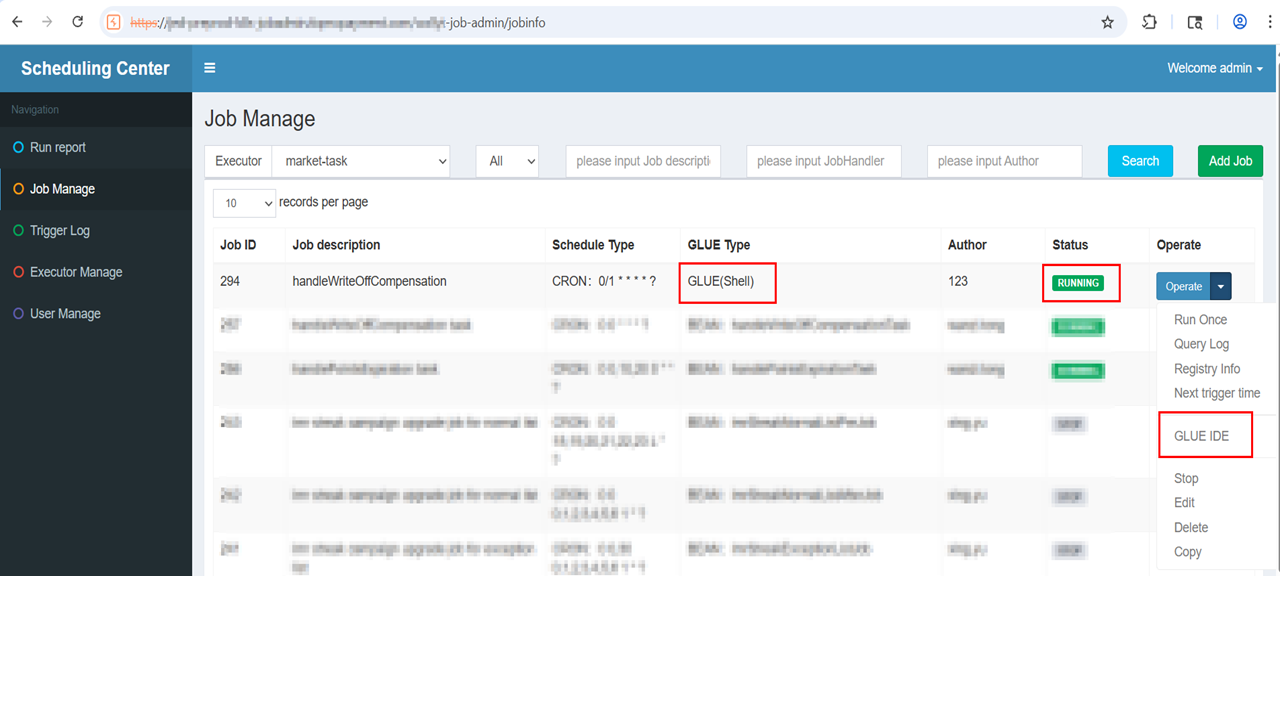
CVE-2026-26718
 ibrahim-sartawi/cve-2026-26718
A Cross-Site Request Forgery (CSRF) vulnerability exists in the xxl-job-admin web application that allows an attacker to perform unauthorized…
exploitationids-ips-evasionpenetration-testing+3
1
ibrahim-sartawi/cve-2026-26718A Cross-Site Request Forgery (CSRF) vulnerability exists in the xxl-job-admin web application that allows an attacker to perform unauthorized…
 greenforcenetworks/cve-2025-41646---critical-authentication-bypass-
CVE-2025-41646 - Critical Authentication bypass
 zs1n/cve-2025-29927
PoC | NextJS Middleware 15.2.2 - Authorization Bypass
 u1tr0nex/cve-2022-30190-follina-lab
Full exploit chain lab and Suricata IDS detection for CVE-2022-30190 (Follina) - MSDT RCE
 streghstreek/cve-2020-1938
Detection rules for CVE-2020-1938 (Ghostcat) vulnerability in Apache Tomcat AJP connector, with Suricata and Bro signatures for network-based…
 gar-re/cve-2022-27438
Proof-of-concept exploit for CVE-2022-27438, demonstrating remote code execution via spoofed update server in Advanced Installer 19.3. Includes DNS…
 exfil0/cve-2025-53770
A sophisticated, wizard-driven Python exploit tool targeting CVE-2025-53770, a critical (CVSS 9.8) unauthenticated remote code execution (RCE)…
 irgoncalves/irule-cve-2022-22965
F5 BIG-IP iRule providing mitigation against CVE-2022-22965 (Spring4Shell) remote code execution vulnerability in Java Spring Framework. Tested on…
 cyberaz0r/typecho-multiple-vulnerabilities
Exploits for Typecho CVE-2024-35538, CVE-2024-35539 and CVE-2024-35540
 smileyface101/crushftp-as2-bypass-research-cve-2025-54309
Research on CrushFTP AS2 authentication bypass allowing unauthenticated admin access. Includes PoC scripts, detection rules, and technical analysis…
 simoesctt/ctt-serverless-rce-v1.0---convergent-time-theory-enhanced-mcp-exploit
Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…