

ad_attack_architecture
 kypvas/ad_attack_architecture
Active Directory Attack Architecture Map Comprehensive Pentest Reference — From Recon to Domain Dominance
curated-resourceseducationidentity-management+7
44
kypvas/ad_attack_architectureActive Directory Attack Architecture Map Comprehensive Pentest Reference — From Recon to Domain Dominance
 microsoft/agent-governance-toolkit
Policy enforcement, zero-trust identity, execution sandboxing, and audit logging for autonomous AI agents. Covers 10/10 OWASP Agentic Top 10 with…
 emrekybs/socmintelligence
A modular OSINT & SOCMINT framework for social media intelligence, investigation, and public data analysis.
 beemdevelopment/aegis
A free, secure and open source app for Android to manage your 2-step verification tokens.
 mafifrizi/tanuki
Tactical Identity Operator for Linux & Hybrid Active Directory
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
 renich/genclave
Centralized, TPM 2.0 hardware-backed cryptographic identity enclave and multi-protocol bridge for Linux (FIDO2/CTAP2 WebAuthn Passkeys, OpenSSH…
 vighnesh91/cloudgarrison
Offline browser-based multi-cloud posture workbench that simulates attack paths, audits IaC compliance, analyzes identity graphs, and maps audit logs…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 matijamiki/ranwhat
Flight recorder and secret scanner for AI coding agents. Reads what Claude Code, Codex, Gemini CLI and 17 more ran, and flags risky actions and…
 roccoammon/active-directory-health-check
PowerShell GUI tool that runs 54 best-practice health and security checks against Active Directory, flagging Kerberoasting, DCSync, delegation and…
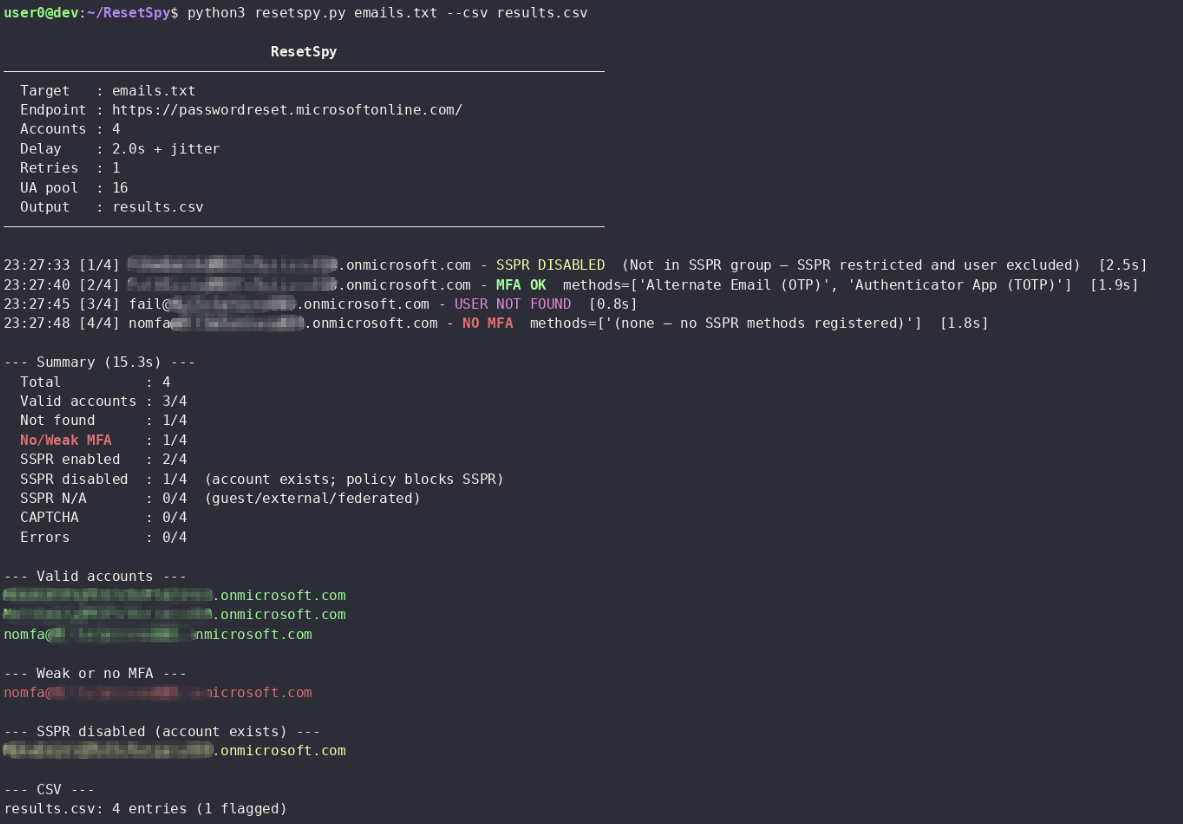 mlcsec/resetspy
Enumerate user accounts and registered authentication methods via the Microsoft Self-Service Password Reset (SSPR) portal
 synacktiv/aadoutsider-py
Python3 rewrite of AsOutsider features of AADInternals
 muhammedhussein17/keycloak
Security research disclosing CVE-2026-9794, an unauthenticated client ID enumeration flaw in Keycloak SAML ECP via faultstring oracle, fixed in…
 sigstore/root-signing
Maintains the TUF repository that securely delivers the Sigstore trust root (trusted_root.json) to clients, using keyholder threshold signing, KMS…