

tugtainer-PoC
 squeeze440/tugtainer-poc
PoC — OIDC id_token accepted without signature/audience/expiry check in Tugtainer (GHSA-crjc-6vc7-xrfh, CVE-2026-87004, CVSS 8.1).
authenticationexploitationidentity-access-management+3
squeeze440/tugtainer-pocPoC — OIDC id_token accepted without signature/audience/expiry check in Tugtainer (GHSA-crjc-6vc7-xrfh, CVE-2026-87004, CVSS 8.1).
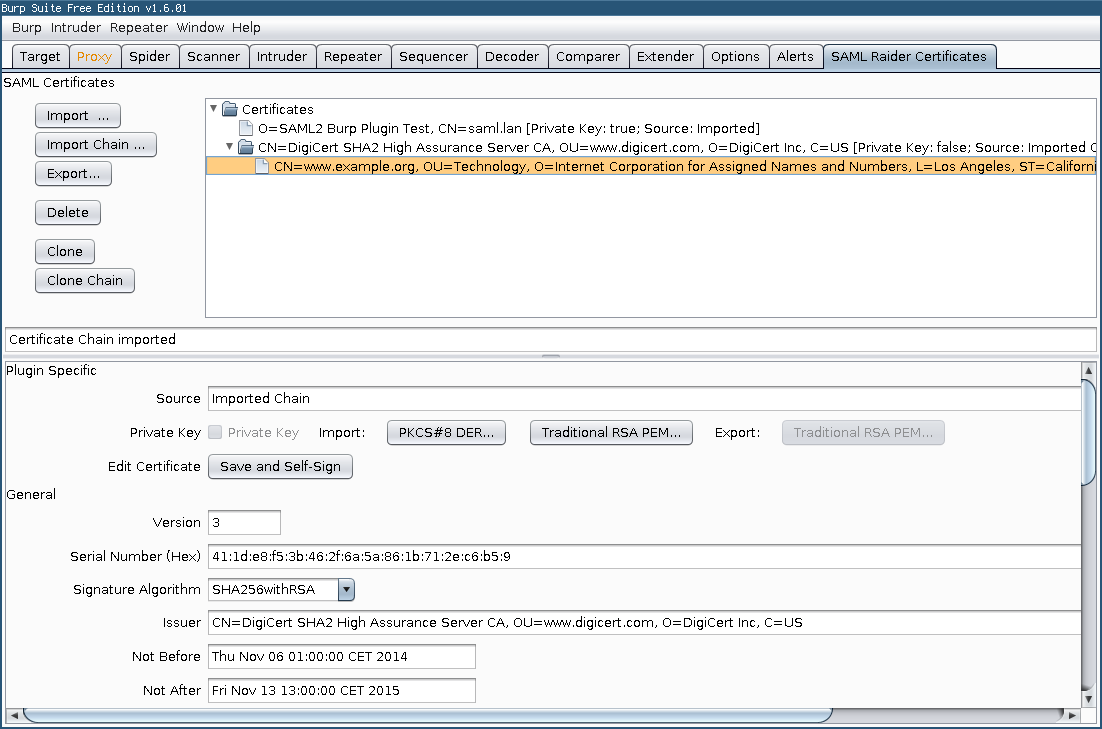 lindi2/samlraider
SAML2 Burp Extension
 7ragnarok7/cve-2021-3754
Vulnerability details and exploit for CVE-2021-3754
 intuitem/ciso-assistant-community
GRC platform for risk management, compliance, and audit with 200+ frameworks, automatic control mapping, vulnerability management, and incident…
 notitssixtyn3in/cve-2025-4172025
Security advisory for CVE-2025-4172025: an authentication bypass vulnerability in Copilot enabling unauthorized account access, session hijacking,…
 saml-toolkits/ruby-saml
Ruby library implementing the SAML Service Provider side of SSO, handling authn requests, response validation, XML signature checks, and IdP metadata…
 anthonyk2923/cve-2026-94609
Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…
 rockmelodies/blackash-cve-2025-41115
CVE-2025-41115