
policy_sentry
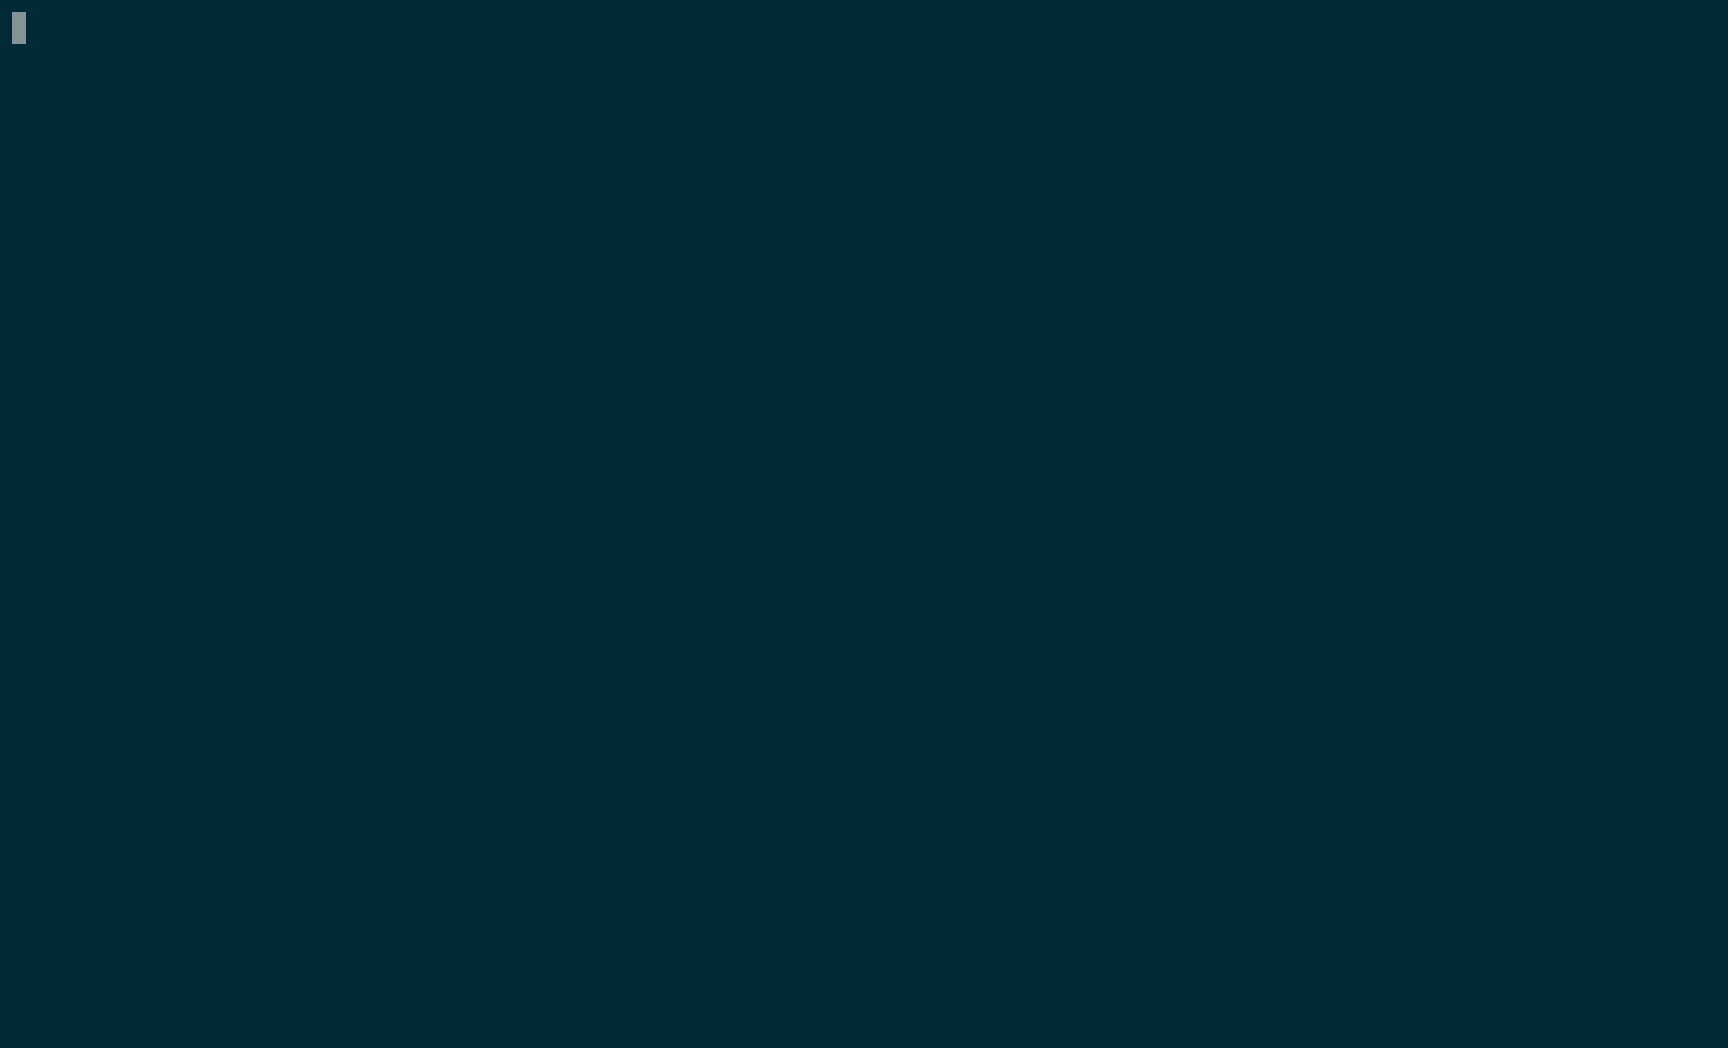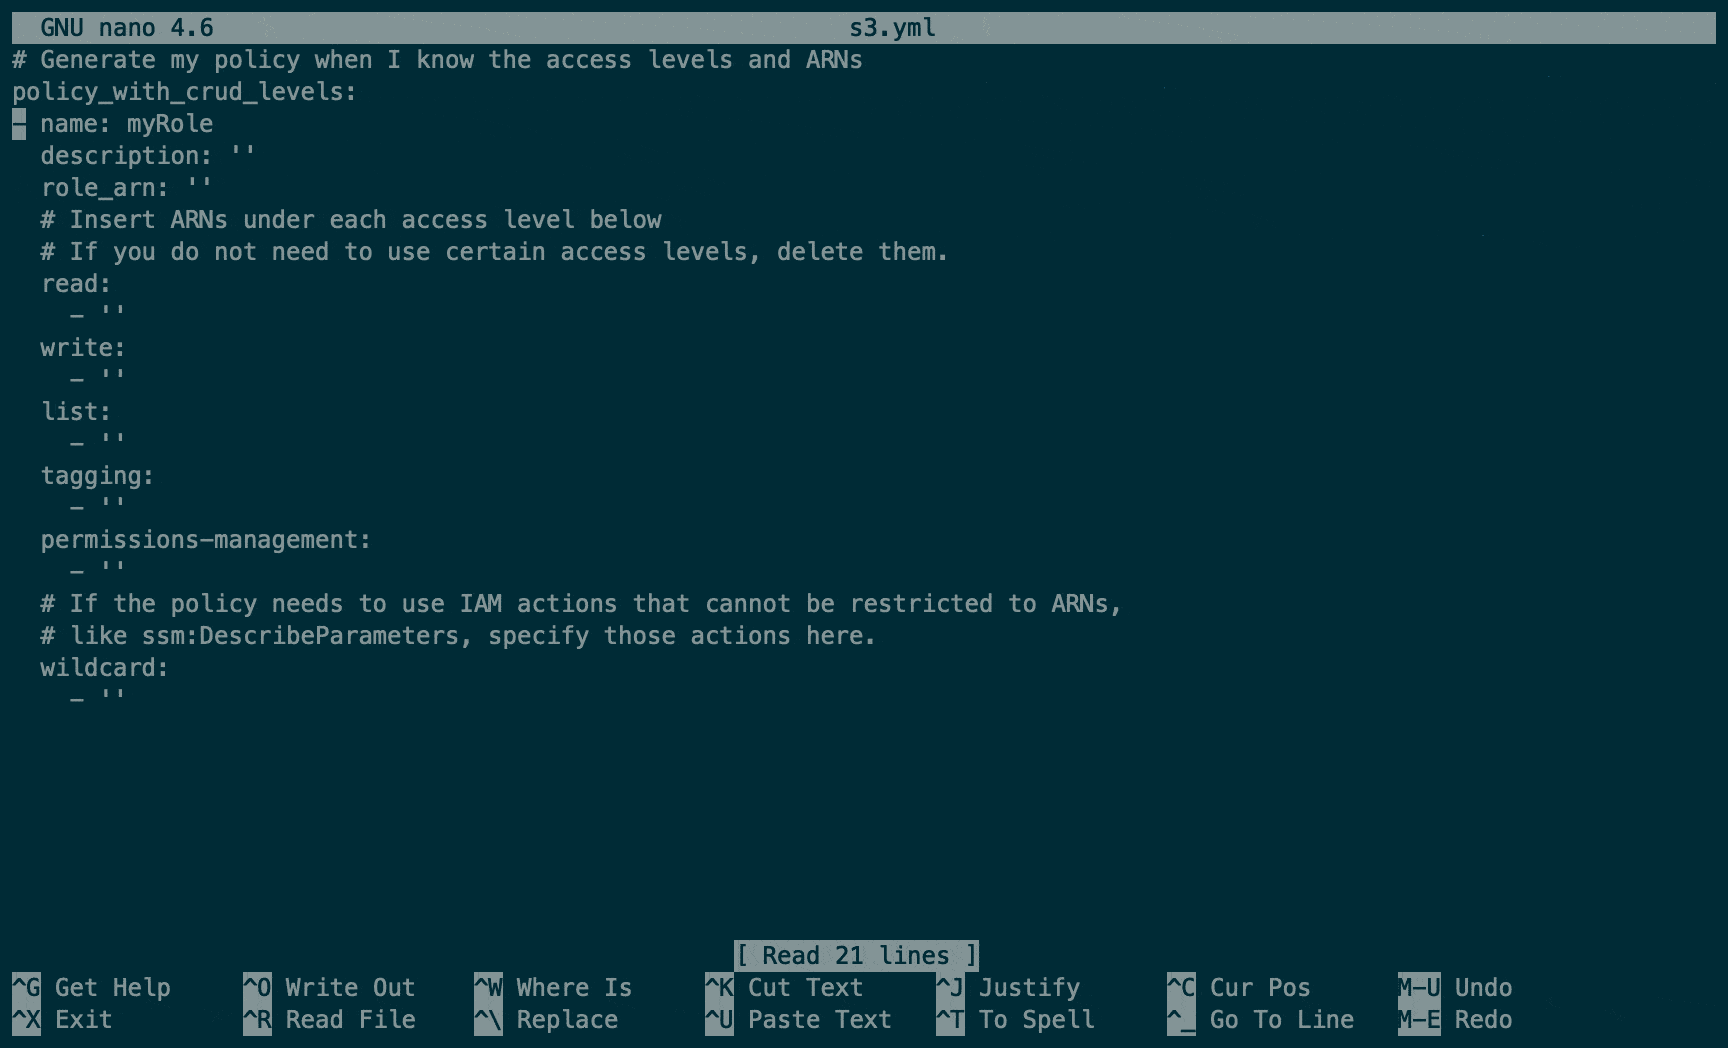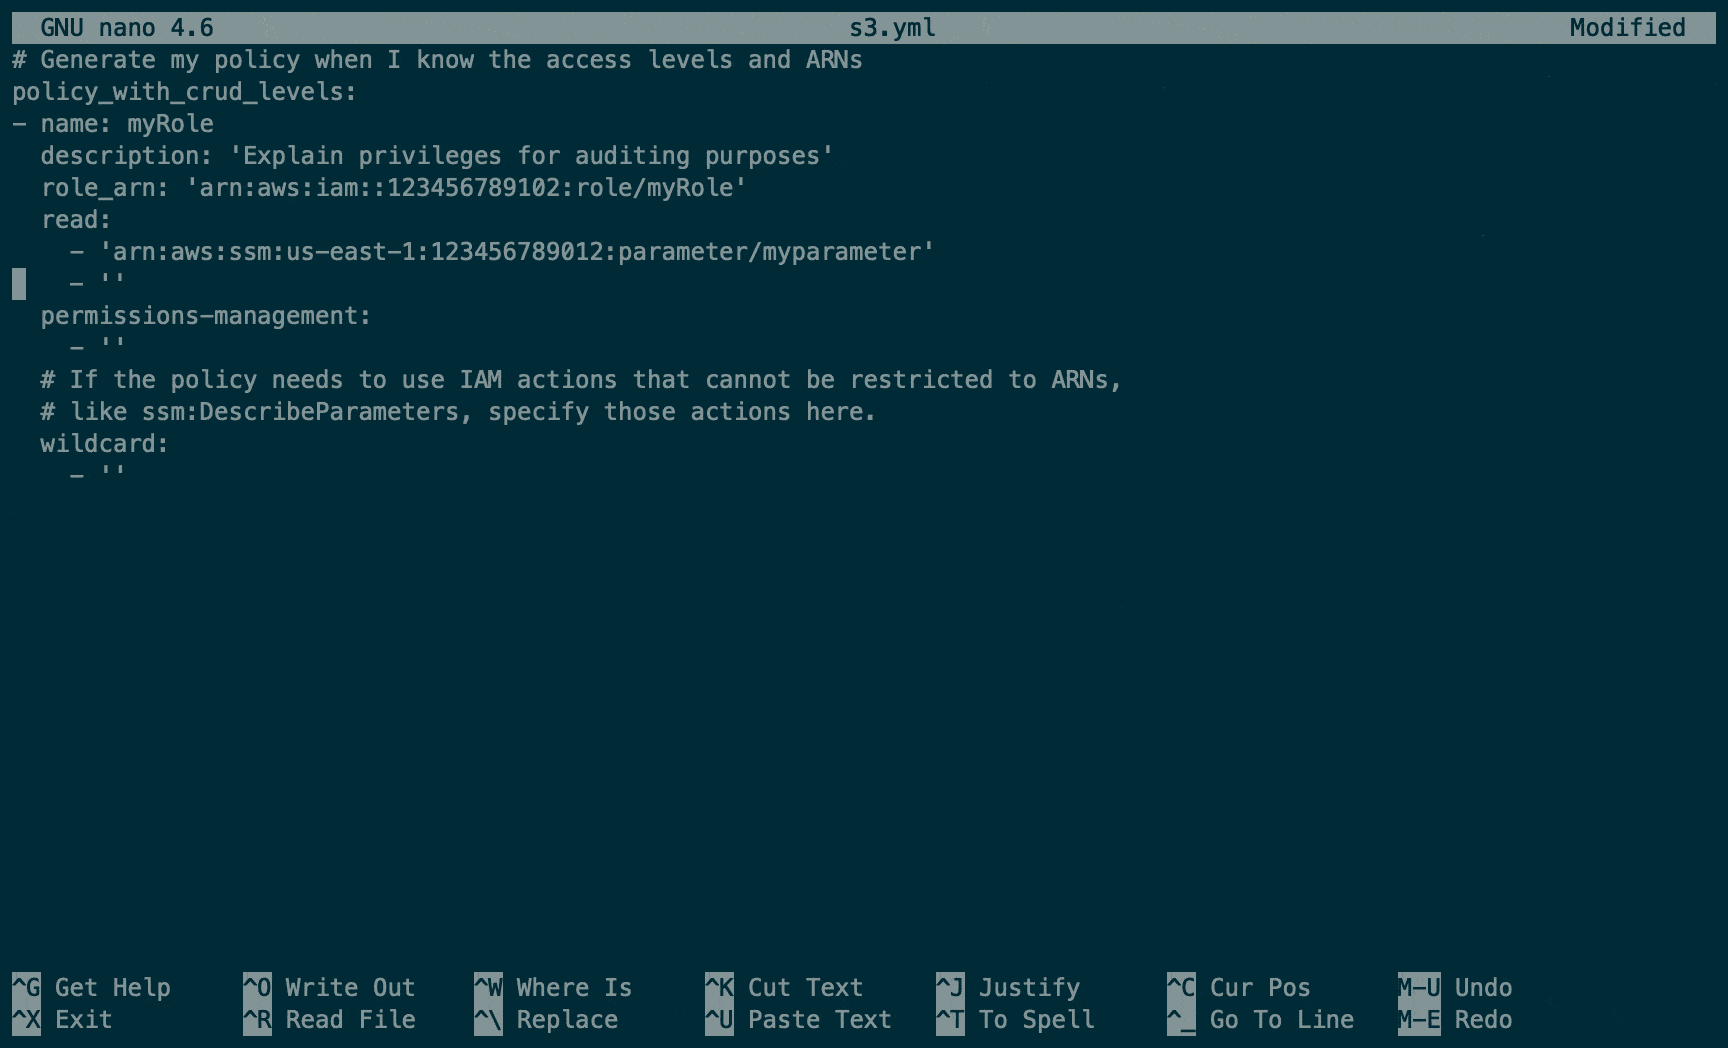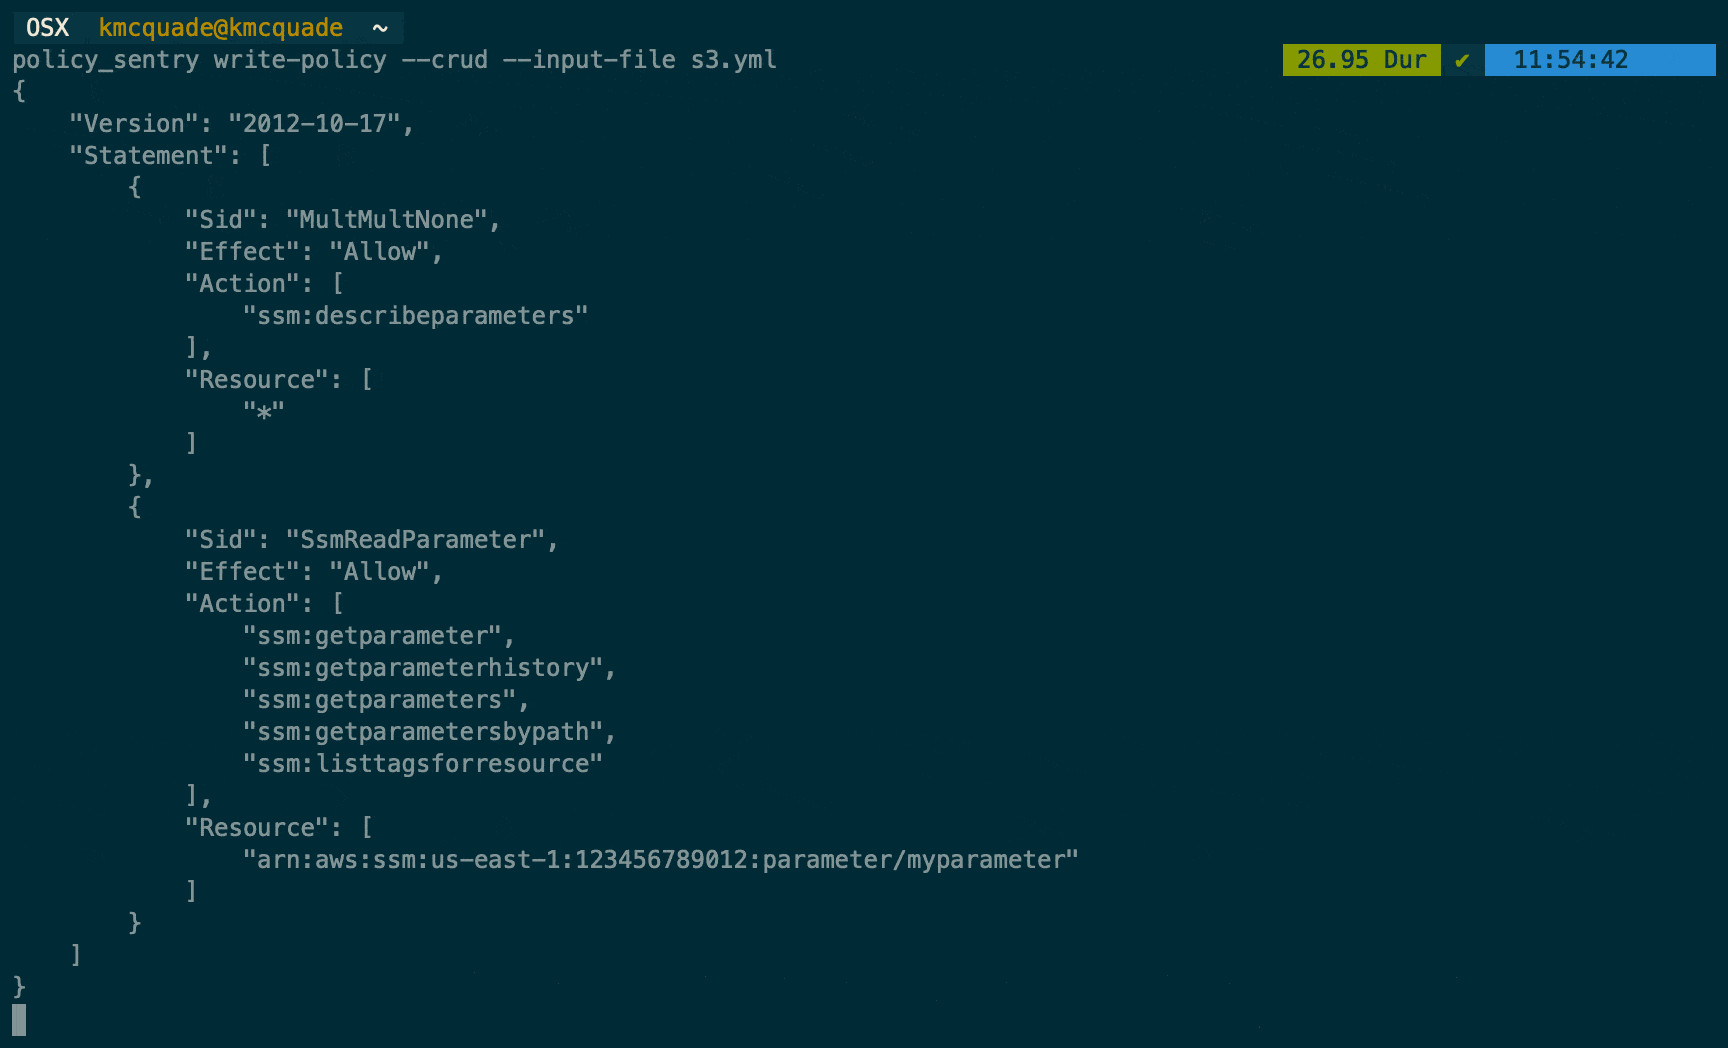
Generates least-privilege AWS IAM policies based on resource ARNs and access levels, automating secure policy creation for cloud infrastructure.

Generates least-privilege AWS IAM policies based on resource ARNs and access levels, automating secure policy creation for cloud infrastructure.

Zero-trust SSH bastion proxy with Vault-backed key management, RBAC policy enforcement, full session recording, and admin TUI for auditable access to…

OAuth and OAuth2 support library for Spring Security, enabling secure API authentication and authorization for consumer and provider implementations…

The OWASP Subtractive Security Top 10 Project is an initiative to identify, document, and promote the highest-impact opportunities for reducing cyber…

High-performance multi-protocol AAA server for RADIUS, DHCPv4/v6, DNS, TACACS+, and VMPS, centralizing network authentication, authorization, and…

A vault for securely storing and accessing AWS credentials in development environments

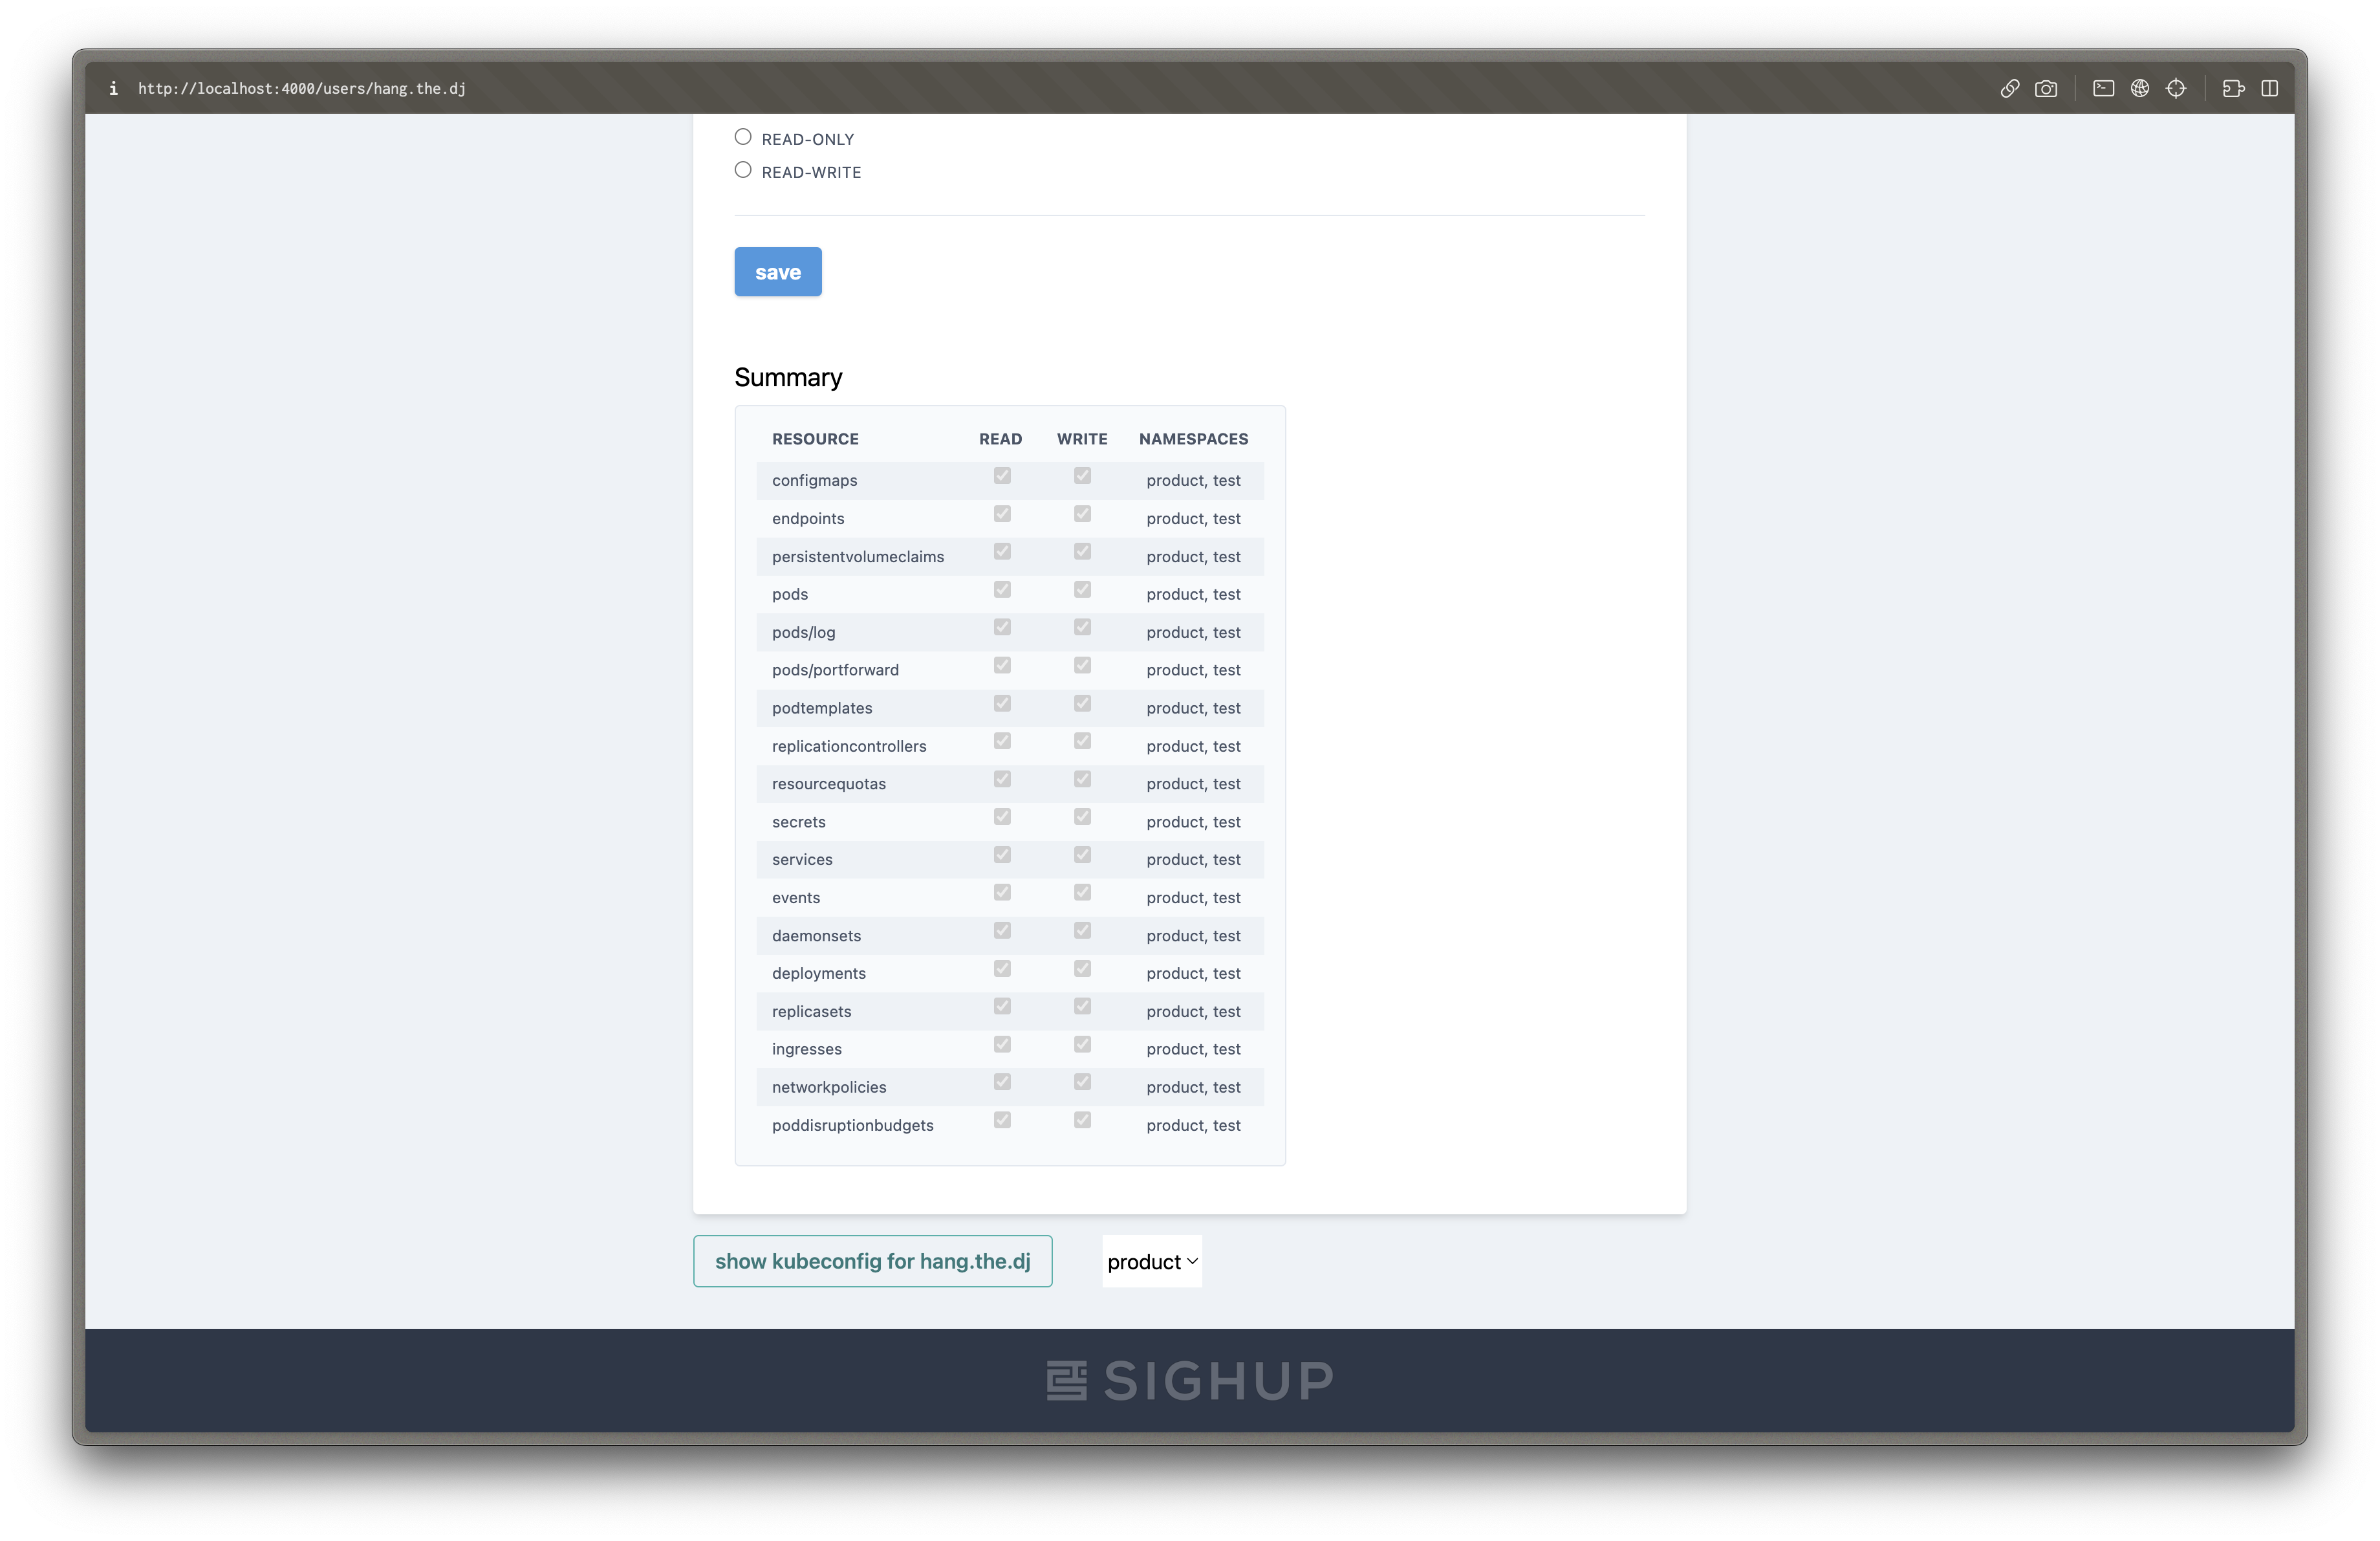
Permission Manager is a project that brings sanity to Kubernetes RBAC and Users management, Web UI FTW

Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…

🔐 Learn authentication by building it right. An extensible, standards-compliant reference implementation for Cloudflare Workers with Hono, Turso,…

Audit program for AzureAD

DSC resources to simplify administration of certificates on a Windows Server.

SkyWrapper helps to discover suspicious creation forms and uses of temporary tokens in AWS

Experimental RP2040 FIDO2/WebAuthn authenticator with packed attestation and documented Windows/Entra interoperability