

BloodHound
 specterops/bloodhound
Six Degrees of Domain Admin
defensive-toolsidentity-access-managementinformation-gathering+4
3.4k
specterops/bloodhoundSix Degrees of Domain Admin
 gerenios/aadinternals
PowerShell module for administering and auditing Azure AD and Office 365, enabling token manipulation, user enumeration, and security assessments of…
 cyberark/skyark
SkyArk helps to discover, assess and secure the most privileged entities in Azure and AWS
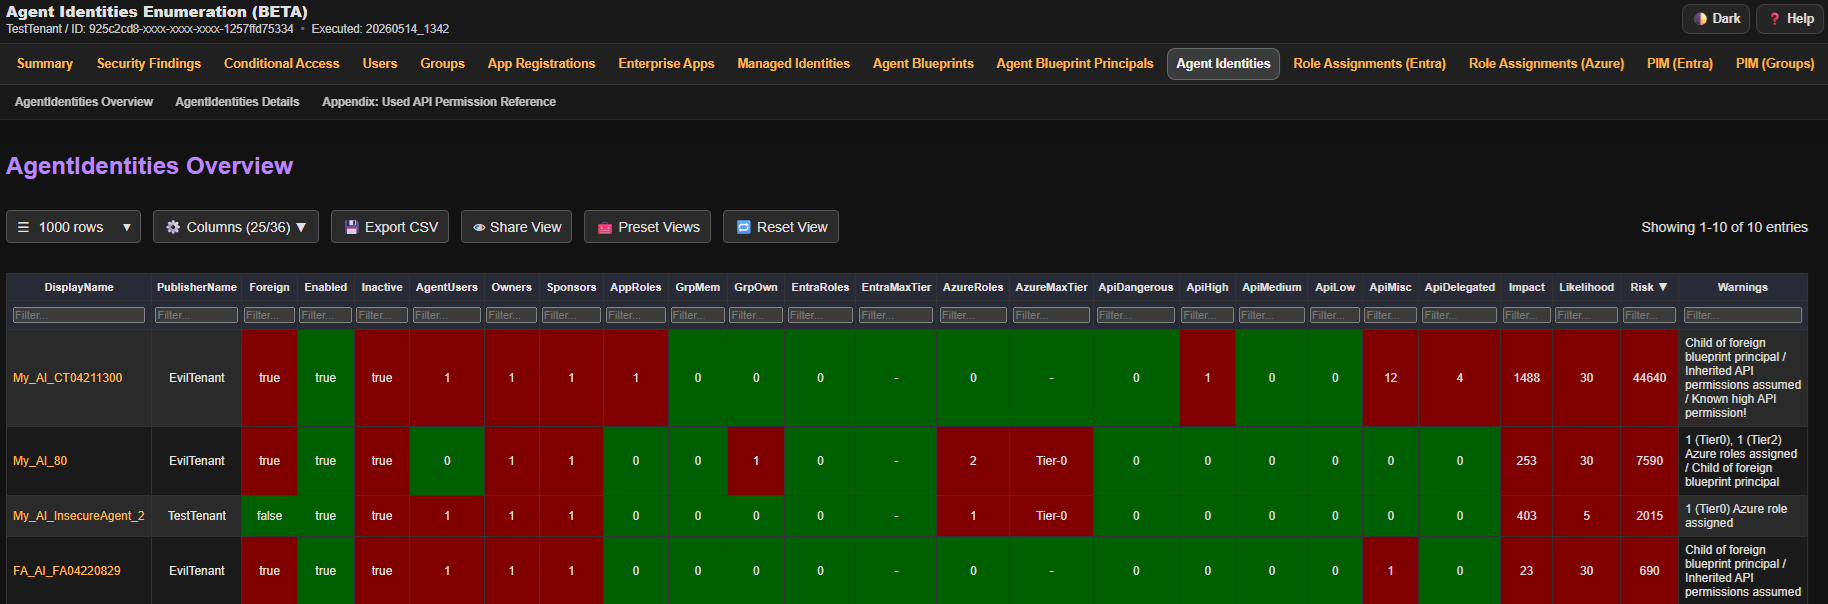 compasssecurity/entrafalcon
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…
 logisek/evilmist
EvilMist is a collection of scripts and utilities designed to support cloud penetration testing & red teaming. The toolkit helps identify…
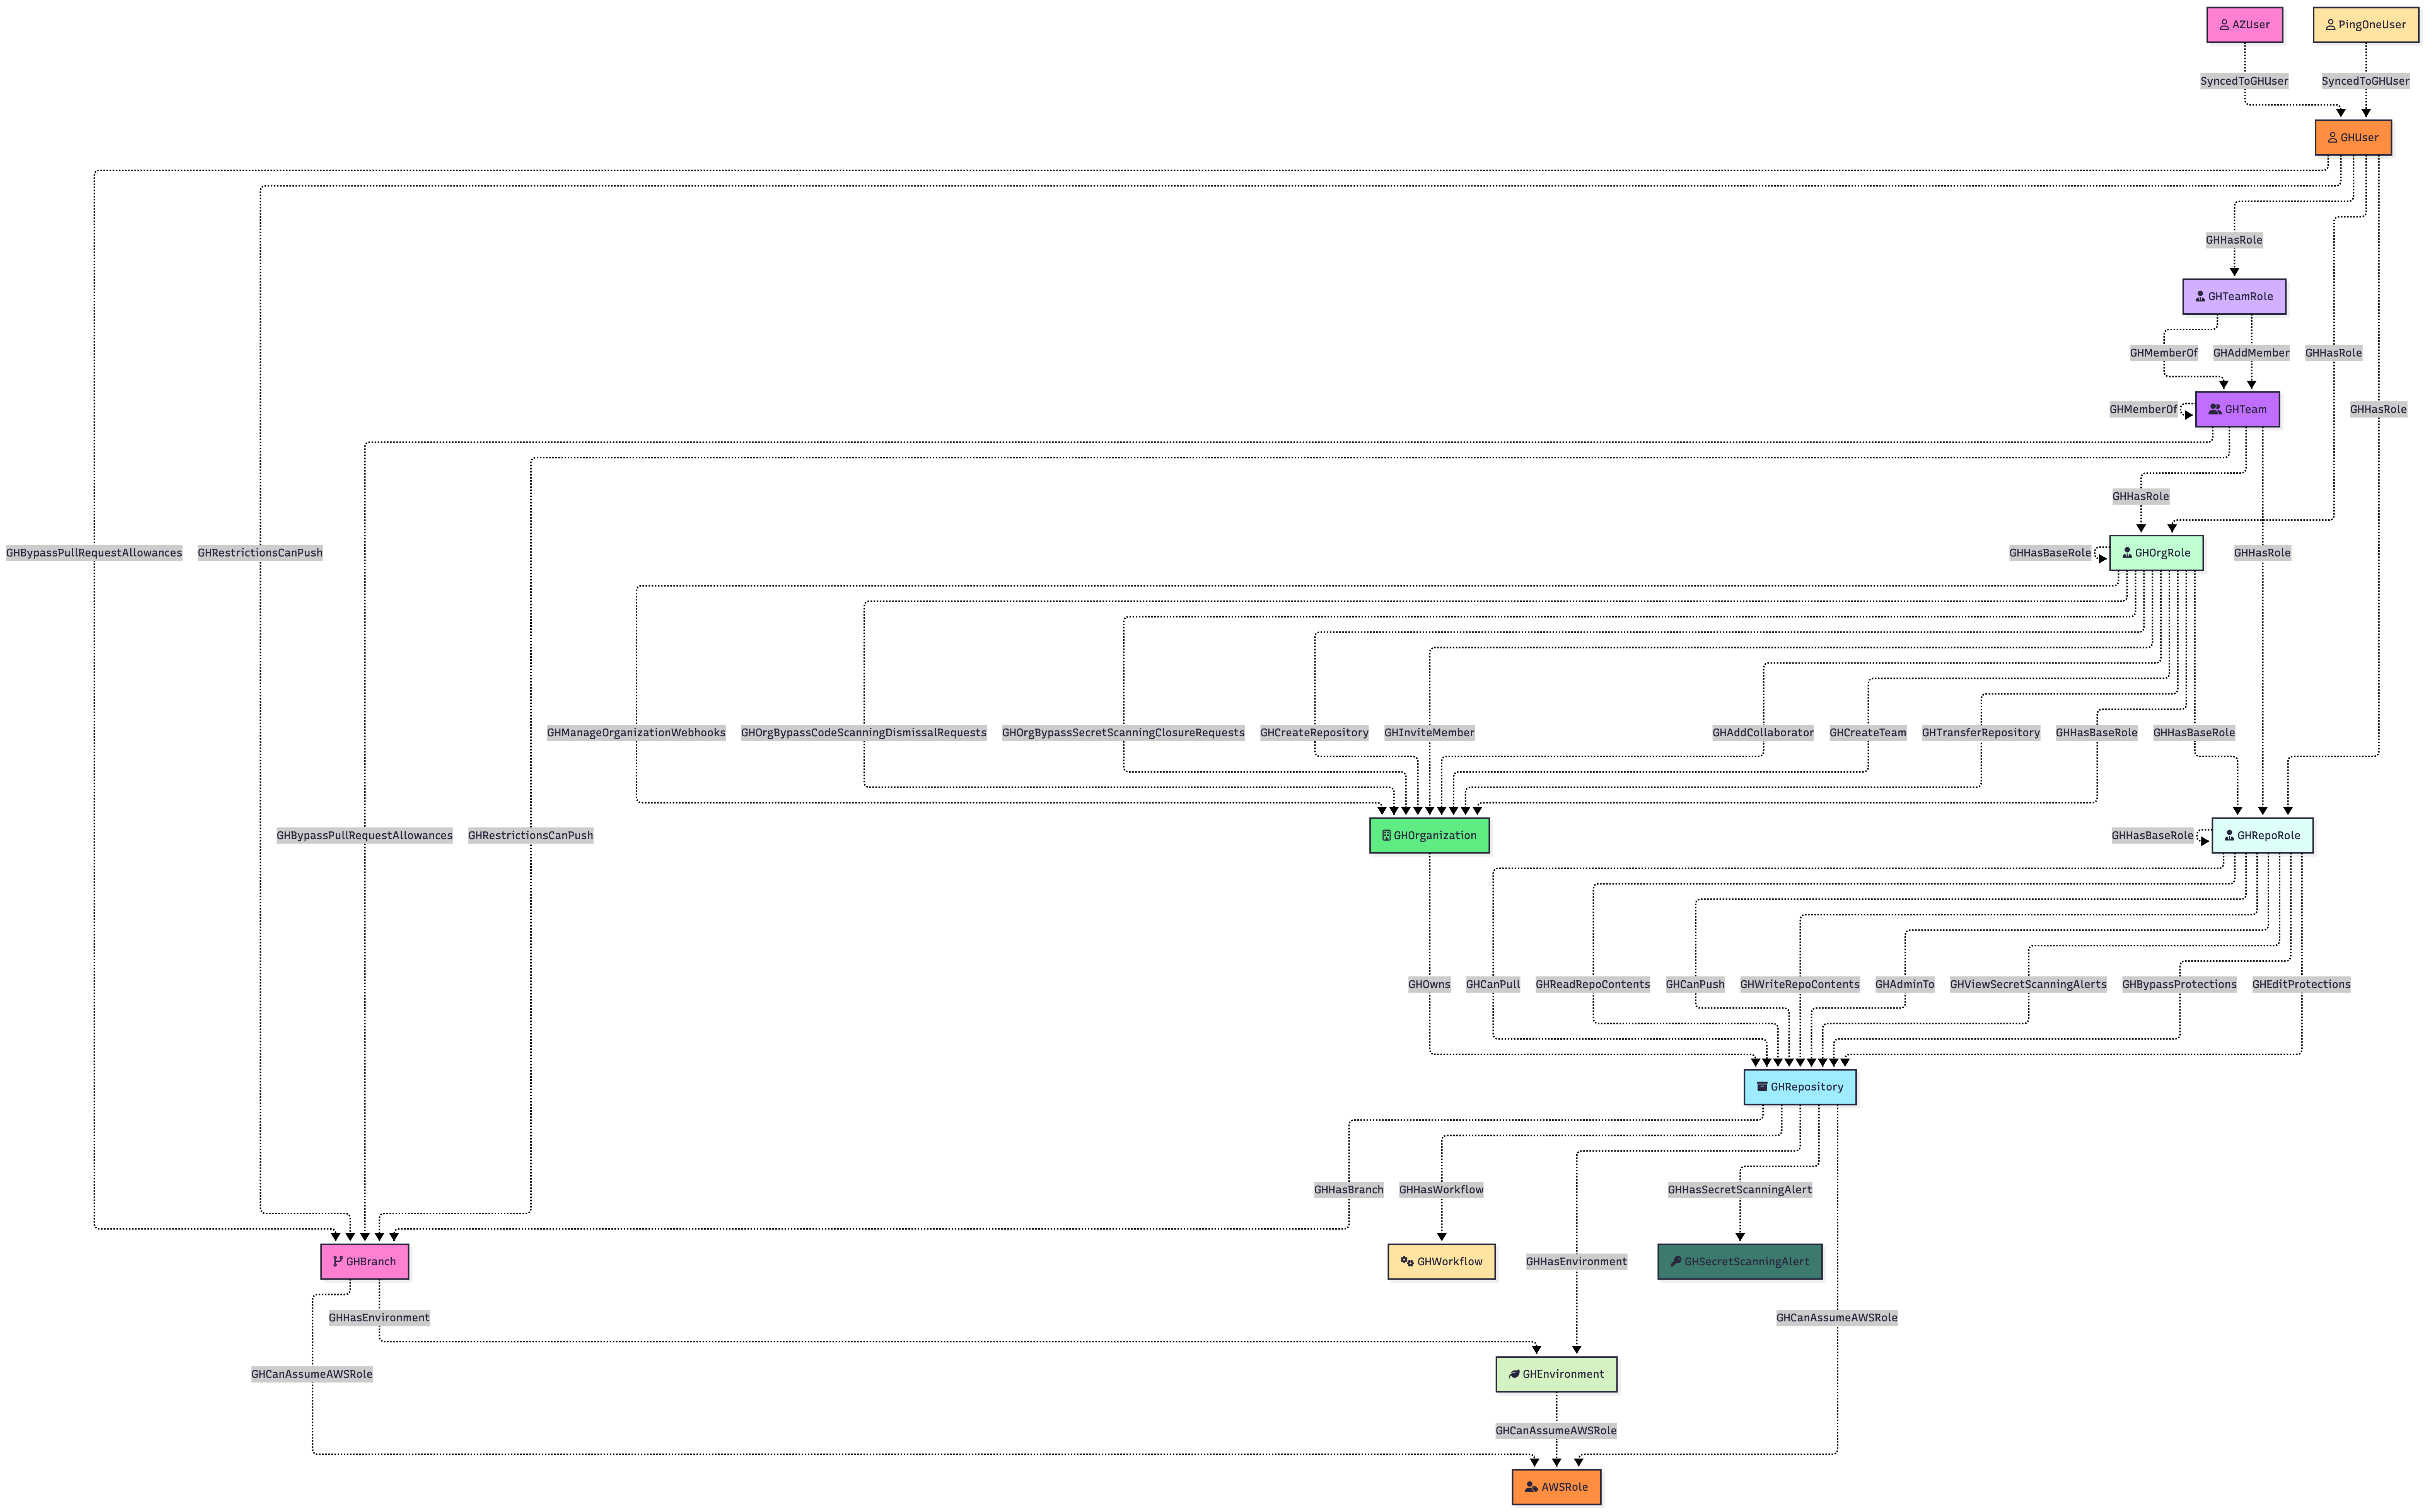 specterops/githound
BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…
 redbyte1337/credspy
Entra ID user enumeration and auth method discovery via the public GetCredentialType API
 drunkf0x/adspider
Monitor changes in Active Directory with replication metadata
 bishopfox/cirro
Creating attacks paths across management and data planes
 t94j0/adexplorersnapshot-rs
Converts Active Directory Explorer snapshot (.dat) files into BloodHound CE JSON archives for graph-based AD attack-path analysis and reconnaissance.
 daddycocoaman/azbelt
AAD related enumeration in Nim
 sap8899/reportly
AzureAD/EntraID user activity reporter for blue teams. Input a suspicious user and time frame to receive a detailed report of user info, actions, and…