printnightmare-detection-mitigation-lab

Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.

Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.

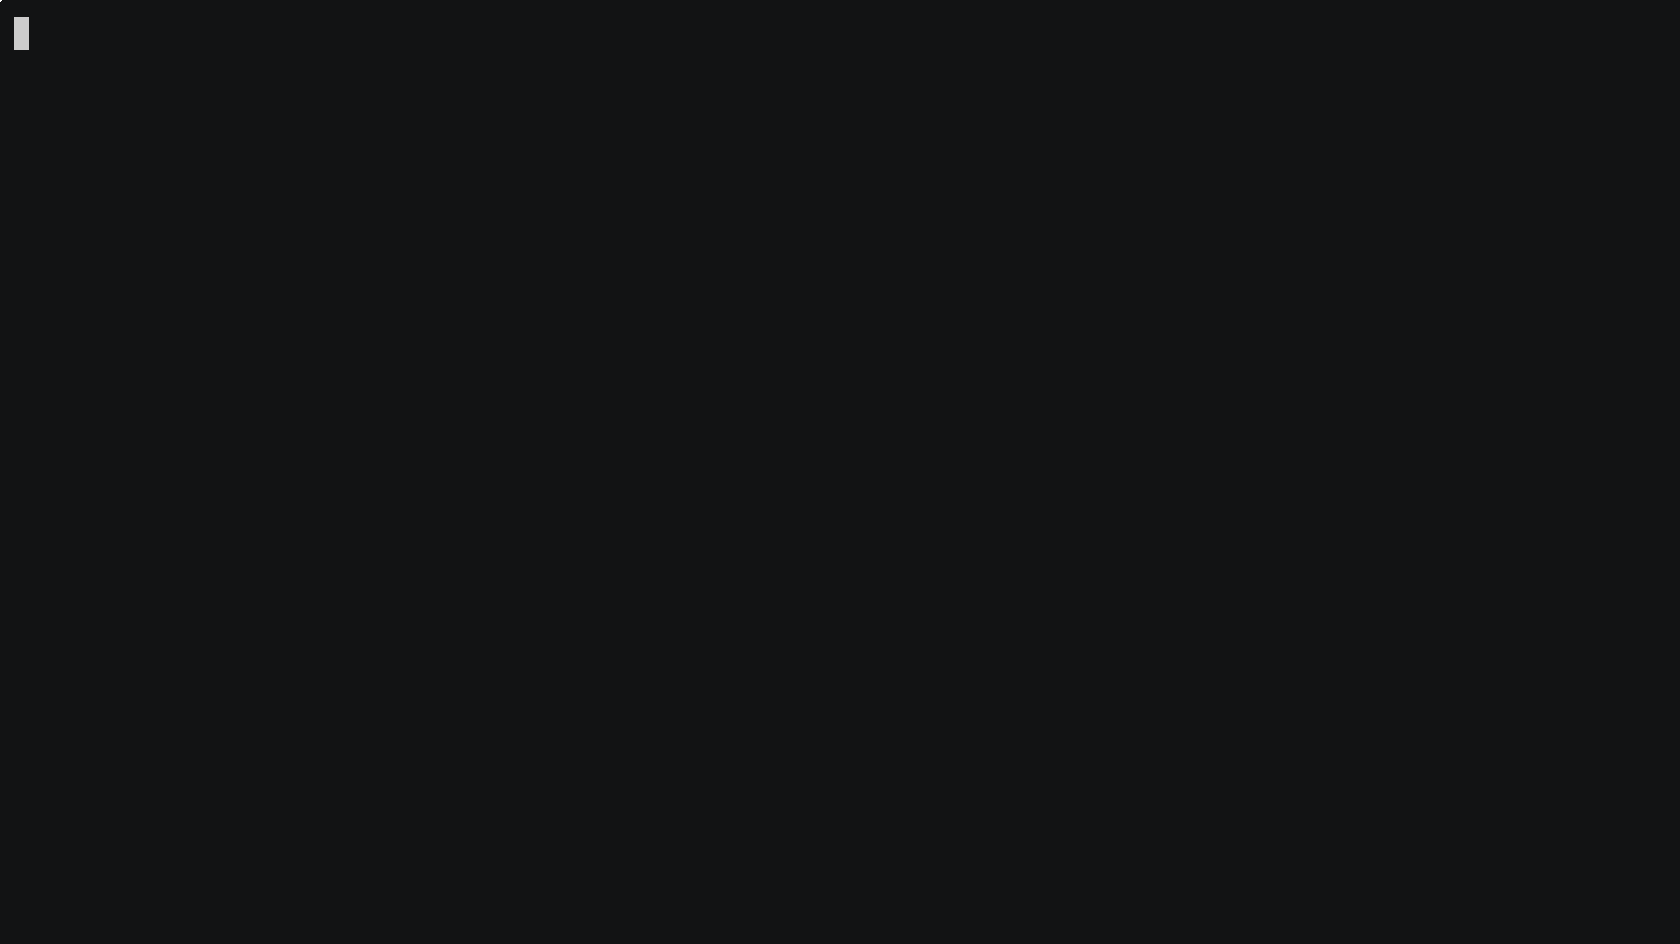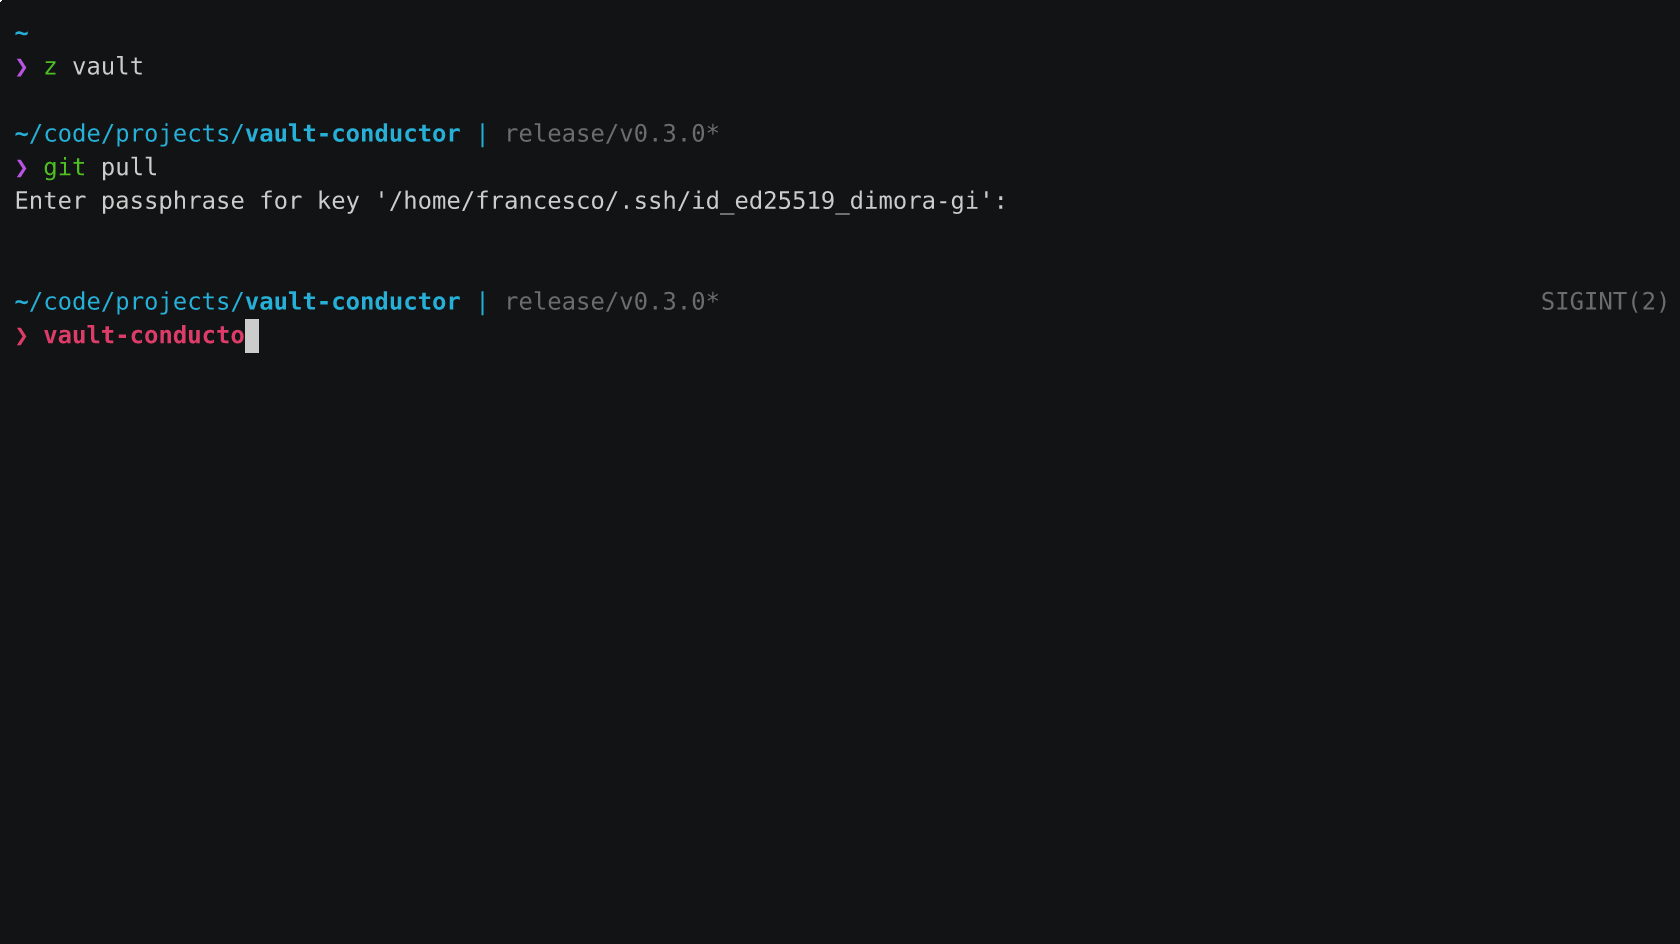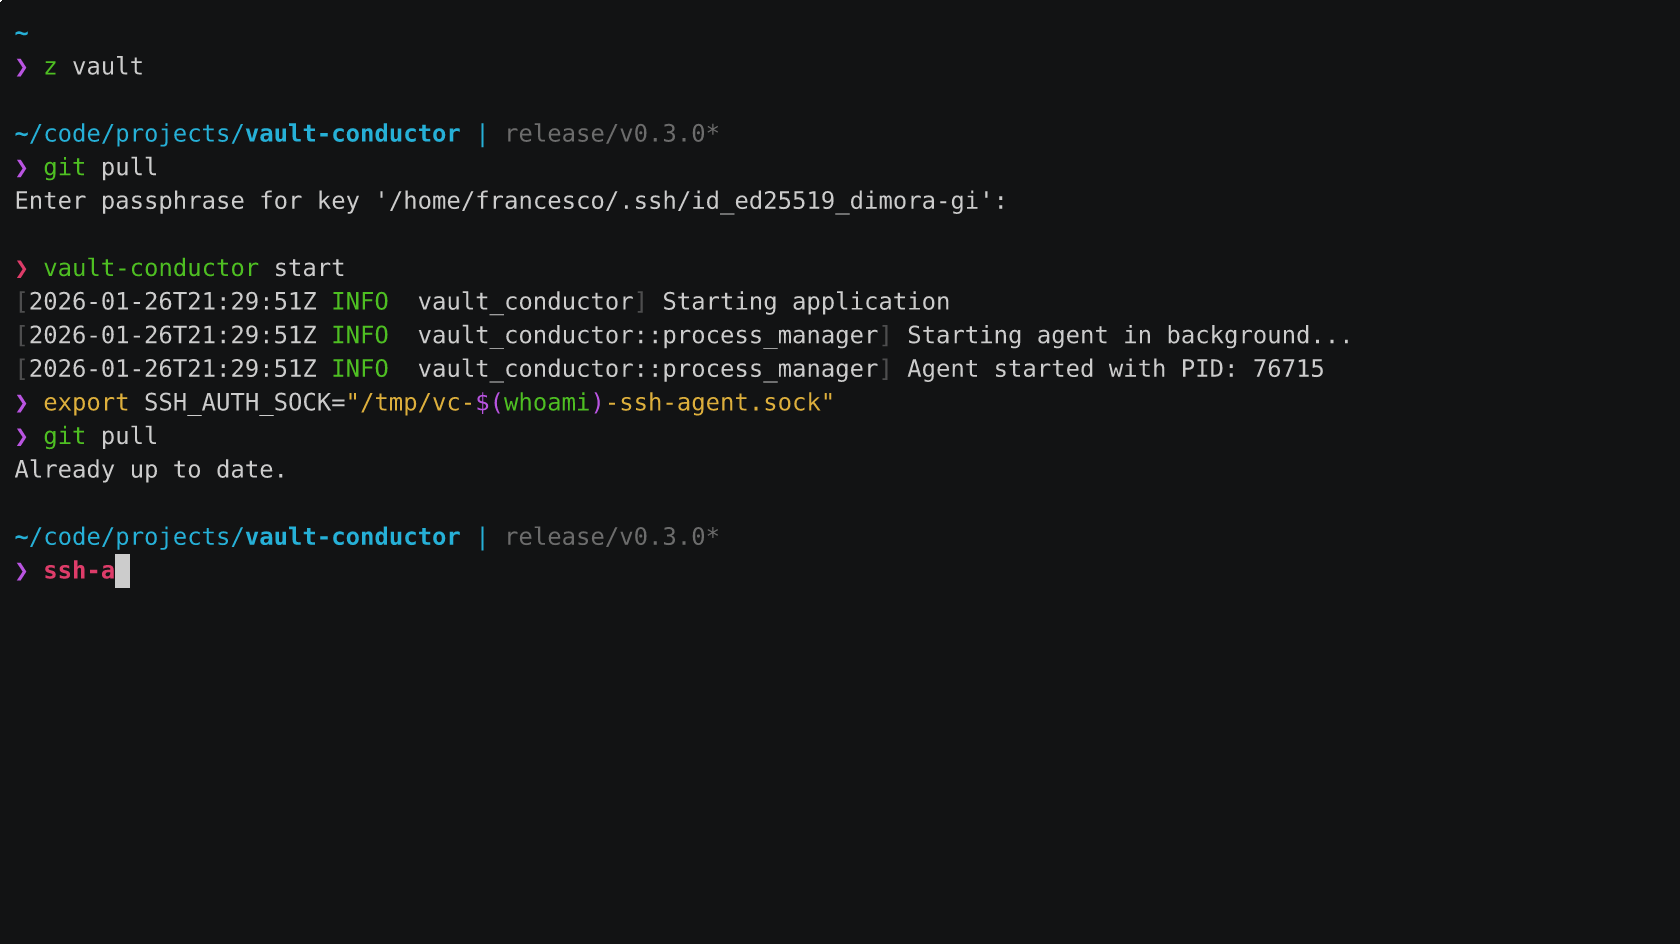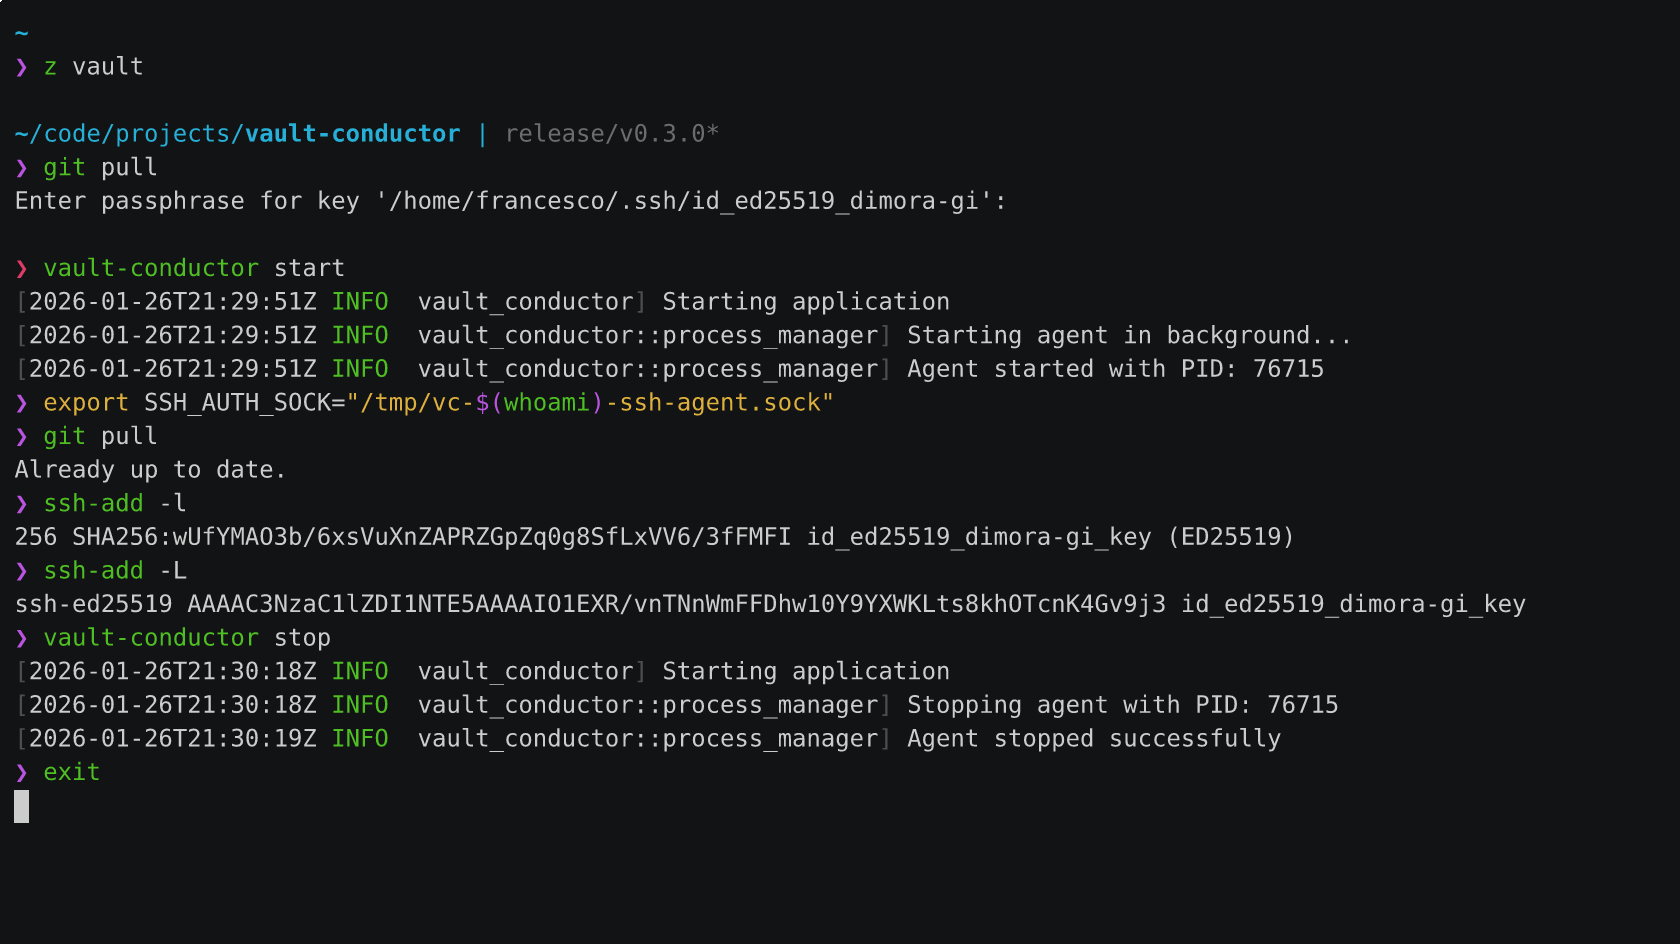
An SSH Agent that provides SSH keys stored in Bitwarden Secrets Manager

Free email OSINT tool, 2500+ platforms, identity clustering, breach detection. No API keys required. pip install mailaccess

Kerberos RC4 deprecation: detection, remediation and guidance (CVE-2026-20833)

MDE/MDI Defender setup for Ludus

Six Degrees of Domain Admin

Para verificar si tu entorno podría ser vulnerable al CVE-2025-29810, necesitamos hacer algunas comprobaciones básicas, como: Versión del sistema…

Client for Cloudflare Tunnel enabling secure outbound-only connections to origins via Zero Trust architecture. Supports HTTP, WebSocket, SSH, and RDP…

A curated list of awesome Security Hardening techniques for Windows.

A little tool to play with Azure Identity - Azure and Entra ID lab creation tool. Blog: https://medium.com/@iknowjason/sentinel-for-purple-teaming-1…

EvilMist is a collection of scripts and utilities designed to support cloud penetration testing & red teaming. The toolkit helps identify…

Monitor changes in Active Directory with replication metadata

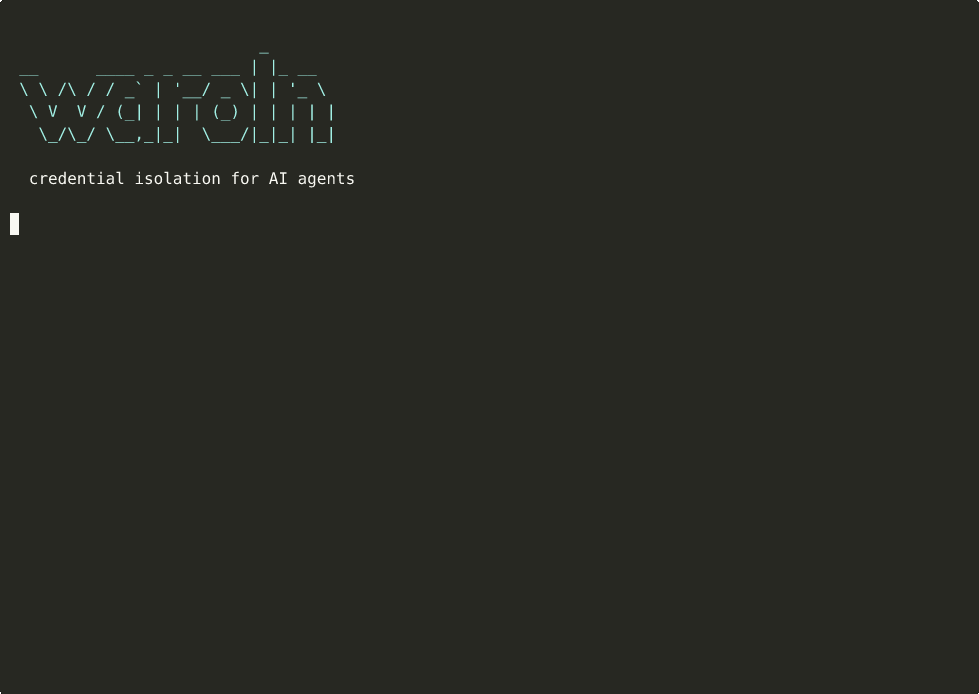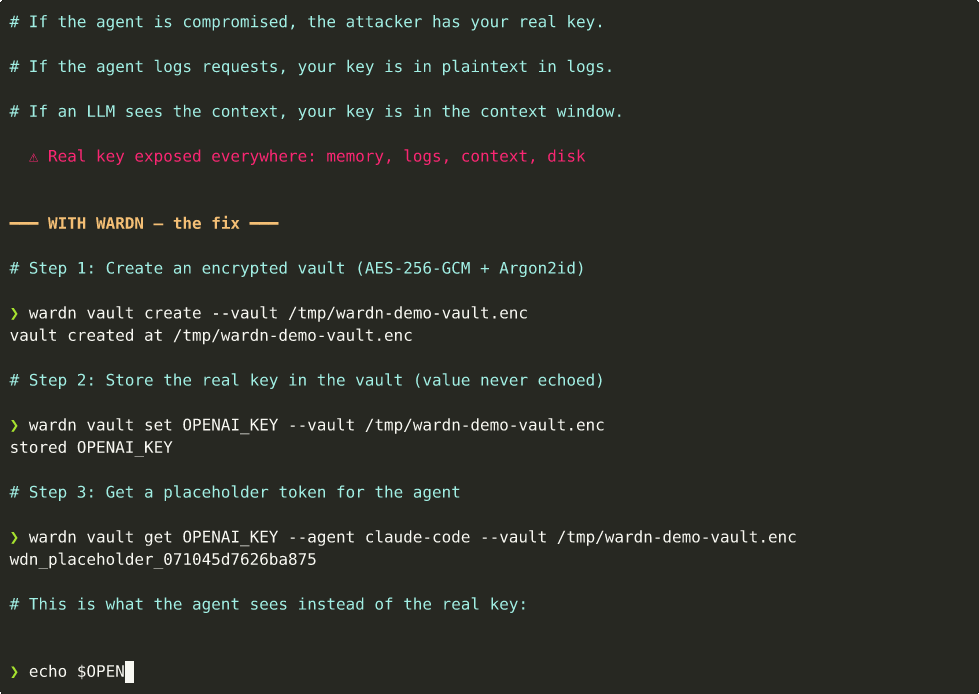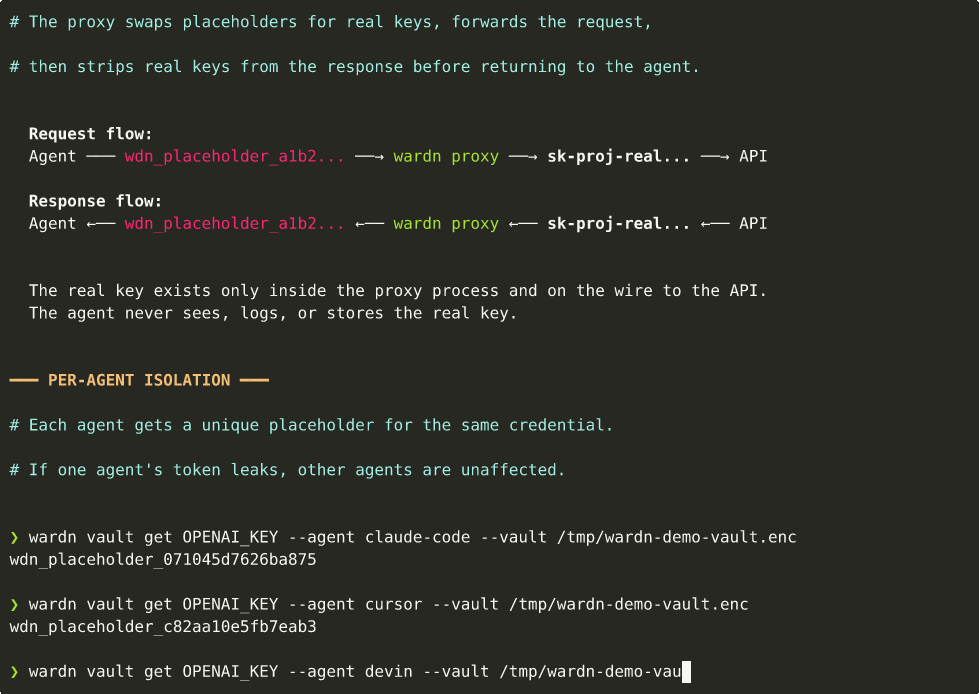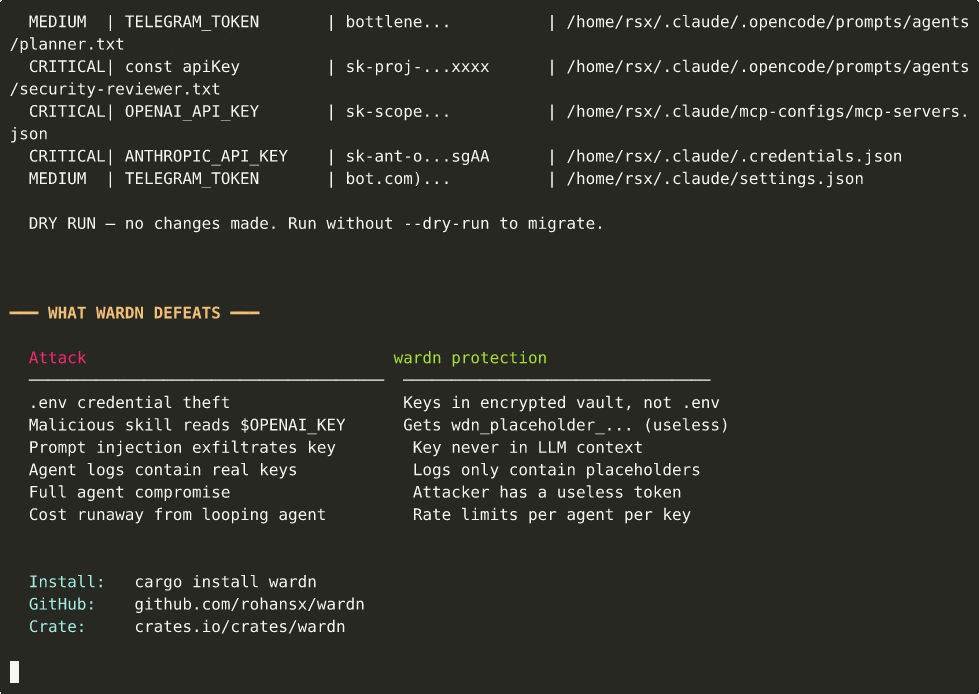
credential isolation for AI agents. Agents never see real API keys - structural guarantee, not policy.

Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…

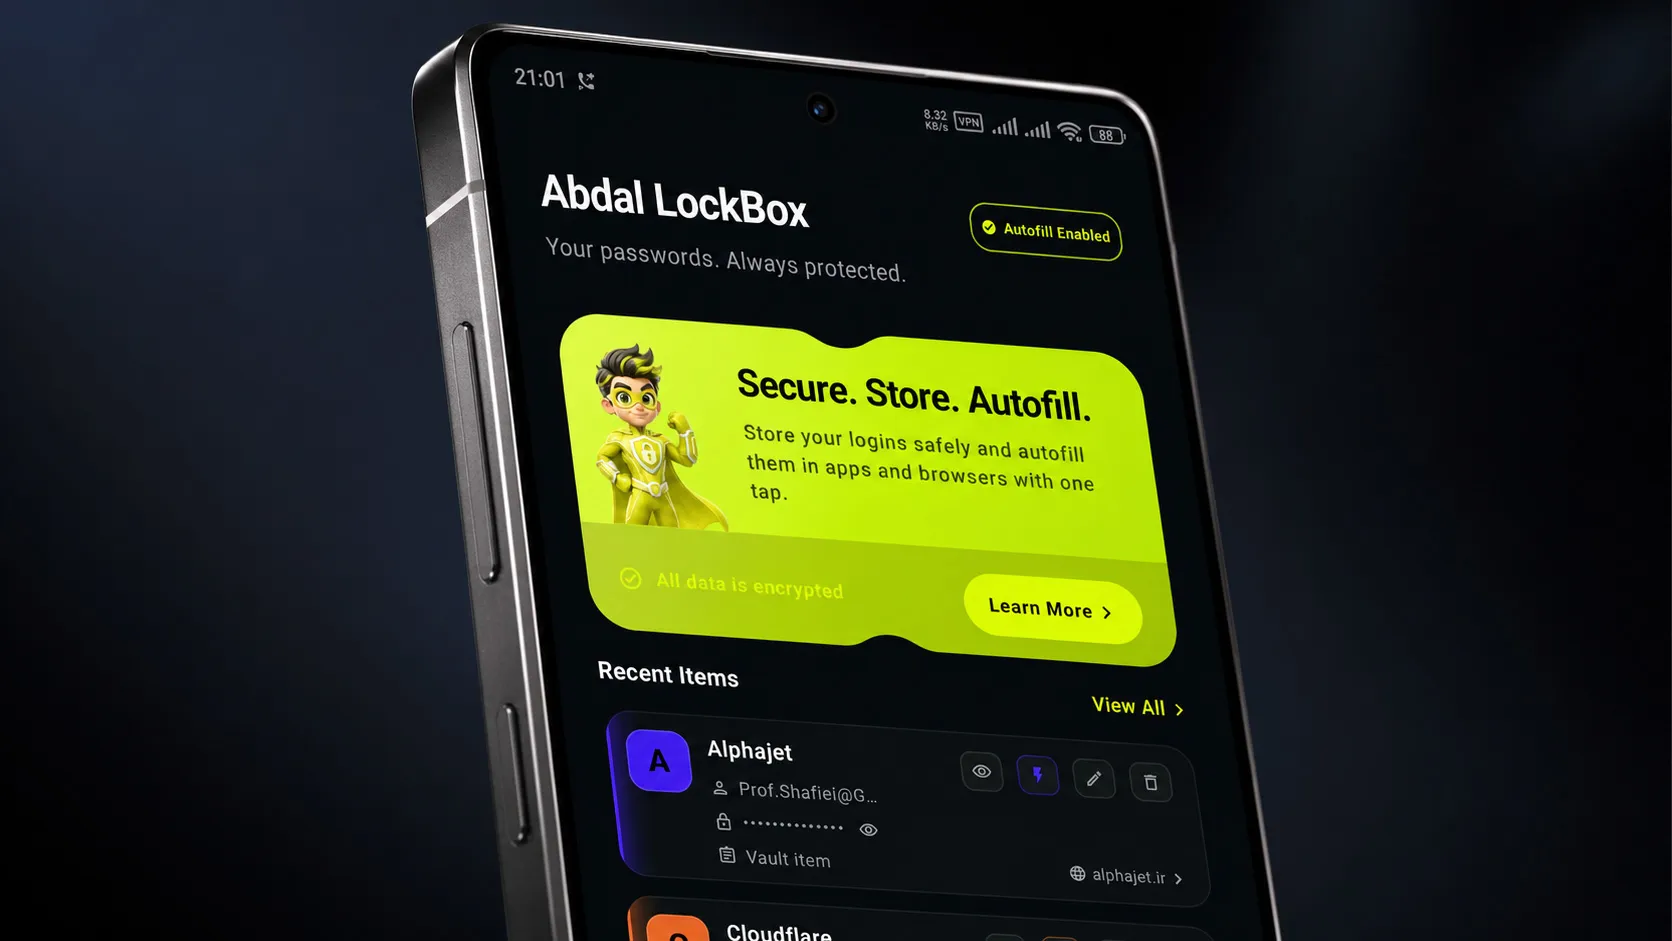
Local-first encrypted password vault for Android with Master Password access, Recovery Key support, Autofill integration, and portable encrypted…

Shadow Vault – Add shadow users with SHA-512 hash, auto aging match, multiple write fallbacks.

Safety cannot be a prompt instruction. TBP provides an external execution-layer boundary for autonomous agents, enforcing hard F/I/W invariants via…

Read-only PowerShell module for detecting UNC2452 and other threat actor artifacts in Azure AD, auditing federated domains, service principals,…