

Awesome-BEC
 randomaccess3/awesome-bec
Repository of attack and defensive information for Business Email Compromise investigations
cloud-securitycurated-resourcesdigital-forensics+7
278
randomaccess3/awesome-becRepository of attack and defensive information for Business Email Compromise investigations
 zephrfish/azureattackkit
Collection of Azure Tools to Pull down for Attacking an Environment + quick tips and other useful information
 fabacab/awesome-cybersecurity-blueteam
:computer:🛡️ A curated collection of awesome resources, tools, and other shiny things for cybersecurity blue teams.
 nccgroup/raccoon
Salesforce object access auditor
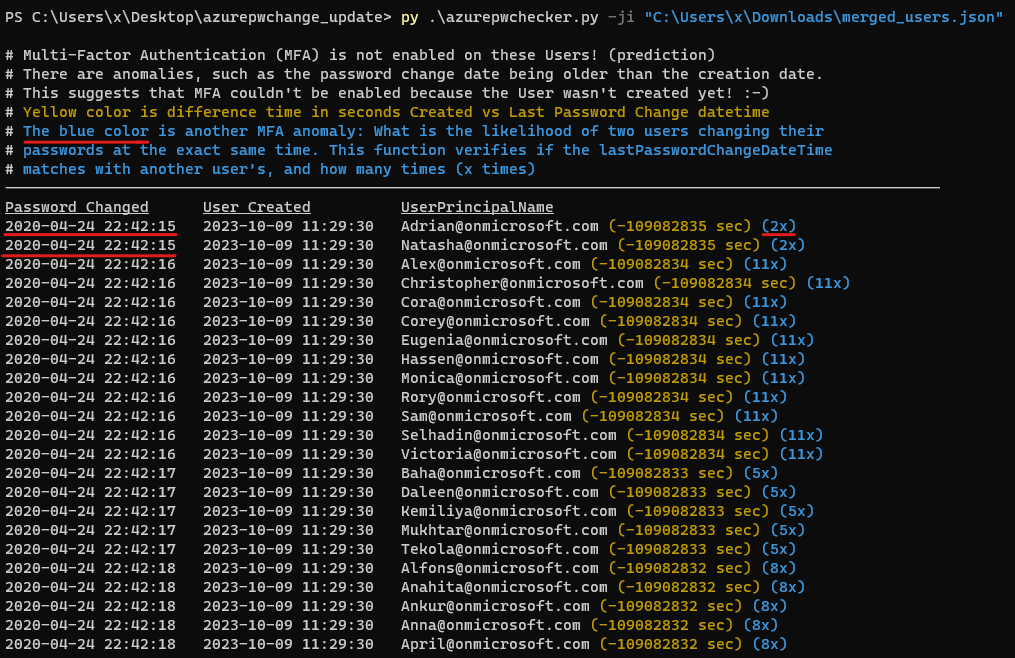 quahac/azure-ad-password-checker
Azure AD Password Checker
 nccgroup/sfpoldevchk
Salesforce Policy Deviation Checker
 specterops/bloodhound
Six Degrees of Domain Admin
 gerenios/aadinternals
PowerShell module for administering and auditing Azure AD and Office 365, enabling token manipulation, user enumeration, and security assessments of…
 cyberark/skyark
SkyArk helps to discover, assess and secure the most privileged entities in Azure and AWS
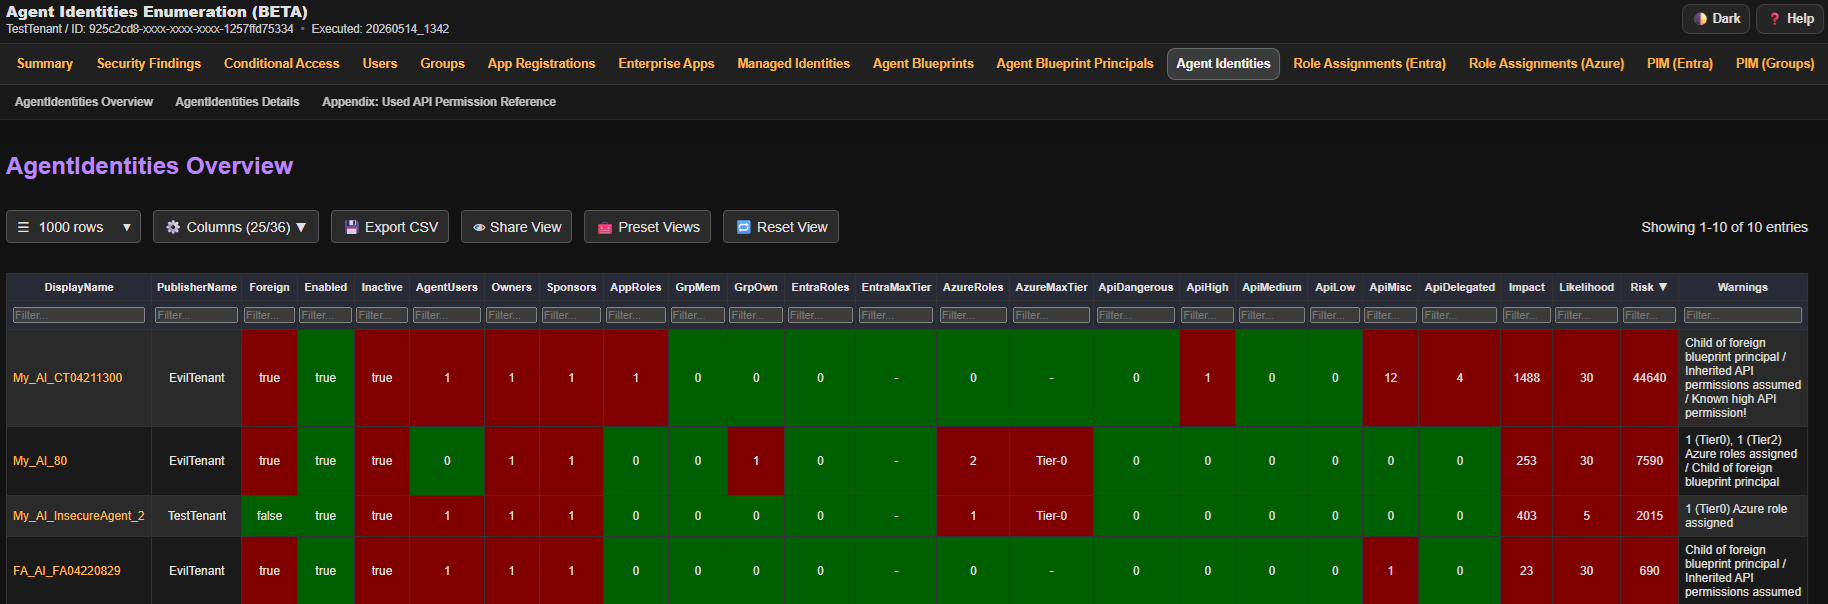 compasssecurity/entrafalcon
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…
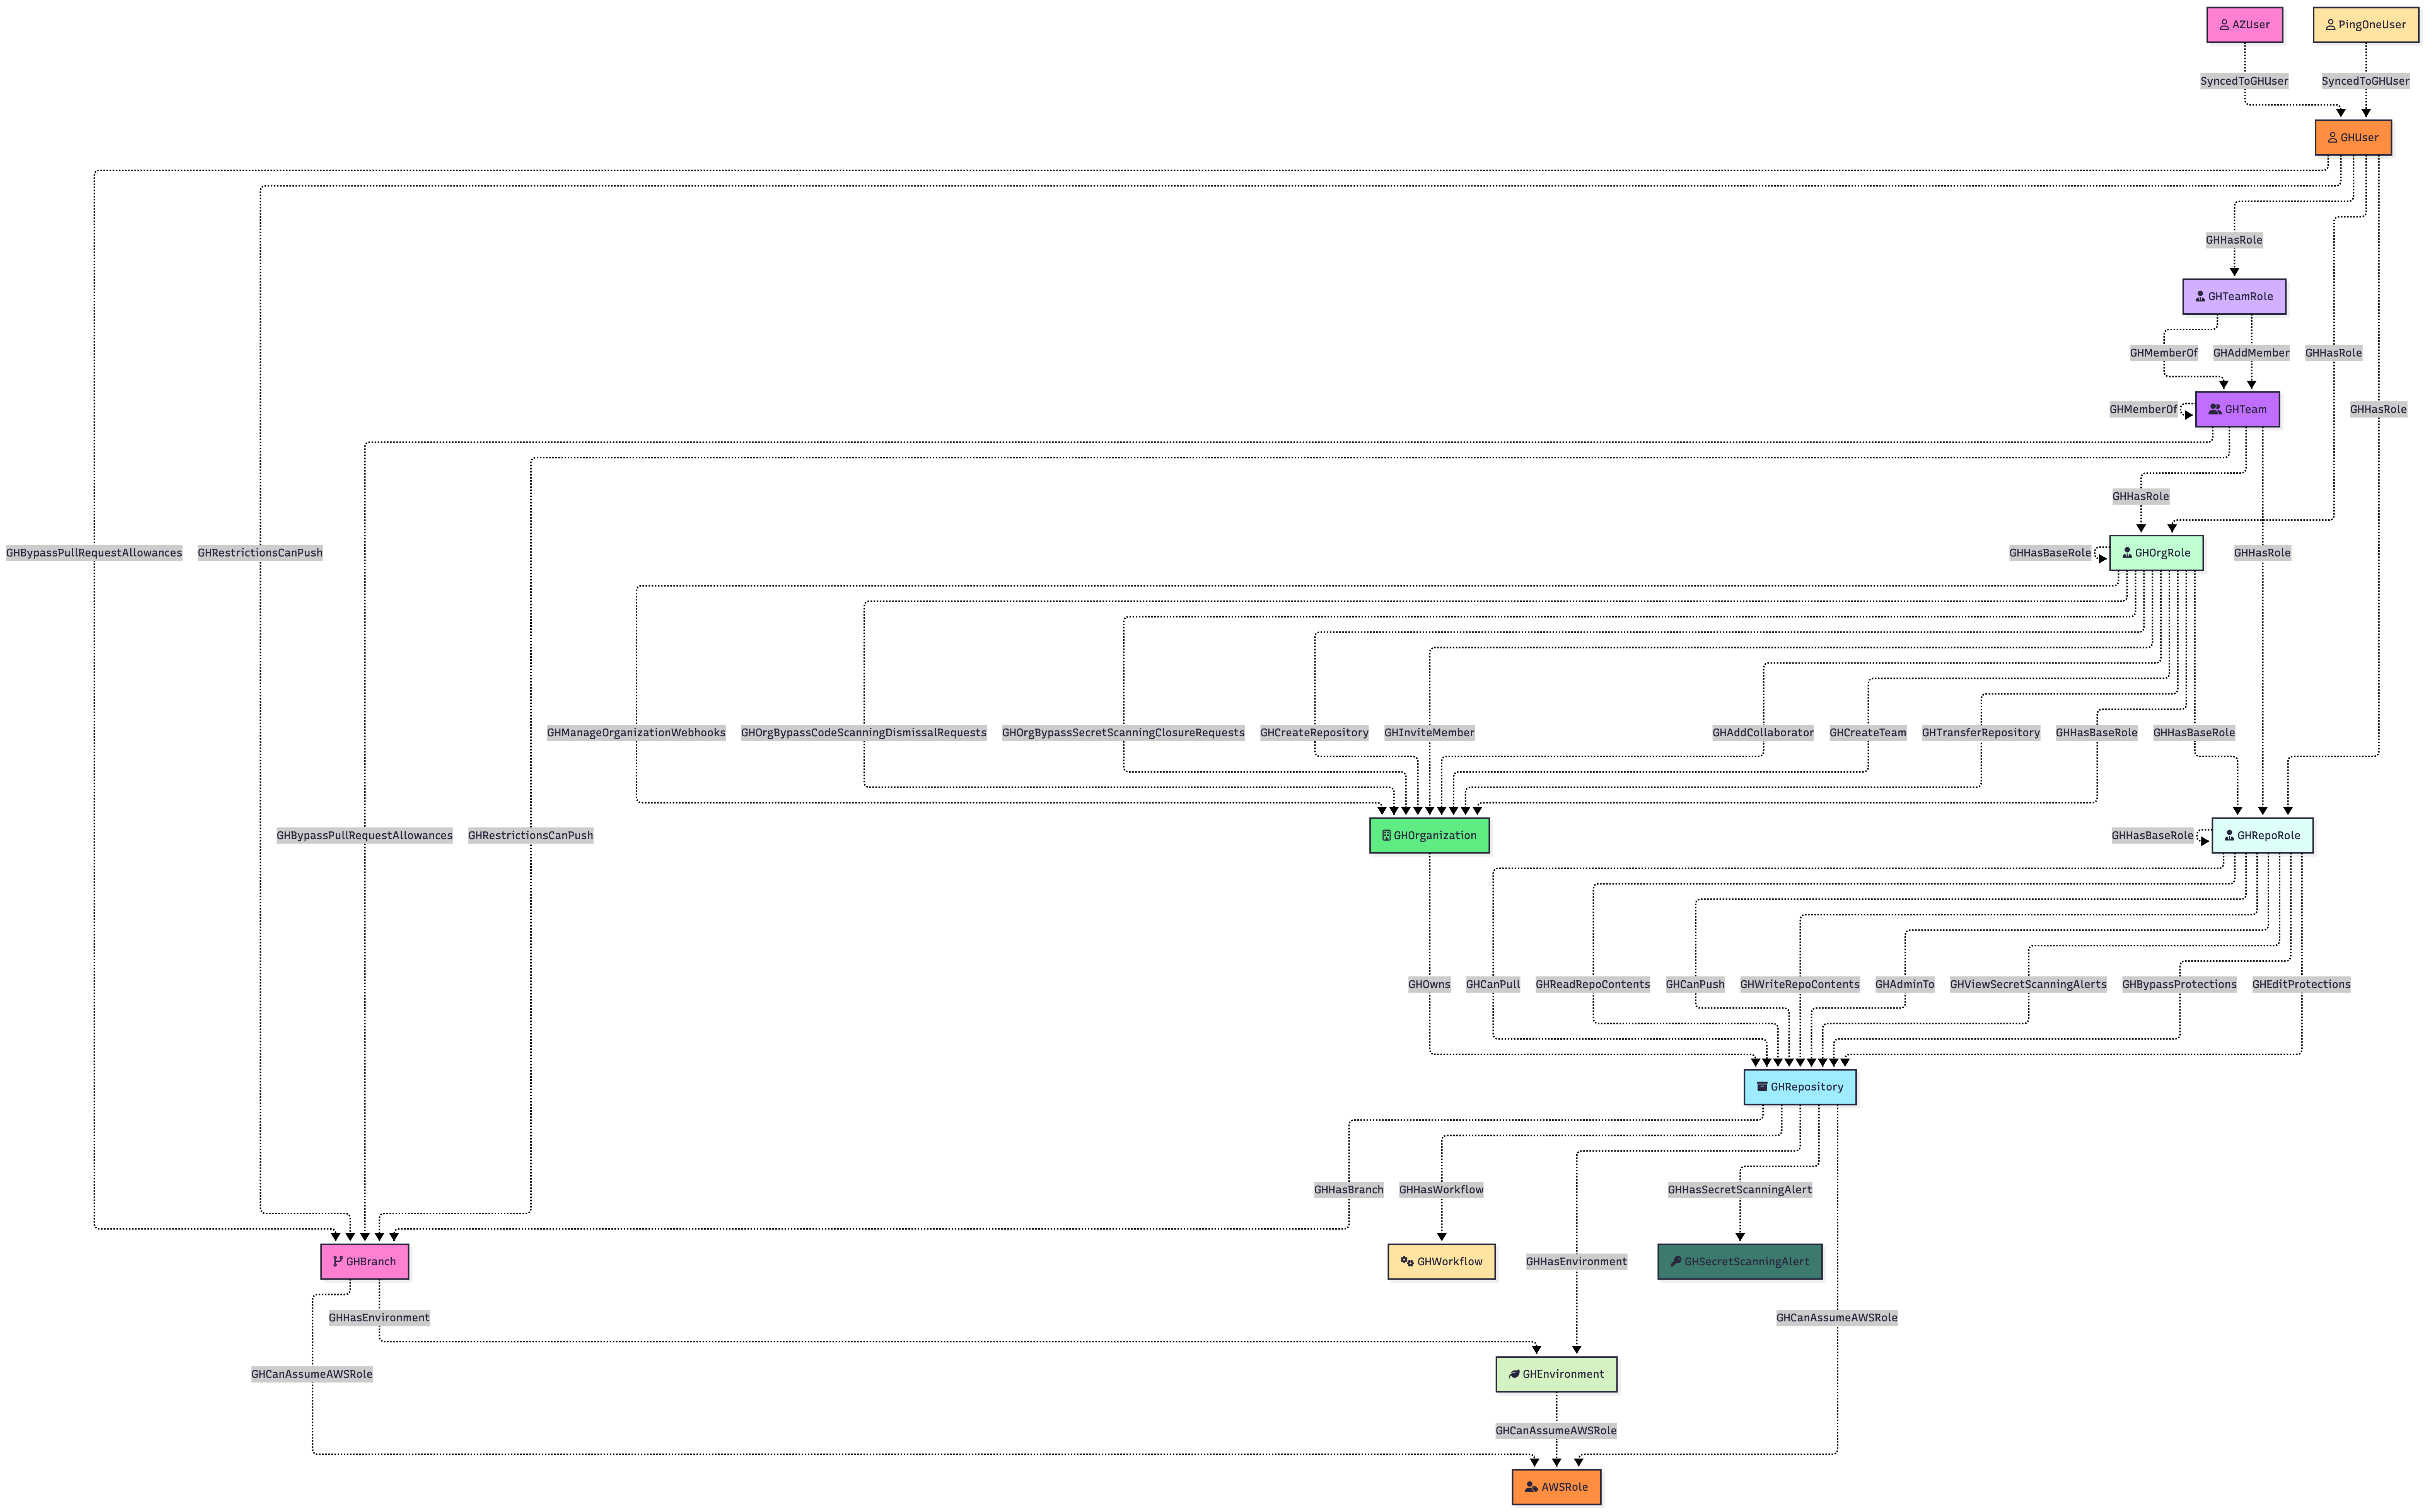 specterops/githound
BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…
 redbyte1337/credspy
Entra ID user enumeration and auth method discovery via the public GetCredentialType API
 logisek/evilmist
EvilMist is a collection of scripts and utilities designed to support cloud penetration testing & red teaming. The toolkit helps identify…
 bishopfox/cirro
Creating attacks paths across management and data planes
 drunkf0x/adspider
Monitor changes in Active Directory with replication metadata
 t94j0/adexplorersnapshot-rs
Converts Active Directory Explorer snapshot (.dat) files into BloodHound CE JSON archives for graph-based AD attack-path analysis and reconnaissance.
 daddycocoaman/azbelt
AAD related enumeration in Nim