
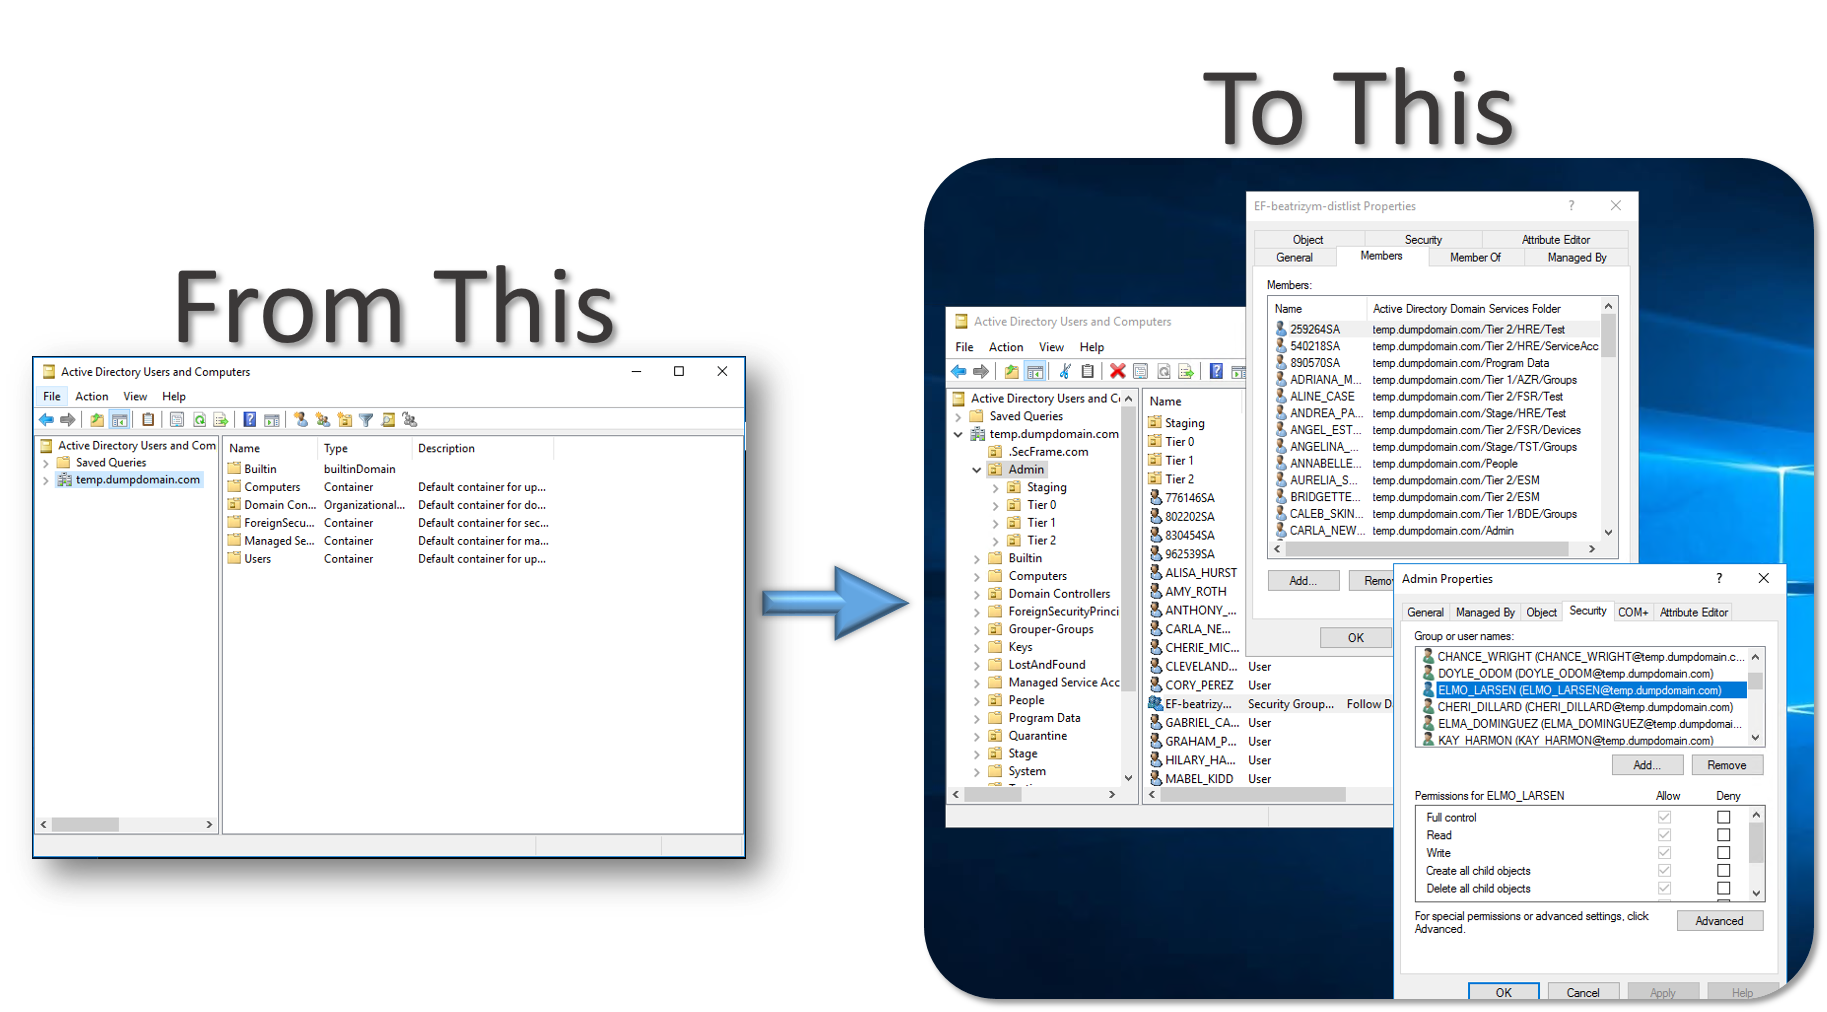
BadBlood
 davidprowe/badblood
BadBlood by @davidprowe, Secframe.com, fills a Microsoft Active Directory Domain with a structure and thousands of objects. The output of the tool is…
educationidentity-access-managementlabs-practice+1
2.3k
davidprowe/badbloodBadBlood by @davidprowe, Secframe.com, fills a Microsoft Active Directory Domain with a structure and thousands of objects. The output of the tool is…
 google/longfellow-zk
Implementation of the Google Zero-Knowledge library for Identity Protocols.
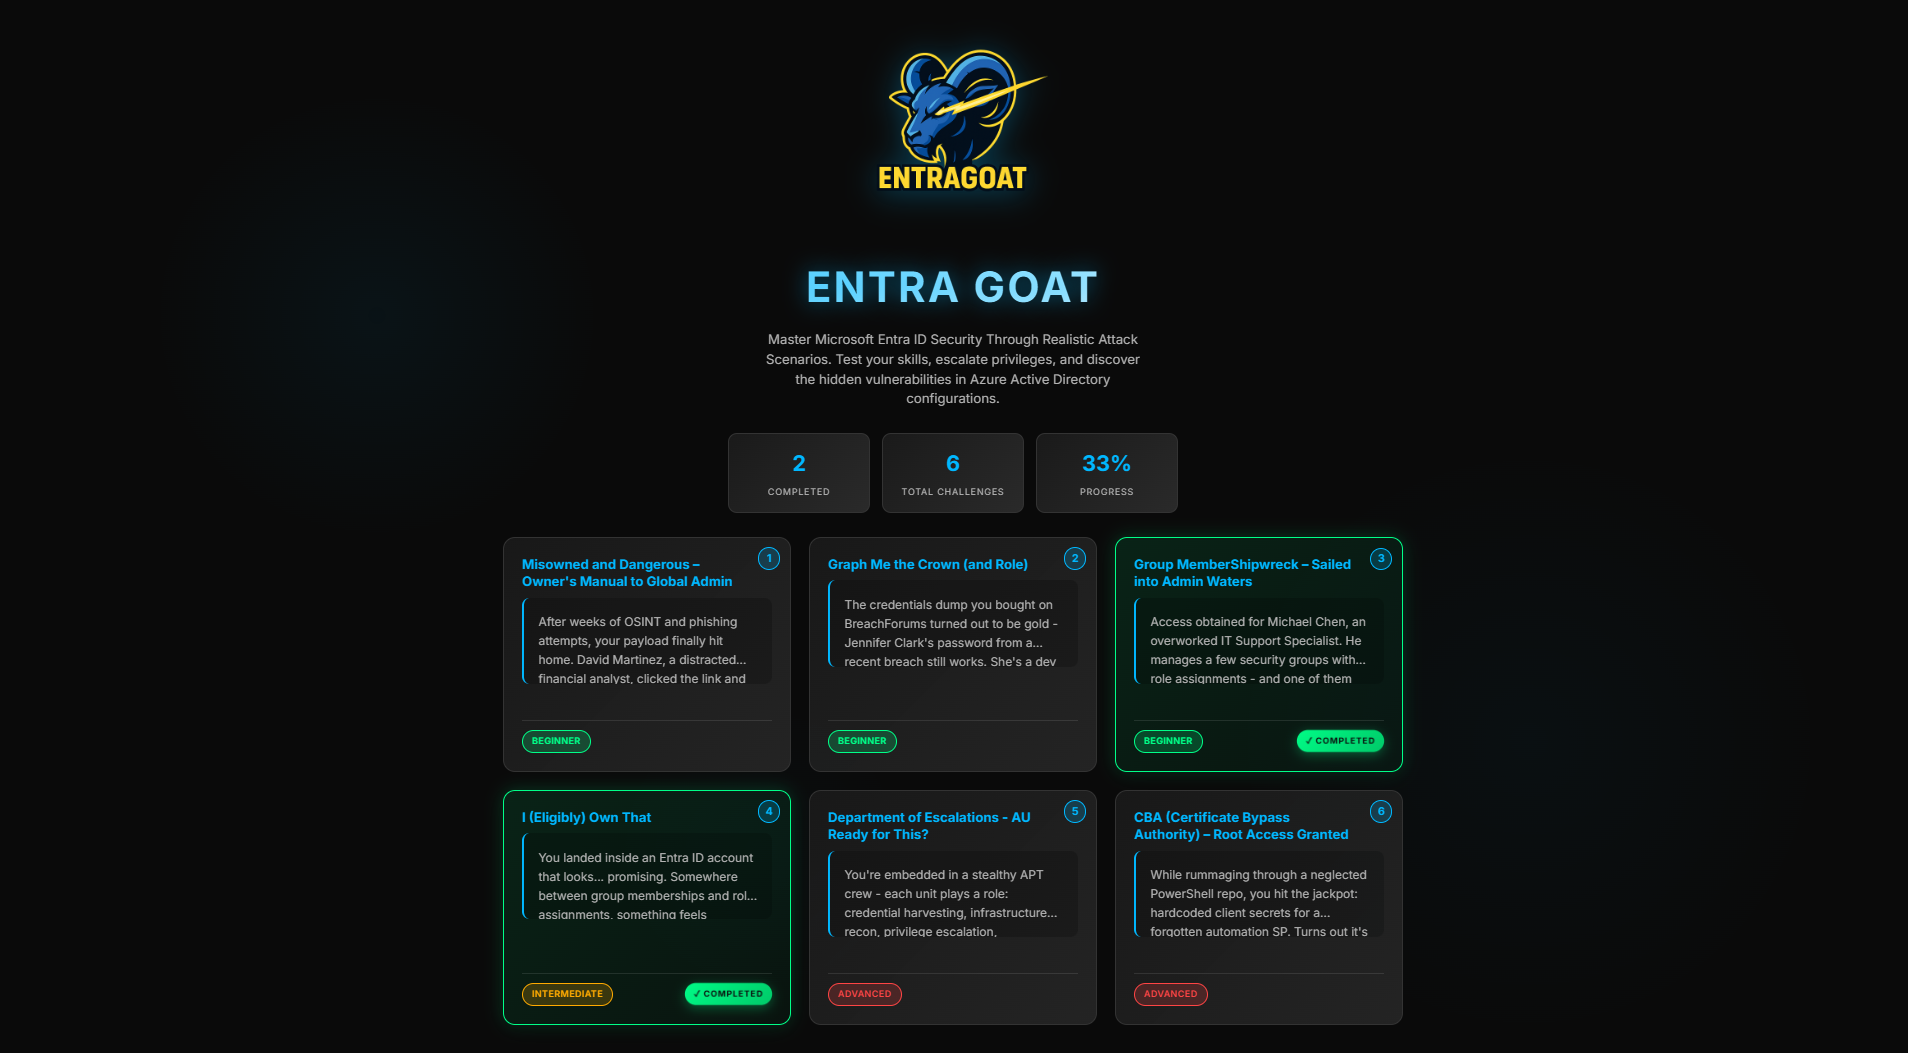 semperis/entragoat
A deliberately vulnerable Microsoft Entra ID environment. Learn identity security through hands-on, realistic attack challenges.
 mvelazc0/badzure
BadZure automates the deployment of intentionally misconfigured Entra ID tenants and Azure subscriptions, populating them with diverse entities and…
 bishopfox/iam-vulnerable
Use Terraform to create your own vulnerable by design AWS IAM privilege escalation playground.
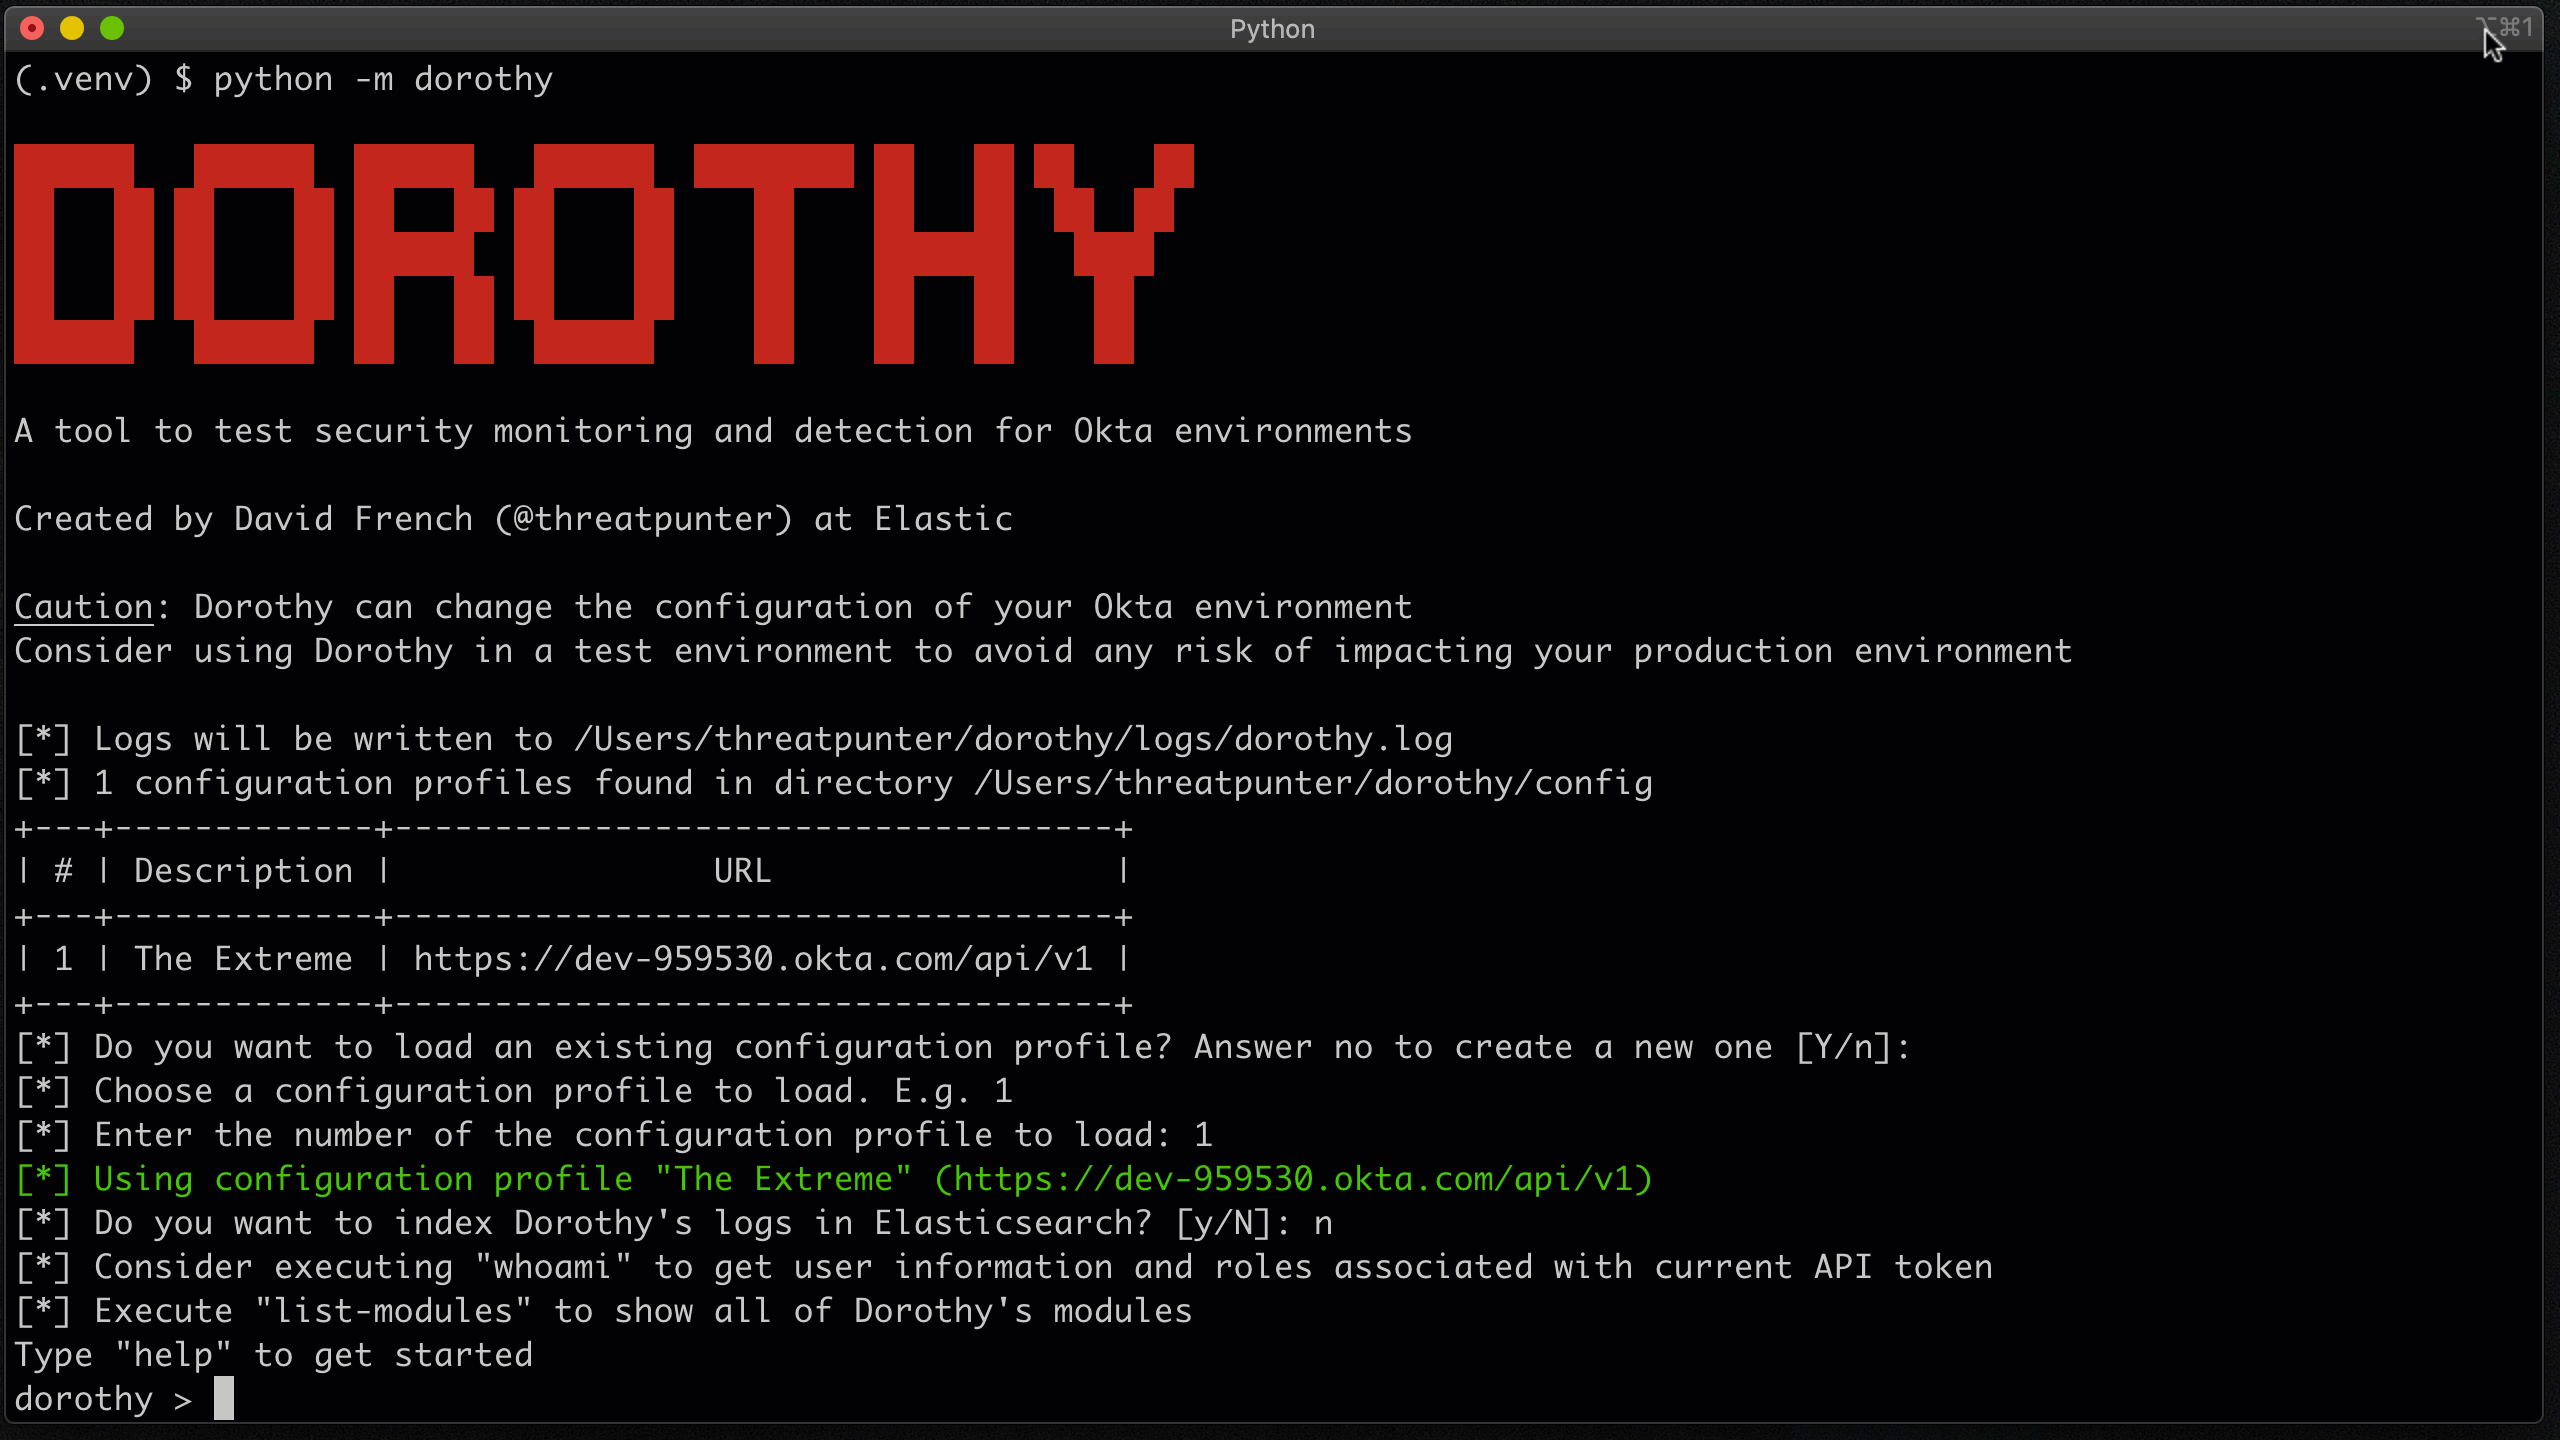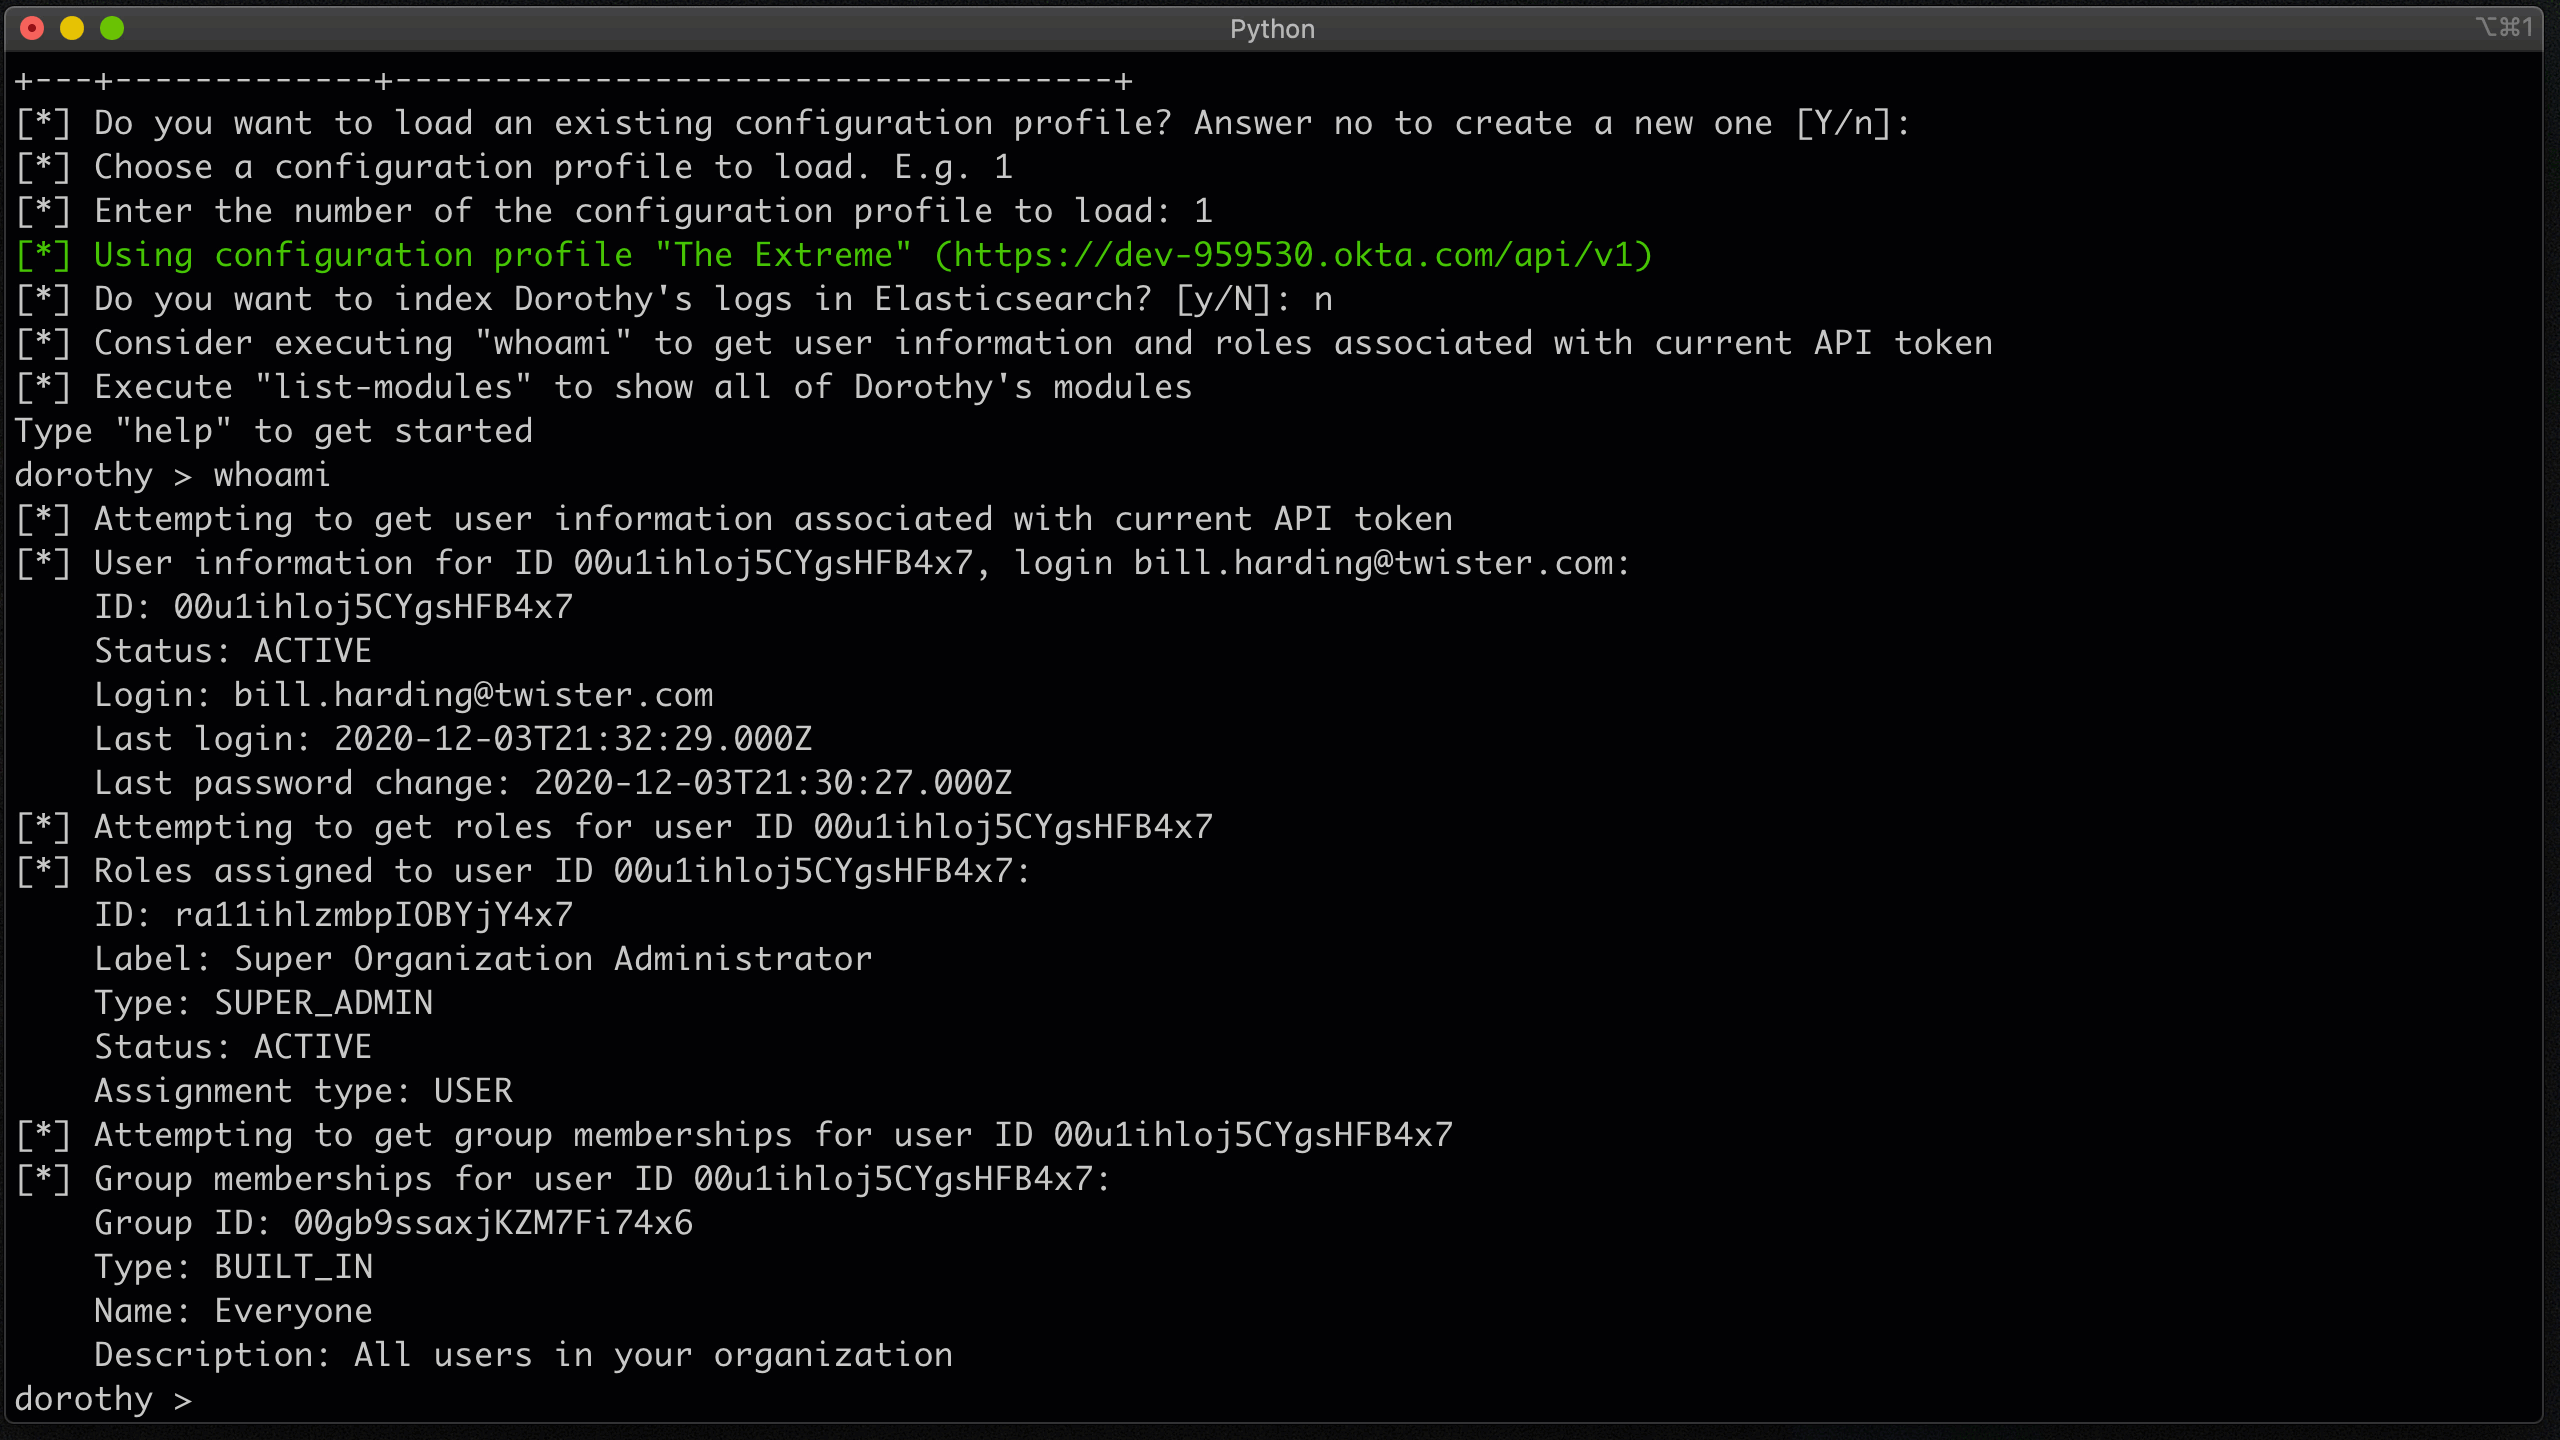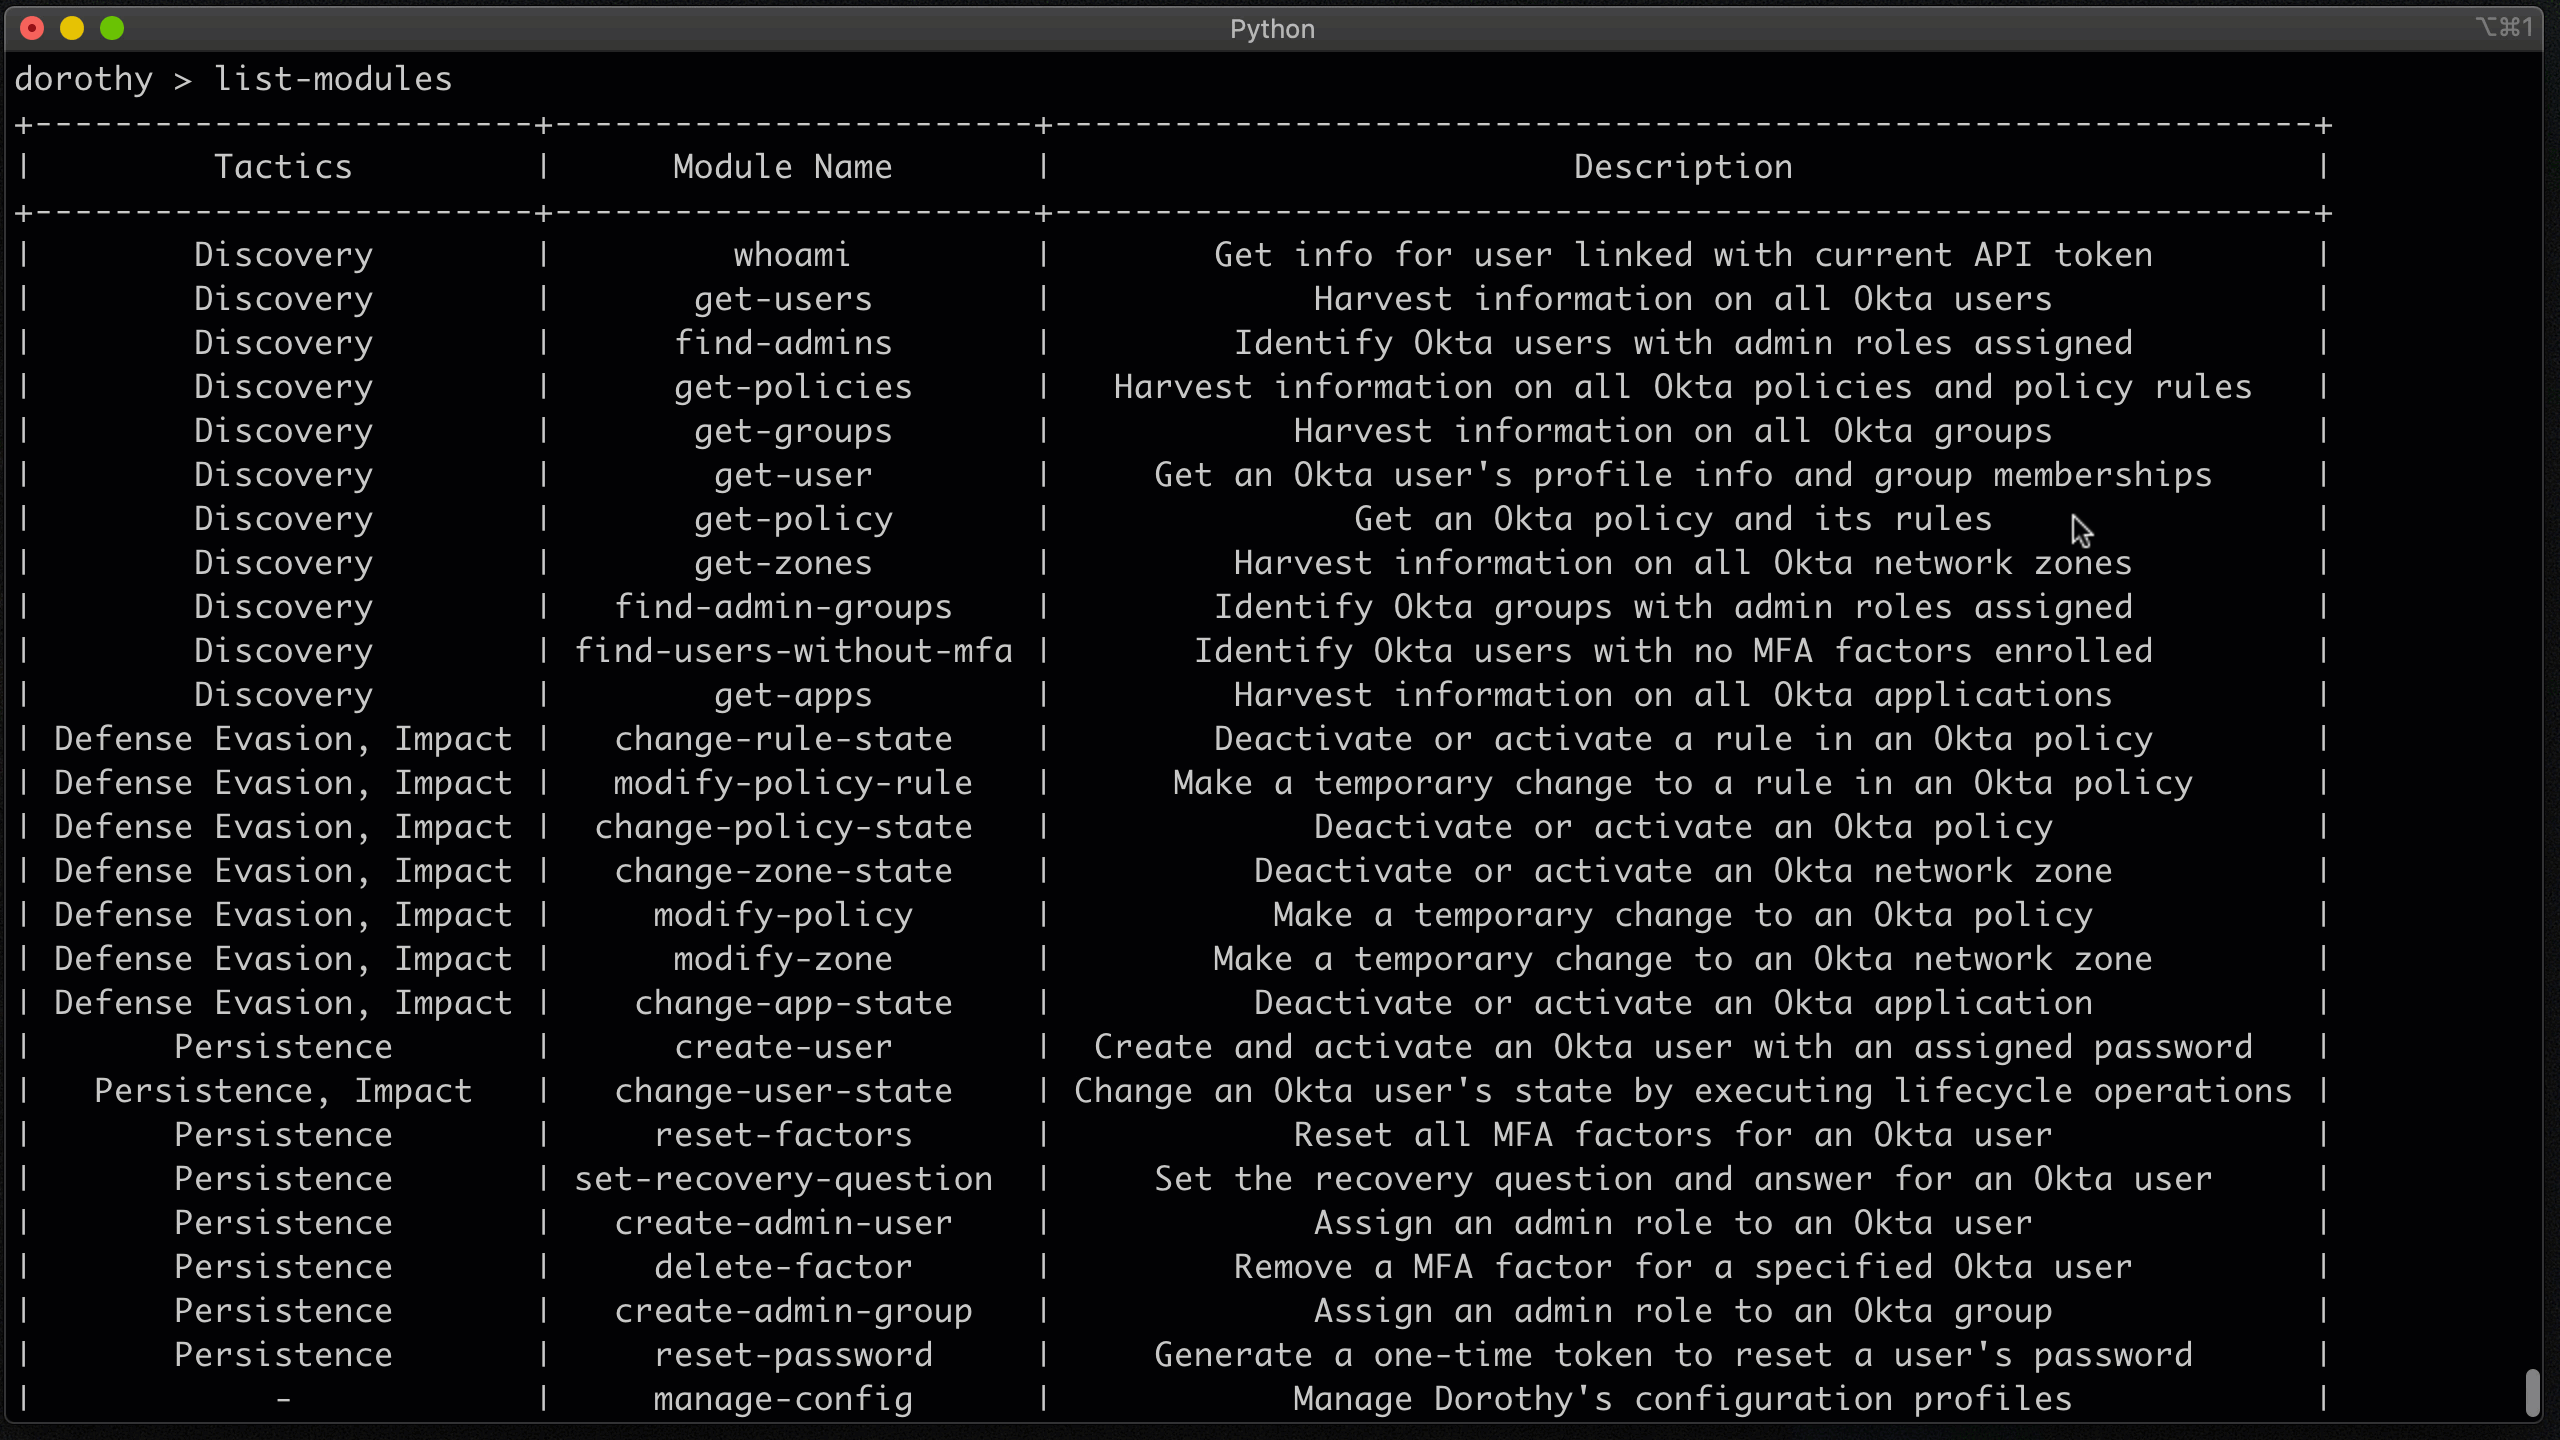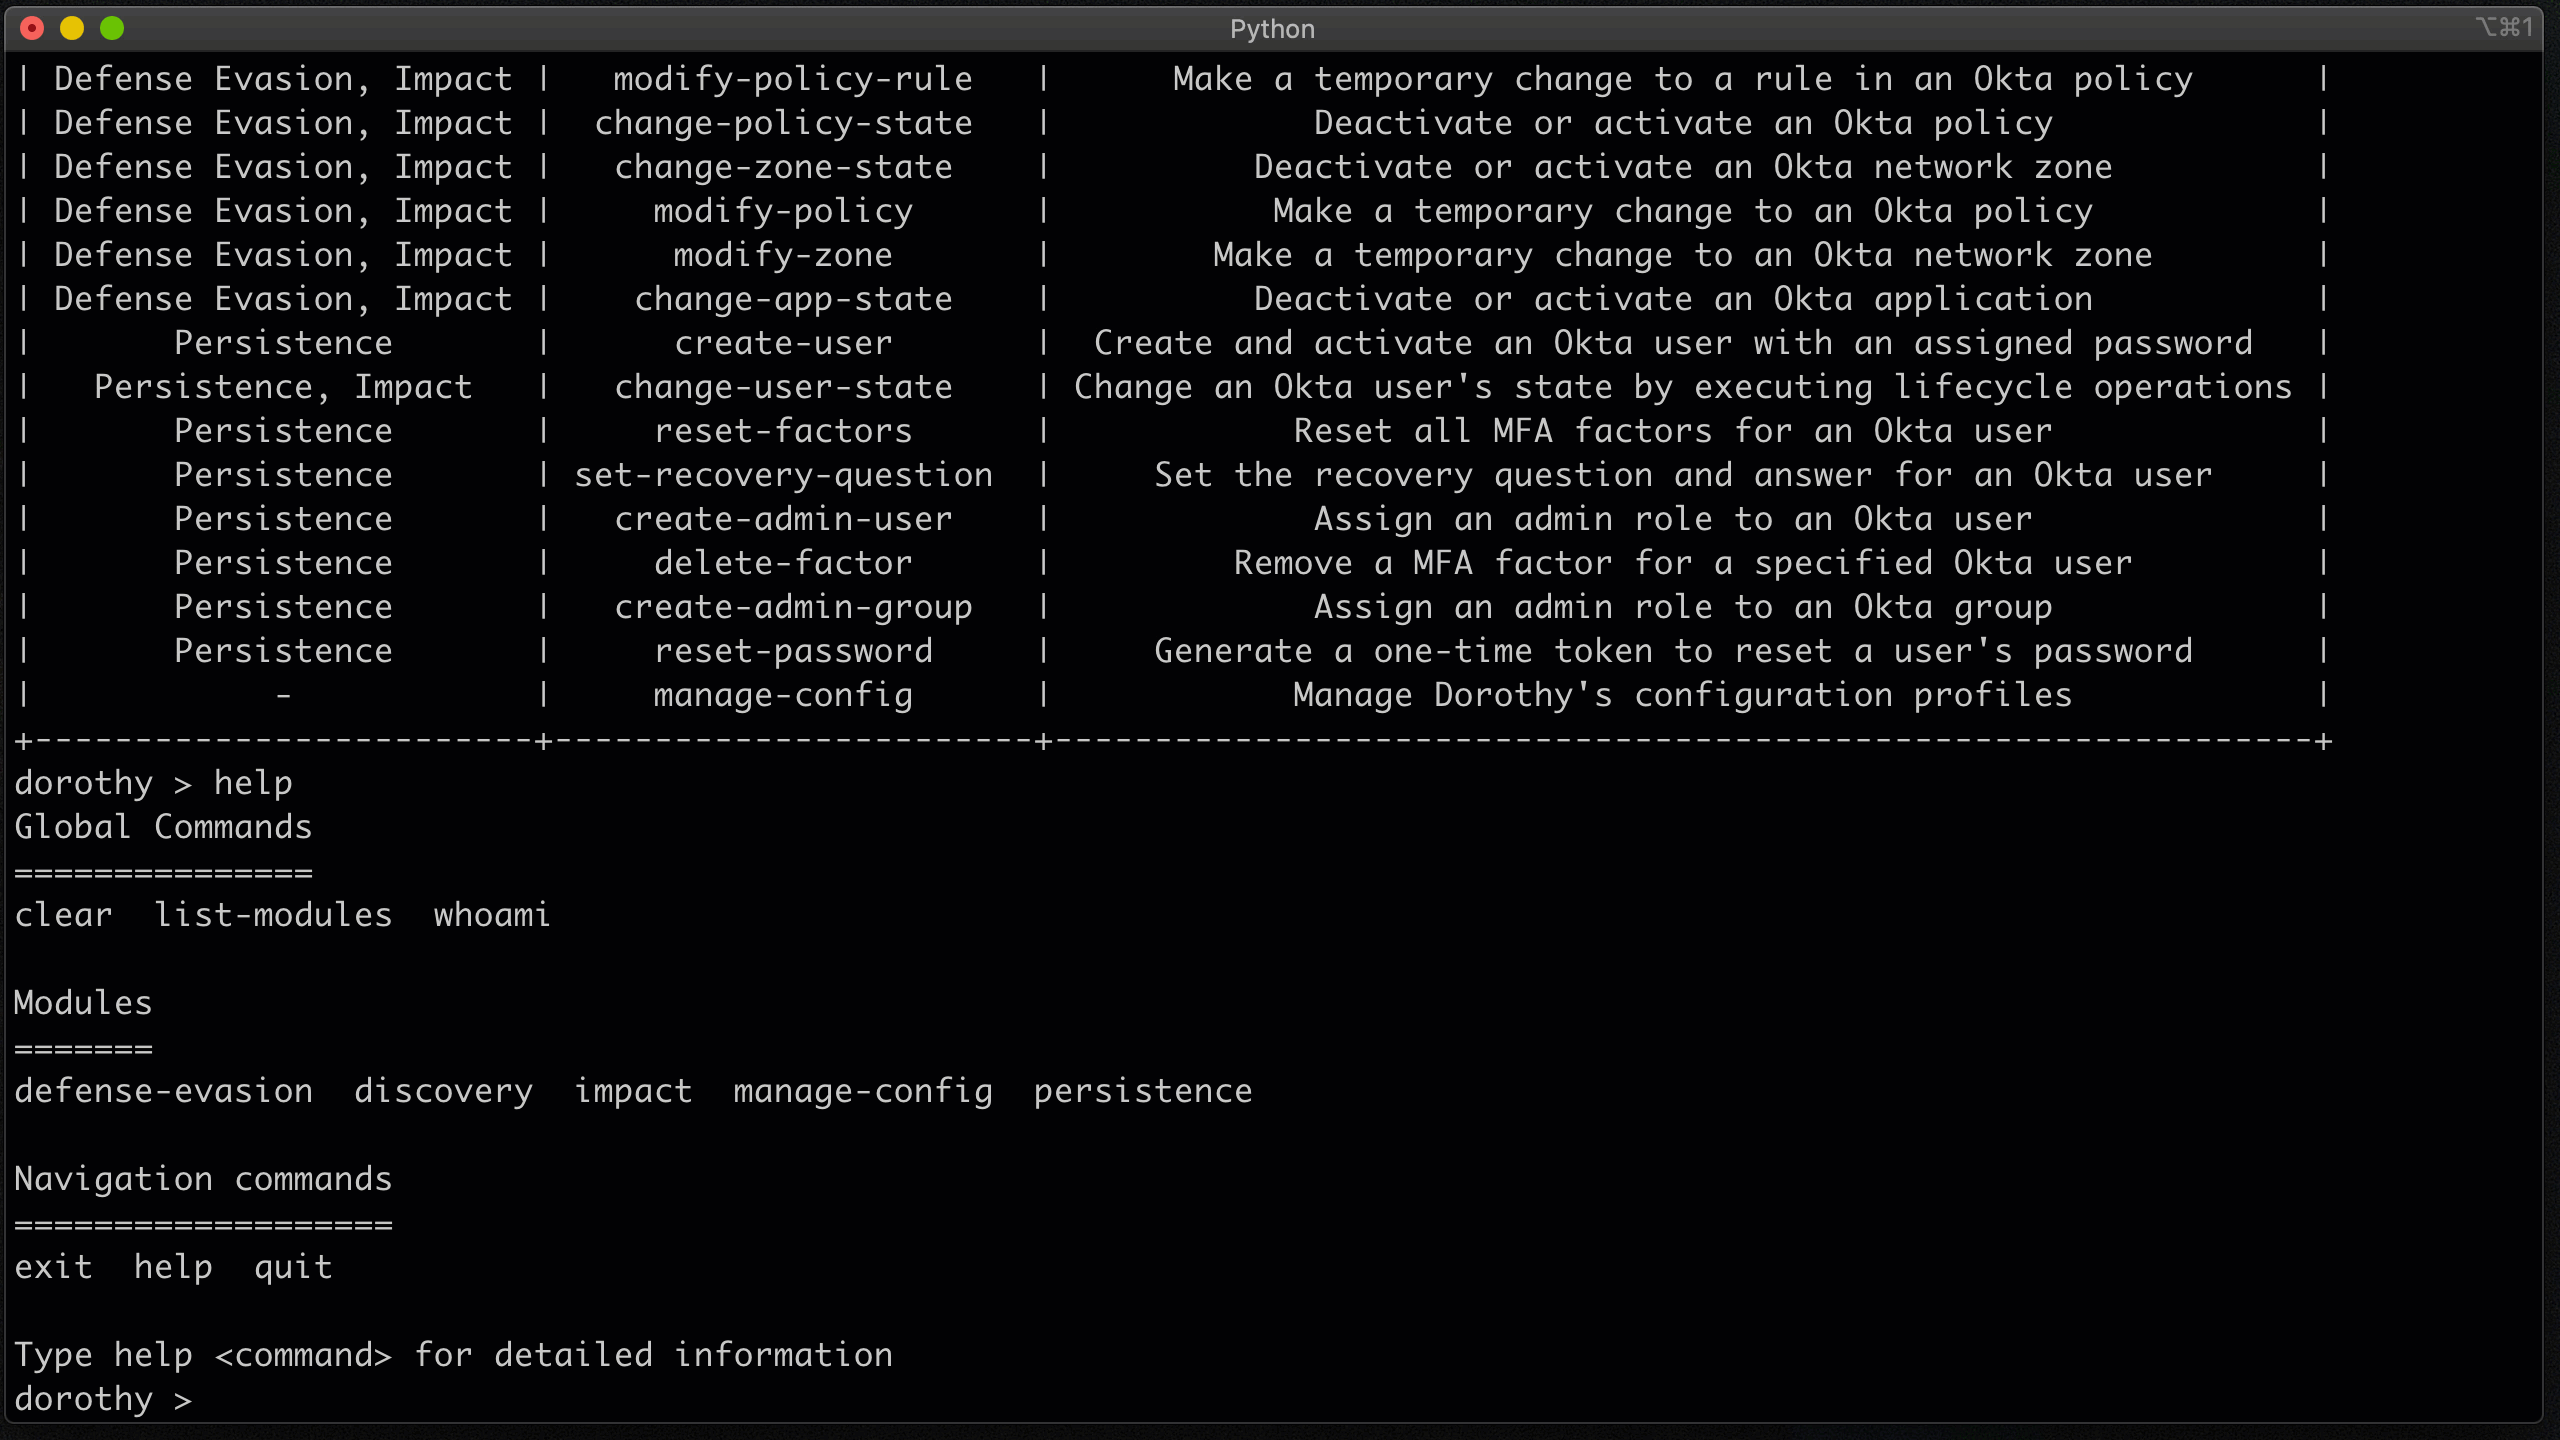 elastic/dorothy
Simulates attacker actions in Okta environments to test monitoring and detection capabilities, with modules mapped to MITRE ATT&CK tactics for red…
 ivanesk315/cve-2026-18963
Docker-based lab and Python exploit for CVE-2026-18963, a Keycloak reset-credentials flow bypass enabling account takeover via email verification…
 dobybaxter127/nimbus-vestige
A forensic reconstruction engine for cloud and identity incident response.
 karitamw/printnightmare-detection-mitigation-lab
Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.
 karaaslanlabs/kl-security-key
Experimental RP2040 FIDO2/WebAuthn authenticator with packed attestation and documented Windows/Entra interoperability