
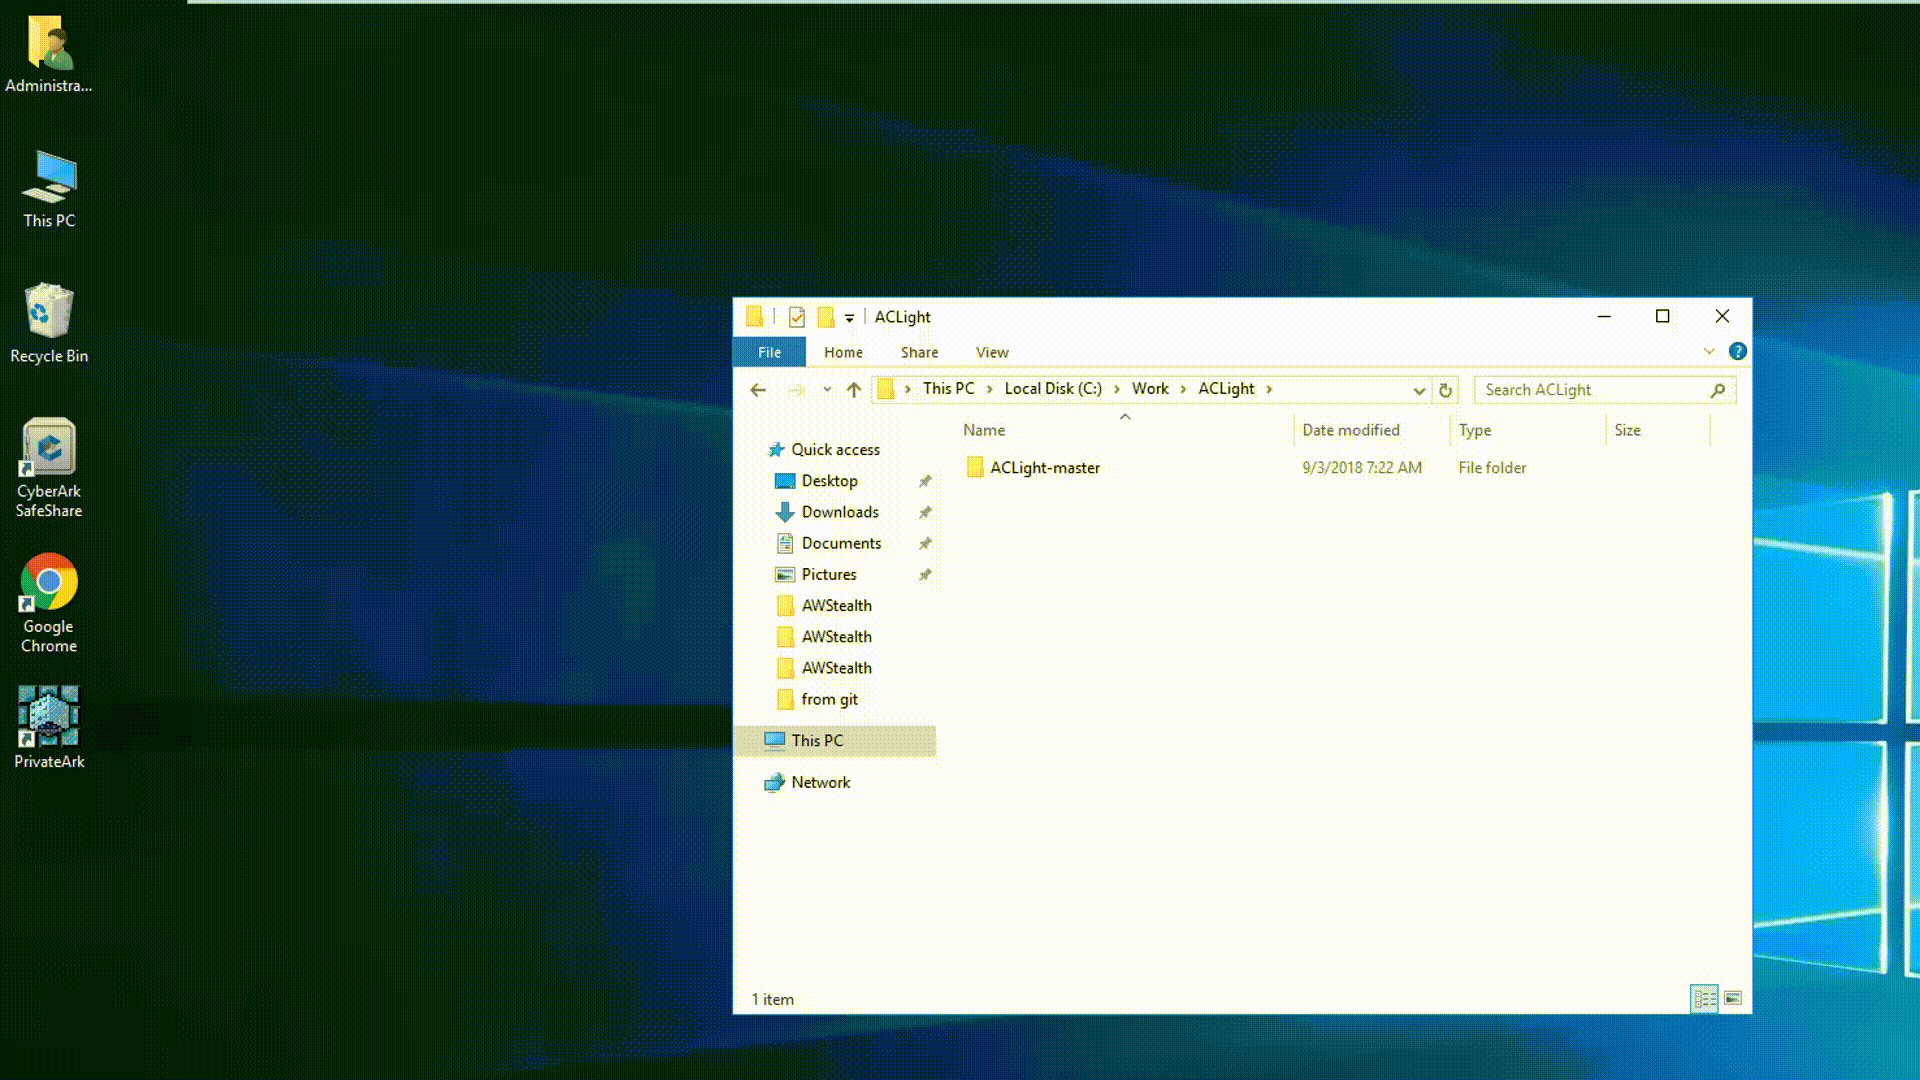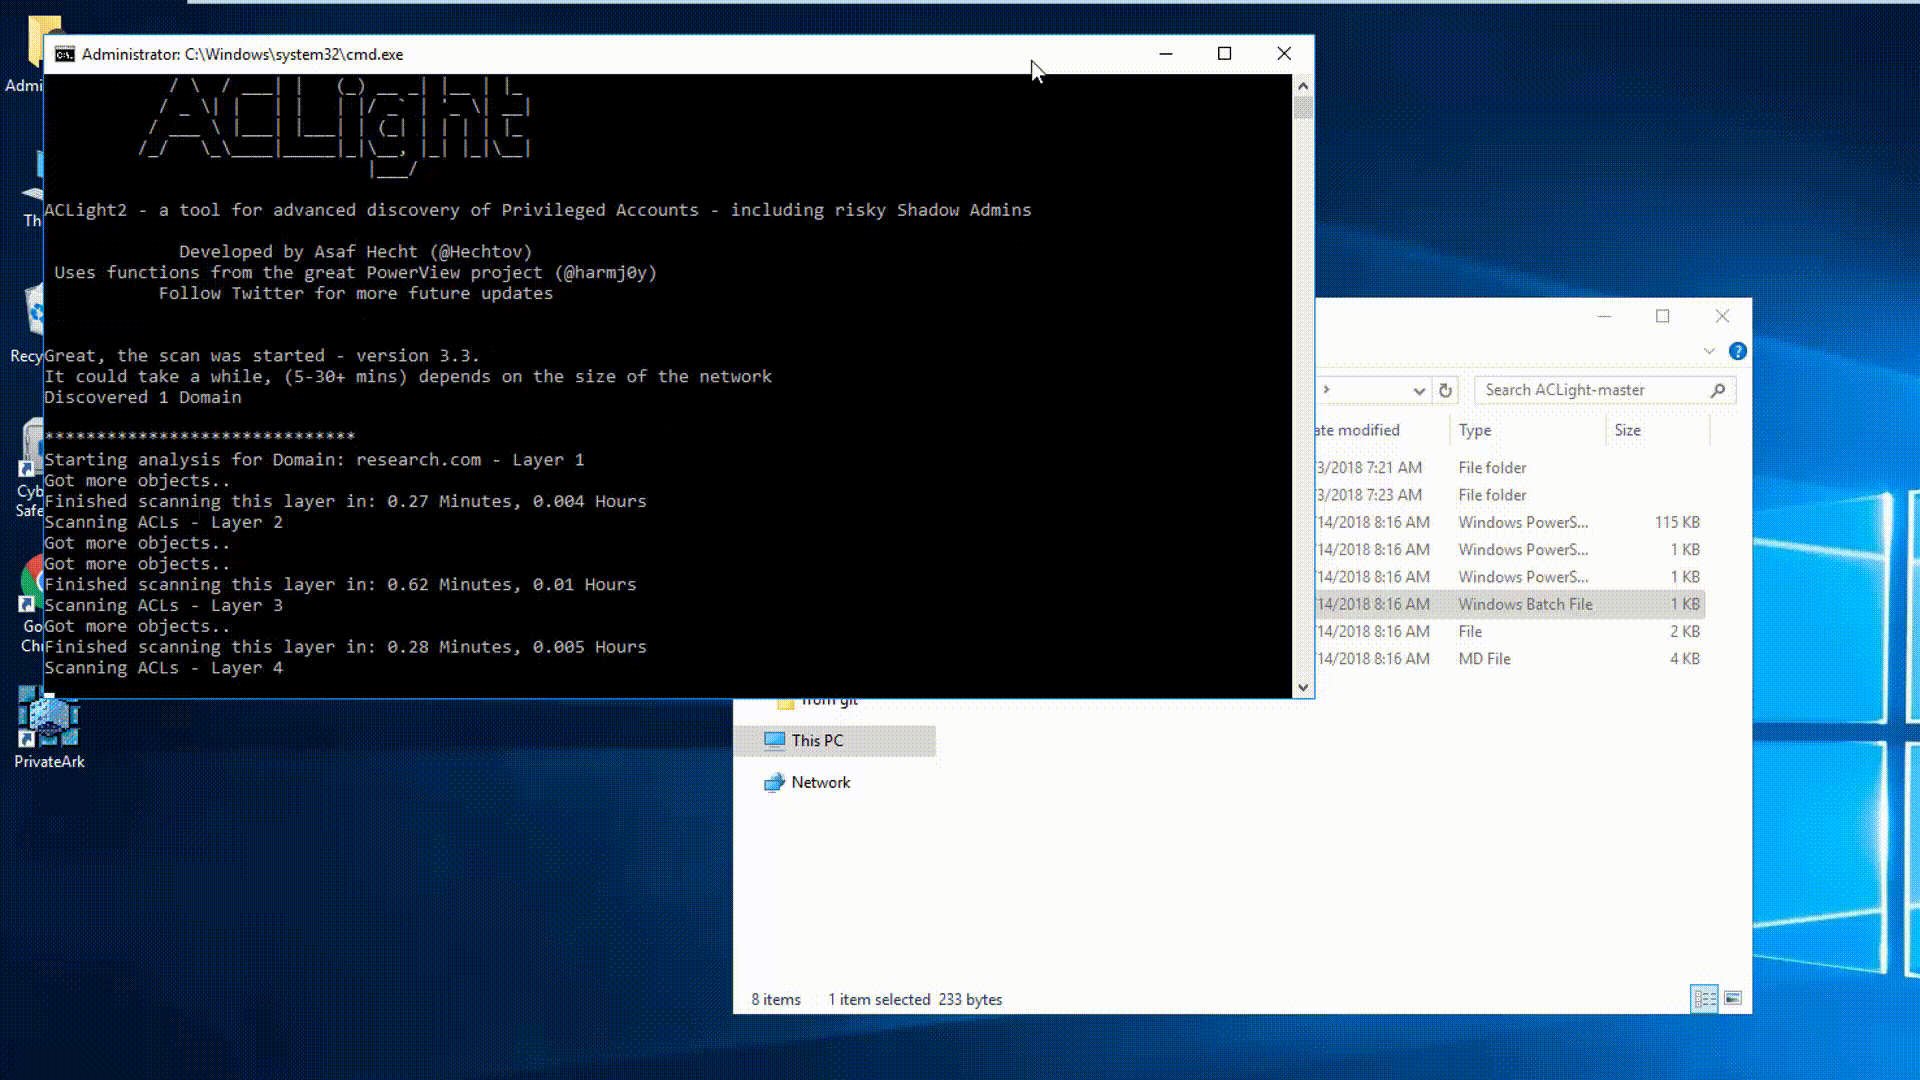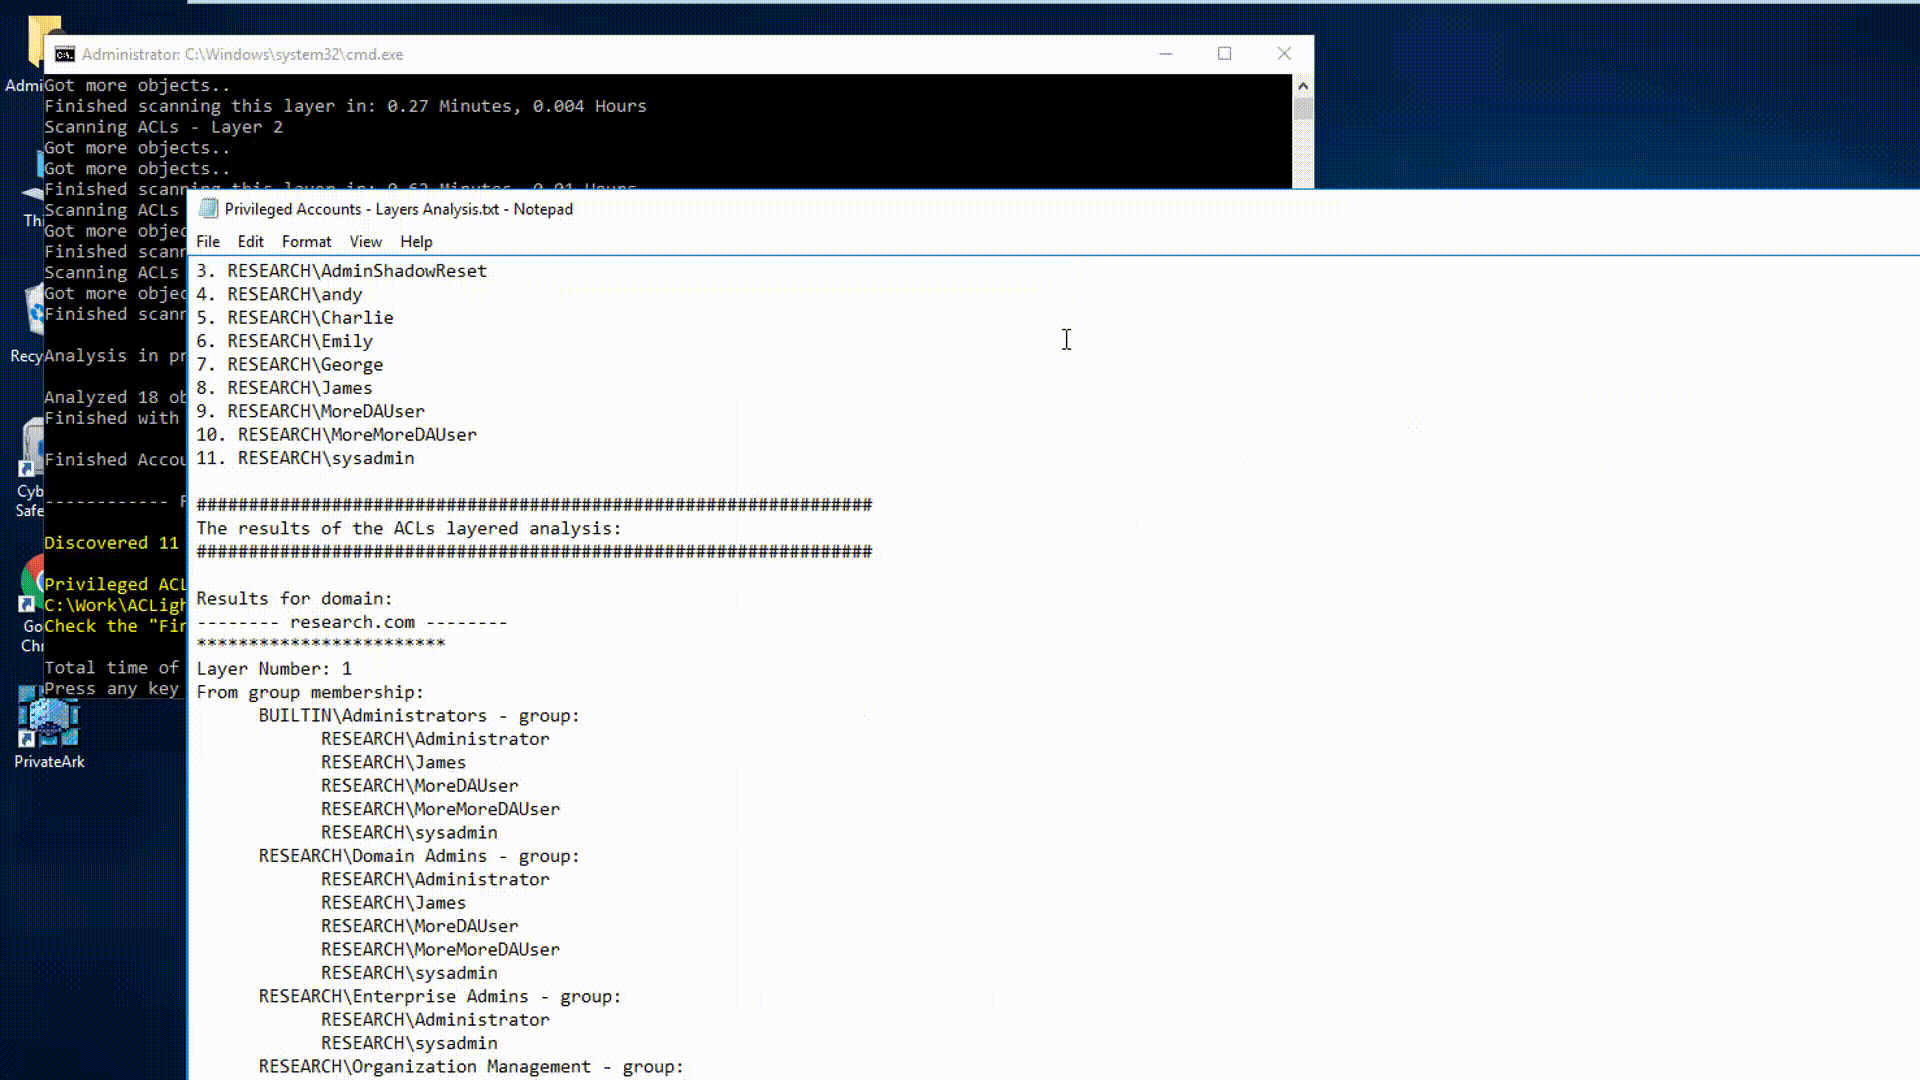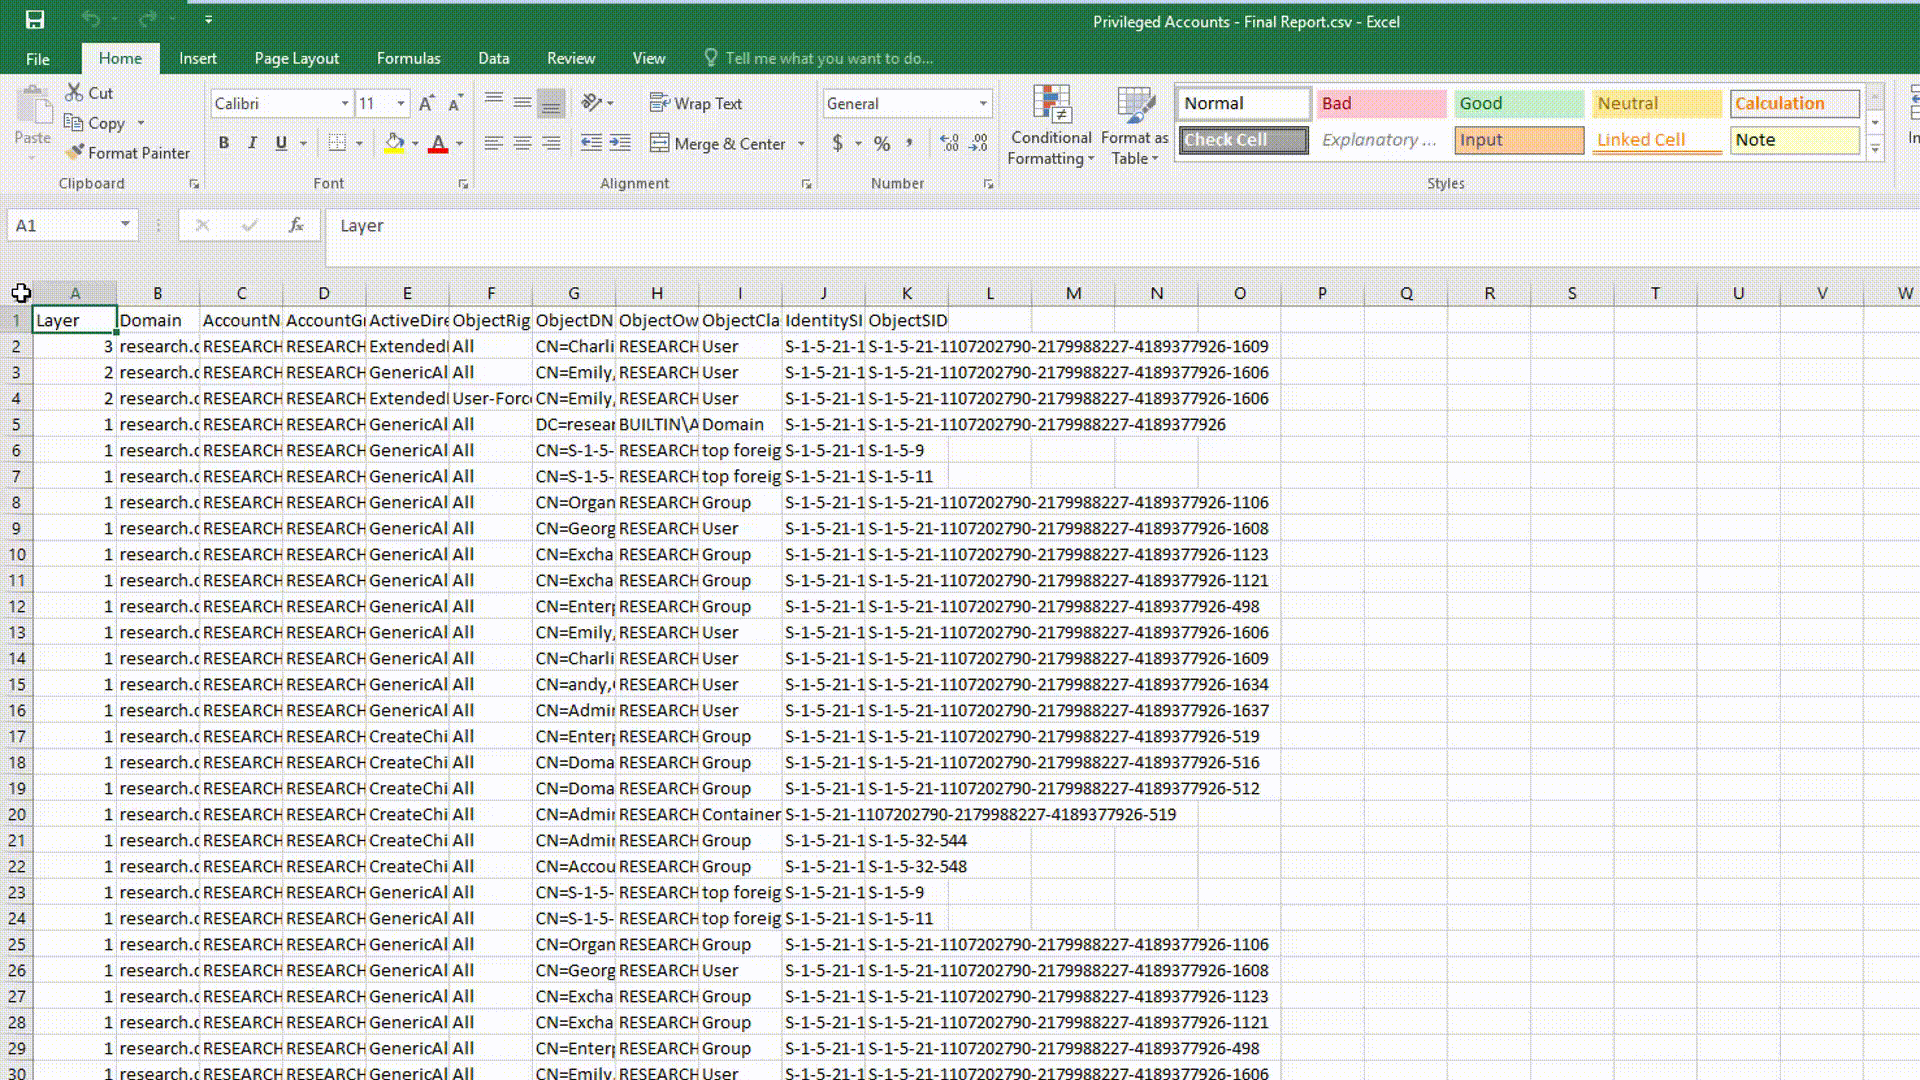
ACLight
 cyberark/aclight
A script for advanced discovery of Privileged Accounts - includes Shadow Admins
identity-access-managementprivilege-escalation
cyberark/aclightA script for advanced discovery of Privileged Accounts - includes Shadow Admins
 crowdstrike/crt
Audits Azure AD and Exchange Online configurations for hard-to-find permissions, federation trusts, mail forwarding rules, and delegated access to…
 microsoft/windowsprotocoltestsuites
⭐⭐ Join us at SNIA SDC for the SMB3 IO Lab (September 28 - October 1, 2026), see upcoming Interoperability Events
 netflix/repokid
AWS Least Privilege for Distributed, High-Velocity Deployment
 cisagov/scubagoggles
SCuBA Secure Configuration Baselines and assessment tool for Google Workspace
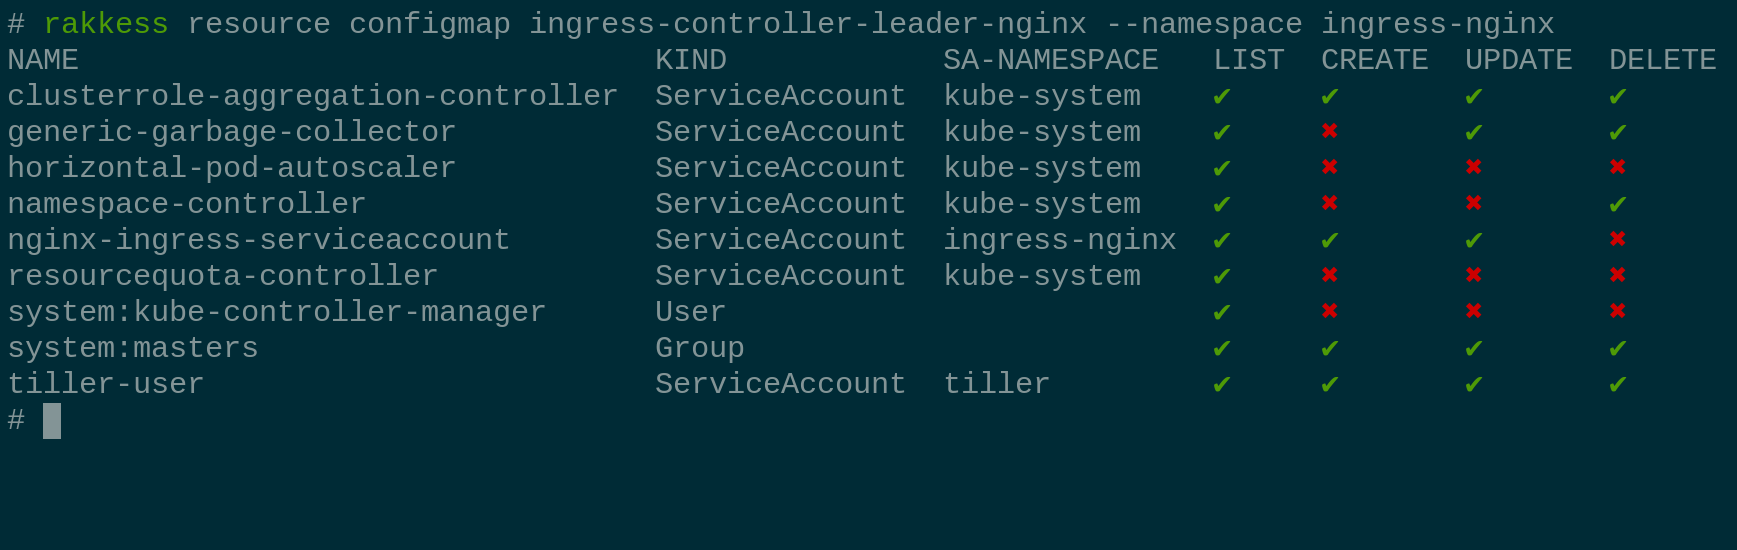 corneliusweig/rakkess
Review Access - kubectl plugin to show an access matrix for k8s server resources
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
 azuread/azureadassessment
Tooling for assessing an Azure AD tenant state and configuration
 cosai-oasis/ws4-secure-design-agentic-systems
Repository for CoSAI Workstream 4, Secure Design Patterns for Agentic Systems
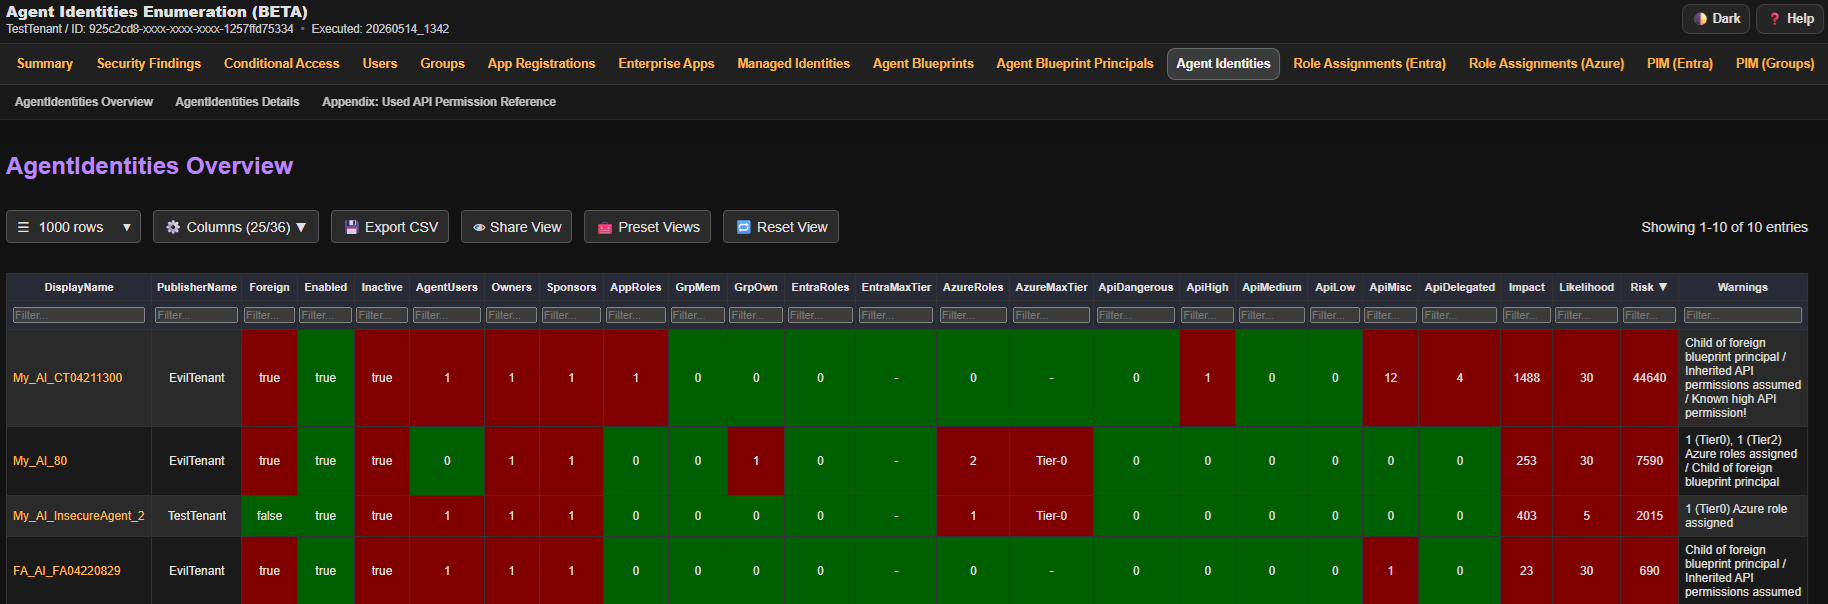 compasssecurity/entrafalcon
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…
 vectra-ai-research/maad-af
MAAD Attack Framework - An attack tool for simple, fast & effective security testing of M365 & Entra ID (Azure AD).
 kontext-security/kontext-cli
Runtime security for AI agents: discover agents, map their permissions, and enforce what they can do.
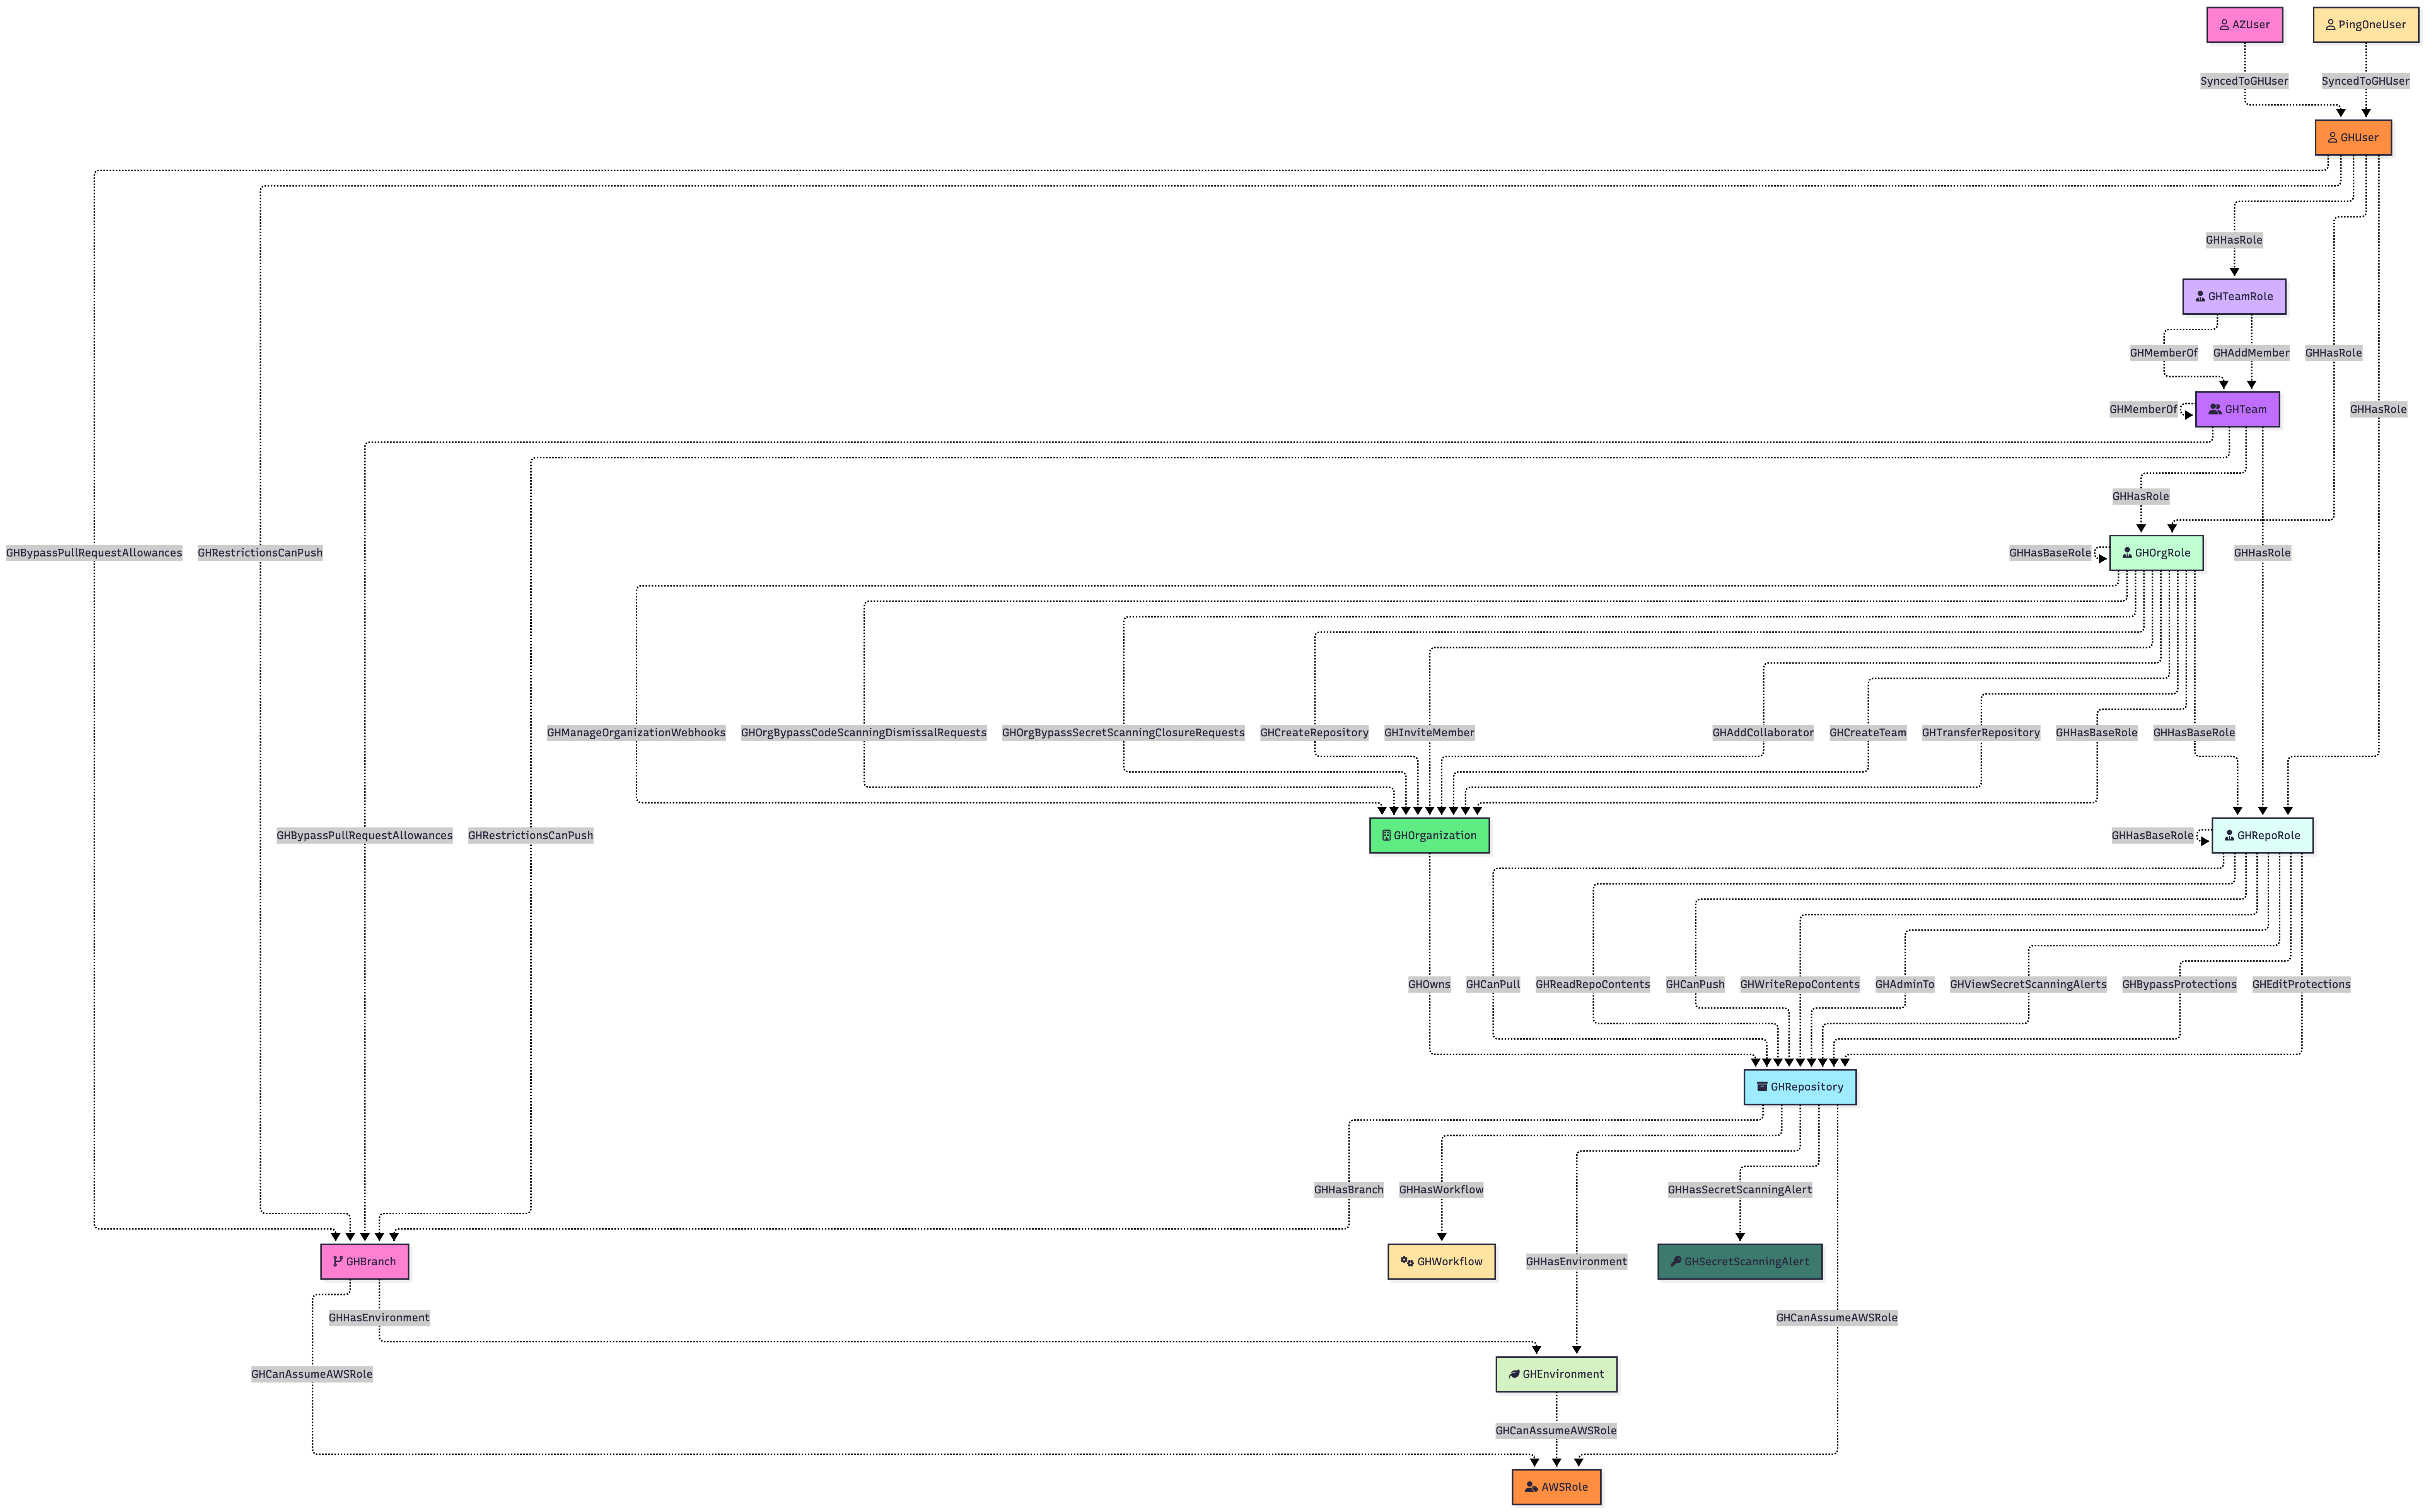 specterops/githound
BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…
 logangoins/cable
.NET post-exploitation toolkit for Active Directory reconnaissance and exploitation
 jakehildreth/locksmith2
An AD CS toolkit for AD Admins, Defensive Security Professionals, and Filthy Red Teamers
 tuskira/ai-agent-gateway
Open-source gateway that secures, governs, and observes AI agents' MCP tool calls and LLM traffic, with API-key authentication and an admin console…
 ibm-security/ibmsecurity
Idempotent functions for IBM Security Appliance REST APIs. Currently covering ISAM and ISDS Appliances.
 zephrfish/azureattackkit
Collection of Azure Tools to Pull down for Attacking an Environment + quick tips and other useful information