

BloodHound
 specterops/bloodhound
Six Degrees of Domain Admin
defensive-toolsidentity-access-managementinformation-gathering+4
specterops/bloodhoundSix Degrees of Domain Admin
 bishopfox/cirro
Creating attacks paths across management and data planes
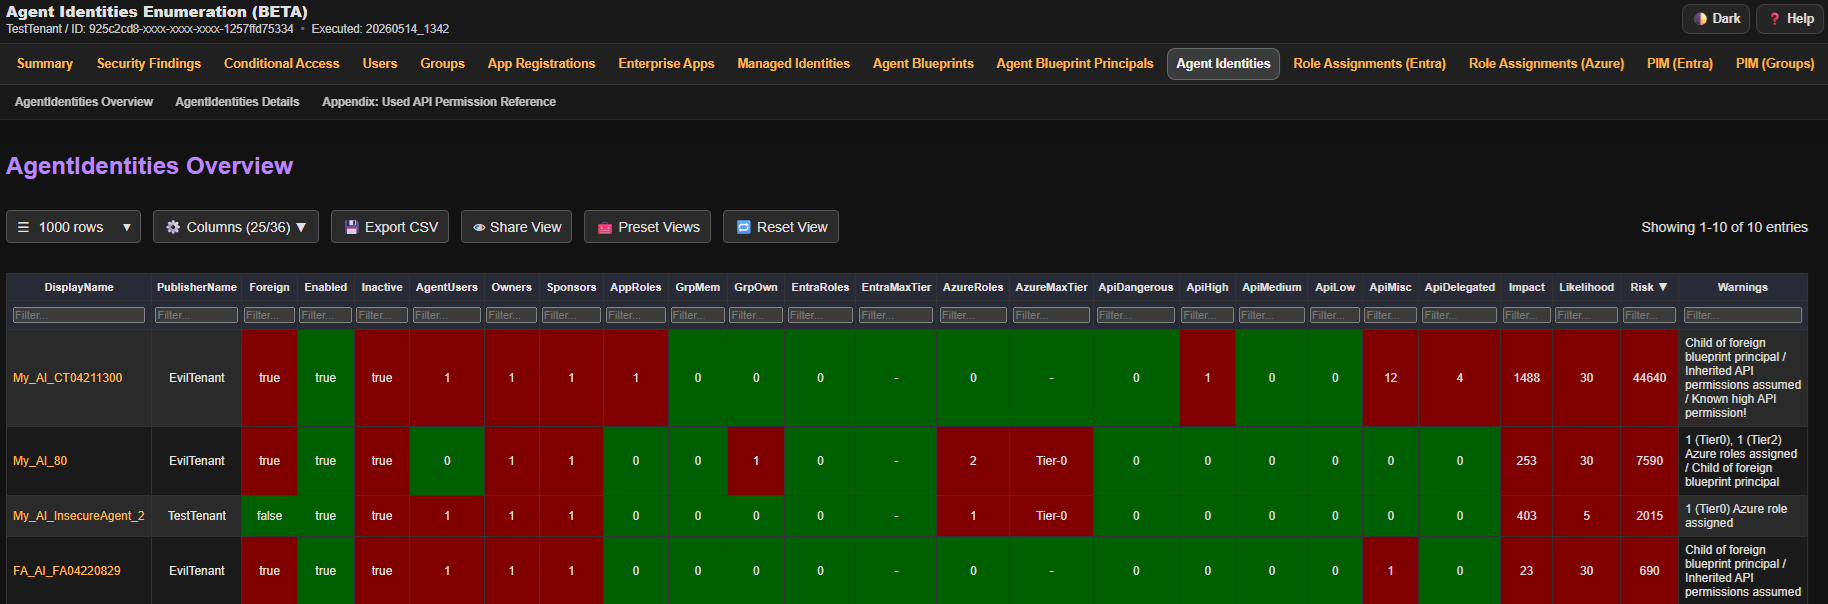 compasssecurity/entrafalcon
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…
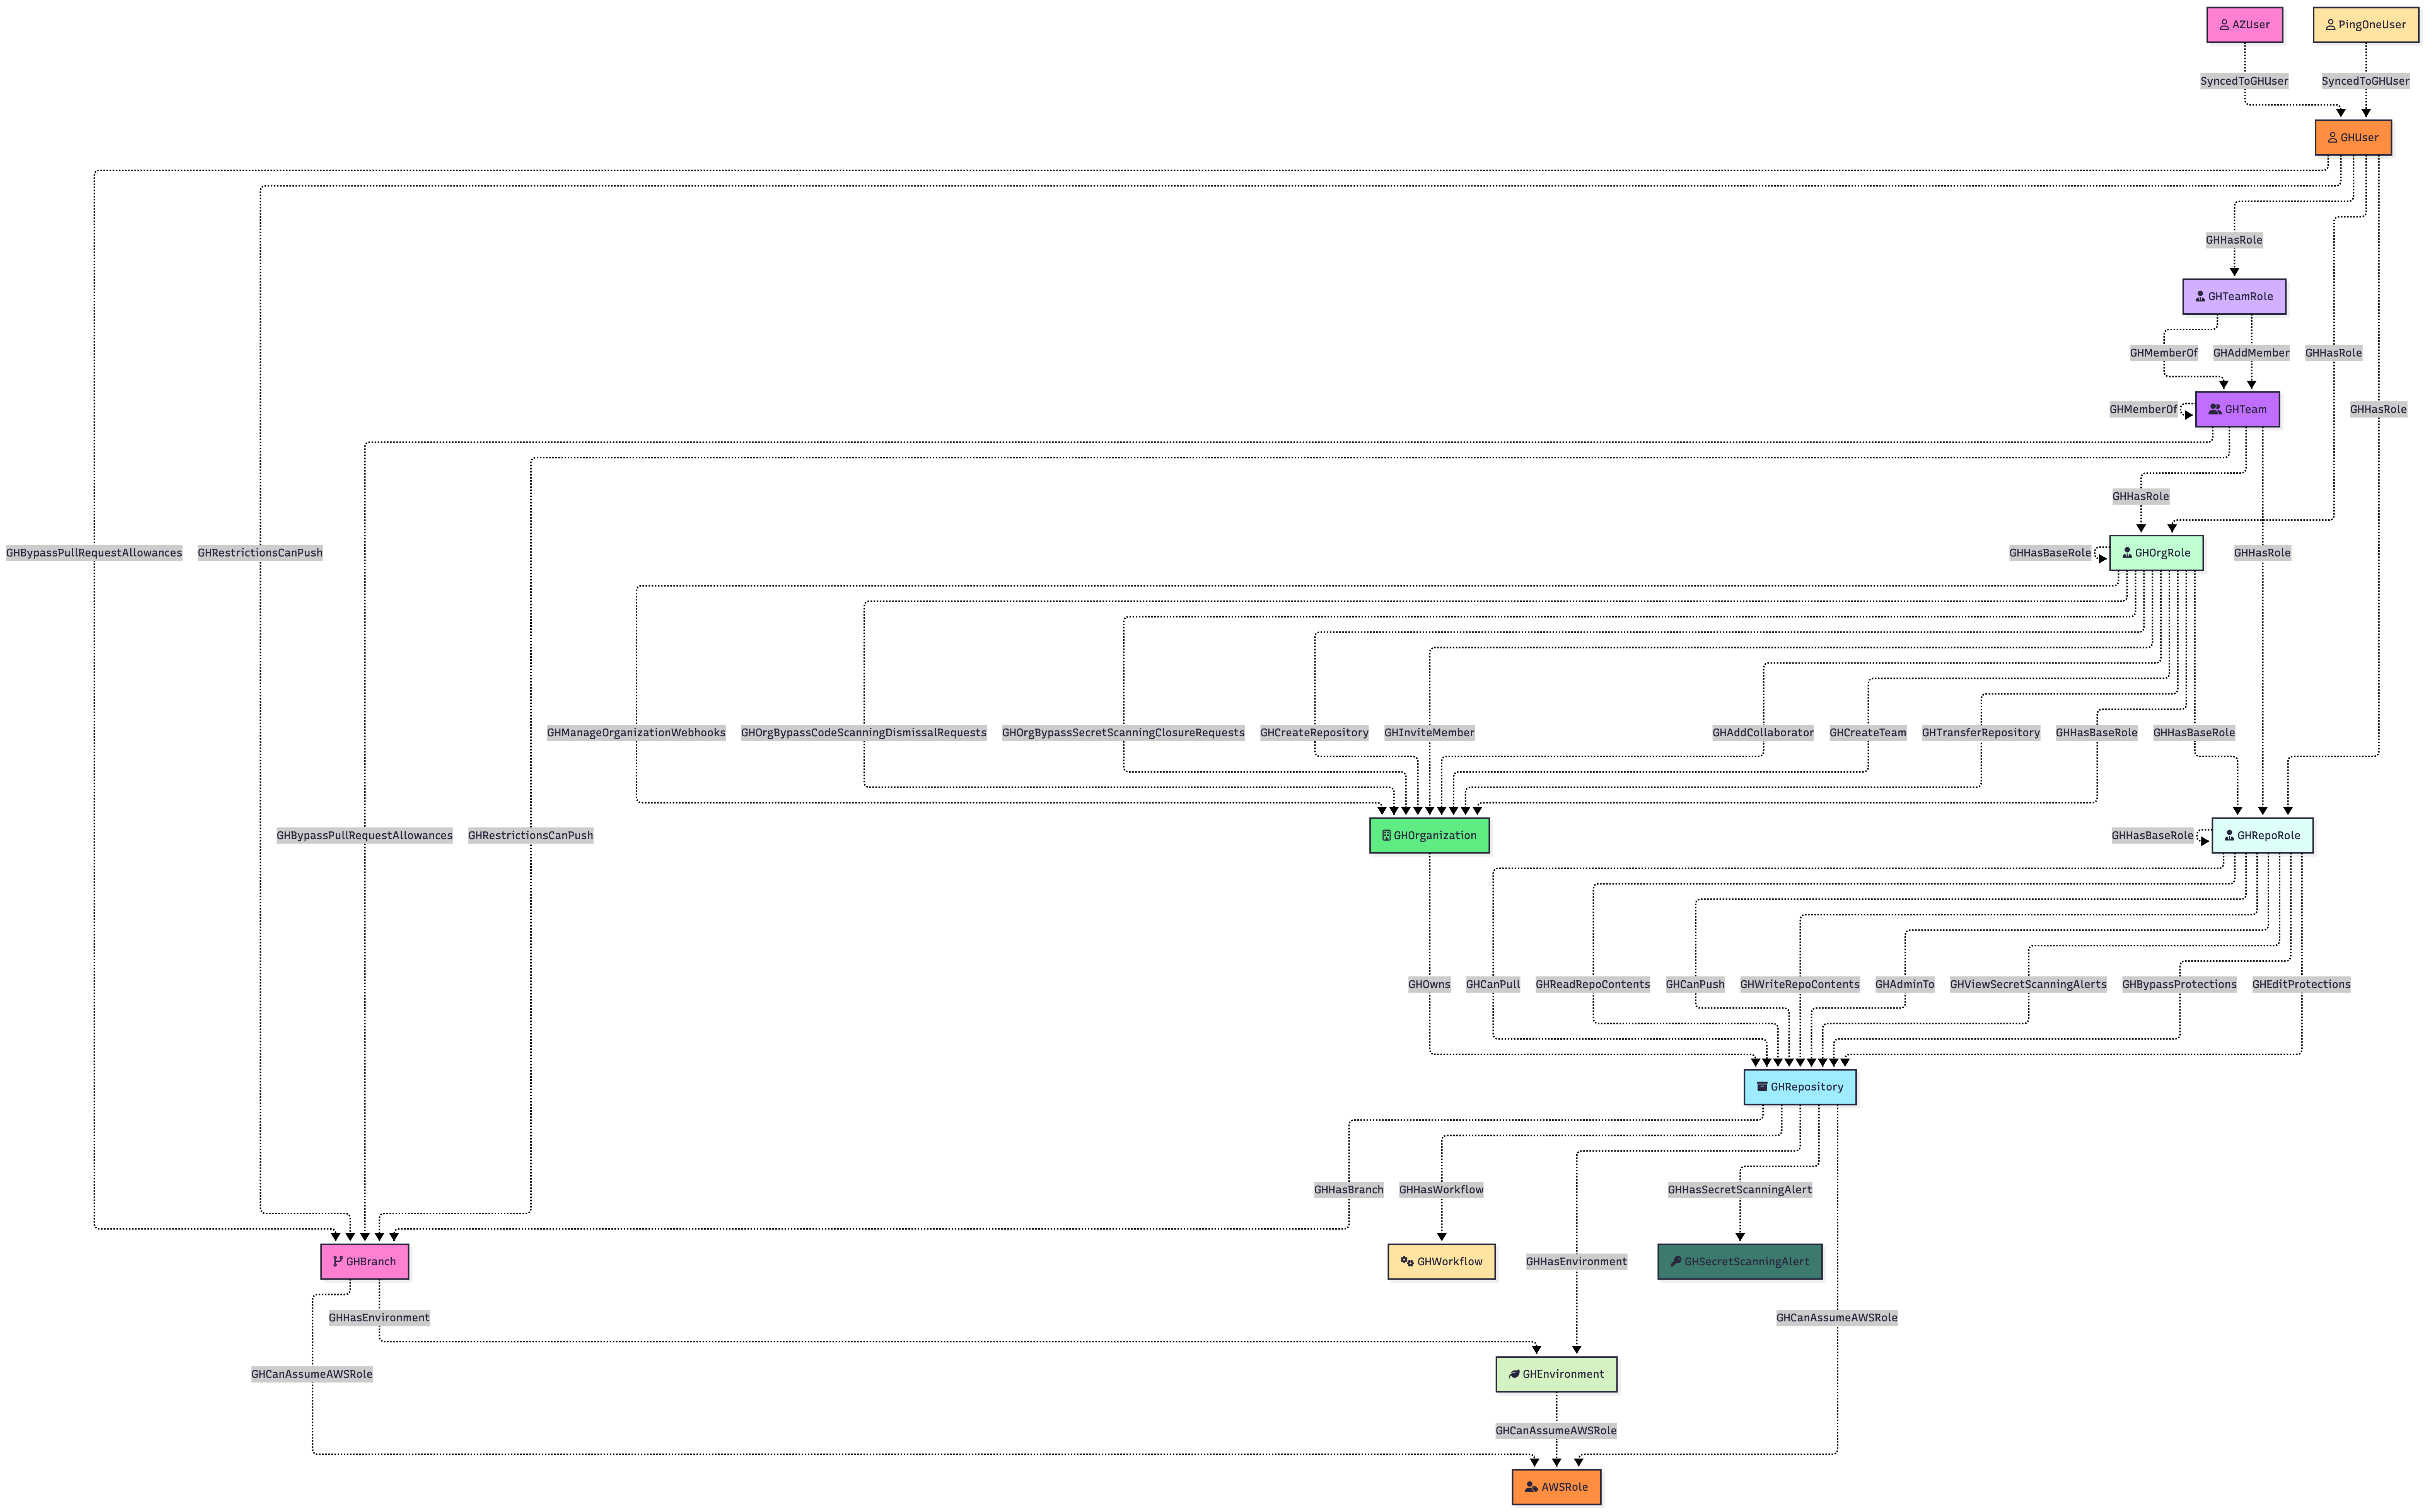 specterops/githound
BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…
 t94j0/adexplorersnapshot-rs
Converts Active Directory Explorer snapshot (.dat) files into BloodHound CE JSON archives for graph-based AD attack-path analysis and reconnaissance.
 cyberark/skyark
SkyArk helps to discover, assess and secure the most privileged entities in Azure and AWS
 drunkf0x/adspider
Monitor changes in Active Directory with replication metadata