cartography
Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…

Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…

Six Degrees of Domain Admin

Infrastructure cloud modulaire, redondante et 100% souveraine pour s'affranchir des GAFAM. Guides techniques, architecture Zero-Trust et chiffrement…

Free email OSINT tool, 2500+ platforms, identity clustering, breach detection. No API keys required. pip install mailaccess

A forensic reconstruction engine for cloud and identity incident response.

Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…

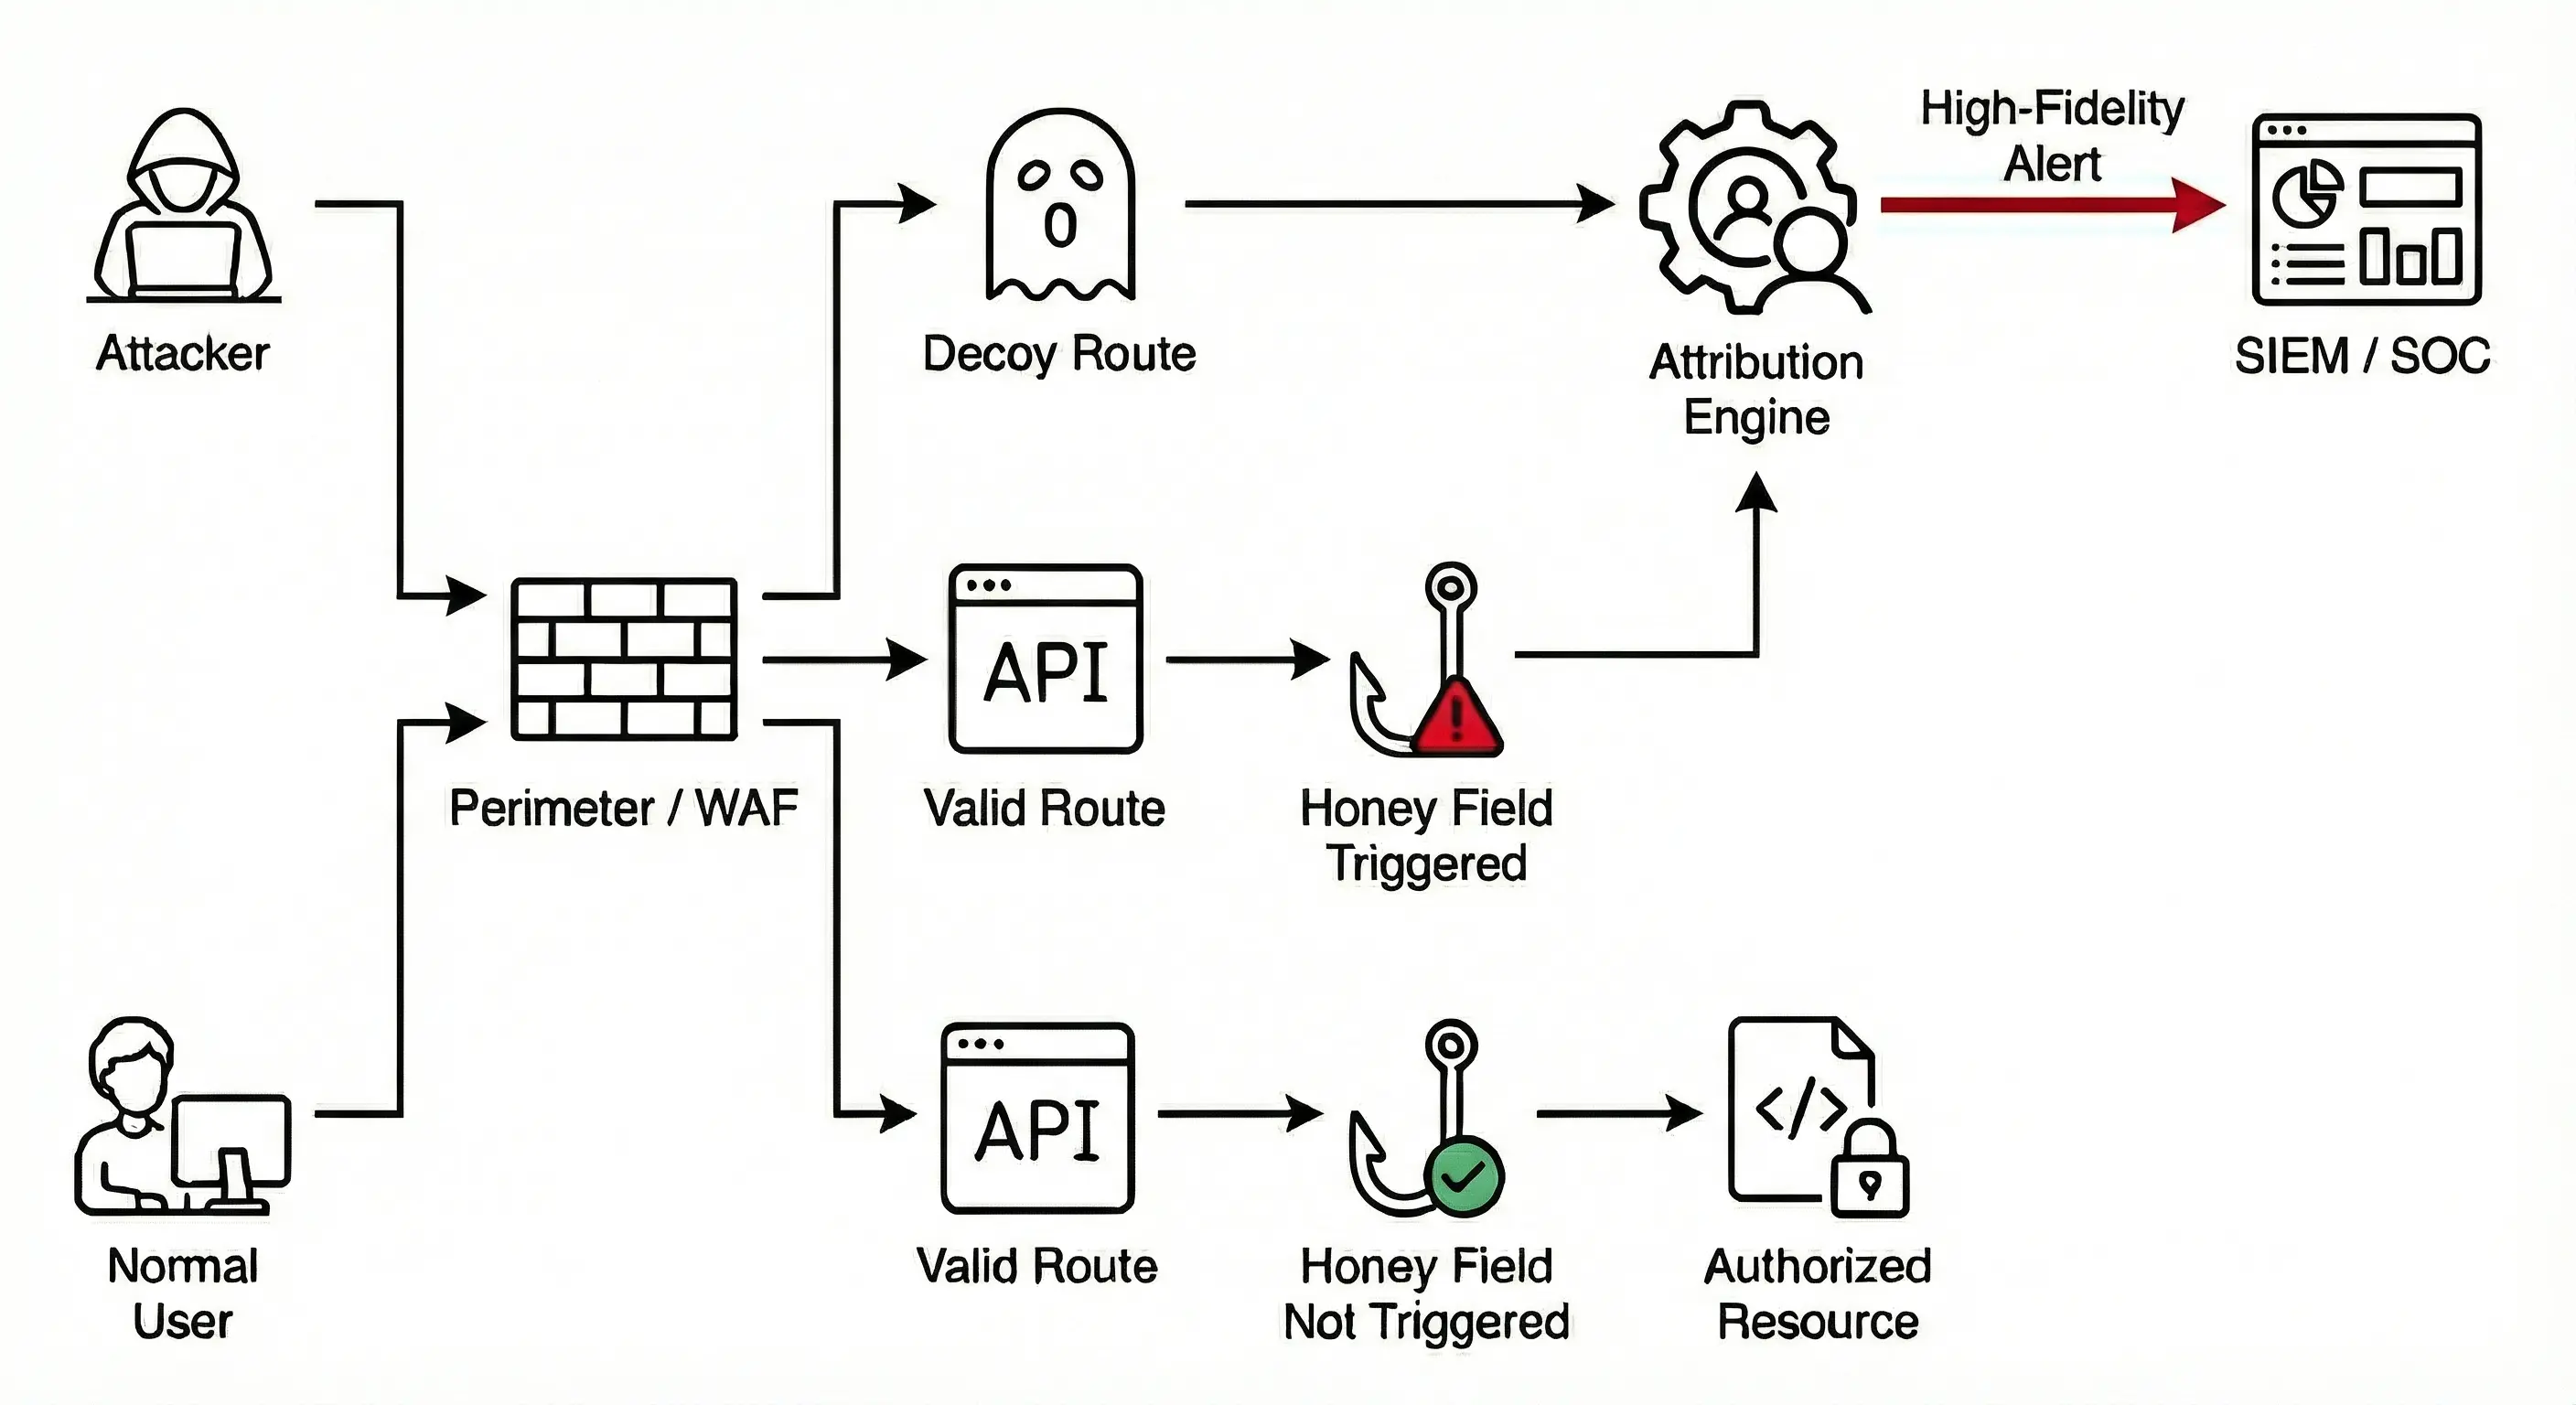
Open-source framework for embedding realistic decoy routes and honey fields into APIs to detect attackers probing business logic, converting…

A collection of Azure AD/Entra tools for offensive and defensive security purposes

In-depth ldap enumeration utility

Creating attacks paths across management and data planes

Entra ID user enumeration and auth method discovery via the public GetCredentialType API

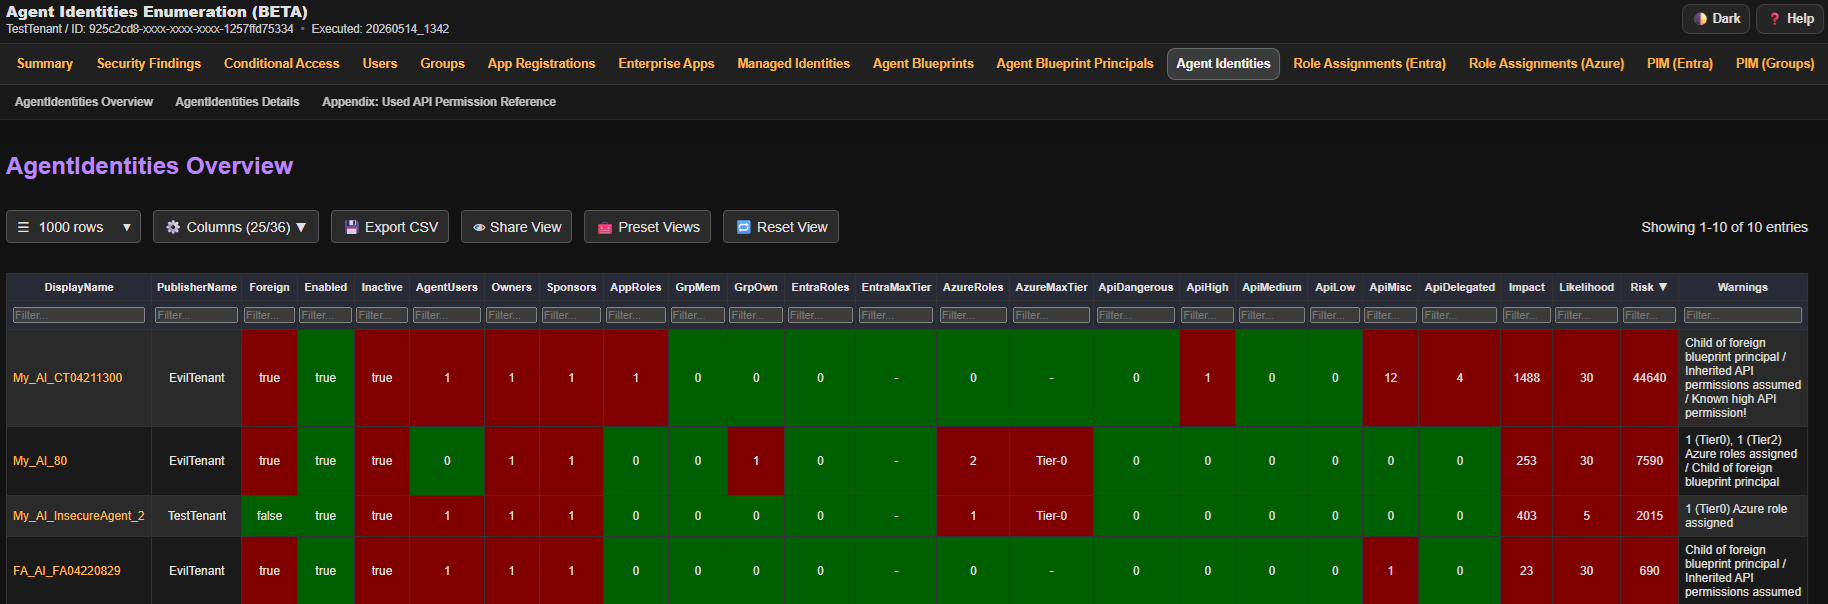
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…

A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…

AI runtime inventory: discover shadow AI, trace LLM calls

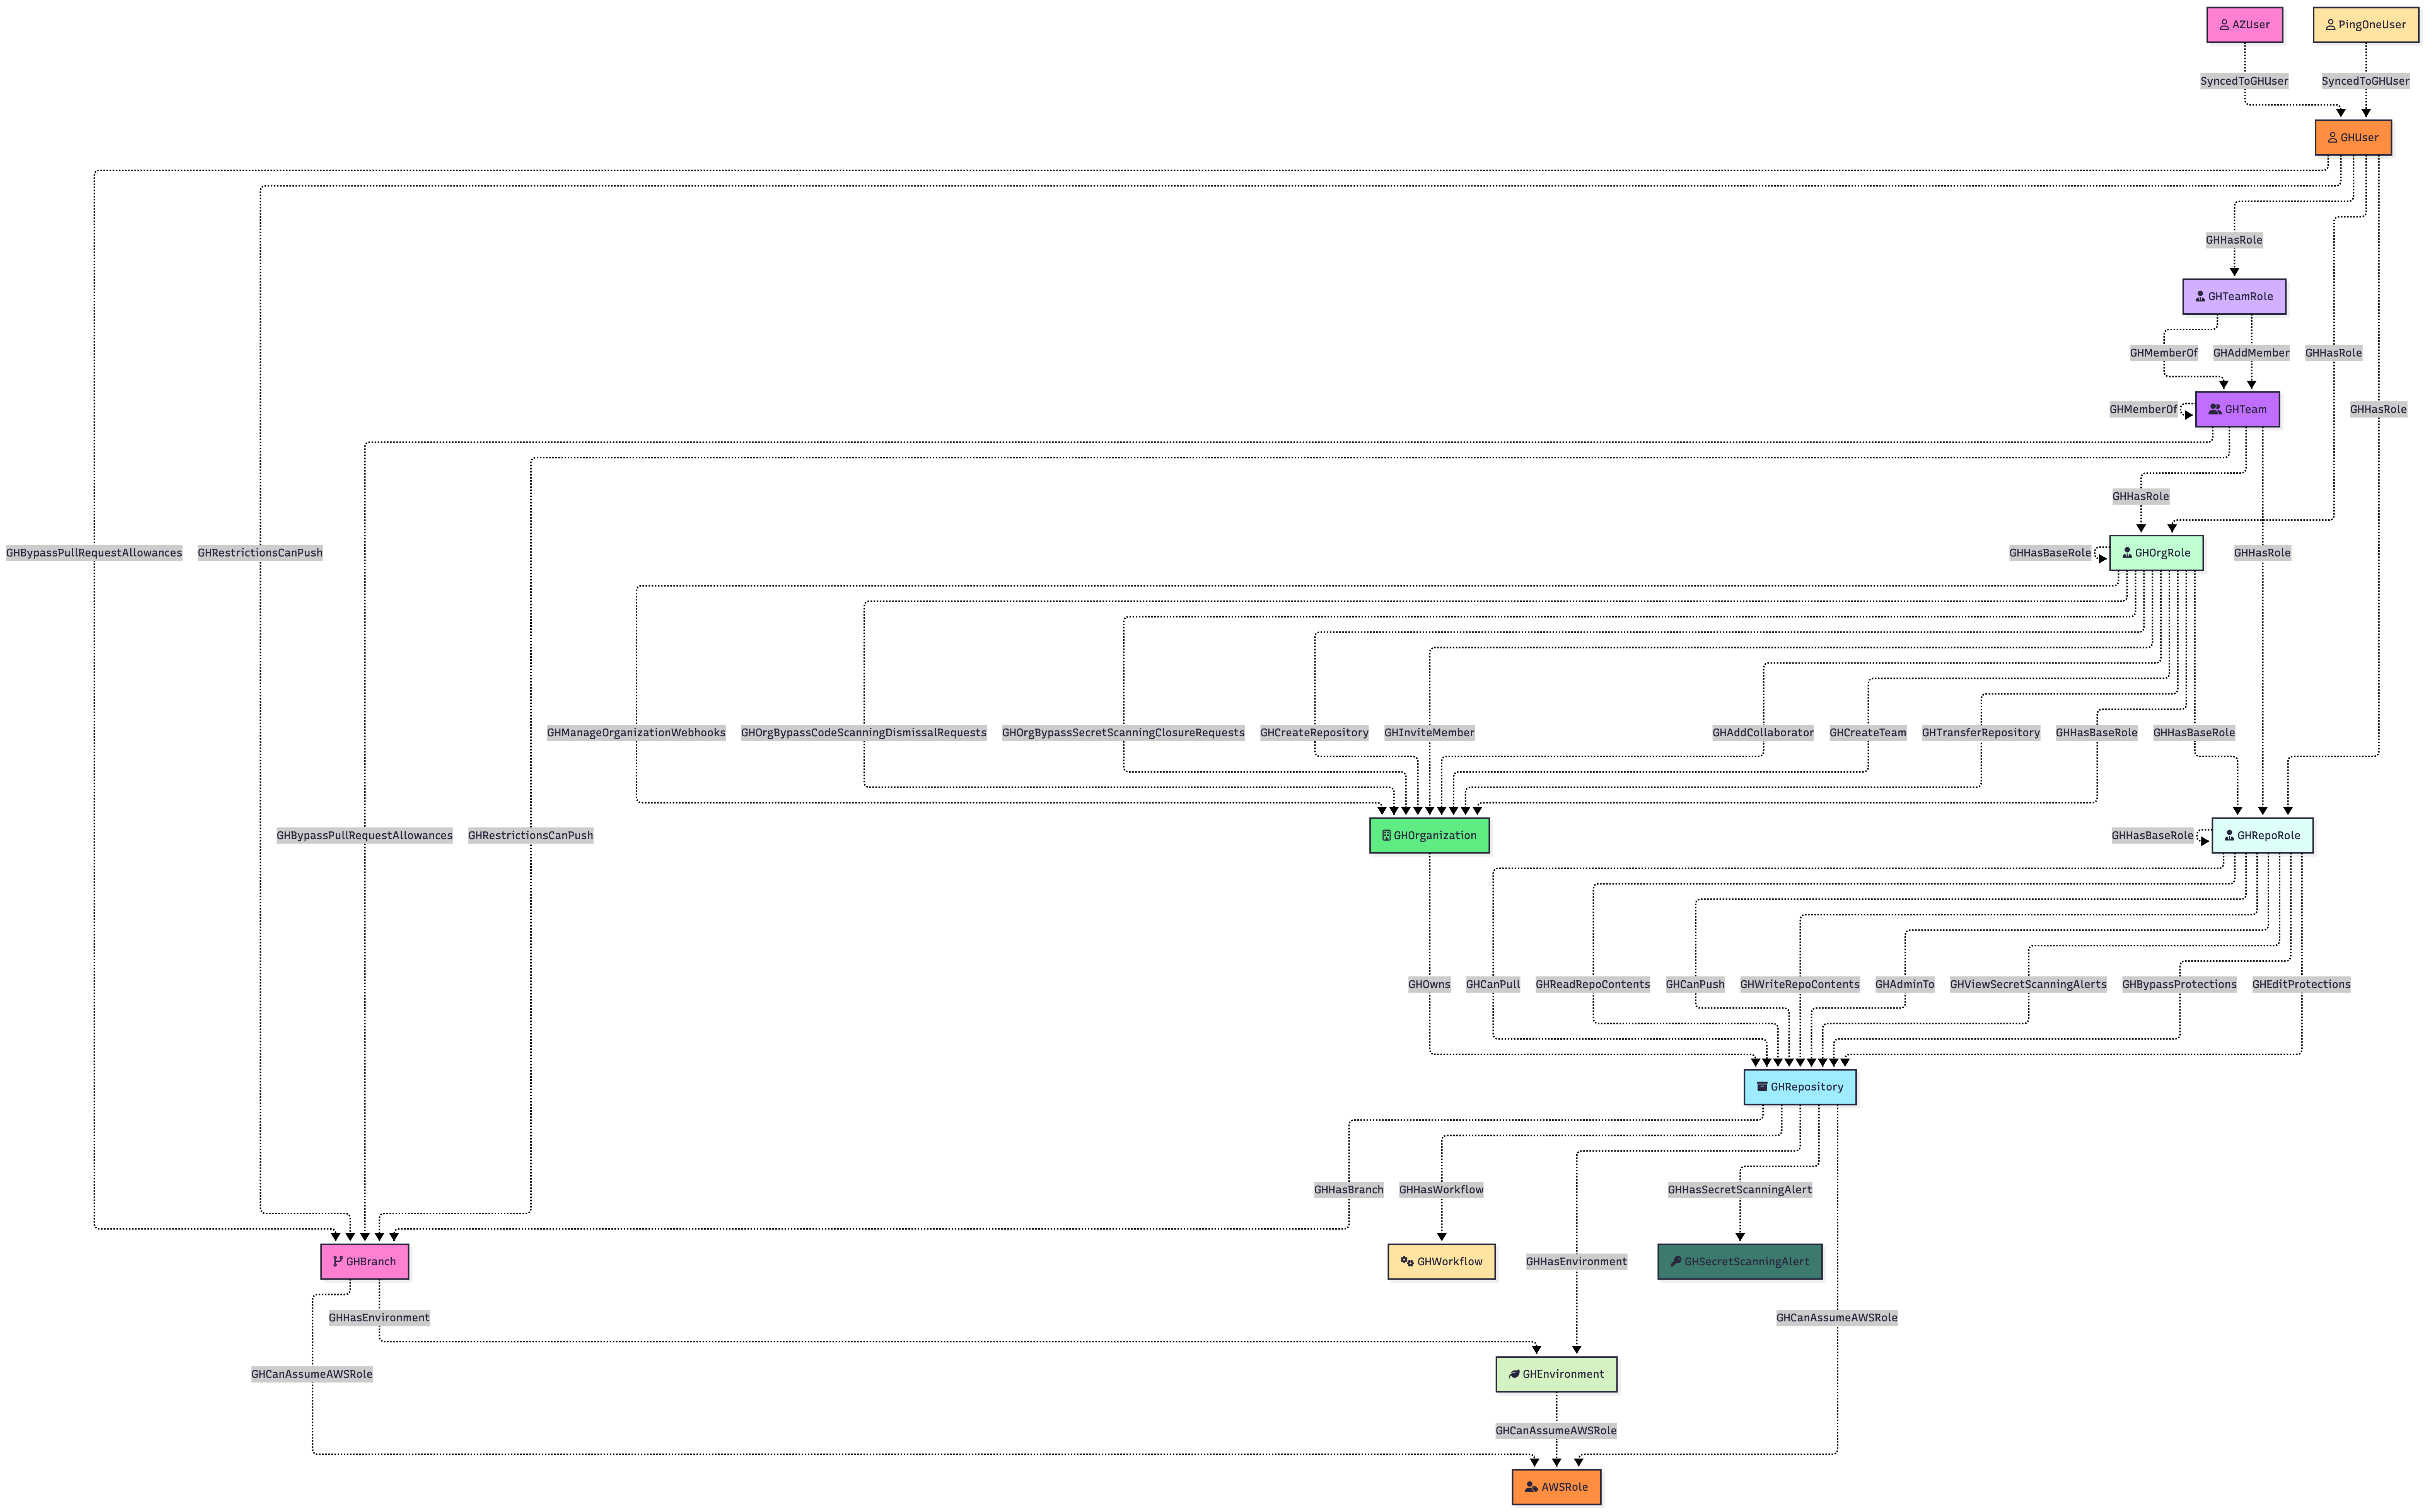
BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…

Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…

Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.

Bash and PowerShell scripts for Azure security assessments, covering IAM privilege escalation, container registry exploitation, Key Vault exposure,…